WAPT - Web Application Penetration Testing in Bangalore, IndiaINR

WAPT - Web Application Penetration Testing Live Online in Bangalore

Overall rating: 4.9 based on 3,795 reviewsG 4.9/5f 4.9/5

Live instructor-led online classes for Bangalore learners

The WAPT (Web Application Penetration Testing) training at WebAsha Technologies in Bangalore is a hands-on, job-oriented web application penetration testing program.

You learn the OWASP Top 10 and more advanced web attacks: SQL and command injection, cross-site scripting (XSS), CSRF, authentication and session flaws, access-control bypasses (IDOR), SSRF, file upload and business-logic attacks. The work is done with Burp Suite, sqlmap and related tools, and you write professional reports on what you find.

The course is meant for aspiring web penetration testers and bug-bounty hunters. It builds skills employers ask for and prepares you for certifications such as WAHS, OSWA and eWPT. You are taught by WebAsha's trainers and practise in real labs.
Duration:40 Hrs (Weekdays & Weekend Session)
Mode:Live Instructor-Led Online Training
Certification:WebAsha WAPT Course Certificate (Job-Oriented)
Institute:WebAsha Technologies
Includes:Hands-On Labs, Real Projects & Attendance Certificate
Trusted By

1000+ leading universities and companies

Our learners are hired by the world's most respected technology, IT services and consulting brands.

  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
Recent Placements Testimonials

WAPT - Web Application Penetration Testing recent reviews

Our learners talk about how the program changed their careers.

Verified Reviews

Student reviews and success stories

Real feedback from learners now placed across top technology and consulting firms.

SG

Sachin Gaikwad

Penetration Tester · Vodafone Idea

“WebAsha's Web Application Penetration Testing training turned a tough certification into an enjoyable learning experience. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. The placement assistance team actively shared openings and guided me until I was placed. Flexible batch timings let me attend alongside my job without any stress. This training accelerated my career growth, and I would gladly recommend it to anyone.”
Verified Student
KG

Kajal Gupta

Penetration Tester · Barclays

“I recently finished the Web Application Penetration Testing course at WebAsha Technologies and it was worth every minute. Flexible batch timings let me attend alongside my job without any stress. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. A big thank you to the trainers and team for such a rewarding learning experience.”
LinkedIn Review
SB

Sandeep Bhosale

Ethical Hacker · Zensar

“I recently finished the Web Application Penetration Testing course at WebAsha Technologies and it was worth every minute. The learning experience was structured, practical and paced just right for working professionals. The study materials and recorded sessions were detailed and easy to revise from. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. If you want practical, job-ready skills in Web Application Penetration Testing, WebAsha is the place to be.”
Google Review
IA

Imran Ansari

SOC Analyst · Wipro

“Enrolling in Web Application Penetration Testing at WebAsha is one of the best career decisions I have made. The trainers are clearly industry experts and answered even my toughest doubts patiently. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. Easily a five-star experience that prepared me for both the exam and real work.”
LinkedIn Review
RR

Rohit Reddy

SOC Analyst · Accenture

“My Web Application Penetration Testing journey with WebAsha gave me exactly the practical depth I was looking for. Every topic was reinforced with practical lab assignments instead of just slides. The trainers are clearly industry experts and answered even my toughest doubts patiently. Hands-on practice on real lab systems built genuine confidence, not just theory. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. A big thank you to the trainers and team for such a rewarding learning experience.”
Facebook Review
KJ

Kavita Jadhav

Penetration Tester · Accenture

“My Web Application Penetration Testing journey with WebAsha gave me exactly the practical depth I was looking for. The placement assistance team actively shared openings and guided me until I was placed. We worked hands-on with ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab, which made every concept stick. Doubt-clearing sessions ran even after class hours, which I really appreciated. Easily a five-star experience that prepared me for both the exam and real work.”
Verified Student
OB

Omkar Bhosale

Ethical Hacker · JPMorgan

“I recently finished the Web Application Penetration Testing course at WebAsha Technologies and it was worth every minute. The real-world implementation examples helped me understand how things work on the job. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. The certification preparation and mock tests made the actual exam feel straightforward. The knowledge and confidence I gained here continue to help me every day at work.”
Google Review
TS

Tejas Shaikh

Security Analyst · Mphasis

“The Web Application Penetration Testing program at WebAsha genuinely lived up to its reputation. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. The cloud labs were available round the clock, so I could practise assignments whenever I had time. The real-world implementation examples helped me understand how things work on the job. The batch was slightly large at times, yet the hands-on focus and support made it well worth it.”
Verified Student
RB

Rajesh Banerjee

Penetration Tester

“WebAsha's Web Application Penetration Testing training turned a tough certification into an enjoyable learning experience. Hands-on practice on real lab systems built genuine confidence, not just theory. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. Easily a five-star experience that prepared me for both the exam and real work.”
Google Review
Career Roadmap

From your first class to placement

A step-by-step path from your first lesson to certification and a job offer.

Step 1 of 8

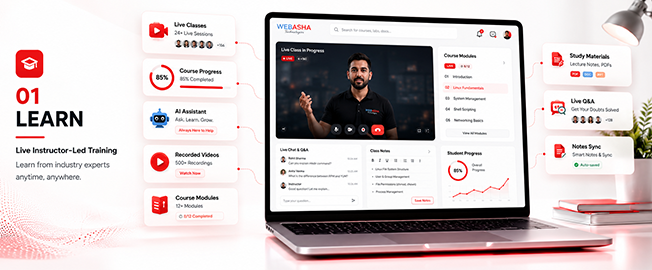
Learn

  • Live instructor-led training
  • Concept-first curriculum
  • Recorded sessions
Foundations & Core Concepts
Learn preview
Training Key Features

WAPT - Web Application Penetration Testing training key features

What you get from our WAPT - Web Application Penetration Testing course: a solid foundation in the basics and real-world, skills you can use at work.

  • Post Training Support

  • Real Time Projects : 2

  • Certification & Job Assistance

  • Course Duration : 2 Months

  • Hands-on Training

  • Full Day Lab Access

Our cloud lab

WAPT - Web Application Penetration Testing cloud lab environment

Our practical lab

Program highlights

What learners get at WebAsha Technologies: practical IT training and the skills employers hire for.

Learning Experience

  • In-Depth Practical Training with Real-World Scenarios
  • Choose Between In-Person or Virtual Classes (Flexible Schedules)
  • Guidance from Seasoned IT Professionals
  • Complimentary Intro to Emerging Tech Topics
  • One-on-One Support for Clarifying Concepts
  • Regular Hands-On Exercises and Live Projects
  • Access to a Library of 150+ Training Videos for a Year

Career Development

  • Tailored Job Placement Support with Multiple Interviews
  • Custom Resume Crafting and Interview Coaching
  • Workshops on Professional Skills and Teamwork
  • Affordable Payment Plans with No Extra Fees
  • Help Preparing for International Certifications
  • Personal Career Guidance from Experts
  • Practice Interviews with Industry Leaders

Why choose WebAsha Technologies

Career-focused IT training with expert mentors, practical labs and vendor certifications, so you stand out when you apply for jobs.

Features Recommended
WebAsha Technologies
Other Institutes
Expert Trainers
10+ Years Experienced Industry Professionals
Freshers or Part-time Instructors
Course Curriculum
Updated for Current Tools (Cybersecurity, Cloud, DevOps, Linux, AI/ML)
Basic or Outdated Content
Hands-on Learning
Real Projects, Labs & Case Studies
Theory-Focused, Limited Practical
Certifications
Vendor-Issued (EC-Council, OffSec, Red Hat, AWS, Microsoft, etc.)
Generic or Unrecognized Certificates
Placement Support
100% Assistance + Resume & Interview Coaching
Limited or No Job Support
Flexible Learning
Classroom & Online Training Options
Rigid Timings, Mostly Classroom-Only
Learning Resources
Lifetime LMS Access, Study Materials, Recorded Sessions
Minimal or No Additional Resources
Batch Size
Small Groups with 1:1 Mentorship
Large, Crowded Batches

Upcoming batches & schedule

Saturday, October 17, 2026

Live Online
Weekend
10:00 AMIST
Enrollment OpenMax intake limit is 10

Monday, October 19, 2026

Live Online
Weekday
8:00 AMIST
Enrollment OpenMax intake limit is 10

Monday, October 19, 2026

Live Online
Weekday
6:30 PMIST
Enrollment OpenMax intake limit is 10

Monday, October 19, 2026

Live Online
Fast Track
11:00 AMIST
Enrollment OpenMax intake limit is 10

Saturday, October 24, 2026

Live Online
Weekend
10:00 AMIST
Enrollment OpenMax intake limit is 10

Monday, October 26, 2026

Live Online
Weekday
8:00 AMIST
Enrollment OpenMax intake limit is 10

Monday, October 26, 2026

Live Online
Weekday
6:30 PMIST
Enrollment OpenMax intake limit is 10

Monday, November 2, 2026

Live Online
Weekday
8:00 AMIST
Enrollment OpenMax intake limit is 10

Monday, November 2, 2026

Live Online
Weekday
6:30 PMIST
Enrollment OpenMax intake limit is 10
Flexible Scheduling

Can't find a schedule that works?

Our counsellors can help you arrange a batch that fits your timing.

Course insight 1Course insight 2

WAPT (Web Application Penetration Testing) course training overview

Learn WAPT in our Classroom and Online WAPT (Web Application Penetration Testing) Training at WebAsha Technologies. The course is practical and aimed at getting you a job in the field.

Training Overview:

WAPT is a hands-on, job-oriented program in web application penetration testing. It covers the OWASP Top 10 and other web attacks: injection, XSS, authentication and access-control flaws, SSRF, file upload and business-logic attacks. You work with Burp Suite and related tools and learn to write a professional report.

Intended Audience:

The course suits aspiring web penetration testers, application-security analysts and bug-bounty hunters who want practical web security skills.

Topics Covered:

  • OWASP Top 10: The core web vulnerability classes.
  • Injection: SQL injection and command injection, with sqlmap.
  • XSS & CSRF: Attacks that run in the user's browser.
  • Auth & Session: Weak logins, sessions and tokens.
  • Access Control: IDOR and authorisation bypasses.
  • SSRF & Upload: Server-side request forgery and file upload attacks.
  • Business Logic: Flaws in how the application's workflow is designed.
  • Reporting: Write a professional report with recommended fixes.

Requirements:

You should have basic computer knowledge. Online participants need a stable internet connection and a laptop or desktop for the live labs.

Pre-Requisites:

You should have basic web and security awareness before WAPT. CEH-level knowledge or the Cyber Security Course gives you that.

Career Benefits:

Employers hire for web security skills. In India, WAPT professionals typically earn ₹5 LPA to ₹30+ LPA, and bug-bounty income can add to that.
Certification path

CategoryTools & components covered
ProxyBurp Suite
Injectionsqlmap
Reconffuf, gobuster, nikto
XSSXSS payloads
ScriptingPython, JavaScript
AnalysisBrowser dev tools
FuzzingWeb fuzzers
PlatformKali Linux

Curriculum WAPT - Web Application Penetration Testing

WAPT (Web Application Penetration Testing): course modules

1. Web Fundamentals & OWASP Top 10

The course starts with how web applications are built and where they usually break. The OWASP Top 10 is the map for the modules that follow.

  • Understand web architecture
  • Map the OWASP Top 10 to the weaknesses you will test for
  • Set up Kali Linux and Burp Suite as your testing platform
  • Inspect requests and responses with browser dev tools
2. Injection Attacks

Injection flaws let attacker input run as a database query or a system command. You exploit them by hand and with tooling.

  • Exploit SQL injection
  • Exploit command injection
  • Use sqlmap effectively
3. XSS, CSRF & Client-Side

This module covers attacks that target the user's browser.

  • Exploit cross-site scripting (XSS) with crafted payloads
  • Exploit cross-site request forgery (CSRF)
  • Chain client-side flaws
  • Read and write the JavaScript these attacks rely on
4. Authentication & Session Attacks

You test how an application identifies its users and keeps them logged in.

  • Break authentication
  • Attack sessions and tokens
  • Intercept and replay login traffic in Burp Suite
5. Access Control & IDOR

Access-control testing checks whether a user can reach data or functions meant for someone else.

  • Bypass authorization
  • Exploit insecure direct object references (IDOR)
  • Compare what different user roles can reach
6. SSRF, File Upload & Business Logic

Server-side flaws and mistakes in the application's own workflow are covered together here.

  • Exploit server-side request forgery (SSRF)
  • Attack file upload features
  • Attack business logic
  • Find hidden content with ffuf, gobuster and nikto
7. Reporting & Remediation

A penetration test ends with a report the client can act on.

  • Write professional reports
  • Recommend fixes
  • Describe each finding so that developers can reproduce it
8. WAPT Projects & Career Guidance

The last module puts the earlier ones together on full assessments and looks at what comes next.

  • Complete real assessments
  • Plan your certification path (WAHS, OffSec OSWA, eWPT)
  • Placement support from WebAsha

Download the complete course syllabus

Get the full curriculum, modules & exam details delivered to you instantly.

Meet our expert trainers

Learn from certified WAPT - Web Application Penetration Testing experts who work in the industry and teach with practical, real-world examples.

  • Simplified Guidance: Break down Linux concepts for beginners.
  • Hands-On Practice: Engage in labs for command-line and admin tasks.
  • Customized Support: Offer one-on-one help for your goals.
  • Career & Lab Aid: Assist with projects and exam prep.
  • Industry Knowledge: Draw from extensive Red Hat experience.
  • Certified Professionals: Hold RHCSA, RHCE credentials.
  • Real-World Application: Insights from enterprise Linux deployments.
  • Training Success: Over 1,000 students guided annually.
  • Corporate Links: Partnerships with IBM, Accenture, Wipro.
Free Skill Assessment

Self assessment

Test your skills with an online assessment exam and find out how ready you are for your certification.

  • Free mock test
  • Instant score report
  • Mapped to the certification
Learner taking an online skills assessment

WAPT (Web Application Penetration Testing): certification & career path

This WAPT program is a hands-on, job-oriented course that ends with a WebAsha completion certificate. It is vendor-neutral and is not tied to one exam. The course builds the full web-pentest skill set and prepares you for certifications such as WAHS, OffSec OSWA and eWPT. WebAsha Technologies in Bangalore adds real web application assessment labs and placement support to help you start a web penetration testing career. The same skills are useful for bug-bounty hunting.

  • Expert Trainers: Taught by experienced web pentesters.
  • Complete OWASP Coverage: The Top 10 and more advanced attacks.
  • Hands-On Labs: You exploit real web applications.
  • Industry Tools: Burp Suite, sqlmap and related tools.
  • Certification Path: Prepares you for WAHS, OSWA and eWPT.
  • Bug-Bounty Ready: The same skills are used in bug-bounty hunting.
  • Placement Support: Help with your resume and interviews.
  • Completion Certificate: A WebAsha WAPT certificate.

WAPT (Web Application Penetration Testing): certification & career path

AttributeDetails
CertificateWebAsha WAPT course completion certificate
FormatHands-on and job-oriented (labs and real assessments)
LevelIntermediate
Prepares ForWAHS, OffSec OSWA, eWPT and other web security certifications
CoverageOWASP Top 10 and advanced web attacks
PrerequisiteBasic web and security awareness
IncludesReal labs, assessments and placement support
ModeOnline or classroom

WAPT (Web Application Penetration Testing): certification & next steps

This WAPT program is a hands-on, job-oriented course that ends with a WebAsha completion certificate. It is vendor-neutral and is not tied to one exam. The course builds the full web-pentest skill set and prepares you for certifications such as WAHS, OffSec OSWA and eWPT. WebAsha Technologies in Bangalore adds real web application assessment labs and placement support to help you start a web penetration testing career. The same skills are useful for bug-bounty hunting.

Job roles and salary outlook after WAPT (Web Application Penetration Testing)

Web application security skills are in demand across India. The table shows typical roles and salary ranges for WAPT professionals, and bug-bounty income can add to them.

Job Title Primary Responsibilities Average Salary (INR)
Web Application Pentester Tests web applications for exploitable flaws. Fresher: ₹5-9 LPA
Experienced: ₹15-28 LPA
Application Security Analyst Analyses the security of web applications. Fresher: ₹5-8 LPA
Experienced: ₹14-26 LPA
Bug Bounty Hunter Finds web flaws and reports them to programme owners. Variable: ₹6-30+ LPA
Penetration Tester Assesses systems and exploits the weaknesses found. Fresher: ₹5-8 LPA
Experienced: ₹14-26 LPA
VAPT Engineer Runs vulnerability assessments and penetration tests. Fresher: ₹5-8 LPA
Experienced: ₹13-24 LPA
Security Consultant (Web) Advises clients on web security. Experienced: ₹14-28 LPA

Salaries vary with experience and skill. WAPT gives you practical ability you can show an employer.


Career benefits of WAPT (Web Application Penetration Testing)

WAPT builds the web application penetration testing skills that employers hire for, and the same skills are a way into bug bounty.

  • Job-Oriented: Practical training aimed at getting you hired.
  • Strong Demand: The salary table below lists the roles that use these skills.
  • Salaries: See the salary table below for typical ranges by role.
  • Hands-On Proof: You finish with real labs and projects to show.
  • Career Growth: A base for the specialised certifications named on this page.
  • Transferable: The method applies to any target you are asked to test.

Why choose WAPT (Web Application Penetration Testing) training at WebAsha Technologies in Bangalore

Learn WAPT (Web Application Penetration Testing) with WebAsha Technologies. Our program is hands-on and job-oriented, with expert trainers and placement support.

  • Expert Trainers: Taught by experienced web pentesters.
  • Complete OWASP Coverage: The Top 10 and more advanced attacks.
  • Hands-On Labs: You exploit real web applications.
  • Industry Tools: Burp Suite, sqlmap and related tools.
  • Certification Path: Prepares you for WAHS, OSWA and eWPT.
  • Bug-Bounty Ready: The same skills are used in bug-bounty hunting.
  • Placement Support: Help with your resume and interviews.
  • Completion Certificate: A WebAsha WAPT certificate.

Learning from Bangalore

Cyber Security for learners in Bangalore, Karnataka, India

About Bangalore

India's largest technology hub, home to major IT services firms, global capability centres of multinational companies and a large startup ecosystem. It is also a centre for aerospace, defence research and biotechnology. GCCs and product companies run large security teams, and cloud security and SOC skills are in steady demand.

Who learns from Bangalore

Learners range from freshers at RVCE, BMSCE and VTU colleges to working software engineers wanting to shift into security, DevOps or ML. Many are mid-career professionals at GCCs aiming for certifications to move up.

Attending online

Commutes along Outer Ring Road, Silk Board or to Electronic City can take hours, which leaves little room for classroom training. Live online classes can be joined from home in the evening or on weekends.

Cyber Security career scope in Bangalore

Cyber Security jobs in Bangalore

Bengaluru's security hiring ranges from service-desk SOCs in Electronic City to aerospace labs in the city's east. Infosys and Wipro run managed security and SOC services for overseas clients from their Electronic City and Sarjapur campuses, Flipkart protects payment and customer data at e-commerce scale, and ISRO and Hindustan Aeronautics Limited guard sensitive engineering networks where clearance and secure configuration matter.

Global capability centres along the Outer Ring Road and in Manyata and Bagmane tech parks add cloud security and threat-intelligence teams. Learners include RV College of Engineering, BMS College of Engineering and VTU-affiliated students, plus working developers moving across into security. A path that fits local interviews runs from CompTIA Security+ to CEH, then SIEM and cloud security work leading to AZ-500 or AWS Security Specialty, with OSCP for penetration testers. Classes run on IST, so a learner stuck in Silk Board traffic can still join later from home.

For students & freshers in Bangalore

For freshers in Bengaluru, being close to employers does not remove the competition, because graduates from across India arrive in the city each year chasing the same roles. A job-oriented program helps VTU-affiliated, RV College of Engineering and BMS College of Engineering students stand out with lab work and internship-style projects in security, cloud or data that go beyond a campus syllabus.

Non-engineering graduates from Bengaluru's degree colleges can use the same structure to enter support, SOC or data analyst roles. WebAsha's placement-guarantee program and its 500+ hiring partners add a route into product companies and global capability centres alongside VTU campus drives. Because sessions are taught on IST, students in hostels around Electronic City or Yelahanka can attend after college, and recordings help them prepare for the many off-campus coding tests that crowd placement season.

Tech community in Bangalore

Meetups, chapters and events near you

Bangalore has more tech meetups than anyone can attend, so it helps to be choosy. For security learners, OWASP Bangalore and null Bangalore are the obvious picks. They meet regularly, often together, sometimes with Garage4Hackers as well, and the meetings are free and open to anyone.

If you are doing an online course in ethical hacking or application security from Bangalore, go to one of these combined meets, listen to a few talks, and stay for the conversations afterwards. Many attendees work in security teams around the city and are happy to point a newcomer toward labs, tools or certifications. Once you are confident, volunteering to present a short session is a very good way to build a reputation.

Independent community groups, listed for reference. They are not run by or affiliated with WebAsha.

Local Economy

Bangalore's industries & employers

Sectors

IT services and software products Global capability centres Aerospace and defence Biotechnology Startups

Districts

Electronic City Whitefield and ITPL Outer Ring Road Manyata Tech Park Bagmane Tech Park

Employers

Infosys Wipro ISRO Hindustan Aeronautics Limited Biocon Flipkart

Context only; no affiliation implied.

Colleges

Indian Institute of Science IIIT Bangalore RV College of Engineering IIM Bangalore

WAPT - Web Application Penetration Testing for other cities

Program Highlights

What the program includes

Learning, career, certification and placement support in one program.

Learning benefits

  • Structured Curriculum
    Concept-first, job-ready syllabus
  • Hands-On Labs
    Practice every concept live
  • Expert-Led Sessions
    Learn from working professionals

Career benefits

  • Resume Building
    ATS-friendly, recruiter-ready
  • Mock Interviews
    Real interview simulations
  • Job Referrals
    Access to hiring partner network

Certification benefits

  • Globally Recognized
    Industry-standard certifications
  • Exam Preparation
    Targeted, exam-focused coaching
  • Practice Tests
    Unlimited mock assessments

Placement benefits

  • 500+ Hiring Partners
    Active recruiter network
  • Placement Drives
    Regular hiring opportunities
  • Salary Negotiation
    Guidance to maximize offers
Success Stories

Where our learners work now

Former students now working at leading companies, and how they got there.

CC

Chetan Chatterjee

Cyber Security Engineer · LTIMindtree

IT Support ExecutiveCyber Security Engineer
“Coming from a IT Support Executive background, switching felt risky, but WebAsha's Web Application Penetration Testing course gave me a clear path forward. The hands-on labs and live projects around ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab rebuilt my confidence from the ground up. I landed a Cyber Security Engineer position at LTIMindtree with a strong hike from 4.5 LPA to 9 LPA, and I owe it to WebAsha.”
IT Support Executive to Cyber Security Engineer at LTIMindtree
VN

Varun Naik

SOC Analyst · TCS

Non-IT ProfessionalSOC Analyst
“After a few years as a Non-IT Professional, I decided it was time for a real change and joined WebAsha's Web Application Penetration Testing training. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. I transitioned into a SOC Analyst role at TCS, nearly doubling my salary from 3 LPA to 6 LPA.”
How I became a SOC Analyst with WebAsha
AP

Ajay Pathan

Ethical Hacker · Amdocs

IT Support ExecutiveEthical Hacker
“I started out as a IT Support Executive and always wanted a stronger technical career, so I enrolled in the Web Application Penetration Testing program at WebAsha. The hands-on labs and live projects around ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab rebuilt my confidence from the ground up. The trainers were patient and genuinely industry-experienced, and the practical focus on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab made everything click. Within a few months I moved from IT Support Executive to Ethical Hacker at Amdocs, and my package grew from 3.5 LPA to 7 LPA.”
My journey: IT Support Executive to Ethical Hacker
TS

Tejas Shaikh

Security Analyst · Mphasis

“The Web Application Penetration Testing program at WebAsha genuinely lived up to its reputation. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. The cloud labs were available round the clock, so I could practise assignments whenever I had time. The real-world implementation examples helped me understand how things work on the job. The batch was slightly large at times, yet the hands-on focus and support made it well worth it.”
Cyber Security Certified
PM

Pallavi More

Penetration Tester · Birlasoft

Manual TesterPenetration Tester
“As a Manual Tester, I felt stuck in my growth, so I took the leap and signed up for Web Application Penetration Testing at WebAsha. Certification preparation, mock tests and repeated mock interviews prepared me for real technical rounds. Within a few months I moved from Manual Tester to Penetration Tester at Birlasoft, and my package grew from 6 LPA to 12 LPA.”
Manual Tester to Penetration Tester at Birlasoft
VT

Varun Thomas

Penetration Tester · Wipro

FresherPenetration Tester
“As a Fresher, I felt stuck in my growth, so I took the leap and signed up for Web Application Penetration Testing at WebAsha. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. I landed a Penetration Tester position at Wipro with a strong hike from 5 LPA to 11 LPA, and I owe it to WebAsha.”
Penetration Tester at Wipro - a career turnaround
MF

Mohit Fernandes

Cyber Security Engineer · Birlasoft

Diploma GraduateCyber Security Engineer
“I started out as a Diploma Graduate and always wanted a stronger technical career, so I enrolled in the Web Application Penetration Testing program at WebAsha. Working on real-world implementations helped me understand exactly how things run on the job. I transitioned into a Cyber Security Engineer role at Birlasoft, nearly doubling my salary from 4.5 LPA to 8.5 LPA.”
From Diploma Graduate to Cyber Security Engineer
VN

Vikas Nair

Ethical Hacker · Persistent Systems

Technical Support AssociateEthical Hacker
“My journey began as a Technical Support Associate with big ambitions, and the Web Application Penetration Testing program at WebAsha became the turning point. The placement team actively shared openings and coached me through resume building and every interview. I landed a Ethical Hacker position at Persistent Systems with a strong hike from 3.5 LPA to 6.5 LPA, and I owe it to WebAsha.”
Technical Support Associate to Ethical Hacker at Persistent Systems
NS

Neha Shaikh

Penetration Tester · Cognizant

Desktop Support EngineerPenetration Tester
“My journey began as a Desktop Support Engineer with big ambitions, and the Web Application Penetration Testing program at WebAsha became the turning point. The hands-on labs and live projects around ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab rebuilt my confidence from the ground up. The placement team actively shared openings and coached me through resume building and every interview. Within a few months I moved from Desktop Support Engineer to Penetration Tester at Cognizant, and my package grew from 2.4 LPA to 4.5 LPA.”
Desktop Support Engineer to Penetration Tester at Cognizant
Quick Summary

WAPT - Web Application Penetration Testing is a hands-on cyber security and ethical hacking training course by WebAsha Technologies, available online and in classroom with live projects, certification prep and placement support. It suits beginners and professionals, runs about 6 to 12 weeks, and leads to roles such as SOC Analyst, Penetration Tester, Security Analyst paying roughly 4.0 to 26.0 LPA.

Key takeaways for Bangalore

  • Master cyber security through hands-on, practical training.
  • Learn footprinting & reconnaissance and network scanning & enumeration.
  • Work on real-world projects and lab exercises.
  • Earn an industry-recognised certificate.
  • Get placement support for roles paying up to 26.0 LPA.

WAPT - Web Application Penetration Testing in Bangalore: WebAsha vs other options

FeatureWebAsha cyber securitySelf-studyGeneric online course
Live instructor-led trainingYesNoSometimes
Hands-on labs & real projectsYesLimitedLimited
Certification exam preparationYesSelf-managedVaries
Doubt-solving & mentorshipYesNoLimited
Placement assistanceYesNoRare
Industry-recognised certificateYesNoVaries

WAPT - Web Application Penetration Testing in Bangalore FAQs

Last updated: 10 July 2026

No. Learners in Whitefield, Electronic City or Koramangala join the same live batches online and avoid Outer Ring Road traffic.
Yes. Evening and weekend batches are available, and you join from home.
Yes. Courses map to certifications like CEH, AWS, Azure, Red Hat and Kubernetes.
Keep Exploring

Related courses

Take the next step in your IT career

Join thousands of learners who upskilled and got placed with WebAsha Technologies.