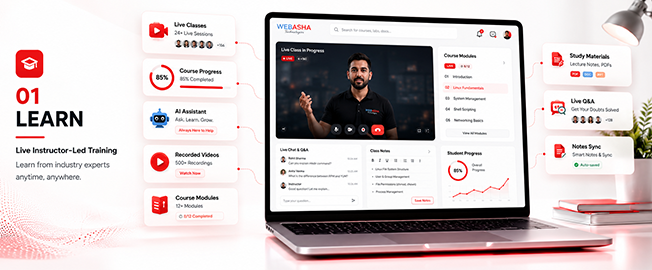
We run Classroom and Online Splunk Training (SIEM & Security Analytics) at WebAsha Technologies. Most of the time goes on practical lab work, and the aim is to get you ready for a job.
Training overview:
This is a hands-on, job-oriented program on Splunk, a data platform widely used for SIEM and security analytics. You learn to ingest and search machine data with SPL, build reports, dashboards and alerts, and apply Splunk to security operations: correlation, detection and SOC analytics. The course prepares you for SOC roles and Which Splunk certifications to take.
Intended audience:
The course suits aspiring SOC analysts, security analysts, Splunk administrators and data professionals who want hands-on SIEM and Splunk skills.
Topics covered:
-
Splunk Fundamentals: Splunk architecture and data ingestion.
-
SPL Search: Searching with the Search Processing Language.
-
Reports & Dashboards: Turning search results into reports and dashboards.
-
Alerts: Alerts that detect a condition and notify you.
-
Data Onboarding: Bringing machine data into Splunk.
-
Security Use Cases: Correlation searches and detection.
-
SOC Analytics: Investigating incidents with Splunk.
-
Certification Path: Which Splunk certifications to take.
Requirements:
Basic computer knowledge is recommended. If you join online, you need a stable internet connection and a laptop or desktop for the live labs.
Prerequisites:
Some familiarity with IT and logs is recommended. The program starts from Splunk fundamentals and is beginner-friendly.
Career benefits:
Splunk skills are in strong demand. In India, professionals with Splunk skills typically earn ₹4 LPA to ₹28+ LPA in SOC and SIEM roles.