WAPT - Web Application Penetration Testing

Overall rating: 4.9 based on 3,796 reviewsG 4.9/5f 4.9/5
The WAPT (Web Application Penetration Testing) training at WebAsha Technologies in Pune is a hands-on, job-oriented web application penetration testing program.

You learn the OWASP Top 10 and more advanced web attacks: SQL and command injection, cross-site scripting (XSS), CSRF, authentication and session flaws, access-control bypasses (IDOR), SSRF, file upload and business-logic attacks. The work is done with Burp Suite, sqlmap and related tools, and you write professional reports on what you find.

The course is meant for aspiring web penetration testers and bug-bounty hunters. It builds skills employers ask for and prepares you for certifications such as WAHS, OSWA and eWPT. You are taught by WebAsha's trainers and practise in real labs.
Duration:40 Hrs (Weekdays & Weekend Session)
Mode:Online/Classroom
Certification:WebAsha WAPT Course Certificate (Job-Oriented)
Institute:WebAsha Technologies
Includes:Hands-On Labs, Real Projects & Attendance Certificate
Trusted By

1000+ leading universities and companies

Our learners are hired by the world's most respected technology, IT services and consulting brands.

  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
Recent Placements Testimonials

WAPT - Web Application Penetration Testing recent reviews

Our learners talk about how the program changed their careers.

Verified Reviews

Student reviews and success stories

Real feedback from learners now placed across top technology and consulting firms.

SG

Sachin Gaikwad

Penetration Tester · Vodafone Idea

“WebAsha's Web Application Penetration Testing training turned a tough certification into an enjoyable learning experience. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. The placement assistance team actively shared openings and guided me until I was placed. Flexible batch timings let me attend alongside my job without any stress. This training accelerated my career growth, and I would gladly recommend it to anyone.”
Verified Student
KG

Kajal Gupta

Penetration Tester · Barclays

“I recently finished the Web Application Penetration Testing course at WebAsha Technologies and it was worth every minute. Flexible batch timings let me attend alongside my job without any stress. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. A big thank you to the trainers and team for such a rewarding learning experience.”
LinkedIn Review
SB

Sandeep Bhosale

Ethical Hacker · Zensar

“I recently finished the Web Application Penetration Testing course at WebAsha Technologies and it was worth every minute. The learning experience was structured, practical and paced just right for working professionals. The study materials and recorded sessions were detailed and easy to revise from. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. If you want practical, job-ready skills in Web Application Penetration Testing, WebAsha is the place to be.”
Google Review
IA

Imran Ansari

SOC Analyst · Wipro

“Enrolling in Web Application Penetration Testing at WebAsha is one of the best career decisions I have made. The trainers are clearly industry experts and answered even my toughest doubts patiently. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. Easily a five-star experience that prepared me for both the exam and real work.”
LinkedIn Review
RR

Rohit Reddy

SOC Analyst · Accenture

“My Web Application Penetration Testing journey with WebAsha gave me exactly the practical depth I was looking for. Every topic was reinforced with practical lab assignments instead of just slides. The trainers are clearly industry experts and answered even my toughest doubts patiently. Hands-on practice on real lab systems built genuine confidence, not just theory. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. A big thank you to the trainers and team for such a rewarding learning experience.”
Facebook Review
KJ

Kavita Jadhav

Penetration Tester · Accenture

“My Web Application Penetration Testing journey with WebAsha gave me exactly the practical depth I was looking for. The placement assistance team actively shared openings and guided me until I was placed. We worked hands-on with ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab, which made every concept stick. Doubt-clearing sessions ran even after class hours, which I really appreciated. Easily a five-star experience that prepared me for both the exam and real work.”
Verified Student
OB

Omkar Bhosale

Ethical Hacker · JPMorgan

“I recently finished the Web Application Penetration Testing course at WebAsha Technologies and it was worth every minute. The real-world implementation examples helped me understand how things work on the job. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. The certification preparation and mock tests made the actual exam feel straightforward. The knowledge and confidence I gained here continue to help me every day at work.”
Google Review
TS

Tejas Shaikh

Security Analyst · Mphasis

“The Web Application Penetration Testing program at WebAsha genuinely lived up to its reputation. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. The cloud labs were available round the clock, so I could practise assignments whenever I had time. The real-world implementation examples helped me understand how things work on the job. The batch was slightly large at times, yet the hands-on focus and support made it well worth it.”
Verified Student
RB

Rajesh Banerjee

Penetration Tester

“WebAsha's Web Application Penetration Testing training turned a tough certification into an enjoyable learning experience. Hands-on practice on real lab systems built genuine confidence, not just theory. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. Easily a five-star experience that prepared me for both the exam and real work.”
Google Review
Career Roadmap

From your first class to placement

A step-by-step path from your first lesson to certification and a job offer.

Step 1 of 8

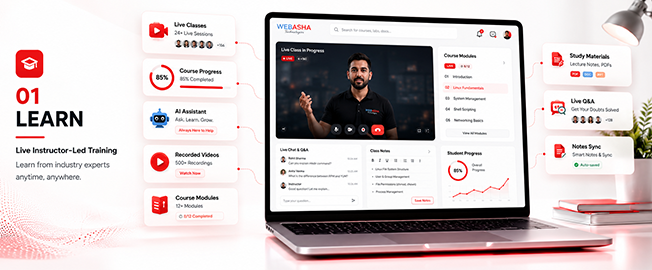
Learn

  • Live instructor-led training
  • Concept-first curriculum
  • Recorded sessions
Foundations & Core Concepts
Learn preview
Training Key Features

WAPT - Web Application Penetration Testing training key features

What you get from our WAPT - Web Application Penetration Testing course: a solid foundation in the basics and real-world, job-ready skills.

  • Post Training Support

  • Real Time Projects : 2

  • Certification & Job Assistance

  • Course Duration : 2 Months

  • Hands-on Training

  • Full Day Lab Access

Our cloud lab

WAPT - Web Application Penetration Testing cloud lab environment

Our Pune classroom practical lab

Program highlights

What learners get at WebAsha Technologies: practical IT training and the skills employers hire for.

Learning Experience

  • In-Depth Practical Training with Real-World Scenarios
  • Choose Between In-Person or Virtual Classes (Flexible Schedules)
  • Guidance from Seasoned IT Professionals
  • Complimentary Intro to Emerging Tech Topics
  • One-on-One Support for Clarifying Concepts
  • Regular Hands-On Exercises and Live Projects
  • Access to a Library of 150+ Training Videos for a Year

Career Development

  • Tailored Job Placement Support with Multiple Interviews
  • Custom Resume Crafting and Interview Coaching
  • Workshops on Professional Skills and Teamwork
  • Affordable Payment Plans with No Extra Fees
  • Help Preparing for International Certifications
  • Personal Career Guidance from Experts
  • Practice Interviews with Industry Leaders

Why choose WebAsha Technologies

Career-focused IT training with expert mentors, practical labs and globally recognized certifications, so you stand out when you apply for jobs.

Features Recommended
WebAsha Technologies
Other Institutes
Expert Trainers
10+ Years Experienced Industry Professionals
Freshers or Part-time Instructors
Course Curriculum
Updated & Industry-Relevant (Cybersecurity, Cloud, DevOps, Linux, AI/ML)
Basic or Outdated Content
Hands-on Learning
Real Projects, Labs & Case Studies
Theory-Focused, Limited Practical
Certifications
Globally Recognized (EC-Council, OffSec, Red Hat, AWS, Microsoft, etc.)
Generic or Unrecognized Certificates
Placement Support
100% Assistance + Resume & Interview Coaching
Limited or No Job Support
Flexible Learning
Classroom & Online Training Options
Rigid Timings, Mostly Classroom-Only
Learning Resources
Lifetime LMS Access, Study Materials, Recorded Sessions
Minimal or No Additional Resources
Batch Size
Small Groups with 1:1 Mentorship
Large, Crowded Batches

Upcoming batches & schedule

Monday, October 12, 2026

Online / Classroom
Weekday
8:00 AMIST
Enrollment OpenMax intake limit is 10

Monday, October 12, 2026

Online / Classroom
Weekday
6:30 PMIST
Enrollment OpenMax intake limit is 10

Monday, October 12, 2026

Online / Classroom
Fast Track
11:00 AMIST
Enrollment OpenMax intake limit is 10

Saturday, October 17, 2026

Online / Classroom
Weekend
10:00 AMIST
Enrollment OpenMax intake limit is 10

Monday, October 19, 2026

Online / Classroom
Weekday
8:00 AMIST
Enrollment OpenMax intake limit is 10

Monday, October 19, 2026

Online / Classroom
Weekday
6:30 PMIST
Enrollment OpenMax intake limit is 10

Saturday, October 24, 2026

Online / Classroom
Weekend
10:00 AMIST
Enrollment OpenMax intake limit is 10

Monday, October 26, 2026

Online / Classroom
Weekday
8:00 AMIST
Enrollment OpenMax intake limit is 10

Monday, October 26, 2026

Online / Classroom
Weekday
6:30 PMIST
Enrollment OpenMax intake limit is 10
Flexible Scheduling

Can't find a schedule that works?

Our counsellors can help you arrange a batch that fits your timing.

Course insight 1Course insight 2

WAPT (Web Application Penetration Testing) course training overview

Learn WAPT in our Classroom and Online WAPT (Web Application Penetration Testing) Training at WebAsha Technologies. The course is practical and aimed at getting you a job in the field.

Training Overview:

WAPT is a hands-on, job-oriented program in web application penetration testing. It covers the OWASP Top 10 and other web attacks: injection, XSS, authentication and access-control flaws, SSRF, file upload and business-logic attacks. You work with Burp Suite and related tools and learn to write a professional report.

Intended Audience:

The course suits aspiring web penetration testers, application-security analysts and bug-bounty hunters who want practical web security skills.

Topics Covered:

  • OWASP Top 10: The core web vulnerability classes.
  • Injection: SQL injection and command injection, with sqlmap.
  • XSS & CSRF: Attacks that run in the user's browser.
  • Auth & Session: Weak logins, sessions and tokens.
  • Access Control: IDOR and authorisation bypasses.
  • SSRF & Upload: Server-side request forgery and file upload attacks.
  • Business Logic: Flaws in how the application's workflow is designed.
  • Reporting: Write a professional report with recommended fixes.

Requirements:

You should have basic computer knowledge. Online participants need a stable internet connection and a laptop or desktop for the live labs.

Pre-Requisites:

You should have basic web and security awareness before WAPT. CEH-level knowledge or the Cyber Security Course gives you that.

Career Benefits:

Employers hire for web security skills. In India, WAPT professionals typically earn ₹5 LPA to ₹30+ LPA, and bug-bounty income can add to that.
Certification path

CategoryTools & components covered
ProxyBurp Suite
Injectionsqlmap
Reconffuf, gobuster, nikto
XSSXSS payloads
ScriptingPython, JavaScript
AnalysisBrowser dev tools
FuzzingWeb fuzzers
PlatformKali Linux

Curriculum WAPT - Web Application Penetration Testing

WAPT (Web Application Penetration Testing): course modules

1. Web Fundamentals & OWASP Top 10

The course starts with how web applications are built and where they usually break. The OWASP Top 10 is the map for the modules that follow.

  • Understand web architecture
  • Map the OWASP Top 10 to the weaknesses you will test for
  • Set up Kali Linux and Burp Suite as your testing platform
  • Inspect requests and responses with browser dev tools
2. Injection Attacks

Injection flaws let attacker input run as a database query or a system command. You exploit them by hand and with tooling.

  • Exploit SQL injection
  • Exploit command injection
  • Use sqlmap effectively
3. XSS, CSRF & Client-Side

This module covers attacks that target the user's browser.

  • Exploit cross-site scripting (XSS) with crafted payloads
  • Exploit cross-site request forgery (CSRF)
  • Chain client-side flaws
  • Read and write the JavaScript these attacks rely on
4. Authentication & Session Attacks

You test how an application identifies its users and keeps them logged in.

  • Break authentication
  • Attack sessions and tokens
  • Intercept and replay login traffic in Burp Suite
5. Access Control & IDOR

Access-control testing checks whether a user can reach data or functions meant for someone else.

  • Bypass authorization
  • Exploit insecure direct object references (IDOR)
  • Compare what different user roles can reach
6. SSRF, File Upload & Business Logic

Server-side flaws and mistakes in the application's own workflow are covered together here.

  • Exploit server-side request forgery (SSRF)
  • Attack file upload features
  • Attack business logic
  • Find hidden content with ffuf, gobuster and nikto
7. Reporting & Remediation

A penetration test ends with a report the client can act on.

  • Write professional reports
  • Recommend fixes
  • Describe each finding so that developers can reproduce it
8. WAPT Projects & Career Guidance

The last module puts the earlier ones together on full assessments and looks at what comes next.

  • Complete real assessments
  • Plan your certification path (WAHS, OffSec OSWA, eWPT)
  • Placement support from WebAsha

Download the complete course syllabus

Get the full curriculum, modules & exam details delivered to you instantly.

Meet our expert trainers

Learn from certified WAPT - Web Application Penetration Testing experts who work in the industry and teach with practical, real-world examples.

  • Simplified Guidance: Break down Linux concepts for beginners.
  • Hands-On Practice: Engage in labs for command-line and admin tasks.
  • Customized Support: Offer one-on-one help for your goals.
  • Career & Lab Aid: Assist with projects and exam prep.
  • Industry Knowledge: Draw from extensive Red Hat experience.
  • Certified Professionals: Hold RHCSA, RHCE credentials.
  • Real-World Application: Insights from enterprise Linux deployments.
  • Training Success: Over 1,000 students guided annually.
  • Corporate Links: Partnerships with IBM, Accenture, Wipro.
Free Skill Assessment

Self assessment

Test your skills with an online assessment exam and find out how ready you are for your certification.

  • Free mock test
  • Instant score report
  • Mapped to the certification
Learner taking an online skills assessment

WAPT (Web Application Penetration Testing): certification & career path

This WAPT program is a hands-on, job-oriented course that ends with a WebAsha completion certificate. It is vendor-neutral and is not tied to one exam. The course builds the full web-pentest skill set and prepares you for certifications such as WAHS, OffSec OSWA and eWPT. WebAsha Technologies in Pune adds real web application assessment labs and placement support to help you start a web penetration testing career. The same skills are useful for bug-bounty hunting.

  • Expert Trainers: Taught by experienced web pentesters.
  • Complete OWASP Coverage: The Top 10 and more advanced attacks.
  • Hands-On Labs: You exploit real web applications.
  • Industry Tools: Burp Suite, sqlmap and related tools.
  • Certification Path: Prepares you for WAHS, OSWA and eWPT.
  • Bug-Bounty Ready: The same skills are used in bug-bounty hunting.
  • Placement Support: Help with your resume and interviews.
  • Completion Certificate: A WebAsha WAPT certificate.

WAPT (Web Application Penetration Testing): certification & career path

AttributeDetails
CertificateWebAsha WAPT course completion certificate
FormatHands-on and job-oriented (labs and real assessments)
LevelIntermediate
Prepares ForWAHS, OffSec OSWA, eWPT and other web security certifications
CoverageOWASP Top 10 and advanced web attacks
PrerequisiteBasic web and security awareness
IncludesReal labs, assessments and placement support
ModeOnline or classroom

WAPT (Web Application Penetration Testing): certification & next steps

This WAPT program is a hands-on, job-oriented course that ends with a WebAsha completion certificate. It is vendor-neutral and is not tied to one exam. The course builds the full web-pentest skill set and prepares you for certifications such as WAHS, OffSec OSWA and eWPT. WebAsha Technologies in Pune adds real web application assessment labs and placement support to help you start a web penetration testing career. The same skills are useful for bug-bounty hunting.

Job roles and salary outlook after WAPT (Web Application Penetration Testing)

Web application security skills are in demand across India. The table shows typical roles and salary ranges for WAPT professionals, and bug-bounty income can add to them.

Job Title Primary Responsibilities Average Salary (INR)
Web Application Pentester Tests web applications for exploitable flaws. Fresher: ₹5-9 LPA
Experienced: ₹15-28 LPA
Application Security Analyst Analyses the security of web applications. Fresher: ₹5-8 LPA
Experienced: ₹14-26 LPA
Bug Bounty Hunter Finds web flaws and reports them to programme owners. Variable: ₹6-30+ LPA
Penetration Tester Assesses systems and exploits the weaknesses found. Fresher: ₹5-8 LPA
Experienced: ₹14-26 LPA
VAPT Engineer Runs vulnerability assessments and penetration tests. Fresher: ₹5-8 LPA
Experienced: ₹13-24 LPA
Security Consultant (Web) Advises clients on web security. Experienced: ₹14-28 LPA

Salaries vary with experience and skill. WAPT gives you practical ability you can show an employer.


Career benefits of WAPT (Web Application Penetration Testing)

WAPT builds the web application penetration testing skills that employers hire for, and the same skills are a way into bug bounty.

  • Job-Oriented: Practical training aimed at getting you hired.
  • Strong Demand: The salary table below lists the roles that use these skills.
  • Salaries: See the salary table below for typical ranges by role.
  • Hands-On Proof: You finish with real labs and projects to show.
  • Career Growth: A base for the specialised certifications named on this page.
  • Transferable: The method applies to any target you are asked to test.

Why choose WAPT (Web Application Penetration Testing) training at WebAsha Technologies in Pune

Learn WAPT (Web Application Penetration Testing) with WebAsha Technologies. Our program is hands-on and job-oriented, with expert trainers and placement support.

  • Expert Trainers: Taught by experienced web pentesters.
  • Complete OWASP Coverage: The Top 10 and more advanced attacks.
  • Hands-On Labs: You exploit real web applications.
  • Industry Tools: Burp Suite, sqlmap and related tools.
  • Certification Path: Prepares you for WAHS, OSWA and eWPT.
  • Bug-Bounty Ready: The same skills are used in bug-bounty hunting.
  • Placement Support: Help with your resume and interviews.
  • Completion Certificate: A WebAsha WAPT certificate.

Certification Path

EC-Council certification roadmap

EC-Council maps a clear path from foundations to expert-level offensive, defensive, forensic and leadership roles. Certifications we train for at WebAsha are linked below.

Not sure where to start or what to take next? Our mentors will map your cyber-security career path.

Plan My Cyber-Security Path
Program Highlights

What the program includes

Learning, career, certification and placement support in one program.

Learning benefits

  • Structured Curriculum
    Concept-first, job-ready syllabus
  • Hands-On Labs
    Practice every concept live
  • Expert-Led Sessions
    Learn from working professionals

Career benefits

  • Resume Building
    ATS-friendly, recruiter-ready
  • Mock Interviews
    Real interview simulations
  • Job Referrals
    Access to hiring partner network

Certification benefits

  • Globally Recognized
    Industry-standard certifications
  • Exam Preparation
    Targeted, exam-focused coaching
  • Practice Tests
    Unlimited mock assessments

Placement benefits

  • 500+ Hiring Partners
    Active recruiter network
  • Placement Drives
    Regular hiring opportunities
  • Salary Negotiation
    Guidance to maximize offers
Success Stories

Where our learners work now

Former students now working at leading companies, and how they got there.

CC

Chetan Chatterjee

Cyber Security Engineer · LTIMindtree

IT Support ExecutiveCyber Security Engineer
“Coming from a IT Support Executive background, switching felt risky, but WebAsha's Web Application Penetration Testing course gave me a clear path forward. The hands-on labs and live projects around ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab rebuilt my confidence from the ground up. I landed a Cyber Security Engineer position at LTIMindtree with a strong hike from 4.5 LPA to 9 LPA, and I owe it to WebAsha.”
IT Support Executive to Cyber Security Engineer at LTIMindtree
VN

Varun Naik

SOC Analyst · TCS

Non-IT ProfessionalSOC Analyst
“After a few years as a Non-IT Professional, I decided it was time for a real change and joined WebAsha's Web Application Penetration Testing training. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. I transitioned into a SOC Analyst role at TCS, nearly doubling my salary from 3 LPA to 6 LPA.”
How I became a SOC Analyst with WebAsha
AP

Ajay Pathan

Ethical Hacker · Amdocs

IT Support ExecutiveEthical Hacker
“I started out as a IT Support Executive and always wanted a stronger technical career, so I enrolled in the Web Application Penetration Testing program at WebAsha. The hands-on labs and live projects around ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab rebuilt my confidence from the ground up. The trainers were patient and genuinely industry-experienced, and the practical focus on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab made everything click. Within a few months I moved from IT Support Executive to Ethical Hacker at Amdocs, and my package grew from 3.5 LPA to 7 LPA.”
My journey: IT Support Executive to Ethical Hacker
TS

Tejas Shaikh

Security Analyst · Mphasis

“The Web Application Penetration Testing program at WebAsha genuinely lived up to its reputation. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. The cloud labs were available round the clock, so I could practise assignments whenever I had time. The real-world implementation examples helped me understand how things work on the job. The batch was slightly large at times, yet the hands-on focus and support made it well worth it.”
Cyber Security Certified
PM

Pallavi More

Penetration Tester · Birlasoft

Manual TesterPenetration Tester
“As a Manual Tester, I felt stuck in my growth, so I took the leap and signed up for Web Application Penetration Testing at WebAsha. Certification preparation, mock tests and repeated mock interviews prepared me for real technical rounds. Within a few months I moved from Manual Tester to Penetration Tester at Birlasoft, and my package grew from 6 LPA to 12 LPA.”
Manual Tester to Penetration Tester at Birlasoft
VT

Varun Thomas

Penetration Tester · Wipro

FresherPenetration Tester
“As a Fresher, I felt stuck in my growth, so I took the leap and signed up for Web Application Penetration Testing at WebAsha. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. I landed a Penetration Tester position at Wipro with a strong hike from 5 LPA to 11 LPA, and I owe it to WebAsha.”
Penetration Tester at Wipro - a career turnaround
MF

Mohit Fernandes

Cyber Security Engineer · Birlasoft

Diploma GraduateCyber Security Engineer
“I started out as a Diploma Graduate and always wanted a stronger technical career, so I enrolled in the Web Application Penetration Testing program at WebAsha. Working on real-world implementations helped me understand exactly how things run on the job. I transitioned into a Cyber Security Engineer role at Birlasoft, nearly doubling my salary from 4.5 LPA to 8.5 LPA.”
From Diploma Graduate to Cyber Security Engineer
VN

Vikas Nair

Ethical Hacker · Persistent Systems

Technical Support AssociateEthical Hacker
“My journey began as a Technical Support Associate with big ambitions, and the Web Application Penetration Testing program at WebAsha became the turning point. The placement team actively shared openings and coached me through resume building and every interview. I landed a Ethical Hacker position at Persistent Systems with a strong hike from 3.5 LPA to 6.5 LPA, and I owe it to WebAsha.”
Technical Support Associate to Ethical Hacker at Persistent Systems
NS

Neha Shaikh

Penetration Tester · Cognizant

Desktop Support EngineerPenetration Tester
“My journey began as a Desktop Support Engineer with big ambitions, and the Web Application Penetration Testing program at WebAsha became the turning point. The hands-on labs and live projects around ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab rebuilt my confidence from the ground up. The placement team actively shared openings and coached me through resume building and every interview. Within a few months I moved from Desktop Support Engineer to Penetration Tester at Cognizant, and my package grew from 2.4 LPA to 4.5 LPA.”
Desktop Support Engineer to Penetration Tester at Cognizant
Quick Summary

WAPT - Web Application Penetration Testing is a hands-on cyber security and ethical hacking training course by WebAsha Technologies, available online and in classroom with live projects, certification prep and placement support. It suits beginners and professionals, runs about 6 to 12 weeks, and leads to roles such as SOC Analyst, Penetration Tester, Security Analyst paying roughly 4.0 to 26.0 LPA.

Key takeaways

  • Master cyber security through hands-on, practical training.
  • Learn footprinting & reconnaissance and network scanning & enumeration.
  • Work on real-world projects and lab exercises.
  • Earn an industry-recognised certificate.
  • Get placement support for roles paying up to 26.0 LPA.

WAPT - Web Application Penetration Testing: WebAsha vs other options

FeatureWebAsha cyber securitySelf-studyGeneric online course
Live instructor-led trainingYesNoSometimes
Hands-on labs & real projectsYesLimitedLimited
Certification exam preparationYesSelf-managedVaries
Doubt-solving & mentorshipYesNoLimited
Placement assistanceYesNoRare
Industry-recognised certificateYesNoVaries

Last updated: 23 June 2026

WAPT - Web Application Penetration Testing FAQs

WAPT - Web Application Penetration Testing is a hands-on training program in cyber security and ethical hacking. It takes you from fundamentals to working skills through live sessions, lab practice and real projects, with an industry-recognised certificate and placement support.

Aspiring ethical hackers and penetration testers IT and network administrators moving into security Fresh graduates targeting a SOC/security career Professionals preparing for EC-Council / OffSec certifications

Basic networking (TCP/IP) understanding Familiarity with Windows and Linux basics Curiosity about how systems are attacked and defended

You will build practical skills including footprinting & reconnaissance, network scanning & enumeration, system hacking & privilege escalation, web application attacks (owasp), malware & social engineering analysis and more, applied through hands-on labs and real projects.

The WAPT - Web Application Penetration Testing syllabus spans cyber security and ethical hacking, from core concepts to advanced modules, each reinforced with lab exercises and a capstone-style project.

WAPT - Web Application Penetration Testing typically runs about 6 to 12 weeks depending on the track (weekday or weekend), plus lab and project time. Fast-track and extended options are available. Ask for the current batch schedule.

WAPT - Web Application Penetration Testing fees depend on the mode (classroom or live-online) and track, and WebAsha Technologies offers flexible / no-cost EMI options. Request the latest fee details and any running offers from the enquiry form.

Both. You can take WAPT - Web Application Penetration Testing as a live-online program or attend classroom sessions, with the same syllabus, hands-on labs and trainers in either mode.

Yes. WAPT - Web Application Penetration Testing runs in weekday, weekend and evening batches so students and working professionals can train without disturbing their schedule.

Yes. WAPT - Web Application Penetration Testing starts from fundamentals so beginners can follow along, while the advanced modules add depth for experienced learners.

Absolutely. Many learners are working professionals. Flexible weekend, evening and live-online WAPT - Web Application Penetration Testing batches let you upskill without a career break.

Yes. WAPT - Web Application Penetration Testing is project-driven. You practise in real labs and build live projects in cyber security and ethical hacking alongside the theory, so you finish interview-ready.

After completing WAPT - Web Application Penetration Testing you can target roles such as SOC Analyst, Penetration Tester, Security Analyst, Ethical Hacker, with senior packages reaching around 26.0 LPA depending on experience and location.

Cyber security and ethical hacking roles typically start around 4.0 LPA for freshers and rise to about 26.0 LPA for experienced professionals. Actual packages depend on your skills, role and employer.

Yes. Cyber security and ethical hacking skills are in strong, growing demand across IT services, product companies and startups, offering clear career progression and rising salaries for certified professionals.

Trained cyber security professionals are hired by IT-services majors, global capability centres, product companies and startups. Organisations across the industry actively recruit for cyber security and ethical hacking.

Yes. WebAsha Technologies provides resume building, mock interviews and referrals to hiring partners as part of dedicated placement support. Outcomes depend on your skills and effort.

WAPT - Web Application Penetration Testing is taught by experienced, industry-certified trainers who bring real project experience into the classroom, so you learn current, job-relevant practices.

Yes. You receive an industry-recognised WebAsha training certificate, and the course also prepares you for the relevant official certification exam.

Yes. Alongside job skills, WAPT - Web Application Penetration Testing includes structured exam preparation, with practice tests and guidance for the recognised cyber security certification employers look for.

Yes. You can book a free demo session for WAPT - Web Application Penetration Testing to meet the trainer and experience the teaching style before you enroll.

WebAsha combines hands-on labs, certified trainers, live projects, certification prep and dedicated placement support. It is a practical, job-focused route into cyber security and ethical hacking.

Click Enroll Now, request a callback, or message our team on WhatsApp to get the latest batch schedule, fees and available offers.

Keep Exploring

Related courses

Take the next step in your IT career

Join thousands of learners who upskilled and got placed with WebAsha Technologies.