OSCP+ | Penetration Testing with Kali Linux (PEN-200) in Hyderabad, IndiaINR

OSCP+ | Penetration Testing with Kali Linux (PEN-200) Live Online in Hyderabad

Overall rating: 4.9 based on 3,795 reviewsG 4.9/5f 4.9/5

Live instructor-led online classes for Hyderabad learners

The OSCP+ | Penetration Testing with Kali Linux (PEN-200) training at WebAsha Technologies in Hyderabad prepares you for OffSec's PEN-200: Penetration Testing with Kali Linux course and the exam that follows it.

OffSec's current syllabus has 19 modules. They cover information gathering, vulnerability scanning, web application and client-side attacks, locating and fixing public exploits, antivirus evasion, password attacks, Windows and Linux privilege escalation, tunneling, the Metasploit Framework and three Active Directory modules.

The exam is a proctored 23-hour-45-minute hands-on test, and you then have 24 hours to write and upload the report. Since the 2024 update, a pass earns both the OSCP, which does not expire, and the OSCP+, which is valid for three years. WebAsha's offensive-security trainers and cyber-range labs give you practice on similar targets, and the course keeps to OffSec's 'Try Harder' approach.
Duration:40 Hrs (Weekdays & Weekend Session)
Mode:Live Instructor-Led Online Training
Certification:Prepares for OffSec OSCP / OSCP+ (PEN-200)
Institute:WebAsha Technologies
Includes:Hands-On Cyber-Range Labs & Attendance Certificate
Trusted By

1000+ leading universities and companies

Our learners are hired by technology, IT services and consulting companies.

  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
Recent Placements Testimonials

OSCP+ | Penetration Testing with Kali Linux (PEN-200) recent reviews

Our learners talk about how the program changed their careers.

Verified Reviews

Student reviews and success stories

Real feedback from learners now placed across top technology and consulting firms.

kavita-more.webp

Kavita More

Penetration Tester · Wipro

“Completing the OSCP Penetration Testing with Kali Linux training at WebAsha was a turning point for me. Each module built logically, and the coverage of ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab was thorough and current. The learning experience was structured, practical and paced just right for working professionals. The placement assistance team actively shared openings and guided me until I was placed. A big thank you to the trainers and team for such a rewarding learning experience.”
Facebook Review
komal-shaikh.webp

Komal Shaikh

Security Analyst · Tech Mahindra

“I joined WebAsha for OSCP Penetration Testing with Kali Linux to level up my skills, and the experience exceeded my expectations. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. The cloud labs were available round the clock, so I could practise assignments whenever I had time. Minor scheduling tweaks aside, the training quality and lab practice were genuinely excellent.”
Verified Student
farhan-das.webp

Farhan Das

Security Analyst · Vodafone Idea

“Enrolling in OSCP Penetration Testing with Kali Linux at WebAsha is one of the best career decisions I have made. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. Live projects gave me the confidence to apply what I learned in a real environment. The batch was slightly large at times, yet the hands-on focus and support made it well worth it.”
Verified Student
riya-iyer.webp

Riya Iyer

SOC Analyst · Vodafone Idea

“I recently finished the OSCP Penetration Testing with Kali Linux course at WebAsha Technologies and it was worth every minute. Each module built logically, and the coverage of ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab was thorough and current. The mock interviews and interview preparation sharpened me for real technical rounds. The knowledge and confidence I gained here continue to help me every day at work.”
Verified Student
sachin-ansari.webp

Sachin Ansari

SOC Analyst · Oracle

“I joined WebAsha for OSCP Penetration Testing with Kali Linux to level up my skills, and the experience exceeded my expectations. Flexible batch timings let me attend alongside my job without any stress. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. Live projects gave me the confidence to apply what I learned in a real environment. The certification preparation and mock tests made the actual exam feel straightforward. If you want practical, job-ready skills in OSCP Penetration Testing with Kali Linux, WebAsha is the place to be.”
Verified Student
rohan-trivedi.webp

Rohan Trivedi

Cyber Security Engineer · Mphasis

“Completing the OSCP Penetration Testing with Kali Linux training at WebAsha was a turning point for me. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. Hands-on practice on real lab systems built genuine confidence, not just theory. The placement assistance team actively shared openings and guided me until I was placed. Doubt-clearing sessions ran even after class hours, which I really appreciated. The knowledge and confidence I gained here continue to help me every day at work.”
Google Review
riya-joshi.webp

Riya Joshi

Ethical Hacker

“Completing the OSCP Penetration Testing with Kali Linux training at WebAsha was a turning point for me. The cloud labs were available round the clock, so I could practise assignments whenever I had time. We worked hands-on with ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab, which made every concept stick. The knowledge and confidence I gained here continue to help me every day at work.”
Facebook Review
sachin-naidu.webp

Sachin Naidu

Security Analyst · Vodafone Idea

“WebAsha's OSCP Penetration Testing with Kali Linux training turned a tough certification into an enjoyable learning experience. The learning experience was structured, practical and paced just right for working professionals. Each module built logically, and the coverage of ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab was thorough and current. The real-world implementation examples helped me understand how things work on the job. A couple of sessions felt a little fast, but overall a strong, practical program I recommend.”
Verified Student
arjun-gupta.webp

Arjun Gupta

Cyber Security Engineer · Tech Mahindra

“WebAsha's OSCP Penetration Testing with Kali Linux training turned a tough certification into an enjoyable learning experience. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. The mock interviews and interview preparation sharpened me for real technical rounds. Easily a five-star experience that prepared me for both the exam and real work.”
Verified Student
Career Roadmap

From your first class to placement

A step-by-step path from your first lesson to certification and a job offer.

Step 1 of 8

Learn

  • Live instructor-led training
  • Concept-first curriculum
  • Recorded sessions
Foundations & Core Concepts
Learn preview
Training Key Features

OSCP+ | Penetration Testing with Kali Linux (PEN-200) training key features

What you get from our OSCP+ | Penetration Testing with Kali Linux (PEN-200) course: a solid foundation in the basics and real-world, skills you can use at work.

  • Post Training Support

  • Real Time Projects : 2

  • Certification & Job Assistance

  • Course Duration : 2 Months

  • Hands-on Training

  • Full Day Lab Access

Our cloud lab

OSCP+ | Penetration Testing with Kali Linux (PEN-200) cloud lab environment

Our practical lab

Program highlights

What learners get at WebAsha Technologies: practical IT training and the skills employers hire for.

Learning Experience

  • In-Depth Practical Training with Real-World Scenarios
  • Choose Between In-Person or Virtual Classes (Flexible Schedules)
  • Guidance from Seasoned IT Professionals
  • Complimentary Intro to Emerging Tech Topics
  • One-on-One Support for Clarifying Concepts
  • Regular Hands-On Exercises and Live Projects
  • Access to a Library of 150+ Training Videos for a Year

Career Development

  • Tailored Job Placement Support with Multiple Interviews
  • Custom Resume Crafting and Interview Coaching
  • Workshops on Professional Skills and Teamwork
  • Affordable Payment Plans with No Extra Fees
  • Help Preparing for International Certifications
  • Personal Career Guidance from Experts
  • Practice Interviews with Industry Leaders

Why choose WebAsha Technologies

Career-focused IT training with expert mentors, practical labs and vendor certifications, so you stand out when you apply for jobs.

Features Recommended
WebAsha Technologies
Other Institutes
Expert Trainers
10+ Years Experienced Industry Professionals
Freshers or Part-time Instructors
Course Curriculum
Updated for Current Tools (Cybersecurity, Cloud, DevOps, Linux, AI/ML)
Basic or Outdated Content
Hands-on Learning
Real Projects, Labs & Case Studies
Theory-Focused, Limited Practical
Certifications
Vendor-Issued (EC-Council, OffSec, Red Hat, AWS, Microsoft, etc.)
Generic or Unrecognized Certificates
Placement Support
100% Assistance + Resume & Interview Coaching
Limited or No Job Support
Flexible Learning
Classroom & Online Training Options
Rigid Timings, Mostly Classroom-Only
Learning Resources
Lifetime LMS Access, Study Materials, Recorded Sessions
Minimal or No Additional Resources
Batch Size
Small Groups with 1:1 Mentorship
Large, Crowded Batches

Upcoming batches & schedule

Wednesday, October 21, 2026

Live Online
Weekday
6:30 PMIST
Enrollment Closed
Enrollment Closed

Saturday, October 24, 2026

Live Online
Weekend
10:00 AMIST
Enrollment OpenMax intake limit is 10

Wednesday, October 28, 2026

Live Online
Weekday
6:30 PMIST
Enrollment OpenMax intake limit is 10

Wednesday, November 4, 2026

Live Online
Weekday
8:00 AMIST
Enrollment OpenMax intake limit is 10
Flexible Scheduling

Can't find a schedule that works?

Our counsellors can help you arrange a batch that fits your timing.

Course insight 1Course insight 2

OSCP+ | Penetration Testing with Kali Linux (PEN-200) course training overview

Learn Penetration Testing with Kali Linux (PEN-200) in our classroom and online OSCP+ training at WebAsha Technologies. You practise the hands-on skills that the OSCP+ exam tests.

Training overview:

OSCP+ is OffSec's penetration-testing certification, and PEN-200 is the course that prepares you for it. The 19 modules in OffSec's current syllabus run from information gathering and vulnerability scanning, through web, client-side and password attacks, to privilege escalation, tunneling and Active Directory. The exam is a proctored practical test in a 24-hour slot.

Intended audience:

This course suits aspiring penetration testers, security analysts, and SOC and IT professionals moving into offensive security. It also suits anyone preparing for the OSCP+ exam.

Topics covered:

  • Information gathering: Passive information gathering, port scanning and service enumeration.
  • Web application attacks: Directory traversal, file inclusion, file upload flaws, command injection and SQL injection.
  • Client-side attacks: Target reconnaissance and attacks that run on the user's own software.
  • Exploitation: Locating, checking and fixing public exploits.
  • Privilege escalation: Windows and Linux systems.
  • Pivoting & tunneling: Reaching internal networks through tunnels.
  • Active Directory: Enumeration, authentication attacks and lateral movement.
  • Reporting: Writing a penetration-test report.

Requirements:

You should be comfortable with Linux and the command line. Online participants need a stable internet connection and a laptop or desktop for the live labs.

Prerequisites:

OffSec sets no formal prerequisites. It strongly recommends a solid understanding of TCP/IP networking, reasonable Windows and Linux administration experience, and familiarity with basic Bash or Python scripting.

Career benefits:

OSCP can lead to senior offensive-security roles. In India, OSCP-certified penetration testers typically earn ₹6 LPA to ₹38+ LPA as they gain experience.
Certification path

CategoryTools & components covered
ReconNmap, Gobuster, feroxbuster
WebBurp Suite, sqlmap, wfuzz
ExploitationMetasploit, searchsploit, msfvenom
PasswordsHydra, John, Hashcat
ADBloodHound, CrackMapExec, impacket
TunnelingSSH, chisel, ligolo
Post-ExploitWinPEAS, LinPEAS, mimikatz
PlatformKali Linux

Curriculum OSCP+ | Penetration Testing with Kali Linux (PEN-200)

Penetration Testing with Kali Linux (PEN-200) (OSCP+): 19 course modules

1. Introduction to Cybersecurity

The opening module covers the core concepts, technologies and good practice of cyber security that the later modules build on.

  • How offensive and defensive security relate to each other
  • Threats and threat actors, and the difference between risks, threats, vulnerabilities and exploits
  • The CIA triad: confidentiality, integrity and availability
  • Security principles, controls and strategies, such as layered defence and restricted privileges
  • Laws, regulations, standards and frameworks, and career opportunities in the field
2. Report Writing for Penetration Testers

You learn to write clear reports that set out each vulnerability, its likely impact and the steps to fix it.

  • Taking notes during an engagement and choosing a note-taking tool
  • Capturing screenshots as evidence
  • Writing an executive summary and a technical summary
  • Describing technical findings and recommendations
  • When to use appendices, resources and references
3. Information Gathering

This module is about mapping a target before you attack it, with tools such as Nmap and Shodan.

  • The stages of a penetration test and where information gathering fits in each
  • Passive information gathering and OSINT, including web server and DNS sources
  • Port scanning with Netcat and Nmap
  • DNS, SMB, SMTP and SNMP enumeration
  • Living-off-the-land techniques
4. Vulnerability Scanning

Scanners such as Nessus and OpenVAS find known vulnerabilities in networks, applications and systems, which shortens the early part of a test.

  • How vulnerability scanning works, the types of scan and what to consider before running one
  • Installing Nessus, configuring a scan and working with the results
  • Authenticated scans and Nessus plugins
  • Lightweight scanning with the Nmap Scripting Engine (NSE), including custom NSE scripts
5. Introduction to Web Applications

How web applications work, the technologies underneath them and the design weaknesses that give attackers a way in.

  • Web application assessment methodology and the OWASP Top 10
  • Enumeration tools and the Burp Suite proxy
  • Inspecting headers, cookies and source code, and testing APIs
  • Cross-site scripting (XSS): the types, basic exploitation and privilege escalation through XSS
6. Common Web Application Attacks

The techniques behind common web attacks, mainly injection flaws, and the ways to stop them.

  • Directory traversal with absolute and relative paths and encoded characters
  • Local and remote file inclusion (LFI and RFI), and PHP wrappers
  • Finding and exploiting file upload vulnerabilities
  • OS command injection used to gain system access
7. SQL Injection Attacks

Manipulating databases through SQL injection to extract sensitive data, compromise back-end systems and escalate privileges.

  • SQL theory, database types and differences in SQL syntax
  • Identifying SQL injection by hand
  • UNION-based, error-based and blind SQLi payloads
  • Code execution through MSSQL xp_cmdshell
  • Automating injection with sqlmap
8. Client-Side Attacks

Attacks on the software that users run themselves, used to compromise their systems and gain access.

  • Target reconnaissance and client fingerprinting
  • Microsoft Office attacks built on Word macros
  • Abusing Windows library files and shortcuts to get code execution
9. Locating Public Exploits

Finding reliable public exploits, judging what they do and using them responsibly in a test.

  • The risk of running untrusted exploit code, and why you read it before you run it
  • Online exploit resources and Google search operators
  • Offline resources: exploit frameworks, SearchSploit and Nmap NSE scripts
  • Enumerating a target, choosing a suitable exploit and using it to get a shell
10. Fixing Exploits

Adapting and customising existing exploits so that they work against the system in front of you.

  • Buffer overflow theory at a high level
  • Cross-compiling binaries
  • Modifying and updating memory corruption exploits
  • Fixing web application exploits and troubleshooting common problems with them
11. Antivirus Evasion

How antivirus software detects payloads, and how testers disguise exploits and payloads to behave as a real attacker would.

  • Known and unknown threats
  • The key components of antivirus software and its detection engines
  • Good practice for testing evasion
  • Evading antivirus by hand and with automated tools
12. Password Attacks

Finding weak authentication by attacking network logins and cracking captured hashes.

  • Attacking SSH and RDP logins and HTTP POST login forms
  • Password cracking fundamentals and mutating wordlists
  • Attacking password manager key files and SSH private key passphrases
  • Obtaining, cracking and passing NTLM hashes
  • Cracking and relaying Net-NTLMv2 hashes
13. Windows Privilege Escalation

Finding and exploiting misconfigurations and vulnerabilities in Windows to gain administrator-level access.

  • Windows privileges and access control mechanisms
  • Situational awareness and searching a system for sensitive information, including what PowerShell leaves behind
  • Automated enumeration tools
  • Hijacking service binaries and DLLs, and abusing unquoted service paths
  • Scheduled tasks, and abusing privileges to run code as a privileged account
14. Linux Privilege Escalation

Escalating privileges on Linux systems until you have root access.

  • Files and user privileges on Linux, with manual and automated enumeration
  • Harvesting credentials from user history files and system trails
  • Abusing insecure cron jobs and file permissions
  • SUID programs, capabilities and sudo permissions
  • Checking the kernel for known vulnerabilities
15. Advanced Tunneling

Tunneling protocols and techniques for pivoting through a network and getting traffic past inspection.

  • Tunneling through deep packet inspection
  • HTTP tunneling with Chisel
  • DNS tunneling with dnscat
16. The Metasploit Framework

Using Metasploit for exploitation, payload generation and post-exploitation work.

  • Setting up and navigating Metasploit, with its auxiliary and exploit modules
  • Staged and non-staged payloads, Meterpreter and executable payloads
  • Post-exploitation with Meterpreter and the post-exploitation modules
  • Pivoting with Metasploit
  • Automating tasks with resource scripts
17. Active Directory: Introduction and Enumeration

The structure of Active Directory, and how to enumerate users, groups, trusts and sensitive configuration to find attack paths with tools such as BloodHound and PowerView.

  • Manual enumeration with legacy Windows tools, PowerShell and .NET
  • Operating systems, permissions and logged-on users
  • Service Principal Names, object permissions and domain shares
  • Collecting domain data with SharpHound and analysing it in BloodHound
18. Attacking Active Directory Authentication

Exploiting weaknesses in Active Directory authentication (Kerberos and NTLM) to compromise credentials and gain access.

  • How NTLM and Kerberos authentication work, and cached AD credentials
  • Password attacks that yield valid user credentials
  • Abusing user account options and the Kerberos SPN mechanism
  • Forging service tickets
  • Impersonating a domain controller to retrieve domain user credentials
19. Lateral Movement in Active Directory

Moving from host to host inside a domain and extending your control after the first compromise.

  • WMI, WinRS and WinRM techniques
  • Lateral movement with PsExec
  • Pass the Hash and Overpass the Hash
  • Abusing DCOM
  • Persistence with golden tickets and shadow copies

Download the complete course syllabus

Get the full curriculum, modules & exam details delivered to you instantly.

Meet our expert trainers

Learn from certified OSCP+ | Penetration Testing with Kali Linux (PEN-200) experts who work in the industry and teach with practical, real-world examples.

  • Simplified Guidance: Break down Linux concepts for beginners.
  • Hands-On Practice: Engage in labs for command-line and admin tasks.
  • Customized Support: Offer one-on-one help for your goals.
  • Career & Lab Aid: Assist with projects and exam prep.
  • Industry Knowledge: Draw from extensive Red Hat experience.
  • Certified Professionals: Hold RHCSA, RHCE credentials.
  • Real-World Application: Insights from enterprise Linux deployments.
  • Training Success: Over 1,000 students guided annually.
  • Corporate Links: Partnerships with IBM, Accenture, Wipro.
Free Skill Assessment

Self assessment

Test your skills with an online assessment exam and find out how ready you are for your certification.

  • Free mock test
  • Instant score report
  • Mapped to the certification
Learner taking an online skills assessment

OSCP+ | Penetration Testing with Kali Linux (PEN-200) Certification Bootcamp

Penetration Testing with Kali Linux (PEN-200) is OffSec's hands-on penetration-testing course. It prepares you for the OSCP+ exam, a 23-hour-45-minute practical test scored out of 100 points with a pass mark of 70. A pass earns both the OSCP, which does not expire, and the renewable OSCP+.

  • Expert Offensive Trainers: Learn from working penetration testers.
  • Cyber-Range Labs: Practise the full attack chain yourself.
  • Exam-Realistic Practice: Challenge networks modelled on the OSCP+ exam.
  • Full AD Coverage: Assumed-breach Active Directory attacks.
  • Report Writing: Practise writing the exam report.
  • Try Harder Mindset: Learn to work through hard problems on your own.
  • Flexible Batches: Weekday/weekend and online/classroom options.
  • Placement Support: Resume building and interview help.

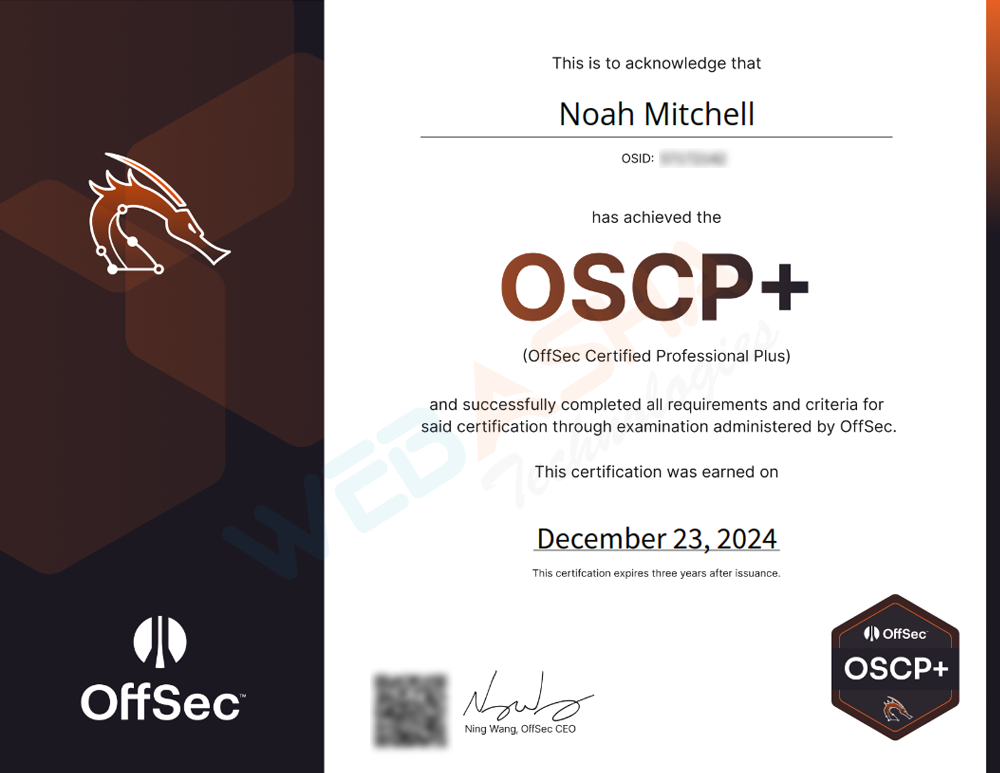
Our Recent Certified Candidates

  • Certified candidate
  • Certified candidate
  • Certified candidate
  • Certified candidate
  • Certified candidate
  • Certified candidate
  • Certified candidate
  • Certified candidate
  • Certified candidate

OSCP+ Exam Details & Format

AttributeDetails
CoursePEN-200: Penetration Testing with Kali Linux (PWK)
CertificationsOSCP (no expiry date) and OSCP+ (expires after 3 years, renewable)
Exam FormatProctored, hands-on penetration test over a private VPN
Hands-On Time23 hours 45 minutes
Reporting TimeA further 24 hours to write and upload the report
Total Points100 points
Structure3 standalone machines (20 points each, 60 in total) and 1 Active Directory set of 3 machines (40 points)
Active DirectoryStarts from an assumed breach with a supplied username and password; the three machines are worth 10, 10 and 20 points
Passing Score70 of 100 points
Bonus PointsNone; the maximum score is 100 (bonus points were removed from 1 November 2024)
ValidityOSCP has no expiry date; OSCP+ expires 3 years after issue unless renewed by a recertification exam, a qualifying OffSec exam or OffSec's CPE programme

OSCP+ Exam Passing Criteria

The OSCP+ exam is a proctored, hands-on penetration test lasting 23 hours 45 minutes. When it ends you have a separate 24 hours to write and upload a professional report. The exam is scored out of 100 points: three standalone machines worth 20 points each (60 in total) and one Active Directory set of three machines worth 40 points. You need 70 points to pass. Since 1 November 2024 the Active Directory set starts from an assumed-breach position with a username and password supplied, its three machines are scored separately (10, 10 and 20 points), and there are no bonus points. A pass earns the OSCP, which does not expire, and the OSCP+, which expires after three years unless you renew it. WebAsha's labs follow the same format, so you practise under exam-like conditions.

Job Roles and Salary Outlook After OSCP+

OSCP is a widely respected offensive-security certification, and OSCP-certified testers are paid well across India's cyber-security industry.

Job Title Primary Responsibilities Average Salary (INR)
Penetration Tester Test systems and applications for weaknesses. Fresher: ₹6-10 LPA
Experienced: ₹16-32 LPA
Security Analyst (Offensive) Assess and report on security posture. Fresher: ₹5-9 LPA
Experienced: ₹14-28 LPA
Red Team Operator Simulate attacks the way a real adversary would. Experienced: ₹18-38 LPA
VAPT Consultant Deliver vulnerability assessment and pen-test engagements. Fresher: ₹6-10 LPA
Experienced: ₹15-30 LPA
Security Consultant Advise clients on offensive security. Experienced: ₹16-34 LPA
Application Security Engineer Find and fix flaws in software. Fresher: ₹6-10 LPA
Experienced: ₹16-32 LPA

Salaries vary with skill and experience. OSCP+ shows employers that you have passed a hands-on exam.

Career Benefits of OSCP+

OSCP shows that you can break into systems under exam conditions, and hiring managers use it to judge hands-on penetration testers.

  • Proven Skill: The exam is practical, so a pass shows you can do the work.
  • Strong Demand: The job roles listed on this page all call for these skills.
  • Salaries: The salary table on this page gives typical ranges by role.
  • Globally Respected: Employers around the world recognise OffSec certifications.
  • Career Growth: Leads to both offensive and defensive security roles.
  • Outlook: Hands-on security skills stay useful as tools change.

Why Choose OSCP+ Training at WebAsha Technologies in Hyderabad

Prepare for OSCP+ with WebAsha Technologies, an OffSec training partner. Our programme is built around the hands-on OSCP+ exam.

  • Expert Offensive Trainers: Learn from working penetration testers.
  • Cyber-Range Labs: Practise the full attack chain yourself.
  • Exam-Realistic Practice: Challenge networks modelled on the OSCP+ exam.
  • Full AD Coverage: Assumed-breach Active Directory attacks.
  • Report Writing: Practise writing the exam report.
  • Try Harder Mindset: Learn to work through hard problems on your own.
  • Flexible Batches: Weekday/weekend and online/classroom options.
  • Placement Support: Resume building and interview help.

Learning from Hyderabad

Cyber Security for learners in Hyderabad, Telangana, India

About Hyderabad

Telangana's capital has grown from a historic pearl and trading city into one of India's largest technology centres, with global capability centres of major US tech firms clustered in its western suburbs. It is also a leading base for bulk drug and vaccine manufacturing. The GCCs in HITEC City and Nanakramguda run security operations, identity and cloud security programmes for their parent companies, and Genome Valley firms must guard regulated research and manufacturing data.

Who learns from Hyderabad

Engineering graduates from Osmania- and JNTU Hyderabad-affiliated colleges make up a large share, alongside testing and support staff in Madhapur and Gachibowli who want to move into security or cloud engineering. IT teams at pharma companies handling validated systems also look for compliance-minded security skills.

Attending online

Getting from Kukatpally, Uppal or Secunderabad to the Financial District at peak hour means crawling through the Biodiversity and Mindspace junctions, so most working learners would rather log in from home after the day ends. WebAsha's live classes are in the same IST timezone, with recordings for nights when a GCC release call runs late.

Cyber Security career scope in Hyderabad

Cyber Security jobs in Hyderabad

Security work in Hyderabad sits in two very different places: the security operations, identity and cloud-security teams that GCCs in HITEC City and Nanakramguda run for their parent companies, and the validated, audit-heavy systems at Dr. Reddy's Laboratories and Bharat Biotech in Genome Valley. Graduates of Osmania University and JNTU Hyderabad-affiliated colleges usually enter through SOC analyst or IT audit roles, while IIIT Hyderabad and University of Hyderabad students tend to aim at product security.

A sensible Hyderabad path starts with networking and Linux, moves to CompTIA Security+ as a baseline and then to CEH for offensive testing; pharma IT staff gain most by pairing that with compliance and access-control practice. Testers at Madhapur firms who want to switch can join an evening IST batch after logging off, and anyone pulled into a US-overlap release call can watch the recording and finish labs on the 24x7 environment before the next class.

For students & freshers in Hyderabad

Hyderabad's fresher market is crowded: GCC drives in Gachibowli and HITEC City draw final-year students from Osmania University, JNTU Hyderabad-affiliated colleges and the University of Hyderabad at the same time, so a transcript alone rarely separates candidates. WebAsha's job-oriented programs and online internships let a JNTU or Osmania final-year student build lab work that shows up in a HITEC City interview, such as a hardened Linux server, a small AWS deployment or a SOC alert investigation.

Classes run live in IST evenings after college, recordings cover days lost to semester exams, and the 24x7 labs suit students who study late in Kukatpally or Secunderabad hostels. Once the project work is ready, the placement-guarantee program helps target GCC, IT services and pharma IT openings, and students who want startup exposure can look at companies incubated at T-Hub.

Tech community in Hyderabad

Meetups, chapters and events near you

Hyderabad has one of the deeper security communities in the country. The OWASP Hyderabad chapter holds regular meetings on application security, and null Hyderabad, the local chapter of the null open security community, runs monthly meetups with talks from practitioners. On the developer side, GDG on Campus chapters at colleges such as VNR Vignana Jyothi and MLR Institute of Technology run workshops and study sessions.

If you are doing an online cybersecurity course from Hyderabad, go to a null meetup early on. Hearing someone explain a real finding makes the theory click, and many regulars started out just as you are. OWASP sessions help with web testing skills. Over time, presenting a short talk yourself is one of the best ways to get noticed by local hiring teams.

Independent community groups, listed for reference. They are not run by or affiliated with WebAsha.
Local Economy

Hyderabad's industries & employers

Sectors

IT services and global capability centres Pharmaceuticals and vaccines Life sciences research Banking and financial operations

Districts

HITEC City Gachibowli Financial District Madhapur Nanakramguda Genome Valley

Employers

Microsoft Google Amazon Deloitte Dr. Reddy's Laboratories Bharat Biotech

Context only; no affiliation implied.

Colleges

University of Hyderabad IIT Hyderabad IIIT Hyderabad Osmania University

OSCP+ | Penetration Testing with Kali Linux (PEN-200) for other cities

Program Highlights

What the program includes

Learning, career, certification and placement support in one program.

Learning benefits

  • Structured Curriculum
    Concept-first, job-ready syllabus
  • Hands-On Labs
    Practice every concept live
  • Expert-Led Sessions
    Learn from working professionals

Career benefits

  • Resume Building
    ATS-friendly, recruiter-ready
  • Mock Interviews
    Real interview simulations
  • Job Referrals
    Access to hiring partner network

Certification benefits

  • Globally Recognized
    Industry-standard certifications
  • Exam Preparation
    Targeted, exam-focused coaching
  • Practice Tests
    Unlimited mock assessments

Placement benefits

  • 500+ Hiring Partners
    Active recruiter network
  • Placement Drives
    Regular hiring opportunities
  • Salary Negotiation
    Guidance to maximize offers
Success Stories

Placement success stories

Starting your first IT job or changing direction? Explore the career paths below and think about what you want from your next role. Our team can help you plan the training and preparation to work towards it.

farhan-das.webp

Farhan Das

Security Analyst · Vodafone Idea

“Enrolling in OSCP Penetration Testing with Kali Linux at WebAsha is one of the best career decisions I have made. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. Live projects gave me the confidence to apply what I learned in a real environment. The batch was slightly large at times, yet the hands-on focus and support made it well worth it.”
OSCP Certified
rahul-pathan.webp

Rahul Pathan

Security Analyst · NTT Data

Manual TesterSecurity Analyst
“I started out as a Manual Tester and always wanted a stronger technical career, so I enrolled in the OSCP Penetration Testing with Kali Linux program at WebAsha. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. The hands-on labs and live projects around ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab rebuilt my confidence from the ground up. I transitioned into a Security Analyst role at NTT Data, nearly doubling my salary from 5 LPA to 11.5 LPA.”
My journey: Manual Tester to Security Analyst
SK

Sagar Kapoor

Penetration Tester · IBM

Final-Year StudentPenetration Tester
“Coming from a Final-Year Student background, switching felt risky, but WebAsha's OSCP Penetration Testing with Kali Linux course gave me a clear path forward. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. Within a few months I moved from Final-Year Student to Penetration Tester at IBM, and my package grew from 6 LPA to 11 LPA.”
My journey: Final-Year Student to Penetration Tester
nikhil-mehta.webp

Nikhil Mehta

Ethical Hacker · Birlasoft

Junior DeveloperEthical Hacker
“After a few years as a Junior Developer, I decided it was time for a real change and joined WebAsha's OSCP Penetration Testing with Kali Linux training. The trainers were patient and genuinely industry-experienced, and the practical focus on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab made everything click. Certification preparation, mock tests and repeated mock interviews prepared me for real technical rounds. I landed a Ethical Hacker position at Birlasoft with a strong hike from 5 LPA to 9 LPA, and I owe it to WebAsha.”
From Junior Developer to Ethical Hacker
sachin-ansari.webp

Sachin Ansari

SOC Analyst · Oracle

“I joined WebAsha for OSCP Penetration Testing with Kali Linux to level up my skills, and the experience exceeded my expectations. Flexible batch timings let me attend alongside my job without any stress. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. Live projects gave me the confidence to apply what I learned in a real environment. The certification preparation and mock tests made the actual exam feel straightforward. If you want practical, job-ready skills in OSCP Penetration Testing with Kali Linux, WebAsha is the place to be.”
OSCP Certified
rohan-trivedi.webp

Rohan Trivedi

Cyber Security Engineer · Mphasis

“Completing the OSCP Penetration Testing with Kali Linux training at WebAsha was a turning point for me. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. Hands-on practice on real lab systems built genuine confidence, not just theory. The placement assistance team actively shared openings and guided me until I was placed. Doubt-clearing sessions ran even after class hours, which I really appreciated. The knowledge and confidence I gained here continue to help me every day at work.”
OSCP Certified
riya-joshi.webp

Riya Joshi

Ethical Hacker

“Completing the OSCP Penetration Testing with Kali Linux training at WebAsha was a turning point for me. The cloud labs were available round the clock, so I could practise assignments whenever I had time. We worked hands-on with ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab, which made every concept stick. The knowledge and confidence I gained here continue to help me every day at work.”
OSCP Certified
varun-nair.webp

Varun Nair

Penetration Tester · Rakuten

“I joined WebAsha for OSCP Penetration Testing with Kali Linux to level up my skills, and the experience exceeded my expectations. Hands-on practice on real lab systems built genuine confidence, not just theory. Each module built logically, and the coverage of ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab was thorough and current. I could choose between online and classroom training, and both were equally well organised. Flexible batch timings let me attend alongside my job without any stress. A big thank you to the trainers and team for such a rewarding learning experience.”
OSCP Certified
RK

Ravi Kadam

Security Analyst · Coforge

Career Break ReturneeSecurity Analyst
“After a few years as a Career Break Returnee, I decided it was time for a real change and joined WebAsha's OSCP Penetration Testing with Kali Linux training. Certification preparation, mock tests and repeated mock interviews prepared me for real technical rounds. I transitioned into a Security Analyst role at Coforge, nearly doubling my salary from 5 LPA to 9.5 LPA.”
My journey: Career Break Returnee to Security Analyst
Quick Summary

OSCP+ | Penetration Testing with Kali Linux (PEN-200) is a hands-on information technology training course by WebAsha Technologies, available online and in classroom with live projects, certification prep and placement support. It suits beginners and professionals, runs about 6 to 12 weeks, and leads to roles such as IT Professional, Specialist Engineer, Senior Engineer paying roughly 3.5 to 30.0 LPA.

Key takeaways for Hyderabad

  • Master IT through hands-on, practical training.
  • Learn core concepts & fundamentals and hands-on practical skills.
  • Work on real-world projects and lab exercises.
  • Earn an industry-recognised certificate.
  • Get placement support for roles paying up to 30.0 LPA.

OSCP+ | Penetration Testing with Kali Linux (PEN-200) in Hyderabad: WebAsha vs other options

FeatureWebAsha ITSelf-studyGeneric online course
Live instructor-led trainingYesNoSometimes
Hands-on labs & real projectsYesLimitedLimited
Certification exam preparationYesSelf-managedVaries
Doubt-solving & mentorshipYesNoLimited
Placement assistanceYesNoRare
Industry-recognised certificateYesNoVaries

OSCP+ | Penetration Testing with Kali Linux (PEN-200) in Hyderabad FAQs

Last updated: 10 July 2026

Weekend batches usually work best for late-evening shifts, and every live session is recorded so you can catch up the next morning. The 24x7 cloud labs let you practise after your shift ends.
Pharma companies need both: security and compliance knowledge for validated, audited systems, and cloud skills as they move lab and ERP workloads to AWS or Azure. A counsellor can suggest a track based on your current role.
Keep Exploring

Related courses

Take the next step in your IT career

Join thousands of learners who upskilled and got placed with WebAsha Technologies.