OSWE | Advanced Web Attacks and Exploitation (WEB-300)

Overall rating: 4.9 based on 3,795 reviewsG 4.9/5f 4.9/5
The OSWE | Advanced Web Attacks and Exploitation (WEB-300) training at WebAsha Technologies in Pune prepares you for OffSec's advanced web-exploitation certification. It follows WEB-300: Advanced Web Attacks and Exploitation (AWAE), OffSec's 300-level web security course.

You will learn to read application source code and turn small flaws into full compromise. The course covers white-box authentication bypasses, type-juggling attacks, blind SQL injection to RCE, insecure deserialization, server-side request forgery, prototype pollution, and chaining several vulnerabilities into remote code execution in real-world applications written in PHP, Java, .NET, Node.js and other languages.

You earn the certification in a 47-hour-45-minute hands-on exam (scored out of 100, pass mark 85), and it does not expire. OSWE is one of the three certifications that together earn the OSCE³ credential. WebAsha's trainers concentrate on code auditing, which the whole exam depends on.
Duration:40 Hrs (Weekdays & Weekend Session)
Mode:Online/Classroom
Certification:Prepares for OffSec OSWE (WEB-300)
Institute:WebAsha Technologies
Includes:Hands-On Cyber-Range Labs & Attendance Certificate
Trusted By

1000+ leading universities and companies

Our learners are hired by technology, IT services and consulting companies.

  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
Recent Placements Testimonials

OSWE | Advanced Web Attacks and Exploitation (WEB-300) recent reviews

Our learners talk about how the program changed their careers.

Verified Reviews

Student reviews and success stories

Real feedback from learners now placed across top technology and consulting firms.

aarti-verma.webp

Aarti Verma

Penetration Tester · Amdocs

“Enrolling in OSWE WEB-300 Advanced Web Attacks and Exploitation at WebAsha is one of the best career decisions I have made. The real-world implementation examples helped me understand how things work on the job. The mock interviews and interview preparation sharpened me for real technical rounds. We worked hands-on with ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab, which made every concept stick. Every topic was reinforced with practical lab assignments instead of just slides. The knowledge and confidence I gained here continue to help me every day at work.”
Verified Student
swati-shaikh.webp

Swati Shaikh

Penetration Tester · Tech Mahindra

“Completing the OSWE WEB-300 Advanced Web Attacks and Exploitation training at WebAsha was a turning point for me. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. The real-world implementation examples helped me understand how things work on the job. Flexible batch timings let me attend alongside my job without any stress. Hands-on practice on real lab systems built genuine confidence, not just theory. If you want practical, job-ready skills in OSWE WEB-300 Advanced Web Attacks and Exploitation, WebAsha is the place to be.”
Google Review
mohit-deshmukh.webp

Mohit Deshmukh

Security Analyst · Amdocs

“I joined WebAsha for OSWE WEB-300 Advanced Web Attacks and Exploitation to level up my skills, and the experience exceeded my expectations. We worked hands-on with ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab, which made every concept stick. The trainers are clearly industry experts and answered even my toughest doubts patiently. The cloud labs were available round the clock, so I could practise assignments whenever I had time. Live projects gave me the confidence to apply what I learned in a real environment. If you want practical, job-ready skills in OSWE WEB-300 Advanced Web Attacks and Exploitation, WebAsha is the place to be.”
LinkedIn Review
abhishek-sharma.webp

Abhishek Sharma

Ethical Hacker · Coforge

“Completing the OSWE WEB-300 Advanced Web Attacks and Exploitation training at WebAsha was a turning point for me. The study materials and recorded sessions were detailed and easy to revise from. The mock interviews and interview preparation sharpened me for real technical rounds. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. I cleared the certification on my first attempt and highly recommend OSWE WEB-300 Advanced Web Attacks and Exploitation at WebAsha.”
LinkedIn Review
snehal-chatterjee.webp

Snehal Chatterjee

Ethical Hacker · DXC Technology

“Enrolling in OSWE WEB-300 Advanced Web Attacks and Exploitation at WebAsha is one of the best career decisions I have made. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. Hands-on practice on real lab systems built genuine confidence, not just theory. Easily a five-star experience that prepared me for both the exam and real work.”
LinkedIn Review
sourabh-kadam.webp

Sourabh Kadam

Security Analyst · Red Hat

“The OSWE WEB-300 Advanced Web Attacks and Exploitation program at WebAsha genuinely lived up to its reputation. Each module built logically, and the coverage of ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab was thorough and current. The real-world implementation examples helped me understand how things work on the job. Live projects gave me the confidence to apply what I learned in a real environment. The batch was slightly large at times, yet the hands-on focus and support made it well worth it.”
Verified Student
ankit-verma.webp

Ankit Verma

Ethical Hacker

“After comparing a few institutes, I chose WebAsha for OSWE WEB-300 Advanced Web Attacks and Exploitation, and I am glad I did. Hands-on practice on real lab systems built genuine confidence, not just theory. We worked hands-on with ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab, which made every concept stick. I cleared the certification on my first attempt and highly recommend OSWE WEB-300 Advanced Web Attacks and Exploitation at WebAsha.”
Verified Student
shubham-mehta.webp

Shubham Mehta

Ethical Hacker

“Completing the OSWE WEB-300 Advanced Web Attacks and Exploitation training at WebAsha was a turning point for me. The study materials and recorded sessions were detailed and easy to revise from. The placement assistance team actively shared openings and guided me until I was placed. I could choose between online and classroom training, and both were equally well organised. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. This training accelerated my career growth, and I would gladly recommend it to anyone.”
Verified Student
meera-rao.webp

Meera Rao

Penetration Tester

“My OSWE WEB-300 Advanced Web Attacks and Exploitation journey with WebAsha gave me exactly the practical depth I was looking for. We worked hands-on with ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab, which made every concept stick. Every topic was reinforced with practical lab assignments instead of just slides. The mock interviews and interview preparation sharpened me for real technical rounds. I cleared the certification on my first attempt and highly recommend OSWE WEB-300 Advanced Web Attacks and Exploitation at WebAsha.”
Verified Student
Career Roadmap

From your first class to placement

A step-by-step path from your first lesson to certification and a job offer.

Step 1 of 8

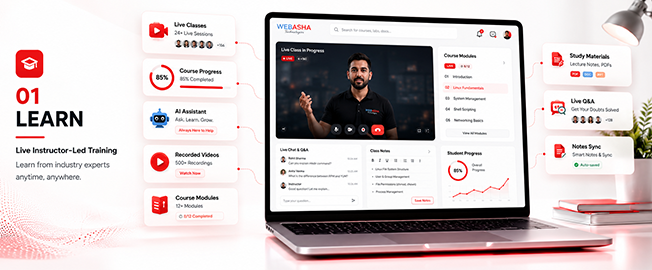
Learn

  • Live instructor-led training
  • Concept-first curriculum
  • Recorded sessions
Foundations & Core Concepts
Learn preview
Training Key Features

OSWE | Advanced Web Attacks and Exploitation (WEB-300) training key features

What you get from our OSWE | Advanced Web Attacks and Exploitation (WEB-300) course: a solid foundation in the basics and real-world, skills you can use at work.

  • Post Training Support

  • Real Time Projects : 2

  • Certification & Job Assistance

  • Course Duration : 2 Months

  • Hands-on Training

  • Full Day Lab Access

Our cloud lab

OSWE | Advanced Web Attacks and Exploitation (WEB-300) cloud lab environment

Our Pune classroom practical lab

Program highlights

What learners get at WebAsha Technologies: practical IT training and the skills employers hire for.

Learning Experience

  • In-Depth Practical Training with Real-World Scenarios
  • Choose Between In-Person or Virtual Classes (Flexible Schedules)
  • Guidance from Seasoned IT Professionals
  • Complimentary Intro to Emerging Tech Topics
  • One-on-One Support for Clarifying Concepts
  • Regular Hands-On Exercises and Live Projects
  • Access to a Library of 150+ Training Videos for a Year

Career Development

  • Tailored Job Placement Support with Multiple Interviews
  • Custom Resume Crafting and Interview Coaching
  • Workshops on Professional Skills and Teamwork
  • Affordable Payment Plans with No Extra Fees
  • Help Preparing for International Certifications
  • Personal Career Guidance from Experts
  • Practice Interviews with Industry Leaders

Why choose WebAsha Technologies

Career-focused IT training with expert mentors, practical labs and vendor certifications, so you stand out when you apply for jobs.

Features Recommended
WebAsha Technologies
Other Institutes
Expert Trainers
10+ Years Experienced Industry Professionals
Freshers or Part-time Instructors
Course Curriculum
Updated for Current Tools (Cybersecurity, Cloud, DevOps, Linux, AI/ML)
Basic or Outdated Content
Hands-on Learning
Real Projects, Labs & Case Studies
Theory-Focused, Limited Practical
Certifications
Vendor-Issued (EC-Council, OffSec, Red Hat, AWS, Microsoft, etc.)
Generic or Unrecognized Certificates
Placement Support
100% Assistance + Resume & Interview Coaching
Limited or No Job Support
Flexible Learning
Classroom & Online Training Options
Rigid Timings, Mostly Classroom-Only
Learning Resources
Lifetime LMS Access, Study Materials, Recorded Sessions
Minimal or No Additional Resources
Batch Size
Small Groups with 1:1 Mentorship
Large, Crowded Batches

Upcoming batches & schedule

Tuesday, November 10, 2026

Online / Classroom
Weekday
6:30 PMIST
Enrollment Closed
Enrollment Closed

Saturday, November 14, 2026

Online / Classroom
Weekend
10:00 AMIST
Enrollment OpenMax intake limit is 10

Tuesday, November 17, 2026

Online / Classroom
Weekday
6:30 PMIST
Enrollment OpenMax intake limit is 10

Tuesday, November 24, 2026

Online / Classroom
Weekday
8:00 AMIST
Enrollment OpenMax intake limit is 10
Flexible Scheduling

Can't find a schedule that works?

Our counsellors can help you arrange a batch that fits your timing.

Course insight 1Course insight 2

OSWE | Advanced Web Attacks and Exploitation (WEB-300) course training overview

Learn Advanced Web Attacks and Exploitation (WEB-300) through Classroom and Online OSWE Training at WebAsha Technologies. The course builds the practical 'Try Harder' skills that the OSWE exam tests.

Training overview:

OSWE is OffSec's advanced web-exploitation certification, earned through the WEB-300 course (Advanced Web Attacks and Exploitation, AWAE). OffSec's current syllabus lists 24 topics. They include source-code analysis, authentication bypass, blind SQL injection, type juggling, deserialization, server-side request forgery and prototype pollution, and the course shows how to chain such flaws into remote code execution. The exam is a 48-hour hands-on test. OSWE is one of the three certifications required for the OSCE³ designation.

Intended audience:

This course suits experienced web-application testers, application and product security engineers, and security researchers who want to learn white-box web exploitation and sit the OSWE exam.

Topics covered:

  • Source-code review: Finding vulnerabilities by reading the application's code.
  • Authentication bypass: Getting past login logic.
  • Type juggling: Abusing PHP's loose comparisons.
  • Blind SQL injection: Extracting data and reaching code execution.
  • Deserialization: Exploiting unsafe handling of serialised objects.
  • SSRF: Reaching internal systems through the server.
  • Prototype pollution: Attacking JavaScript objects through their prototype.
  • Chaining to RCE: Combining several flaws into full compromise.

Requirements:

You should be comfortable with Linux and the command line. If you join online, you need a stable internet connection and a laptop or desktop for the live labs.

Prerequisites:

There are no formal certification prerequisites. OffSec recommends that you can read and write at least one programming language, write simple scripts in Python, Perl, PHP or Bash, know Linux, have used web proxies and understand common web attack vectors. The course builds on PEN-200 and WEB-200 (OSWA).

Career benefits:

OSWE is an advanced credential. In India, OSWE-certified professionals typically earn ₹8 LPA to ₹40+ LPA in senior application and product security roles.
Certification path

CategoryTools & components covered
ProxyBurp Suite
Code reviewSource-code analysis
ScriptingPython exploit development
DatabasesBlind SQLi tooling
DebuggingApplication debuggers
LanguagesPHP, Java, .NET, Node.js
Deserializationysoserial and gadget chains
PlatformKali Linux

Curriculum OSWE | Advanced Web Attacks and Exploitation (WEB-300)

Advanced Web Attacks and Exploitation (WEB-300): 24 syllabus topics

1. JavaScript Prototype Pollution

How an attacker manipulates JavaScript's inheritance model to inject malicious data, compromise application logic and execute code remotely.

  • JavaScript prototypes and inheritance
  • Injecting attacker-controlled data through a polluted prototype
  • Taking prototype pollution through to remote code execution
2. Advanced Server-Side Request Forgery (SSRF)

Using SSRF to bypass filters, reach internal resources and attack complex application architectures.

  • Bypassing filters that are meant to stop SSRF
  • Accessing internal resources through the vulnerable server
  • Exploiting SSRF in complex, multi-service applications
3. Web Security Tools and Methodologies

The tools and working methods the course relies on throughout.

  • Fuzzing
  • Static analysis
  • Dynamic analysis
  • Manual code review
4. Source Code Analysis

Reading source code and following application logic to find attack vectors and security vulnerabilities.

  • Parsing application logic from the source
  • Identifying potential attack vectors
  • Recognising vulnerable code
5. Persistent Cross-Site Scripting

How attackers store malicious code on a web server so that it runs against many users over time.

  • How a stored XSS payload reaches the server
  • Attacking several users with one stored payload
6. Session Hijacking

How attackers take over user sessions to reach sensitive data and functionality.

  • Taking over another user's session
  • Using a hijacked session to access data and functions
7. .NET Deserialization

The ways attackers exploit vulnerabilities caused by deserialization in .NET applications.

  • Serialization and deserialization in .NET
  • Identifying unsafe deserialization in an application
  • Exploiting deserialization flaws
8. Remote Code Execution

The techniques attackers use to run system-compromising code on a targeted web server.

  • Routes from a web vulnerability to code execution
  • Running code on the target web server
9. Blind SQL Injection

Techniques for exploiting SQL injection to compromise a database when the application gives no direct feedback.

  • Recognising SQL injection without visible output
  • Different techniques for extracting data blind
  • Compromising the database through the injection
10. Data Exfiltration

How attackers extract sensitive data from web applications.

  • Exfiltration through SQL injection
  • Exfiltration through XXE attacks
  • Exfiltration through compromised file uploads
11. Bypassing File Upload Restrictions and File Extension Filters

How attackers get past the mechanisms meant to stop malicious files from being uploaded.

  • How upload restrictions work
  • Bypassing file extension filters
  • Uploading a malicious file despite the checks
12. PHP Type Juggling with Loose Comparisons

Exploiting type juggling and loose comparison behaviour in PHP to bypass authentication.

  • Loose and strict comparisons in PHP
  • How PHP converts values between types
  • Bypassing authentication with a loose comparison
13. PostgreSQL Extension and User-Defined Functions

How attackers use PostgreSQL extensions and user-defined functions to read private data, execute commands and set up persistent backdoors.

  • PostgreSQL extensions
  • User-defined functions (UDFs)
  • Command execution and backdoors through the database
14. Bypassing REGEX Restrictions

Evading regex-based input validation to inject malicious payloads into web applications.

  • How regex-based input validation works
  • Evading the validation pattern
  • Delivering a payload past the filter
15. Magic Hashes

Bypassing authentication and performing unauthorised actions by exploiting "magic hashes" in PHP applications.

  • What a magic hash is in PHP
  • Using magic hashes to bypass authentication
16. Bypassing Character Restrictions

Techniques for getting past character restrictions so that a payload can still be injected and the application's behaviour changed.

  • Working out which characters are restricted
  • Building payloads that avoid them
17. UDF Reverse Shells

Using user-defined functions to create a reverse shell and reach the underlying operating system.

  • Creating a user-defined function for a shell
  • Getting a reverse shell on the database host
18. PostgreSQL Large Objects

How attackers abuse large objects in PostgreSQL to store and execute malicious code and to exfiltrate data.

  • Large objects in PostgreSQL
  • Storing and executing code through large objects
  • Exfiltrating sensitive data
19. DOM-Based Cross-Site Scripting (Black Box)

How the browser's Document Object Model (DOM) can be manipulated to run malicious JavaScript without direct server-side interaction. This topic is taught black box, without source code.

  • The DOM and how DOM-based XSS arises
  • Finding DOM-based XSS without access to source
  • Executing JavaScript in the victim's browser
20. Server-Side Template Injection

Identifying and exploiting vulnerabilities in server-side templates to execute code remotely, disclose information or escalate privileges.

  • Identifying template injection
  • Remote code execution through a template
  • Information disclosure and privilege escalation
21. Weak Random Token Generation

The risks of poorly implemented random token generation and how attackers exploit it to compromise user sessions.

  • Why weakly generated tokens are predictable
  • Exploiting weak tokens to compromise a session
22. XML External Entity Injection

How attackers exploit weaknesses in XML parsers to access files, execute commands or cause denial of service, and how XXE can be prevented.

  • XML parsers and external entities
  • Reading files and executing commands through XXE
  • Preventing XXE vulnerabilities
23. RCE via Database Functions

How vulnerabilities in database functions can be exploited to execute arbitrary code on the server.

  • Database functions that can be abused
  • Executing arbitrary code on the server through them
24. OS Command Injection via WebSockets (Black Box)

Identifying WebSocket vulnerabilities that allow operating system commands to be injected, giving control of the underlying server. This topic is taught black box.

  • How the application uses WebSockets
  • Injecting OS commands through a WebSocket
  • Mitigating the vulnerability

Download the complete course syllabus

Get the full curriculum, modules & exam details delivered to you instantly.

Meet our expert trainers

Learn from certified OSWE | Advanced Web Attacks and Exploitation (WEB-300) experts who work in the industry and teach with practical, real-world examples.

  • Simplified Guidance: Break down Linux concepts for beginners.
  • Hands-On Practice: Engage in labs for command-line and admin tasks.
  • Customized Support: Offer one-on-one help for your goals.
  • Career & Lab Aid: Assist with projects and exam prep.
  • Industry Knowledge: Draw from extensive Red Hat experience.
  • Certified Professionals: Hold RHCSA, RHCE credentials.
  • Real-World Application: Insights from enterprise Linux deployments.
  • Training Success: Over 1,000 students guided annually.
  • Corporate Links: Partnerships with IBM, Accenture, Wipro.
Free Skill Assessment

Self assessment

Test your skills with an online assessment exam and find out how ready you are for your certification.

  • Free mock test
  • Instant score report
  • Mapped to the certification
Learner taking an online skills assessment

OSWE | Advanced Web Attacks and Exploitation (WEB-300) Certification Bootcamp

Advanced Web Attacks and Exploitation (WEB-300) is a hands-on OffSec course. It prepares you for the OSWE exam: 47 hours 45 minutes of white-box exploitation, scored out of 100 with a pass mark of 85. The certification does not expire and counts towards the OSCE³ designation.

  • Expert Trainers: Learn white-box exploitation from trainers who do security research.
  • Source-Code Labs: Audit the source code of real applications.
  • Exploit Chaining: Chain small flaws into RCE.
  • Several languages: Targets written in PHP, Java, .NET and Node.js.
  • Exam-Realistic Practice: Practice scenarios modelled on the OSWE exam.
  • OSCE³ Path: One of the three certifications needed for OSCE³.
  • Flexible Batches: Weekday or weekend, online or classroom.
  • Placement Support: Help with your resume and interview preparation.

OSWE Exam Details & Format

AttributeDetails
CourseWEB-300: Advanced Web Attacks and Exploitation (AWAE)
CertificationOffSec Web Expert (OSWE)
Exam FormatProctored, hands-on white-box web exploitation over a private VPN
Hands-On Time47 hours 45 minutes
Reporting TimeAdditional 24 hours to upload documentation
StructureSeveral target machines to compromise, with a written report for each
Scoring100 points in total, with partial or full points for each objective
Passing Score85 of 100 points
ValidityLifetime (does not expire)
Part OfOSCE³ (with OSEP and OSED)

OSWE Exam Passing Criteria

The OSWE exam is proctored and fully hands-on. You get 47 hours 45 minutes for white-box web exploitation, then 24 hours to upload your documentation. You analyse and exploit the target applications, retrieve the proof and document your work. The exam is scored out of 100 points and you need 85 to pass. Missing documentation can cost points. OSWE does not expire and is one of the three certifications required for the OSCE³ designation. WebAsha's labs give you practice in source-code review and exploit chaining before you sit the exam.

Job Roles and Salary Outlook After OSWE

OSWE is an advanced web-exploitation certification. The table below shows typical salaries for OSWE-certified professionals in application security and product security across India.

Job Title Primary Responsibilities Average Salary (INR)
Senior Web App Pentester Perform white-box web exploitation. Experienced: ₹16-34 LPA
Application Security Engineer Secure and audit application code. Fresher: ₹8-14 LPA
Experienced: ₹18-36 LPA
Product Security Engineer Own security for a product. Experienced: ₹20-40 LPA
Security Researcher Discover novel web vulnerabilities. Experienced: ₹18-38 LPA
Bug Bounty Hunter (Advanced) Chain flaws for high-value rewards. Variable: ₹ depends on findings
Security Consultant (Web) Deliver advanced web assessments. Experienced: ₹18-36 LPA

Salaries vary with experience and proven skill. OSWE shows employers that you have done this work hands-on.


Career Benefits of OSWE

OSWE shows that you can read code and chain flaws into remote code execution. It is aimed at senior web exploitation and product security roles.
  • Proven skill: The OSWE exam is practical, so passing it shows you can do the work.
  • Demand: The job roles listed below all ask for this skill set.
  • Salaries: In India, typical packages run from ₹8 LPA to ₹40+ LPA, depending on role and experience.
  • Recognised worldwide: Employers in India and abroad know OffSec certifications.
  • Career growth: It can lead to both offensive and defensive security roles.
  • Lasting value: Practical security skills stay useful as tools change, and OSWE does not expire.

Why Choose OSWE Training at WebAsha Technologies in Pune

Prepare for OSWE with WebAsha Technologies, an OffSec training partner. Our programme follows the practical format of the OSWE exam.

  • Expert Trainers: Learn white-box exploitation from trainers who do security research.
  • Source-Code Labs: Audit the source code of real applications.
  • Exploit Chaining: Chain small flaws into RCE.
  • Several languages: Targets written in PHP, Java, .NET and Node.js.
  • Exam-Realistic Practice: Practice scenarios modelled on the OSWE exam.
  • OSCE³ Path: One of the three certifications needed for OSCE³.
  • Flexible Batches: Weekday or weekend, online or classroom.
  • Placement Support: Help with your resume and interview preparation.

Certification Path

OffSec learning paths

OffSec organises its hands-on certifications into discipline-based learning paths, from foundations to advanced exploitation. Certifications we train for at WebAsha are linked below.

Not sure where to start or what to take next? Our mentors will map your cyber-security career path.

Plan My Cyber-Security Path
Program Highlights

What the program includes

Learning, career, certification and placement support in one program.

Learning benefits

  • Structured Curriculum
    Concept-first, job-ready syllabus
  • Hands-On Labs
    Practice every concept live
  • Expert-Led Sessions
    Learn from working professionals

Career benefits

  • Resume Building
    ATS-friendly, recruiter-ready
  • Mock Interviews
    Real interview simulations
  • Job Referrals
    Access to hiring partner network

Certification benefits

  • Globally Recognized
    Industry-standard certifications
  • Exam Preparation
    Targeted, exam-focused coaching
  • Practice Tests
    Unlimited mock assessments

Placement benefits

  • 500+ Hiring Partners
    Active recruiter network
  • Placement Drives
    Regular hiring opportunities
  • Salary Negotiation
    Guidance to maximize offers
Success Stories

Placement success stories

Starting your first IT job or changing direction? Explore the career paths below and think about what you want from your next role. Our team can help you plan the training and preparation to work towards it.

SS

Suraj Sayyad

SOC Analyst · NTT Data

Junior DeveloperSOC Analyst
“As a Junior Developer, I felt stuck in my growth, so I took the leap and signed up for OSWE WEB-300 Advanced Web Attacks and Exploitation at WebAsha. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. Within a few months I moved from Junior Developer to SOC Analyst at NTT Data, and my package grew from 4.5 LPA to 8 LPA.”
From Junior Developer to SOC Analyst
rahul-reddy.webp

Rahul Reddy

Security Analyst · Hexaware

Network Support TraineeSecurity Analyst
“After a few years as a Network Support Trainee, I decided it was time for a real change and joined WebAsha's OSWE WEB-300 Advanced Web Attacks and Exploitation training. The placement team actively shared openings and coached me through resume building and every interview. The trainers were patient and genuinely industry-experienced, and the practical focus on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab made everything click. Within a few months I moved from Network Support Trainee to Security Analyst at Hexaware, and my package grew from 2.4 LPA to 5.5 LPA.”
Network Support Trainee to Security Analyst at Hexaware
SJ

Sanjana Jadhav

Penetration Tester · JPMorgan

Technical Support AssociatePenetration Tester
“My journey began as a Technical Support Associate with big ambitions, and the OSWE WEB-300 Advanced Web Attacks and Exploitation program at WebAsha became the turning point. Working on real-world implementations helped me understand exactly how things run on the job. The placement team actively shared openings and coached me through resume building and every interview. I landed a Penetration Tester position at JPMorgan with a strong hike from 4 LPA to 9.5 LPA, and I owe it to WebAsha.”
From Technical Support Associate to Penetration Tester
shubham-mehta.webp

Shubham Mehta

Ethical Hacker

“Completing the OSWE WEB-300 Advanced Web Attacks and Exploitation training at WebAsha was a turning point for me. The study materials and recorded sessions were detailed and easy to revise from. The placement assistance team actively shared openings and guided me until I was placed. I could choose between online and classroom training, and both were equally well organised. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. This training accelerated my career growth, and I would gladly recommend it to anyone.”
OSWE Certified
riya-kulkarni.webp

Riya Kulkarni

Cyber Security Engineer · Cognizant

“Enrolling in OSWE WEB-300 Advanced Web Attacks and Exploitation at WebAsha is one of the best career decisions I have made. The trainers are clearly industry experts and answered even my toughest doubts patiently. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. The real-world implementation examples helped me understand how things work on the job. A big thank you to the trainers and team for such a rewarding learning experience.”
OSWE Certified
suraj-joshi.webp

Suraj Joshi

Penetration Tester · Oracle

“Enrolling in OSWE WEB-300 Advanced Web Attacks and Exploitation at WebAsha is one of the best career decisions I have made. The mock interviews and interview preparation sharpened me for real technical rounds. The real-world implementation examples helped me understand how things work on the job. Each module built logically, and the coverage of ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab was thorough and current. A couple of sessions felt a little fast, but overall a strong, practical program I recommend.”
OSWE Certified
AB

Aniket Bose

Security Analyst · Coforge

FresherSecurity Analyst
“I started out as a Fresher and always wanted a stronger technical career, so I enrolled in the OSWE WEB-300 Advanced Web Attacks and Exploitation program at WebAsha. The placement team actively shared openings and coached me through resume building and every interview. The hands-on labs and live projects around ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab rebuilt my confidence from the ground up. Today I proudly work as a Security Analyst at Coforge, and the jump from 4.5 LPA to 8 LPA still feels surreal.”
Fresher to Security Analyst at Coforge
AB

Ayaan Bansal

Security Analyst · Coforge

Desktop Support EngineerSecurity Analyst
“My journey began as a Desktop Support Engineer with big ambitions, and the OSWE WEB-300 Advanced Web Attacks and Exploitation program at WebAsha became the turning point. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. The hands-on labs and live projects around ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab rebuilt my confidence from the ground up. Within a few months I moved from Desktop Support Engineer to Security Analyst at Coforge, and my package grew from 4 LPA to 7 LPA.”
Security Analyst at Coforge - a career turnaround
SA

Sana Ansari

Security Analyst · Barclays

Diploma GraduateSecurity Analyst
“Coming from a Diploma Graduate background, switching felt risky, but WebAsha's OSWE WEB-300 Advanced Web Attacks and Exploitation course gave me a clear path forward. Working on real-world implementations helped me understand exactly how things run on the job. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. Today I proudly work as a Security Analyst at Barclays, and the jump from 4 LPA to 7.5 LPA still feels surreal.”
From Diploma Graduate to Security Analyst
Quick Summary

OSWE | Advanced Web Attacks and Exploitation (WEB-300) is a hands-on information technology training course by WebAsha Technologies, available online and in classroom with live projects, certification prep and placement support. It suits beginners and professionals, runs about 6 to 12 weeks, and leads to roles such as IT Professional, Specialist Engineer, Senior Engineer paying roughly 3.5 to 30.0 LPA.

Key takeaways

  • Master IT through hands-on, practical training.
  • Learn core concepts & fundamentals and hands-on practical skills.
  • Work on real-world projects and lab exercises.
  • Earn an industry-recognised certificate.
  • Get placement support for roles paying up to 30.0 LPA.

OSWE | Advanced Web Attacks and Exploitation (WEB-300): WebAsha vs other options

FeatureWebAsha ITSelf-studyGeneric online course
Live instructor-led trainingYesNoSometimes
Hands-on labs & real projectsYesLimitedLimited
Certification exam preparationYesSelf-managedVaries
Doubt-solving & mentorshipYesNoLimited
Placement assistanceYesNoRare
Industry-recognised certificateYesNoVaries

Last updated: 23 June 2026

OSWE | Advanced Web Attacks and Exploitation (WEB-300) FAQs

OSWE | Advanced Web Attacks and Exploitation (WEB-300) is a hands-on training program in information technology. It takes you from fundamentals to working skills through live sessions, lab practice and real projects, with an industry-recognised certificate and placement support.

Freshers and graduates Working IT professionals upskilling Career changers entering tech Professionals preparing for certification

Basic computer familiarity Interest in the subject No prior experience required; we start from fundamentals

You will build practical skills including core concepts & fundamentals, hands-on practical skills, industry tools & best practices, real-world project work, problem solving & troubleshooting and more, applied through hands-on labs and real projects.
The OSWE | Advanced Web Attacks and Exploitation (WEB-300) syllabus spans information technology, from core concepts to advanced modules, each reinforced with lab exercises and a capstone-style project.
OSWE | Advanced Web Attacks and Exploitation (WEB-300) typically runs about 6 to 12 weeks depending on the track (weekday or weekend), plus lab and project time. Fast-track and extended options are available. Ask for the current batch schedule.

OSWE | Advanced Web Attacks and Exploitation (WEB-300) fees depend on the mode (classroom or live-online) and track, and WebAsha Technologies offers flexible / no-cost EMI options. Request the latest fee details and any running offers from the enquiry form.

Both. You can take OSWE | Advanced Web Attacks and Exploitation (WEB-300) as a live-online program or attend classroom sessions, with the same syllabus, hands-on labs and trainers in either mode.

Yes. OSWE | Advanced Web Attacks and Exploitation (WEB-300) runs in weekday, weekend and evening batches so students and working professionals can train without disturbing their schedule.

Yes. OSWE | Advanced Web Attacks and Exploitation (WEB-300) starts from fundamentals so beginners can follow along, while the advanced modules add depth for experienced learners.

Absolutely. Many learners are working professionals. Flexible weekend, evening and live-online OSWE | Advanced Web Attacks and Exploitation (WEB-300) batches let you upskill without a career break.

Yes. OSWE | Advanced Web Attacks and Exploitation (WEB-300) is project-driven. You practise in real labs and build live projects in information technology alongside the theory, so you finish interview-ready.

After completing OSWE | Advanced Web Attacks and Exploitation (WEB-300) you can target roles such as IT Professional, Specialist Engineer, Senior Engineer, Consultant, with senior packages reaching around 30.0 LPA depending on experience and location.

Information technology roles typically start around 3.5 LPA for freshers and rise to about 30.0 LPA for experienced professionals. Actual packages depend on your skills, role and employer.

Yes. Information technology skills are in strong, growing demand across IT services, product companies and startups, offering clear career progression and rising salaries for certified professionals.

Trained IT professionals are hired by IT-services majors, global capability centres, product companies and startups. Organisations across the industry actively recruit for information technology.

Yes. WebAsha Technologies provides resume building, mock interviews and referrals to hiring partners as part of dedicated placement support. Outcomes depend on your skills and effort.

OSWE | Advanced Web Attacks and Exploitation (WEB-300) is taught by experienced, industry-certified trainers who bring real project experience into the classroom, so you learn current, job-relevant practices.

Yes. You receive an industry-recognised WebAsha training certificate, and the course also prepares you for the relevant official certification exam.

Yes. Alongside job skills, OSWE | Advanced Web Attacks and Exploitation (WEB-300) includes structured exam preparation, with practice tests and guidance for the recognised IT certification employers look for.

Yes. You can book a free demo session for OSWE | Advanced Web Attacks and Exploitation (WEB-300) to meet the trainer and experience the teaching style before you enroll.

WebAsha combines hands-on labs, certified trainers, live projects, certification prep and dedicated placement support. It is a practical, job-focused route into information technology.

Click Enroll Now, request a callback, or message our team on WhatsApp to get the latest batch schedule, fees and available offers.

Keep Exploring

Related courses

Take the next step in your IT career

Join thousands of learners who upskilled and got placed with WebAsha Technologies.