OSWP | OffSec Wireless Professional (PEN-210)

Overall rating: 4.9 based on 3,795 reviewsG 4.9/5f 4.9/5
The OSWP | OffSec Wireless Professional (PEN-210) training at WebAsha Technologies in Pune is OffSec's respected wireless penetration-testing certification, delivered through the PEN-210: Wireless Network Attacks course.

You will learn to audit and attack real Wi-Fi networks: 802.11 protocols and encryption, Linux wireless tooling, capturing and analysing frames with Wireshark, cracking WEP and WPA/WPA2 pre-shared keys with Aircrack-ng, attacking WPS, standing up rogue access points, breaking WPA Enterprise and captive portals, and working with bettercap and Kismet.

The certification is earned in a practical, proctored, 3-hour-45-minute hands-on exam (plus 24 hours to report) against live wireless targets, and it never expires. WebAsha's trainers give you the radio-level skills that wireless assessments ask for.
Duration:40 Hrs (Weekdays & Weekend Session)
Mode:Online/Classroom
Certification:Prepares for OffSec OSWP (PEN-210)
Institute:WebAsha Technologies
Includes:Hands-On Cyber-Range Labs & Attendance Certificate
Trusted By

1000+ leading universities and companies

Our learners are hired by technology, IT services and consulting companies.

  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
  • Hiring partner
Recent Placements Testimonials

OSWP | OffSec Wireless Professional (PEN-210) recent reviews

Our learners talk about how the program changed their careers.

Verified Reviews

Student reviews and success stories

Real feedback from learners now placed across top technology and consulting firms.

shubham-menon.webp

Shubham Menon

Ethical Hacker · Vodafone Idea

“Completing the OSWP PEN-210 OffSec Wireless Network Attacks training at WebAsha was a turning point for me. Flexible batch timings let me attend alongside my job without any stress. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. Hands-on practice on real lab systems built genuine confidence, not just theory. The batch was slightly large at times, yet the hands-on focus and support made it well worth it.”
Verified Student
imran-verma.webp

Imran Verma

Penetration Tester · IBM

“I recently finished the OSWP PEN-210 OffSec Wireless Network Attacks course at WebAsha Technologies and it was worth every minute. Each module built logically, and the coverage of ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab was thorough and current. The placement assistance team actively shared openings and guided me until I was placed. The study materials and recorded sessions were detailed and easy to revise from. A couple of sessions felt a little fast, but overall a strong, practical program I recommend.”
Verified Student
tejas-chatterjee.webp

Tejas Chatterjee

SOC Analyst · DXC Technology

“After comparing a few institutes, I chose WebAsha for OSWP PEN-210 OffSec Wireless Network Attacks, and I am glad I did. The mock interviews and interview preparation sharpened me for real technical rounds. We worked hands-on with ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab, which made every concept stick. This training accelerated my career growth, and I would gladly recommend it to anyone.”
Verified Student
rohan-pathan.webp

Rohan Pathan

Cyber Security Engineer · Red Hat

“WebAsha's OSWP PEN-210 OffSec Wireless Network Attacks training turned a tough certification into an enjoyable learning experience. Live projects gave me the confidence to apply what I learned in a real environment. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. I cleared the certification on my first attempt and highly recommend OSWP PEN-210 OffSec Wireless Network Attacks at WebAsha.”
Verified Student
mohit-ansari.webp

Mohit Ansari

Ethical Hacker

“Enrolling in OSWP PEN-210 OffSec Wireless Network Attacks at WebAsha is one of the best career decisions I have made. The syllabus covered ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab in real depth rather than skimming the surface. The cloud labs were available round the clock, so I could practise assignments whenever I had time. Easily a five-star experience that prepared me for both the exam and real work.”
Google Review
riya-more.webp

Riya More

SOC Analyst · Tech Mahindra

“I recently finished the OSWP PEN-210 OffSec Wireless Network Attacks course at WebAsha Technologies and it was worth every minute. We worked hands-on with ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab, which made every concept stick. The certification preparation and mock tests made the actual exam feel straightforward. A big thank you to the trainers and team for such a rewarding learning experience.”
LinkedIn Review
ajay-nair.webp

Ajay Nair

SOC Analyst · TCS

“The OSWP PEN-210 OffSec Wireless Network Attacks program at WebAsha genuinely lived up to its reputation. The course focused on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab through practical, real-world scenarios. The mock interviews and interview preparation sharpened me for real technical rounds. Hands-on practice on real lab systems built genuine confidence, not just theory. I could choose between online and classroom training, and both were equally well organised. A big thank you to the trainers and team for such a rewarding learning experience.”
LinkedIn Review
aniket-iyer.webp

Aniket Iyer

Ethical Hacker · Mphasis

“My OSWP PEN-210 OffSec Wireless Network Attacks journey with WebAsha gave me exactly the practical depth I was looking for. Each module built logically, and the coverage of ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab was thorough and current. The placement assistance team actively shared openings and guided me until I was placed. This training accelerated my career growth, and I would gladly recommend it to anyone.”
Verified Student
mahesh-thomas.webp

Mahesh Thomas

Cyber Security Engineer · Barclays

“I joined WebAsha for OSWP PEN-210 OffSec Wireless Network Attacks to level up my skills, and the experience exceeded my expectations. The learning experience was structured, practical and paced just right for working professionals. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. I cleared the certification on my first attempt and highly recommend OSWP PEN-210 OffSec Wireless Network Attacks at WebAsha.”
Verified Student
Career Roadmap

From your first class to placement

A step-by-step path from your first lesson to certification and a job offer.

Step 1 of 8

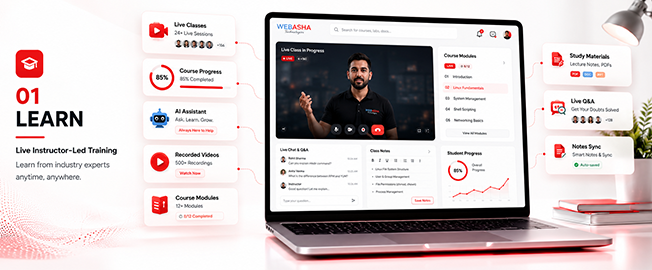
Learn

  • Live instructor-led training
  • Concept-first curriculum
  • Recorded sessions
Foundations & Core Concepts
Learn preview
Training Key Features

OSWP | OffSec Wireless Professional (PEN-210) training key features

What you get from our OSWP | OffSec Wireless Professional (PEN-210) course: a solid foundation in the basics and real-world, skills you can use at work.

  • Post Training Support

  • Real Time Projects : 2

  • Certification & Job Assistance

  • Course Duration : 2 Months

  • Hands-on Training

  • Full Day Lab Access

Our cloud lab

OSWP | OffSec Wireless Professional (PEN-210) cloud lab environment

Our Pune classroom practical lab

Program highlights

What learners get at WebAsha Technologies: practical IT training and the skills employers hire for.

Learning Experience

  • In-Depth Practical Training with Real-World Scenarios
  • Choose Between In-Person or Virtual Classes (Flexible Schedules)
  • Guidance from Seasoned IT Professionals
  • Complimentary Intro to Emerging Tech Topics
  • One-on-One Support for Clarifying Concepts
  • Regular Hands-On Exercises and Live Projects
  • Access to a Library of 150+ Training Videos for a Year

Career Development

  • Tailored Job Placement Support with Multiple Interviews
  • Custom Resume Crafting and Interview Coaching
  • Workshops on Professional Skills and Teamwork
  • Affordable Payment Plans with No Extra Fees
  • Help Preparing for International Certifications
  • Personal Career Guidance from Experts
  • Practice Interviews with Industry Leaders

Why choose WebAsha Technologies

Career-focused IT training with expert mentors, practical labs and vendor certifications, so you stand out when you apply for jobs.

Features Recommended
WebAsha Technologies
Other Institutes
Expert Trainers
10+ Years Experienced Industry Professionals
Freshers or Part-time Instructors
Course Curriculum
Updated for Current Tools (Cybersecurity, Cloud, DevOps, Linux, AI/ML)
Basic or Outdated Content
Hands-on Learning
Real Projects, Labs & Case Studies
Theory-Focused, Limited Practical
Certifications
Vendor-Issued (EC-Council, OffSec, Red Hat, AWS, Microsoft, etc.)
Generic or Unrecognized Certificates
Placement Support
100% Assistance + Resume & Interview Coaching
Limited or No Job Support
Flexible Learning
Classroom & Online Training Options
Rigid Timings, Mostly Classroom-Only
Learning Resources
Lifetime LMS Access, Study Materials, Recorded Sessions
Minimal or No Additional Resources
Batch Size
Small Groups with 1:1 Mentorship
Large, Crowded Batches

Upcoming batches & schedule

Saturday, October 24, 2026

Online / Classroom
Weekend
6:30 PMIST
Enrollment Closed
Enrollment Closed

Sunday, October 25, 2026

Online / Classroom
Weekend
10:00 AMIST
Enrollment OpenMax intake limit is 10

Saturday, October 31, 2026

Online / Classroom
Weekend
6:30 PMIST
Enrollment OpenMax intake limit is 10

Monday, November 9, 2026

Online / Classroom
Weekday
8:00 AMIST
Enrollment OpenMax intake limit is 10
Flexible Scheduling

Can't find a schedule that works?

Our counsellors can help you arrange a batch that fits your timing.

Course insight 1Course insight 2

OSWP | OffSec Wireless Professional (PEN-210) course training overview

Learn OffSec Wireless Professional (PEN-210) through our classroom and online OSWP training at WebAsha Technologies. The course builds the hands-on, 'Try Harder' skills that the OSWP exam tests.

Training overview:

OSWP is OffSec's specialist wireless-security certification, earned through the PEN-210 course. You learn to audit and attack 802.11 wireless networks: cracking WEP, WPA/WPA2 pre-shared keys and WPS, attacking WPA Enterprise and captive portals, and deploying rogue access points. You prove these skills in a practical, hands-on wireless exam.

Intended audience:

The course suits penetration testers, network security engineers and security consultants who want a recognised, hands-on specialisation in wireless attacks.

Topics covered:

  • 802.11 and encryption: How Wi-Fi and its security work.
  • Wireless tooling: Linux drivers, stacks and adapters.
  • Frame analysis: Capturing and reading wireless traffic.
  • PSK cracking: WEP and WPA/WPA2.
  • WPS attacks: Exploiting Wi-Fi Protected Setup.
  • Rogue access points: Luring and intercepting clients.
  • WPA Enterprise: Attacking corporate Wi-Fi.
  • Captive portals: Bypassing and attacking portals.

Requirements:

Comfort with Linux and the command line is recommended. Online participants need a stable internet connection and a laptop/desktop for the live labs.

Prerequisites:

OffSec recommends comfort with the Linux command line, a solid grasp of TCP/IP networking, and basic wireless concepts such as 802.11 and encryption. A compatible wireless adapter is needed for practice.

Career benefits:

Wireless testing is a specialisation employers pay for. In India, OSWP-certified professionals typically earn ₹5 LPA to ₹34+ LPA as part of penetration-testing and red-team roles.
Certification path

CategoryTools & components covered
CrackingAircrack-ng suite
CaptureWireshark
Interceptionbettercap
DiscoveryKismet
WPSReaver, Bully
AdaptersMonitor-mode Wi-Fi cards
Rogue APhostapd, evil-twin tooling
PlatformKali Linux

Curriculum OSWP | OffSec Wireless Professional (PEN-210)

PEN-210: Wireless Network Attacks (OSWP): 16 course modules

1. IEEE 802.11

The opening module covers the IEEE 802.11 standards that Wi-Fi is built on, so you understand the radio layer before you attack it.

  • The 802.11 standards and their amendments
  • How antenna diversity differs from MIMO
  • The bands, channels and radio concepts behind Wi-Fi
2. Wireless Networks

You look at how wireless networks are put together and how clients and access points talk to each other.

  • Infrastructure, ad-hoc and mesh topologies
  • Wireless distribution systems and Wi-Fi Direct
  • Putting an adapter into monitor mode
3. Wi-Fi Encryption

This module walks through the encryption schemes used on Wi-Fi and where each one is weak.

  • Open networks, WEP and the WPA family through WPA3
  • Opportunistic Wireless Encryption and WPS
  • Management frame protection with 802.11w
4. Linux Wireless Tools, Drivers, and Stacks

You set up the Linux side of wireless testing: the drivers, tools and stacks that make capture and injection possible.

  • Loading and unloading wireless drivers
  • The Linux wireless stack and common tools
  • Preparing an adapter for assessment work
5. Wireshark Essentials

Wireshark is the main tool for reading wireless traffic, and this module shows how to capture and filter it cleanly.

  • Capturing 802.11 traffic and applying display filters
  • Working with Wireshark from the command line
  • Remote packet capture and advanced preferences
6. Frames and Network Interactions

You study the 802.11 frame in detail and how devices associate and exchange data.

  • The difference between packets and frames
  • 802.11 MAC frame structure and frame types
  • How clients interact with a network
7. Aircrack-ng Essentials

This module takes you through the Aircrack-ng suite tool by tool, from capture to cracking.

  • Monitor mode and capture with airmon-ng and airodump-ng
  • Injection and deauthentication with aireplay-ng
  • Cracking and decrypting with aircrack-ng and airdecap-ng
8. Cracking Authentication Hashes

You crack captured WPA/WPA2 handshakes using several tools and wordlist techniques.

  • Cracking WPA/WPA2 pre-shared keys from a handshake
  • Building custom wordlists for the target
  • Using Hashcat, Airolib-ng and coWPAtty
9. Attacking WPS Networks

Wi-Fi Protected Setup has well-known flaws, and this module shows how to exploit them to recover the key.

  • How WPS works and where it is weak
  • Recovering the PIN and the pre-shared key
  • Running the WPS attack in practice
10. Rogue Access Points

You build rogue and evil-twin access points to lure clients and intercept their traffic.

  • How rogue access points work
  • Discovering target networks and clients
  • Standing up a rogue AP to capture connections
11. Attacking WPA Enterprise

This module covers enterprise Wi-Fi authentication and how to attack it to capture credentials.

  • How WPA Enterprise authentication works
  • The PEAP exchange
  • Capturing and attacking enterprise credentials
12. Attacking Captive Portals

Captive portals gate access to many networks, and here you learn to bypass and attack them.

  • How captive portals control access
  • Bypassing portal authentication
  • Behaviours that affect the attack
13. bettercap Essentials

You use bettercap for live wireless attacks and man-in-the-middle work.

  • Installing and running bettercap
  • Modules and commands, including the Wi-Fi module
  • Interacting with targets during an attack
14. Kismet Essentials

Kismet handles discovery and monitoring, and this module covers it end to end.

  • Installing and configuring Kismet
  • Detecting access points and clients from the web interface
  • Remote capture, logging and exporting data
15. Determining Chipsets and Drivers

Hardware choice decides what attacks you can run, so this module helps you identify chipsets and drivers.

  • Identifying the chipset in a wireless adapter
  • Working out the matching driver
  • Choosing adapters that support monitor mode and injection
16. Manual Network Connections

The final module connects to and sets up networks from the command line, without graphical tools.

  • Connecting to an access point from the command line
  • Setting up an access point manually
  • Working without graphical wireless tools

Download the complete course syllabus

Get the full curriculum, modules & exam details delivered to you instantly.

Meet our expert trainers

Learn from certified OSWP | OffSec Wireless Professional (PEN-210) experts who work in the industry and teach with practical, real-world examples.

  • Simplified Guidance: Break down Linux concepts for beginners.
  • Hands-On Practice: Engage in labs for command-line and admin tasks.
  • Customized Support: Offer one-on-one help for your goals.
  • Career & Lab Aid: Assist with projects and exam prep.
  • Industry Knowledge: Draw from extensive Red Hat experience.
  • Certified Professionals: Hold RHCSA, RHCE credentials.
  • Real-World Application: Insights from enterprise Linux deployments.
  • Training Success: Over 1,000 students guided annually.
  • Corporate Links: Partnerships with IBM, Accenture, Wipro.
Free Skill Assessment

Self assessment

Test your skills with an online assessment exam and find out how ready you are for your certification.

  • Free mock test
  • Instant score report
  • Mapped to the certification
Learner taking an online skills assessment

OSWP | OffSec Wireless Professional (PEN-210) Certification Bootcamp

OffSec Wireless Professional (PEN-210) is a hands-on OffSec certification. It prepares you for the OSWP exam, a 3-hour-45-minute hands-on wireless assessment where you compromise two of three live networks, and it is a lifetime credential.

  • Expert Trainers: Learn wireless attacks from practitioners.
  • Live Wireless Labs: Practise against real Wi-Fi networks.
  • Complete Coverage: WEP, WPA/WPA2, WPS, Enterprise and captive portals.
  • Hardware Guidance: Choose the right adapters and chipsets.
  • Exam-Realistic Practice: Scenarios like the OSWP exam.
  • Flexible Batches: Weekday/weekend and online/classroom options.
  • Placement Support: Resume building and interviews.
  • Lifetime Credential: OSWP never expires.

OSWP Exam Details & Format

AttributeDetails
CoursePEN-210: Wireless Network Attacks
CertificationOffSec Wireless Professional (OSWP)
Exam FormatProctored, hands-on attacks against live wireless networks
Hands-On Time3 hours 45 minutes
Reporting TimeAdditional 24 hours to write and upload the report
Structure3 wireless network scenarios (one active at a time)
ObjectiveRecover the key, connect, and retrieve proof.txt from each target
Passing RequirementComplete 2 of 3 scenarios, including one mandatory scenario
ValidityLifetime; does not expire
LevelSpecialist / intermediate (Level 200)

OSWP Exam Passing Criteria

The OSWP exam is a proctored, fully hands-on wireless assessment of 3 hours 45 minutes, followed by 24 hours to write and upload your report. You face three wireless network scenarios (only one active at a time); for each you recover the wireless key, connect to the access point and retrieve a proof file. To pass you must complete two of the three scenarios, including one mandatory scenario identified at the start. OffSec does not publish a numeric score for OSWP. The OSWP certification never expires, and WebAsha's live wireless labs let you practise the attack techniques the exam requires.

Job Roles and Salary Outlook After OSWP

Wireless security is a specialist skill in short supply, and OSWP-certified testers add Wi-Fi assessment ability that commands strong pay across India.

Job Title Primary Responsibilities Average Salary (INR)
Wireless Penetration Tester Audit and attack Wi-Fi networks. Fresher: ₹5-9 LPA
Experienced: ₹14-28 LPA
Penetration Tester Add wireless to full-scope testing. Fresher: ₹6-10 LPA
Experienced: ₹15-30 LPA
Security Consultant Deliver wireless assessments. Experienced: ₹16-32 LPA
Network Security Engineer Secure enterprise wireless. Fresher: ₹5-9 LPA
Experienced: ₹14-26 LPA
Red Team Operator Use wireless as an entry vector. Experienced: ₹18-34 LPA
VAPT Consultant Include Wi-Fi in engagements. Fresher: ₹6-10 LPA
Experienced: ₹15-28 LPA

Salaries vary with proven skill; OSWP demonstrates real, hands-on ability employers value.


Career Benefits of OSWP

OSWP shows you can break into wireless networks, a specialist edge that sets penetration testers apart in real engagements.

  • Proven Skill: The exam is fully hands-on, so passing shows real ability.
  • Strong Demand: Wireless testing is a specialist area employers hire for.
  • Salaries: Specialist wireless skills tend to pay well.
  • Globally Respected: OffSec certifications are recognised worldwide.
  • Career Growth: Opens offensive and defensive security roles.
  • Outlook: Hands-on security skills stay in demand.

Why Choose OSWP Training at WebAsha Technologies in Pune

Prepare for OSWP with WebAsha Technologies, an OffSec training partner. Our program is built around the real, hands-on OSWP exam.

  • Expert Trainers: Learn wireless attacks from practitioners.
  • Live Wireless Labs: Practise against real Wi-Fi networks.
  • Complete Coverage: WEP, WPA/WPA2, WPS, Enterprise and captive portals.
  • Hardware Guidance: Choose the right adapters and chipsets.
  • Exam-Realistic Practice: Scenarios like the OSWP exam.
  • Flexible Batches: Weekday/weekend and online/classroom options.
  • Placement Support: Resume building and interviews.
  • Lifetime Credential: OSWP never expires.
Certification Path

OffSec learning paths

OffSec organises its hands-on certifications into discipline-based learning paths, from foundations to advanced exploitation. Certifications we train for at WebAsha are linked below.

Not sure where to start or what to take next? Our mentors will map your cyber-security career path.

Plan My Cyber-Security Path
Program Highlights

What the program includes

Learning, career, certification and placement support in one program.

Learning benefits

  • Structured Curriculum
    Concept-first, job-ready syllabus
  • Hands-On Labs
    Practice every concept live
  • Expert-Led Sessions
    Learn from working professionals

Career benefits

  • Resume Building
    ATS-friendly, recruiter-ready
  • Mock Interviews
    Real interview simulations
  • Job Referrals
    Access to hiring partner network

Certification benefits

  • Globally Recognized
    Industry-standard certifications
  • Exam Preparation
    Targeted, exam-focused coaching
  • Practice Tests
    Unlimited mock assessments

Placement benefits

  • 500+ Hiring Partners
    Active recruiter network
  • Placement Drives
    Regular hiring opportunities
  • Salary Negotiation
    Guidance to maximize offers
Success Stories

Placement success stories

Starting your first IT job or changing direction? Explore the career paths below and think about what you want from your next role. Our team can help you plan the training and preparation to work towards it.

rohit-chauhan.webp

Rohit Chauhan

Security Analyst · Oracle

Help Desk EngineerSecurity Analyst
“I started out as a Help Desk Engineer and always wanted a stronger technical career, so I enrolled in the OSWP PEN-210 OffSec Wireless Network Attacks program at WebAsha. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. The trainers were patient and genuinely industry-experienced, and the practical focus on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab made everything click. Within a few months I moved from Help Desk Engineer to Security Analyst at Oracle, and my package grew from 4.5 LPA to 8.5 LPA.”
Help Desk Engineer to Security Analyst at Oracle
AM

Ayaan Mathew

Penetration Tester · Capgemini

Data Entry OperatorPenetration Tester
“My journey began as a Data Entry Operator with big ambitions, and the OSWP PEN-210 OffSec Wireless Network Attacks program at WebAsha became the turning point. The trainers were patient and genuinely industry-experienced, and the practical focus on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab made everything click. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. I landed a Penetration Tester position at Capgemini with a strong hike from 4.5 LPA to 7.5 LPA, and I owe it to WebAsha.”
My journey: Data Entry Operator to Penetration Tester
rohan-pathan.webp

Rohan Pathan

Cyber Security Engineer · Red Hat

“WebAsha's OSWP PEN-210 OffSec Wireless Network Attacks training turned a tough certification into an enjoyable learning experience. Live projects gave me the confidence to apply what I learned in a real environment. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. I cleared the certification on my first attempt and highly recommend OSWP PEN-210 OffSec Wireless Network Attacks at WebAsha.”
Cyber Security Certified
mahesh-thomas.webp

Mahesh Thomas

Cyber Security Engineer · Barclays

“I joined WebAsha for OSWP PEN-210 OffSec Wireless Network Attacks to level up my skills, and the experience exceeded my expectations. The learning experience was structured, practical and paced just right for working professionals. What impressed me was how the trainers connected ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab to actual production use. I cleared the certification on my first attempt and highly recommend OSWP PEN-210 OffSec Wireless Network Attacks at WebAsha.”
Cyber Security Certified
yogesh-sayyad.webp

Yogesh Sayyad

SOC Analyst · Amdocs

Junior DeveloperSOC Analyst
“My journey began as a Junior Developer with big ambitions, and the OSWP PEN-210 OffSec Wireless Network Attacks program at WebAsha became the turning point. Certification preparation, mock tests and repeated mock interviews prepared me for real technical rounds. Within a few months I moved from Junior Developer to SOC Analyst at Amdocs, and my package grew from 7 LPA to 16 LPA.”
My journey: Junior Developer to SOC Analyst
VD

Vinay Das

Security Analyst · Mphasis

Non-IT ProfessionalSecurity Analyst
“My journey began as a Non-IT Professional with big ambitions, and the OSWP PEN-210 OffSec Wireless Network Attacks program at WebAsha became the turning point. Working on real-world implementations helped me understand exactly how things run on the job. I transitioned into a Security Analyst role at Mphasis, nearly doubling my salary from 7 LPA to 16 LPA.”
Security Analyst at Mphasis - a career turnaround
AS

Ayaan Singh

SOC Analyst · Cognizant

Technical Support AssociateSOC Analyst
“I started out as a Technical Support Associate and always wanted a stronger technical career, so I enrolled in the OSWP PEN-210 OffSec Wireless Network Attacks program at WebAsha. The placement team actively shared openings and coached me through resume building and every interview. I transitioned into a SOC Analyst role at Cognizant, nearly doubling my salary from 2.4 LPA to 4.5 LPA.”
How I became a SOC Analyst with WebAsha
AM

Anjali More

Security Analyst · Tech Mahindra

Operations ExecutiveSecurity Analyst
“My journey began as a Operations Executive with big ambitions, and the OSWP PEN-210 OffSec Wireless Network Attacks program at WebAsha became the turning point. The trainers were patient and genuinely industry-experienced, and the practical focus on ethical hacking, reconnaissance, scanning, exploitation and penetration testing in a safe lab made everything click. I landed a Security Analyst position at Tech Mahindra with a strong hike from 5 LPA to 8.5 LPA, and I owe it to WebAsha.”
How I became a Security Analyst with WebAsha
jayesh-shaikh.webp

Jayesh Shaikh

Penetration Tester · Cisco

Bank EmployeePenetration Tester
“After a few years as a Bank Employee, I decided it was time for a real change and joined WebAsha's OSWP PEN-210 OffSec Wireless Network Attacks training. Certification preparation, mock tests and repeated mock interviews prepared me for real technical rounds. Cloud labs, recorded sessions and after-hours doubt support meant I could learn seriously alongside my job. I landed a Penetration Tester position at Cisco with a strong hike from 3.5 LPA to 7.5 LPA, and I owe it to WebAsha.”
How I became a Penetration Tester with WebAsha
Quick Summary

OSWP | OffSec Wireless Professional (PEN-210) is a hands-on information technology training course by WebAsha Technologies, available online and in classroom with live projects, certification prep and placement support. It suits beginners and professionals, runs about 6 to 12 weeks, and leads to roles such as IT Professional, Specialist Engineer, Senior Engineer paying roughly 3.5 to 30.0 LPA.

Key takeaways

  • Master IT through hands-on, practical training.
  • Learn core concepts & fundamentals and hands-on practical skills.
  • Work on real-world projects and lab exercises.
  • Earn an industry-recognised certificate.
  • Get placement support for roles paying up to 30.0 LPA.

OSWP | OffSec Wireless Professional (PEN-210): WebAsha vs other options

FeatureWebAsha ITSelf-studyGeneric online course
Live instructor-led trainingYesNoSometimes
Hands-on labs & real projectsYesLimitedLimited
Certification exam preparationYesSelf-managedVaries
Doubt-solving & mentorshipYesNoLimited
Placement assistanceYesNoRare
Industry-recognised certificateYesNoVaries

Last updated: 23 June 2026

OSWP | OffSec Wireless Professional (PEN-210) FAQs

OSWP | OffSec Wireless Professional (PEN-210) is a hands-on training program in information technology. It takes you from fundamentals to working skills through live sessions, lab practice and real projects, with an industry-recognised certificate and placement support.

Freshers and graduates Working IT professionals upskilling Career changers entering tech Professionals preparing for certification

Basic computer familiarity Interest in the subject No prior experience required; we start from fundamentals

You will build practical skills including core concepts & fundamentals, hands-on practical skills, industry tools & best practices, real-world project work, problem solving & troubleshooting and more, applied through hands-on labs and real projects.

The OSWP | OffSec Wireless Professional (PEN-210) syllabus spans information technology, from core concepts to advanced modules, each reinforced with lab exercises and a capstone-style project.

OSWP | OffSec Wireless Professional (PEN-210) typically runs about 6 to 12 weeks depending on the track (weekday or weekend), plus lab and project time. Fast-track and extended options are available. Ask for the current batch schedule.

OSWP | OffSec Wireless Professional (PEN-210) fees depend on the mode (classroom or live-online) and track, and WebAsha Technologies offers flexible / no-cost EMI options. Request the latest fee details and any running offers from the enquiry form.

Both. You can take OSWP | OffSec Wireless Professional (PEN-210) as a live-online program or attend classroom sessions, with the same syllabus, hands-on labs and trainers in either mode.

Yes. OSWP | OffSec Wireless Professional (PEN-210) runs in weekday, weekend and evening batches so students and working professionals can train without disturbing their schedule.

Yes. OSWP | OffSec Wireless Professional (PEN-210) starts from fundamentals so beginners can follow along, while the advanced modules add depth for experienced learners.

Absolutely. Many learners are working professionals. Flexible weekend, evening and live-online OSWP | OffSec Wireless Professional (PEN-210) batches let you upskill without a career break.

Yes. OSWP | OffSec Wireless Professional (PEN-210) is project-driven. You practise in real labs and build live projects in information technology alongside the theory, so you finish interview-ready.

After completing OSWP | OffSec Wireless Professional (PEN-210) you can target roles such as IT Professional, Specialist Engineer, Senior Engineer, Consultant, with senior packages reaching around 30.0 LPA depending on experience and location.

Information technology roles typically start around 3.5 LPA for freshers and rise to about 30.0 LPA for experienced professionals. Actual packages depend on your skills, role and employer.

Yes. Information technology skills are in strong, growing demand across IT services, product companies and startups, offering clear career progression and rising salaries for certified professionals.

Trained IT professionals are hired by IT-services majors, global capability centres, product companies and startups. Organisations across the industry actively recruit for information technology.

Yes. WebAsha Technologies provides resume building, mock interviews and referrals to hiring partners as part of dedicated placement support. Outcomes depend on your skills and effort.

OSWP | OffSec Wireless Professional (PEN-210) is taught by experienced, industry-certified trainers who bring real project experience into the classroom, so you learn current, job-relevant practices.

Yes. You receive an industry-recognised WebAsha training certificate, and the course also prepares you for the relevant official certification exam.

Yes. Alongside job skills, OSWP | OffSec Wireless Professional (PEN-210) includes structured exam preparation, with practice tests and guidance for the recognised IT certification employers look for.

Yes. You can book a free demo session for OSWP | OffSec Wireless Professional (PEN-210) to meet the trainer and experience the teaching style before you enroll.

WebAsha combines hands-on labs, certified trainers, live projects, certification prep and dedicated placement support. It is a practical, job-focused route into information technology.

Click Enroll Now, request a callback, or message our team on WhatsApp to get the latest batch schedule, fees and available offers.

Keep Exploring

Related courses

Take the next step in your IT career

Join thousands of learners who upskilled and got placed with WebAsha Technologies.