How DMARC Works and Why It Matters for Email Security
DMARC (Domain-based Message Authentication, Reporting and Conformance, RFC 7489) lets a domain owner tell receiving mail servers what to do with email that claims to come from their domain but fails authentication. It builds on SPF, which lists servers allowed to send for the domain, and DKIM, which signs messages cryptographically.
Topic: Cyber Threats, Scams & Online Safety in Cybersecurity & Ethical Hacking · Explainer
Also covers: Cybersecurity Foundations
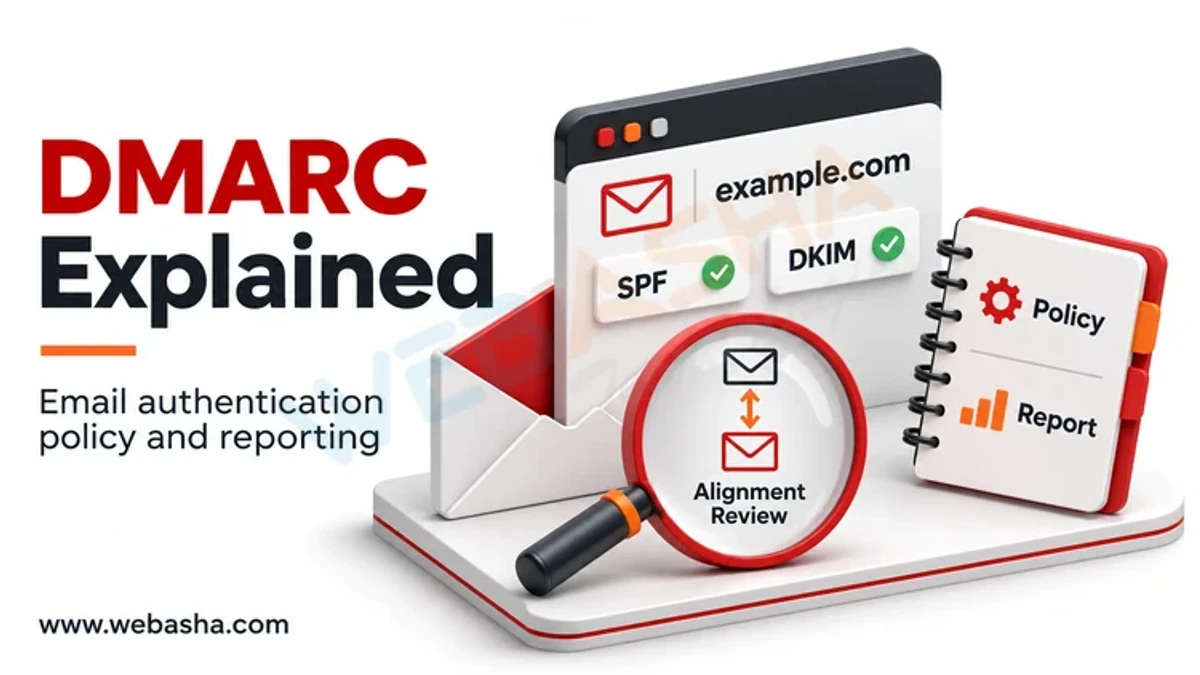
Quick answer: DMARC (Domain-based Message Authentication, Reporting and Conformance, RFC 7489) lets a domain owner tell receiving mail servers what to do with email that claims to come from their domain but fails authentication. It builds on SPF, which lists servers allowed to send for the domain, and DKIM, which signs messages cryptographically. A message passes DMARC if SPF or DKIM passes and the authenticated domain aligns with the visible From address. The domain publishes a policy of none (monitor), quarantine (spam folder) or reject, and receives reports showing who is sending as it. A reject policy stops attackers spoofing your exact domain.
Key takeaways
- DMARC requires SPF or DKIM to pass and align with the From domain.
- Start with p=none to collect reports, then move to quarantine and reject.
- Google and Yahoo require DMARC for bulk senders since 2024.
- DMARC stops exact-domain spoofing, not lookalike domains.
- Reports reveal forgotten services sending as your domain.
Table of Contents
- How Do SPF, DKIM and DMARC Fit Together?
- What Is Alignment?
- What Does a DMARC Record Look Like?
- How Do You Roll Out DMARC Safely?
- How Do You Check a Domain's Records?
- What Doesn't DMARC Stop?
- References
How Do SPF, DKIM and DMARC Fit Together?
| Standard | What it checks | RFC |
|---|---|---|
| SPF | Is the sending server authorised for the envelope domain? | 7208 |
| DKIM | Is the message signed by the domain and unchanged? | 6376 |
| DMARC | Does SPF or DKIM pass and align with the From domain? What to do if not? | 7489 |
What Is Alignment?
SPF checks the envelope sender (Return-Path) and DKIM checks the signing domain (d=). Users see the From header. DMARC requires one of those authenticated domains to match the From domain, either exactly (strict) or within the same organisational domain (relaxed). Without alignment, attackers could pass SPF with their own domain while showing yours in From.
What Does a DMARC Record Look Like?
_dmarc.example.com. TXT "v=DMARC1; p=reject; rua=mailto:[email protected]; adkim=s; aspf=r; pct=100"| Tag | Meaning |
|---|---|
p | Policy: none, quarantine or reject |
rua | Where to send aggregate reports |
adkim, aspf | Strict (s) or relaxed (r) alignment |
sp | Policy for subdomains |
pct | Percentage of messages the policy applies to |
How Do You Roll Out DMARC Safely?
- Inventory every service that sends as your domain: mail servers, marketing, CRM, ticketing, payroll.
- Publish SPF and set up DKIM signing for each service.
- Publish
p=nonewith a reporting address and analyse reports for a few weeks. - Fix legitimate senders that fail.
- Move to
p=quarantine, thenp=reject. - Protect domains that never send email with
v=spf1 -allandp=reject.
Since February 2024, Google and Yahoo require bulk senders to have SPF, DKIM and DMARC. US federal agencies were required to adopt DMARC reject under CISA BOD 18-01.
How Do You Check a Domain's Records?
dig +short TXT example.com | grep spf
dig +short TXT _dmarc.example.com
dig +short TXT selector1._domainkey.example.com    # DKIM key (selector varies)
In a received email, look at the Authentication-Results header for spf=pass, dkim=pass and dmarc=pass.
What Doesn't DMARC Stop?
- Lookalike domains such as examp1e.com.
- Display-name spoofing from a different domain.
- Messages from compromised legitimate accounts.
Combine DMARC with user training, lookalike domain monitoring and phishing-resistant MFA. The UK NCSC's email security guidance covers these layers. Related: QR code phishing. WebAsha offers email security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.