Phases of Penetration Testing Explained: A Step-by-Step Guide
A penetration test follows defined phases. The Penetration Testing Execution Standard (PTES) lists seven: pre-engagement interactions, intelligence gathering, threat modelling, vulnerability analysis, exploitation, post-exploitation and reporting. NIST SP 800-115 groups the work into four: planning, discovery, attack and reporting.
Topic: Penetration Testing in Cybersecurity & Ethical Hacking · Lab / project
Also covers: Ethical Hacking
Learning path: Ethical Hacking for Beginners, lesson 9 of 13
Quick answer: A penetration test follows defined phases. The Penetration Testing Execution Standard (PTES) lists seven: pre-engagement interactions, intelligence gathering, threat modelling, vulnerability analysis, exploitation, post-exploitation and reporting. NIST SP 800-115 groups the work into four: planning, discovery, attack and reporting. Every test starts with written authorisation and rules of engagement that define scope, timing, allowed techniques and emergency contacts. Testers then gather information, find and safely validate weaknesses, measure business impact and deliver a report with clear fixes. Without signed permission, the same activity is a crime under India's IT Act 2000.
Key takeaways
- Authorisation and rules of engagement come before any technical work.
- PTES has seven phases; NIST SP 800-115 has four broader ones.
- Validation must be controlled to avoid harming production systems.
- The report is the real product of a penetration test.
- Retesting confirms that fixes actually work.
Table of Contents
- Why Do Authorisation and Rules of Engagement Come First?
- What Are the Phases of Penetration Testing?
- What Happens in the Discovery and Analysis Phases?
- How Are Weaknesses Validated Safely?
- What Should a Penetration Test Report Contain?
- References
Why Do Authorisation and Rules of Engagement Come First?
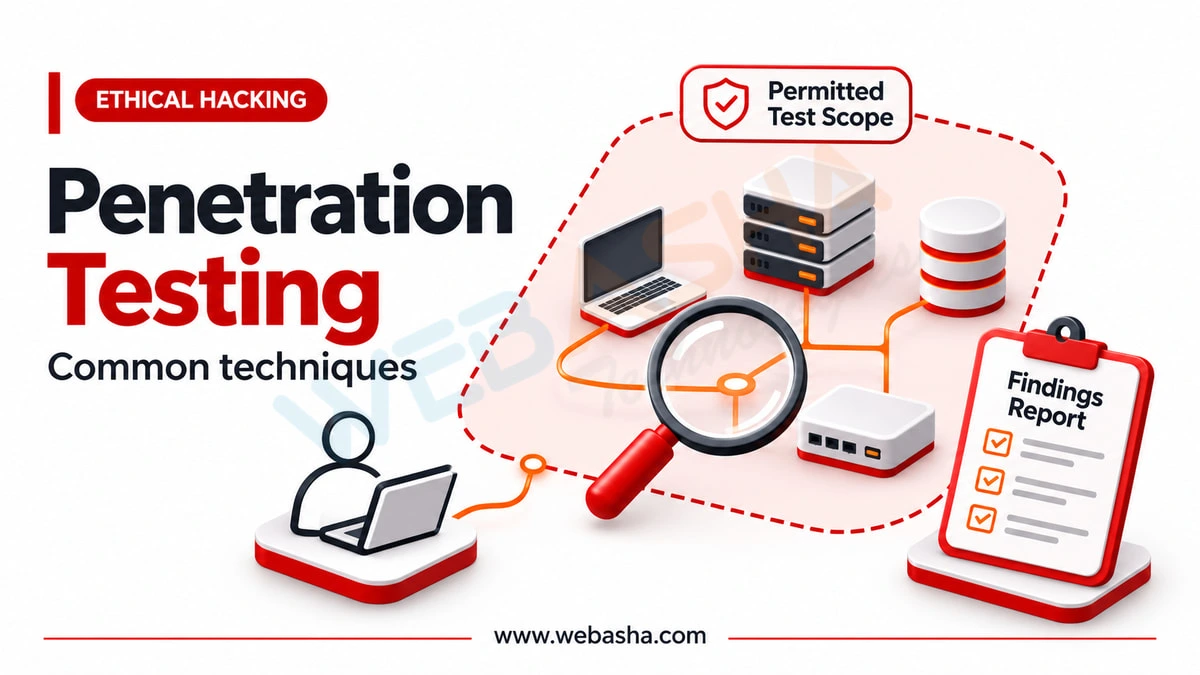
Pre-engagement is the first PTES phase for a reason. Before testing, both sides sign documents that cover:
| Item | What it defines |
|---|---|
| Authorisation letter | Who owns the systems and who allows the test |
| Scope | IP ranges, domains, apps and anything explicitly excluded |
| Rules of engagement | Allowed techniques, testing hours, data handling, social engineering limits |
| Communication plan | Emergency contacts and when to stop testing |
| Third-party approval | Permission from cloud or hosting providers where their policy requires it |
Testing outside this scope can breach Sections 43 and 66 of the IT Act 2000. Government and regulated bodies in India often use CERT-In empanelled auditors.
What Are the Phases of Penetration Testing?
| PTES phase | NIST SP 800-115 phase | Main output |
|---|---|---|
| 1. Pre-engagement | Planning | Signed scope and rules of engagement |
| 2. Intelligence gathering | Discovery | Asset and exposure list |
| 3. Threat modelling | Discovery | Likely attackers and high-value targets |
| 4. Vulnerability analysis | Discovery | Candidate weaknesses |
| 5. Exploitation | Attack | Validated findings with evidence |
| 6. Post-exploitation | Attack | Business impact assessment |
| 7. Reporting | Reporting | Findings, risk ratings and fixes |
Sources: PTES and NIST SP 800-115. Web tests often follow the OWASP Web Security Testing Guide.
What Happens in the Discovery and Analysis Phases?
Intelligence gathering collects public and technical information about in-scope assets, such as domains, exposed services and technologies in use. Threat modelling asks who would realistically attack this organisation and what they would want, often using MITRE ATT&CK to describe likely techniques. Vulnerability analysis combines automated scanning with manual review to build a list of possible weaknesses, which testers then confirm or discard.
How Are Weaknesses Validated Safely?
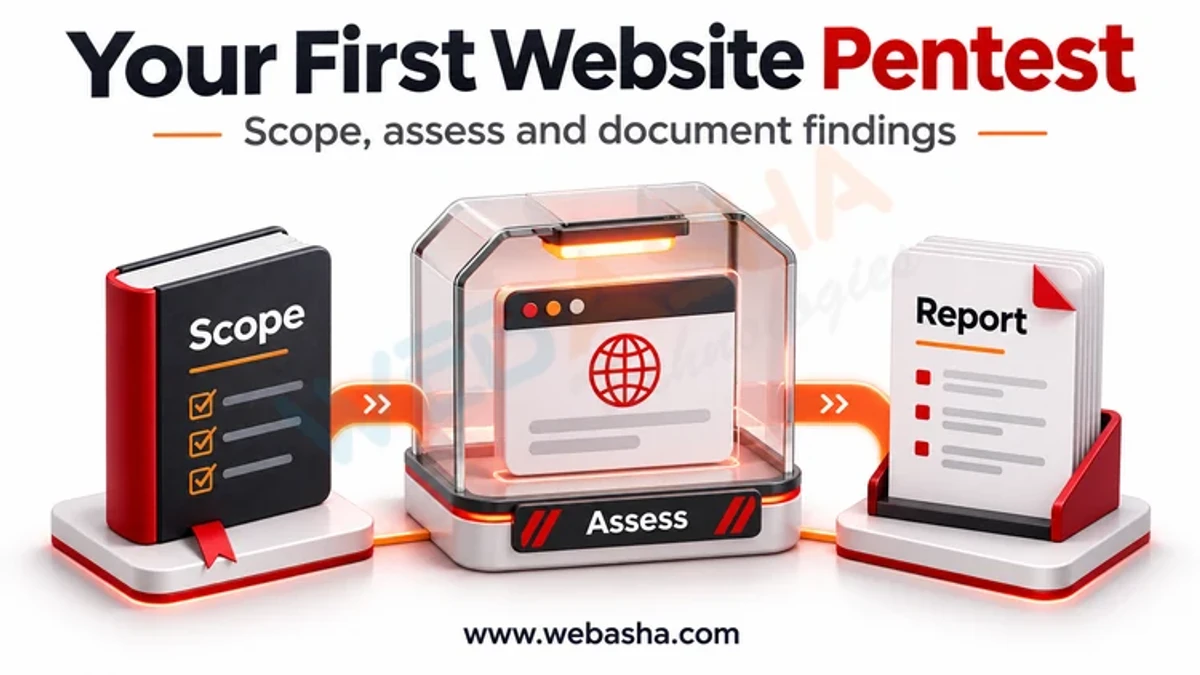
In the attack phase, testers prove that a weakness is real, within the agreed rules. Good practice includes avoiding denial of service, using the least intrusive proof, never copying real personal data, keeping a detailed activity log and stopping immediately if a critical issue or sign of a real attacker appears. Post-exploitation measures impact, for example whether a flaw would expose customer records, and then cleans up any test artefacts. For a beginner walk through of the overall process on a web app, see performing your first website pentest.
What Should a Penetration Test Report Contain?
- Executive summary in plain business language.
- Scope, dates, method and limitations.
- Each finding with severity, evidence, affected assets and impact.
- Clear, prioritised remediation steps.
- Retest results once fixes are applied.
Reports often contain sensitive details, so share them only with named recipients over secure channels and agree how long the tester keeps evidence.
PCI DSS requires regular penetration testing for cardholder data environments; see the PCI SSC document library for its guidance. Preparing for jobs in this field? Review our penetration testing interview questions.
Learn each phase in authorised labs with our ethical hacking and VAPT training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.