Common Port Numbers List: Legacy Ports and Their Secure Alternatives
A port number identifies which service on a host should receive network traffic. IANA keeps the official registry and splits the 65,536 port numbers into three ranges: system or well-known ports (0 to 1023), user or registered ports (1024 to 49151) and dynamic or private ports (49152 to 65535). Many older protocols such as Telnet (23), FTP (21), HTTP (80), POP3 (110) and IMAP (143) send data in clear text.
Topic: Ethical Hacking in Cybersecurity & Ethical Hacking · Explainer
Also covers: Networking
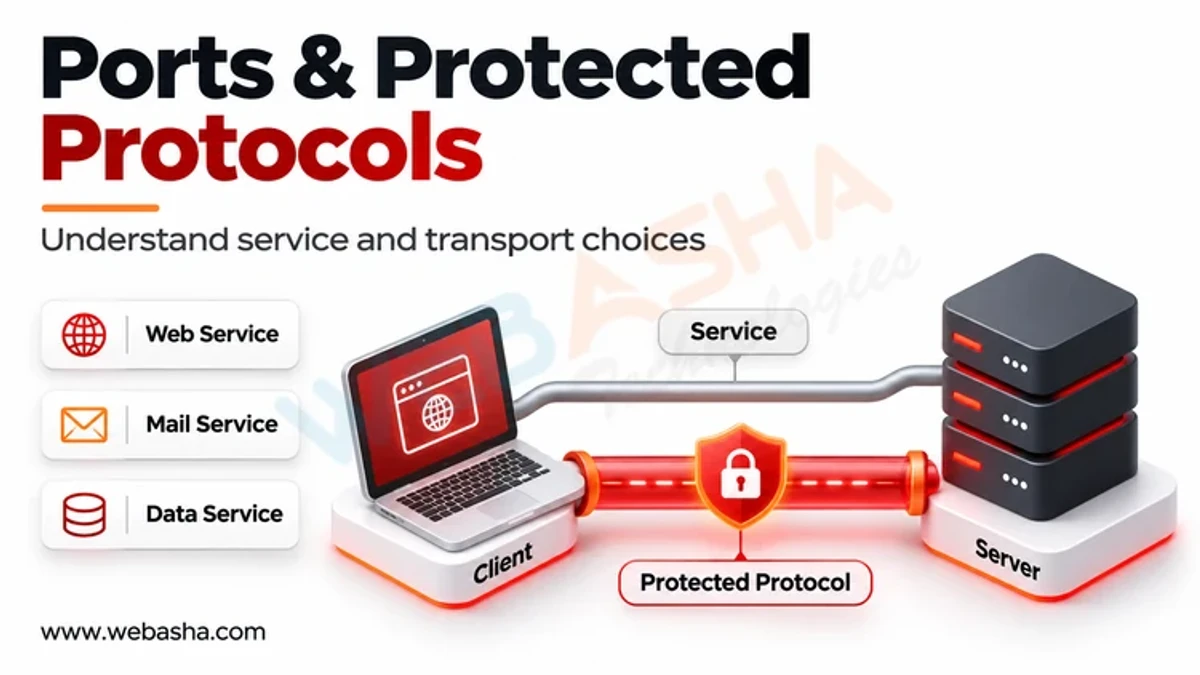
Quick answer: A port number identifies which service on a host should receive network traffic. IANA keeps the official registry and splits the 65,536 port numbers into three ranges: system or well-known ports (0 to 1023), user or registered ports (1024 to 49151) and dynamic or private ports (49152 to 65535). Many older protocols such as Telnet (23), FTP (21), HTTP (80), POP3 (110) and IMAP (143) send data in clear text. Their secure alternatives, such as SSH (22), HTTPS (443), POP3S (995) and IMAPS (993), add encryption. The port number itself does not make traffic secure; the protocol running on it does.
Key takeaways
- IANA assigns port numbers; RFC 6335 defines the three ranges.
- Well-known ports 0 to 1023 host core services like DNS, HTTP and SSH.
- Legacy clear-text protocols have encrypted replacements, often on a different port.
- Changing a port hides a service from casual noise but is not a security control.
- Close or filter every port that does not need to be reachable.
Table of Contents
- What Is a Port Number?
- What Are the Three Port Number Ranges?
- Which Port Numbers Should Everyone Know?
- Which Legacy Ports Have Secure Alternatives?
- Does Changing a Port Number Make a Service Secure?
- How Do You Check Which Ports Are Open on Your Own System?
- How Should Organisations Manage Exposed Ports?
- References
What Is a Port Number?
An IP address gets a packet to the right host. The port number, carried in the TCP or UDP header, gets it to the right application on that host. A web server listens on port 443, a mail server on 25 or 587, and so on. Your computer picks a temporary source port for each outgoing connection.
The IANA port number registry records which service is assigned to which number for TCP, UDP, SCTP and DCCP.
What Are the Three Port Number Ranges?
RFC 6335 defines the ranges and how IANA assigns them.
| Range | Name | Use |
|---|---|---|
| 0 to 1023 | System (well-known) ports | Core services; binding usually needs admin rights on Unix-like systems |
| 1024 to 49151 | User (registered) ports | Applications registered with IANA, such as 3306 for MySQL |
| 49152 to 65535 | Dynamic (private, ephemeral) ports | Temporary client-side ports; never assigned by IANA |
Which Port Numbers Should Everyone Know?
| Port | Protocol | Service |
|---|---|---|
| 22 | TCP | SSH, SFTP |
| 25 | TCP | SMTP relay between mail servers |
| 53 | UDP and TCP | DNS |
| 67 and 68 | UDP | DHCP |
| 80 | TCP | HTTP |
| 123 | UDP | NTP |
| 161 and 162 | UDP | SNMP and SNMP traps |
| 443 | TCP and UDP | HTTPS (UDP for HTTP/3 over QUIC) |
| 445 | TCP | SMB file sharing |
| 3389 | TCP and UDP | Remote Desktop Protocol |
For a longer lookup list, see our guide to the most commonly used TCP and UDP ports.
Which Legacy Ports Have Secure Alternatives?
| Legacy (clear text) | Secure alternative | What changes |
|---|---|---|
| Telnet, 23 | SSH, 22 | Encrypted remote shell (RFC 4253) |
| FTP, 20 and 21 | SFTP on 22, or FTPS on 990 | Credentials and files encrypted |
| HTTP, 80 | HTTPS, 443 | TLS protects web traffic |
| SMTP submission, 25 | 587 with STARTTLS, or 465 implicit TLS | Authenticated, encrypted mail submission |
| POP3, 110 | POP3S, 995 | Implicit TLS |
| IMAP, 143 | IMAPS, 993 | Implicit TLS |
| DNS, 53 | DNS over TLS, 853; DNS over HTTPS, 443 | Queries hidden from on-path observers |
| LDAP, 389 | LDAPS, 636 | Directory traffic encrypted |
| SNMPv1 and v2c, 161 | SNMPv3, still 161 | Same port, but adds authentication and encryption |
RFC 8314 recommends implicit TLS on 465, 993 and 995 for mail clients, and RFC 7858 assigns 853 to DNS over TLS. Notice SNMPv3: the port stays the same and only the protocol version changes.
Does Changing a Port Number Make a Service Secure?
No. Moving SSH from 22 to another port cuts down automated log noise, but anyone scanning all ports will still find it. Security comes from encryption, strong authentication, patching and limiting who can reach the service. Treat a non-standard port as tidiness, not protection.
How Do You Check Which Ports Are Open on Your Own System?
List listening sockets on machines you own or manage:
# Linux
ss -tulpn

# Windows (PowerShell)
Get-NetTCPConnection -State Listen
netstat -ano | findstr LISTENING
Scanning networks you do not own needs written authorisation. Unauthorised scanning can fall under Sections 43 and 66 of India's IT Act 2000.
How Should Organisations Manage Exposed Ports?
- Keep an inventory of every listening service and its owner.
- Default-deny inbound firewall rules; open only what is needed.
- Never expose management interfaces such as RDP, SSH or admin panels directly to the internet; CISA's BOD 23-02 explains why.
- Block SMB (445) at the perimeter and follow Microsoft SMB hardening guidance.
- Retire Telnet, FTP and SNMPv1/v2c wherever possible.
- Log connections and keep logs for 180 days to meet CERT-In directions.
Our TCP/IP model guide explains where ports sit in the stack. To practise this hands-on, ask about our networking and cybersecurity training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.