What is DevSecOps?
DevSecOps is a combination of developing software, securing code, and managing data - all while keeping the business running smoothly. In short, it's about having the right people in place to manage security throughout the entire application lifecycle (SDLC). DevSecOps brings together a lot of disciplines including developers, operations, information technology, architects, solutions providers and others. And it can be done at any stage of your organization's SDLC. Let's take a look at some of these different roles.
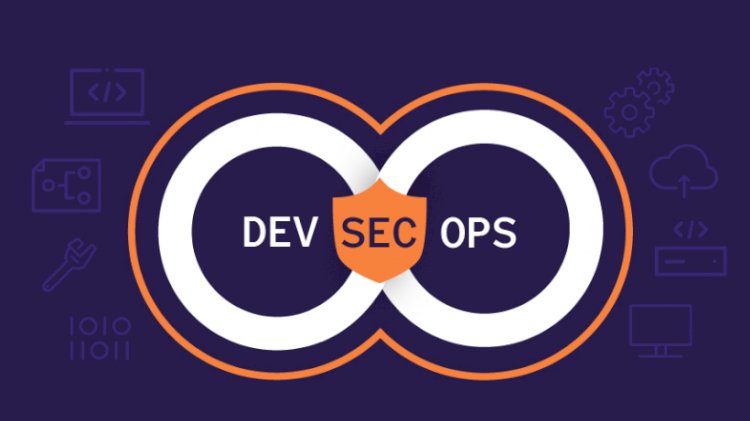
Quick answer: DevSecOps means building security into every stage of software development and operations, instead of checking it at the end. Development, security and operations teams share responsibility, using automated tests and scans in the CI/CD pipeline. The benefits are fewer vulnerabilities reaching production, faster releases and lower cost of fixing problems.
Key takeaways
- DevSecOps builds security checks into each stage of development rather than at the end.
- Automated code and dependency scans in the pipeline are the usual first step.
- The Wikipedia definition quoted in the post is loose, so rely on practice.
According to Wikipedia:
- "DevSecOps (Development, Security and Operations) is an approach that builds security into every stage of the software delivery process, shared across development, security and operations teams. The goal of the DevSecOps movement is to achieve faster application deployment and continuous integration/deployment while maintaining a high level of security."
How does DevSecOps differ from traditional software development?
The primary difference between DevSecOps and traditional software development is the inclusion of security operations within an Agile environment. By including operational aspects into the SDLC, DevOps helps protect the business at a much higher level than traditional methods would allow. Instead of just focusing on completing a piece of code, developers now have to worry about securing their infrastructure to avoid exposing sensitive information to cyber criminals.
Benefits of DevSecOps
There are many benefits associated with DevSecOps and they range all across the board. From improved scalability and agility to reduced costs and time to market, here are some of the major advantages DevSecOps brings to the table:
- Increased Security & Efficiency - One of the biggest issues faced by companies today is poor security practices that leave them vulnerable to hackers and cyber attacks. To combat these threats, businesses need to adopt an agile software development methodology that includes security concerns from the beginning of the SDLC. In doing so, DevSecOps streamlines the implementation of secure practices that prevent data breaches and ensure the integrity of applications.
- Improved Scalability & Agility - Traditional methods rely heavily on manual tasks, whereas DevSecOps incorporates automation into its workflow to improve productivity and reduce overhead. If the methodologies being implemented aren't suitable for each company's unique situation, DevSecOps provides adaptable ways to implement the best practices.
- Reduced Costs & Time to Market - As previously mentioned, DevSecOps increases the speed of product releases by implementing automated procedures for testing, deploying, and monitoring software. These actions help prevent problems before they happen and help reduce downtime by finding potential issues earlier. Additionally, DevSecOps makes use of automation tools that reduce the amount of work required to complete certain processes and increase the likelihood of success.
- Improves Team Communication - A well-managed DevSecOps program involves having strong communication among stakeholders. Developers, testers, QA specialists, and security experts collaborate to create better products that meet customer demands. If all parties involved understand what they're working towards, then they're able to communicate effectively to get the job done.
To take this further with guided labs and an instructor, see our Certified DevSecOps Engineer training.
Related reading
- What is continuous and shift-left intrusion testing in DevSecOps and why is it important for modern security teams?
- How Security Champions & Shift‑Left Culture Are Transforming DevSecOps in 2026
- How AI‑Driven DevSecOps & AIOps Are Transforming Security Automation in 2026
Reference
For the authoritative details, see OWASP.
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0
With a passion for staying on the cutting edge of technology trends, I am dedicated to delivering content that not only informs but also inspires. Whether you need in-depth analysis pieces, informative guides, or thought-provoking opinion pieces, I craft content that resonates with tech enthusiasts and professionals alike.