Smart City Cybersecurity: Risks, Controls and a Practical Checklist
Smart cities are protected by treating connected city services as operational technology (OT): keep a full inventory of devices, separate OT networks from office IT and the internet, control remote and vendor access, patch or isolate devices that cannot be patched, monitor traffic, and rehearse incident response with the people who run the services.
Topic: Cyber Threats, Scams & Online Safety in Cybersecurity & Ethical Hacking · Explainer
Also covers: Cybersecurity Foundations
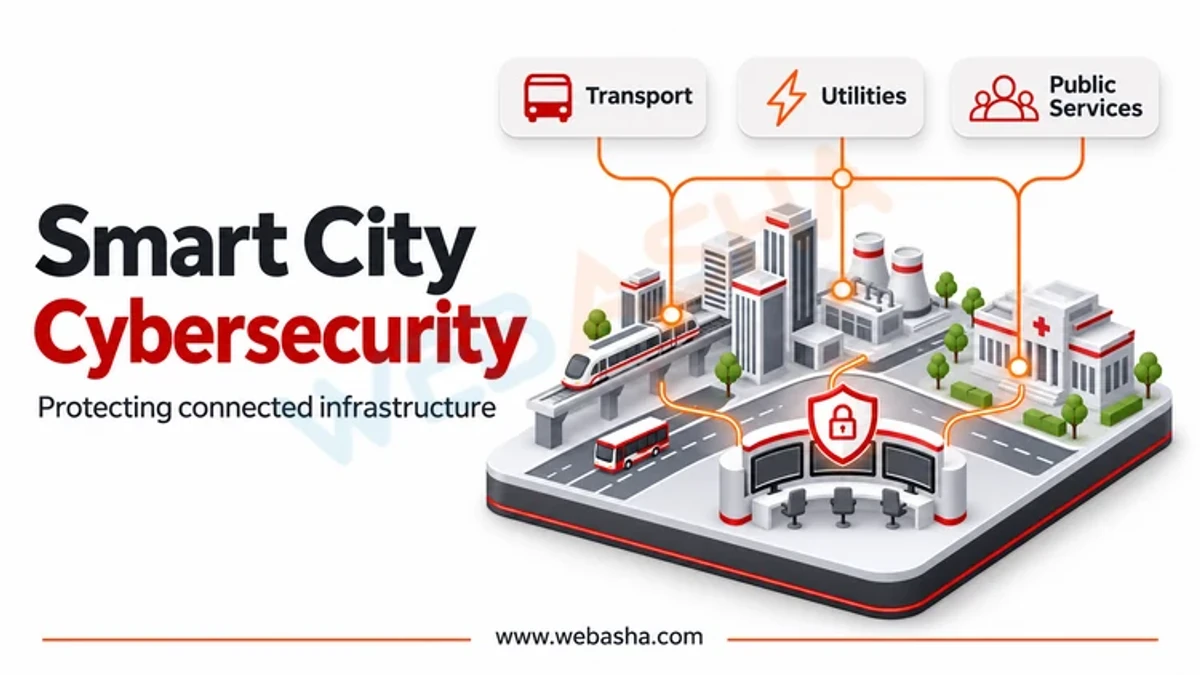
Quick answer: Smart cities are protected by treating connected city services as operational technology (OT): keep a full inventory of devices, separate OT networks from office IT and the internet, control remote and vendor access, patch or isolate devices that cannot be patched, monitor traffic, and rehearse incident response with the people who run the services. Frameworks such as NIST CSF 2.0, NIST SP 800-82 for OT and IEC 62443 give the structure, and security requirements belong in every procurement contract.
Key takeaways
- A smart city joins IT with OT, so attacks can disrupt physical services.
- You cannot protect devices you have not inventoried.
- Segmentation into zones and conduits limits how far an intruder can move.
- Vendor remote access is a frequent entry point; control and log it.
- Ransomware on city administrations is documented, for example Atlanta in 2018.
Table of Contents
- What Makes Smart Cities Hard to Secure?
- Which Systems Are Most at Risk?
- Which Frameworks Apply?
- How Does Segmentation Work in Practice?
- How Should Cities Monitor and Respond?
- What Belongs in Procurement Contracts?
- What Can Atlanta 2018 Teach?
- References
What Makes Smart Cities Hard to Secure?
City systems are built by many vendors over many years. Traffic controllers, water pumps and building systems often run old software, have long replacement cycles and cannot be rebooted at will. They are also connected to cloud dashboards and mobile apps for convenience, which opens paths from the internet to physical equipment.
Which Systems Are Most at Risk?
| System | Main risk | Priority control |
|---|---|---|
| Traffic signals and sensors | Disruption, unsafe states | Isolated network, signed firmware |
| Water and wastewater SCADA | Process tampering | OT segmentation, no direct internet access |
| CCTV and video analytics | Privacy breach, botnet use | Changed default credentials, separate VLAN |
| Public Wi-Fi | Pivot into city networks | Full separation from internal systems |
| Citizen service portals | Data theft, ransomware | MFA, patching, tested backups |
| Integrated command centres | Single point of failure | Strict access, redundancy, logging |
Which Frameworks Apply?
- NIST CSF 2.0: six functions (Govern, Identify, Protect, Detect, Respond, Recover) for the overall programme.
- NIST SP 800-82 Rev. 3: guidance specific to OT security.
- ISA/IEC 62443: zones and conduits, security levels, and requirements for component suppliers.
How Does Segmentation Work in Practice?
Group devices into zones with similar trust and function, then allow only the traffic each conduit needs. A simplified firewall policy between a traffic-control zone and the command centre:
# zone: traffic-ot (10.20.0.0/16)   zone: command-centre (10.10.5.0/24)
allow  10.10.5.10  -> 10.20.0.0/16  tcp/502     # SCADA polling from one historian only
allow  10.20.0.0/16 -> 10.10.5.10   tcp/443     # telemetry upload
deny   any         -> 10.20.0.0/16  any  log    # everything else, logged
deny   10.20.0.0/16 -> internet     any  log    # OT never browses out
Vendor access should arrive through a jump host with MFA, session recording and time-limited approval, never through a permanently open VPN.
How Should Cities Monitor and Respond?
- Collect logs from firewalls, jump hosts and servers into a SIEM.
- Use passive OT monitoring that understands industrial protocols.
- Write playbooks for ransomware, device tampering and data leaks.
- Run joint exercises with operations staff, not only IT.
- In India, report incidents to CERT-In within six hours as its April 2022 directions require.
What Belongs in Procurement Contracts?
- No default or hard-coded passwords; unique credentials per device.
- A software bill of materials and a vulnerability disclosure process.
- Security update support for the expected device lifetime.
- Logging that can be exported to the city SIEM.
- Right to security-test the product before deployment.
What Can Atlanta 2018 Teach?
In March 2018 SamSam ransomware disrupted City of Atlanta systems. The US Department of Justice later indicted two men for the SamSam campaign against hospitals, municipalities and public institutions. The lessons are ordinary ones: patch exposed services, limit remote access, and keep offline backups that are tested.
Read our zero trust guide, or talk to a WebAsha training advisor about OT and network security courses.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

With a passion for staying on the cutting edge of technology trends, I am dedicated to delivering content that not only informs but also inspires. Whether you need in-depth analysis pieces, informative guides, or thought-provoking opinion pieces, I craft content that resonates with tech enthusiasts and professionals alike.