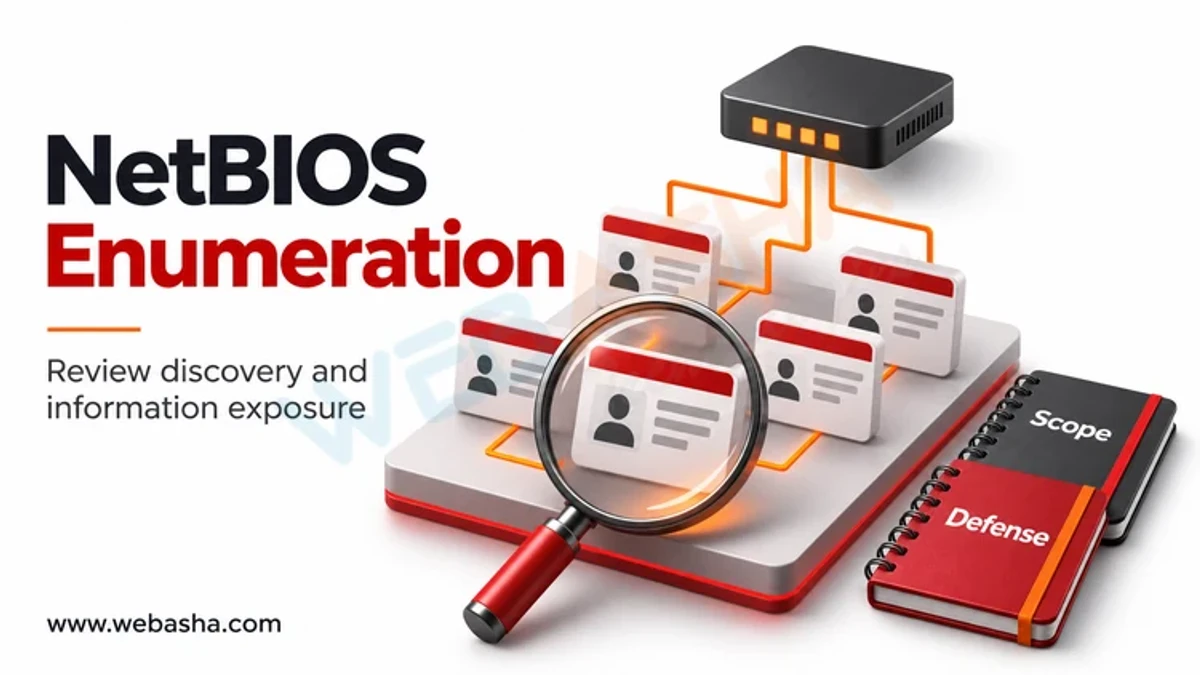
NetBIOS Enumeration Explained: Risks, Detection and Defence
NetBIOS enumeration is the process of querying the legacy NetBIOS over TCP/IP service on Windows networks to learn computer names, workgroup or domain names, running services and sometimes shared folders. Attackers use it early in an intrusion to map targets, and authorised penetration testers use it to show how much a network gives away. It relies on UDP 137 and 138 and TCP 139, defined in RFC 1001 and RFC 1002.