Types of Security Logs: A Complete Guide for Cybersecurity Monitoring
Security logs are timestamped records of events that help you detect and investigate attacks. The main types are authentication logs, operating system and endpoint logs, firewall and network logs, DNS and web proxy logs, application and web server logs, cloud audit logs, database logs, email logs and endpoint detection (EDR) telemetry.
Topic: SOC & Blue Team in Cybersecurity & Ethical Hacking · Explainer
Learning path: SOC Analyst, lesson 3 of 16
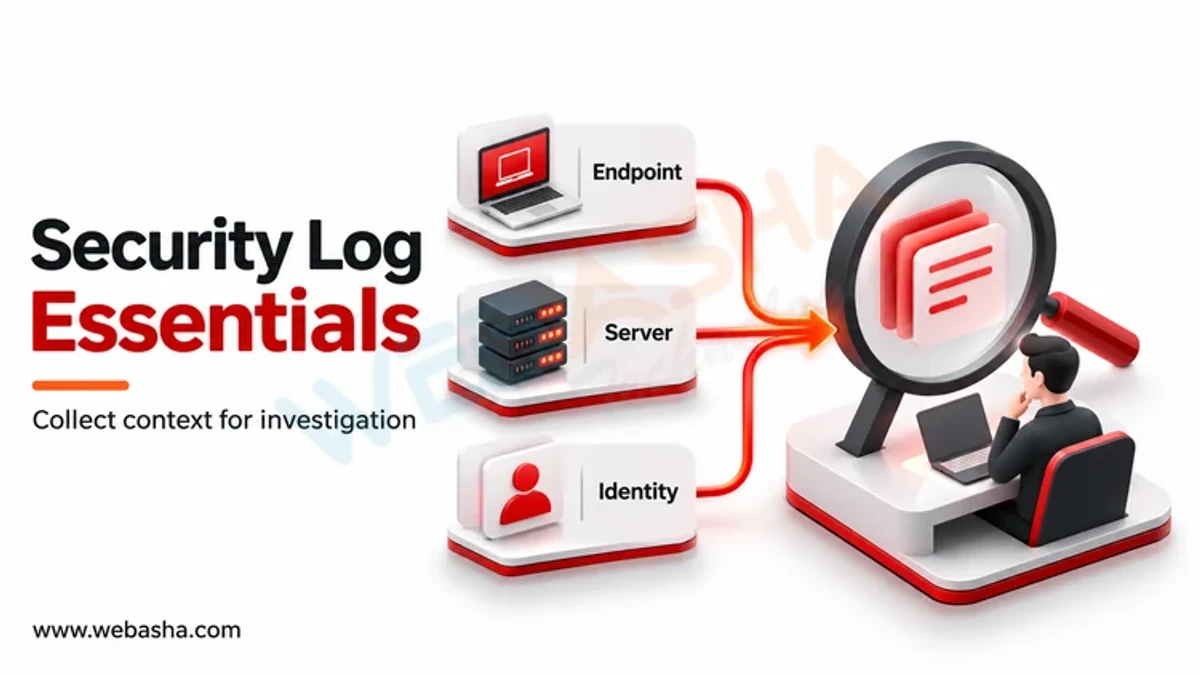
Quick answer: Security logs are timestamped records of events that help you detect and investigate attacks. The main types are authentication logs, operating system and endpoint logs, firewall and network logs, DNS and web proxy logs, application and web server logs, cloud audit logs, database logs, email logs and endpoint detection (EDR) telemetry. Each answers a different question: who logged in, what ran, what talked to what, and what changed. Collect them centrally in a SIEM, synchronise clocks, protect them from tampering, and in India keep them for at least 180 days as CERT-In directions require.
Key takeaways
- No single log type shows the whole attack; combine several.
- Authentication, endpoint and network logs give the fastest wins.
- Accurate time synchronisation makes logs usable as evidence.
- CERT-In requires 180 days of logs kept within India.
- NIST SP 800-92 and CISA guidance describe good log management.
Table of Contents
- What Are Security Logs?
- What Are the Main Types of Security Logs?
- Which Events Should You Watch First?
- How Should You Collect and Protect Logs?
- What Do Indian Rules Require?
- References
What Are Security Logs?
A log entry records what happened, when, where and who or what caused it. NIST SP 800-92 describes log management as generating, transmitting, storing, analysing and disposing of these records. Logs support alerting, incident investigation, compliance audits and troubleshooting. During an incident, NIST SP 800-61 Rev. 3 treats them as core evidence.
What Are the Main Types of Security Logs?
| Log type | Examples | What it reveals |
|---|---|---|
| Authentication | Active Directory, Entra ID, VPN, SSO | Logins, failures, MFA prompts, lockouts |
| Operating system | Windows Security log, Linux auth.log or journald | Process starts, privilege use, service changes |
| Endpoint (EDR) | EDR or Sysmon telemetry | Malicious processes, persistence, file changes |
| Firewall and network | Firewall, NetFlow, IDS | Allowed and blocked connections, scans |
| DNS and proxy | Resolver logs, web proxy | Malware callbacks, phishing domains |
| Application and web server | Apache, Nginx, IIS, app audit trails | Injection attempts, abuse of business logic |
| Cloud audit | AWS CloudTrail, Azure Activity Log, Google Cloud Audit Logs | API calls, permission changes, new keys |
| Database | Database audit logs | Bulk reads, privilege grants, schema changes |
| Mail gateway and mailbox audit | Phishing delivery, forwarding rules |
The OWASP Logging Cheat Sheet explains what application developers should record and what to leave out, such as passwords and session tokens.
Which Events Should You Watch First?
| Source | Event | Why it matters |
|---|---|---|
| Windows | 4624 and 4625 | Successful and failed logons |
| Windows | 4688 | New process created (enable command line capture) |
| Windows | 4720 and 4732 | Account created, user added to a security group |
| Windows | 1102 | Security log cleared |
| Linux | sshd entries in auth.log or journald | SSH logins and failures |
| Cloud | New access keys, disabled logging | Common attacker actions after access |
Windows events depend on advanced audit policy being enabled. On Linux you can review recent SSH activity with:
sudo journalctl -u ssh --since "24 hours ago"On some distributions the unit is named sshd instead of ssh.
How Should You Collect and Protect Logs?
- Centralise logs in a SIEM; see our guide on how SIEM works.
- Synchronise time with NTP on every system.
- Use standard formats such as syslog per RFC 5424 and forward over TLS.
- Protect integrity with restricted access and write-once or immutable storage.
- Alert on gaps, since a silent source can mean an attacker disabled logging.
- Prioritise sources, as recommended in the joint CISA event logging best practices.
What Do Indian Rules Require?
The CERT-In directions of 28 April 2022 require service providers, intermediaries, data centres and government bodies to enable logs of all their ICT systems, keep them securely for a rolling 180 days within India, and report listed incidents within 6 hours of noticing them. Logs that contain personal data must also be handled under the DPDP Act 2023. WebAsha offers practical SOC and log analysis training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.