STP Attack Explained: Spanning Tree Risks and How to Prevent Them
An STP attack abuses the Spanning Tree Protocol, which switches use to prevent loops. A device on an access port sends forged bridge protocol data units (BPDUs), claiming to be the best root bridge, or floods topology changes. The network then recalculates, traffic may flow through the rogue device, or the LAN becomes unstable and unavailable.
Topic: Networking in IT Infrastructure · Tutorial
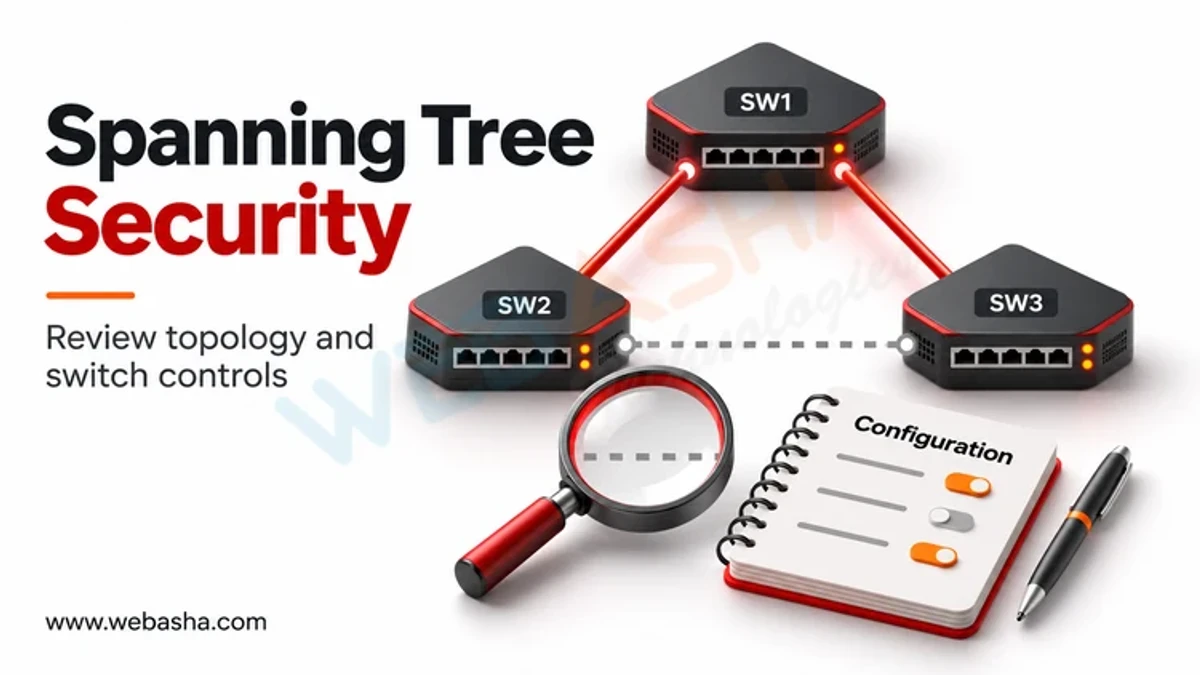
Quick answer: An STP attack abuses the Spanning Tree Protocol, which switches use to prevent loops. A device on an access port sends forged bridge protocol data units (BPDUs), claiming to be the best root bridge, or floods topology changes. The network then recalculates, traffic may flow through the rogue device, or the LAN becomes unstable and unavailable. You prevent it by setting the root bridge deliberately, enabling BPDU guard on all edge ports, applying root guard on ports that should never lead to the root, and using loop guard, storm control and monitoring of topology changes.
Key takeaways
- STP trusts BPDUs by default, which is why access ports must be protected.
- Main risks are traffic interception through a rogue root and denial of service.
- Pin the root bridge with a low priority on your core switches.
- BPDU guard on edge ports and root guard on designated ports block most abuse.
- Frequent topology change notifications are an early warning sign.
Table of Contents
- What Does Spanning Tree Do?
- What Is an STP Attack?
- What Is the Impact?
- How Do You Prevent STP Attacks?
- What Does a Hardened Configuration Look Like?
- How Do You Detect STP Problems?
- References
What Does Spanning Tree Do?
Switched networks often have redundant links. Without control, broadcast frames would loop forever. STP elects one root bridge, the switch with the lowest bridge ID, and blocks redundant paths. Switches share this information in BPDUs. Rapid PVST+ and MSTP are faster versions used today. For exam-style revision, see our CCNA STP questions.
What Is an STP Attack?
STP has no built-in authentication. If an untrusted port accepts BPDUs, a connected device can announce a better bridge ID and win the root election, or send repeated topology changes. This falls under the interception family MITRE calls Adversary-in-the-Middle, and it can also be a denial of service. A careless user plugging in a home switch can cause similar disruption without any bad intent.
What Is the Impact?
| Risk | What happens |
|---|---|
| Traffic interception | Traffic between segments may pass through the rogue root |
| Denial of service | Repeated reconvergence drops traffic and flushes MAC tables |
| Suboptimal paths | Traffic takes slow links through an access switch |
| Broadcast storms | Loops form if ports are misconfigured |
How Do You Prevent STP Attacks?
| Control | Where to apply | Effect |
|---|---|---|
| Root bridge priority | Core or distribution switches | Makes the intended root win elections |
| BPDU guard | All PortFast edge ports | Err-disables a port that receives any BPDU |
| Root guard | Designated ports toward access layer | Blocks a port that hears a superior BPDU |
| Loop guard | Non-designated ports | Prevents loops when BPDUs stop unexpectedly |
| Storm control | Access ports | Limits broadcast floods |
Avoid BPDU filter on edge ports unless you understand it, because it can hide a real loop. These controls match the least functionality and denial of service protections in NIST SP 800-53, and the NSA Network Infrastructure Security Guide recommends protecting switch ports in the same spirit.
What Does a Hardened Configuration Look Like?
A Cisco IOS example on your own switches (adjust VLANs and interfaces):
spanning-tree mode rapid-pvst
spanning-tree vlan 10,20 priority 4096
spanning-tree portfast edge default
spanning-tree portfast edge bpduguard default
!
interface GigabitEthernet1/0/48
 description downlink to access switch
 spanning-tree guard root
!
errdisable recovery cause bpduguard
errdisable recovery interval 300
How Do You Detect STP Problems?
- Run show spanning-tree root and confirm the expected root on every VLAN.
- Check show spanning-tree detail for frequent topology changes.
- Send syslog for err-disable and root guard events to your SIEM.
- Keep logs for 180 days, as the CERT-In directions require.
NIST SP 800-215 covers wider enterprise network design. Pair STP hardening with the controls in our VLAN hopping prevention guide. Testing must happen only on your own lab or with written authorisation under the IT Act 2000, Sections 43 and 66. WebAsha offers CCNA and network security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.