Virus vs Worm: What Is the Difference? Explained With a Table
A virus attaches itself to a host file or program and spreads only when that host is run or shared, so it usually needs a person to do something. A worm is a standalone program that copies itself across networks without any user action, typically by exploiting a vulnerability or weak credentials. That makes worms faster and able to reach many unpatched machines in hours.
Topic: Cybersecurity Foundations in Cybersecurity & Ethical Hacking · Comparison
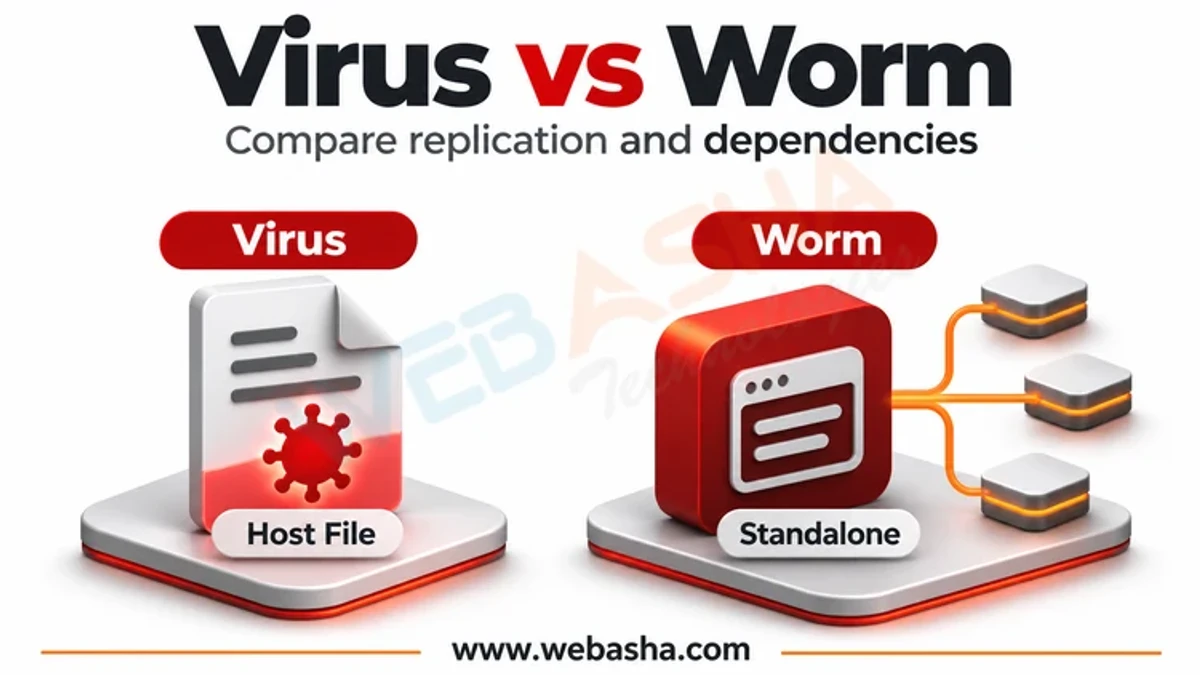
Quick answer: A virus attaches itself to a host file or program and spreads only when that host is run or shared, so it usually needs a person to do something. A worm is a standalone program that copies itself across networks without any user action, typically by exploiting a vulnerability or weak credentials. That makes worms faster and able to reach many unpatched machines in hours. WannaCry in 2017 spread as a worm through the Windows SMBv1 flaw fixed by MS17-010. Viruses are stopped mainly by macro, script and application controls; worms are stopped mainly by patching, closing exposed services and network segmentation.
Key takeaways
- Virus: needs a host and usually a user action.
- Worm: standalone and self-propagating.
- Worms spread far faster across networks.
- Patching and segmentation are the main worm defences.
- Many modern threats combine both behaviours.
Table of Contents
- How Do NIST Definitions Separate the Two?
- What Are the Differences Side by Side?
- What Do Real Examples Show?
- How Do You Tell Which One You Have?
- Which Defences Work Against Each?
- References
How Do NIST Definitions Separate the Two?
NIST describes a virus as code that replicates by infecting other programs, and a worm as a self-replicating, self-contained program that propagates through networks without needing a host. NIST SP 800-83 uses the same split. The key test is simple: does it need to live inside something else, and does it need you to run it?
What Are the Differences Side by Side?
| Point | Virus | Worm |
|---|---|---|
| Needs a host file | Yes | No |
| Needs user action | Usually | No |
| Main spread path | Shared files, documents, USB drives | Network services, weak passwords |
| Speed | Slower, follows human sharing | Fast, can be automatic |
| Typical first damage | Corrupted or modified files | Network load and mass infection |
| ATT&CK technique | User execution of infected files | T1210 Exploitation of Remote Services |
USB spreading sits between the two. Some worms copy themselves to removable drives, tracked as T1091, which still relies on a person carrying the drive.
What Do Real Examples Show?
In May 2017 WannaCry ransomware spread as a worm by exploiting SMBv1 on Windows. CISA's alert linked it to the vulnerability Microsoft had patched two months earlier in MS17-010. Machines that had installed the update were protected from the worm component. Macro viruses of the late 1990s show the virus side: they lived inside Word documents and spread when people opened and forwarded them.
The lesson from both is different. A virus outbreak follows human behaviour, so awareness and file controls slow it. A worm outbreak follows unpatched services, so the organisations hit hardest are usually those with old systems that cannot be updated quickly and flat networks where every machine can reach every other.
How Do You Tell Which One You Have?
- Signs of a worm: many hosts alerting at once, a spike in SMB, RDP or SSH connections between internal machines, new services on many hosts.
- Signs of a virus: changed executables or documents, infections that follow shared folders or USB use, alerts tied to one user opening a file.
Your endpoint tool's alert usually names the family, which settles it. Use this read-only command on Windows to check whether the legacy SMBv1 server, the protocol WannaCry abused, is still enabled:
Get-SmbServerConfiguration | Select-Object EnableSMB1ProtocolWhich Defences Work Against Each?
| Control | Helps most against |
|---|---|
| Prompt patching of network services | Worms |
| Disabling SMBv1 and closing exposed ports | Worms |
| Network segmentation and host firewalls | Worms |
| Macro blocking and application control | Viruses |
| Blocking USB autorun and scanning removable media | Both |
| Behaviour-based endpoint protection and backups | Both |
Trojans are a third category that neither replicates nor spreads alone; they rely on disguise. See types of Trojan malware for that comparison, and what a computer worm is for more on worm mechanics. Indian organisations must report worm or virus outbreaks covered by CERT-In rules within 6 hours. WebAsha offers network security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
1
 Dislike
0
 Love
1
 Funny
1
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.