What Is a CASB? How to Choose a Cloud Access Security Broker
A cloud access security broker (CASB) sits between users and cloud services to give visibility and control over how SaaS and cloud apps are used. It discovers unapproved "shadow IT", applies data loss prevention to files and messages, detects risky behaviour such as mass downloads or impossible travel, and checks app configurations against policy.
Topic: Cloud & Container Security in Cybersecurity & Ethical Hacking · Explainer
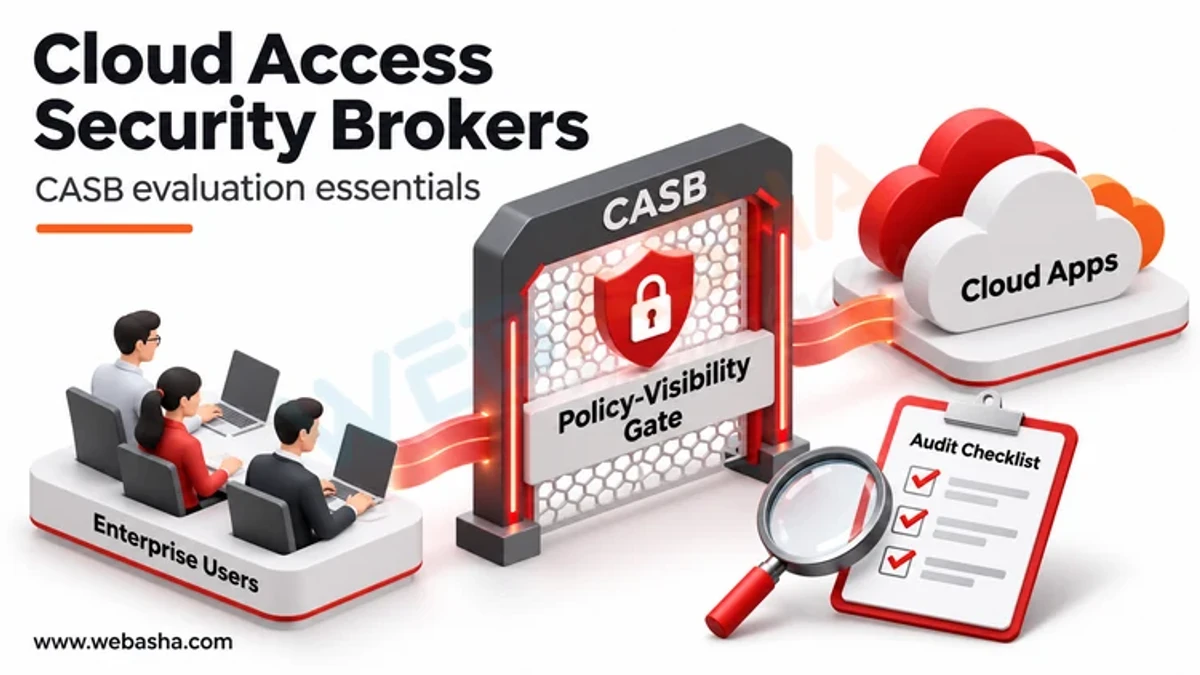
Quick answer: A cloud access security broker (CASB) sits between users and cloud services to give visibility and control over how SaaS and cloud apps are used. It discovers unapproved "shadow IT", applies data loss prevention to files and messages, detects risky behaviour such as mass downloads or impossible travel, and checks app configurations against policy. CASBs work through APIs connected to sanctioned apps, through proxies that inspect traffic in real time, or both. Today CASB is usually delivered as part of a security service edge (SSE) or SASE platform. The best choice depends on which SaaS apps you use, your identity provider, and whether you need inline control or API-based monitoring.
Key takeaways
- CASBs cover four areas: visibility, data security, threat protection and compliance.
- API mode protects data at rest in sanctioned apps; proxy mode controls activity in real time.
- CASB is now commonly part of SSE alongside secure web gateway and zero trust access.
- Start with native controls in Microsoft 365 or Google Workspace; add a CASB for multi-app coverage.
- Evaluate products against your own apps and data, not generic rankings.
Table of Contents
- What Does a CASB Do?
- How Are CASBs Deployed?
- How Do CASB, SSE and SASE Relate?
- Which Products Are Available?
- How Do You Evaluate a CASB?
- What Does a CASB Policy Look Like?
- Do You Need a CASB at All?
- References
What Does a CASB Do?
| Pillar | Capabilities |
|---|---|
| Visibility | Discover cloud apps from firewall and proxy logs; risk-score apps |
| Data security | DLP on uploads, sharing and downloads; encryption; labels |
| Threat protection | Anomalous behaviour, compromised accounts, malware in cloud storage |
| Compliance | Configuration checks, audit trails, data residency controls |
How Are CASBs Deployed?
| Mode | How it works | Strengths | Limits |
|---|---|---|---|
| API | Connects to sanctioned apps' APIs | No traffic changes; scans existing data | Near-real-time, not inline; only supported apps |
| Forward proxy | User traffic routed through the CASB via agent or network | Controls any app, including shadow IT | Needs agents or network changes |
| Reverse proxy | App login redirected through the CASB | Works for unmanaged devices | App compatibility issues |
| Log analysis | Imports firewall or proxy logs | Fast discovery of shadow IT | Visibility only |
How Do CASB, SSE and SASE Relate?
Security service edge (SSE) combines CASB with a secure web gateway and zero trust network access, delivered from the cloud. SASE adds networking (SD-WAN) to SSE. Many organisations now buy CASB capability as part of these platforms rather than as a standalone product. Google's BeyondCorp-style access is an example of zero trust access that complements CASB controls.
Which Products Are Available?
Examples include Microsoft Defender for Cloud Apps, Netskope, Palo Alto Networks Prisma Access, Zscaler, Skyhigh Security, Cisco and Forcepoint, among others. Capabilities, licensing and integrations change frequently, so compare them against your requirements rather than relying on lists of "best" products. Microsoft documents its offering in Defender for Cloud Apps.
How Do You Evaluate a CASB?
- List your critical SaaS apps and check API and inline support for each.
- Check integration with your identity provider and endpoint management.
- Test DLP accuracy on your own sample documents, including Indian identifiers such as Aadhaar and PAN formats.
- Check where data is processed and stored, for data residency and DPDP obligations.
- Measure user impact: latency, certificate issues and app breakage in proxy mode.
- Review alert quality and integration with your SIEM.
What Does a CASB Policy Look Like?
Policies combine conditions and actions. A typical example, expressed in plain form:
Policy: Block confidential downloads to unmanaged devices
  Apps:        Microsoft 365, Google Workspace, Salesforce
  Condition:   file label = "Confidential" OR DLP match = "Aadhaar number"
  Device:      not managed / not compliant
  Action:      block download, allow view in browser, notify user
  Alert:       send to SOC if more than 20 blocks per user per hour
Do You Need a CASB at All?
If you mainly use one suite, its native controls (sharing restrictions, DLP, conditional access, audit logs) may cover most needs. CISA's SCuBA baselines provide secure configuration guidance for Microsoft 365 and Google Workspace. A CASB adds value when you use many SaaS apps, need consistent policy across them, or must control shadow IT. NIST SP 800-210 covers cloud access control principles. Related: cloud security fundamentals. WebAsha offers cloud security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.