Cloud Security Fundamentals: Shared Responsibility to Best Practices
Cloud security is the set of controls that protect data, applications and infrastructure running in public, private or hybrid clouds. Its foundation is the shared responsibility model: the provider secures the underlying infrastructure, and the customer secures how they use it, including identities, data, configurations and, depending on the service model, operating systems and applications.
Topic: Cloud & Container Security in Cybersecurity & Ethical Hacking · Explainer
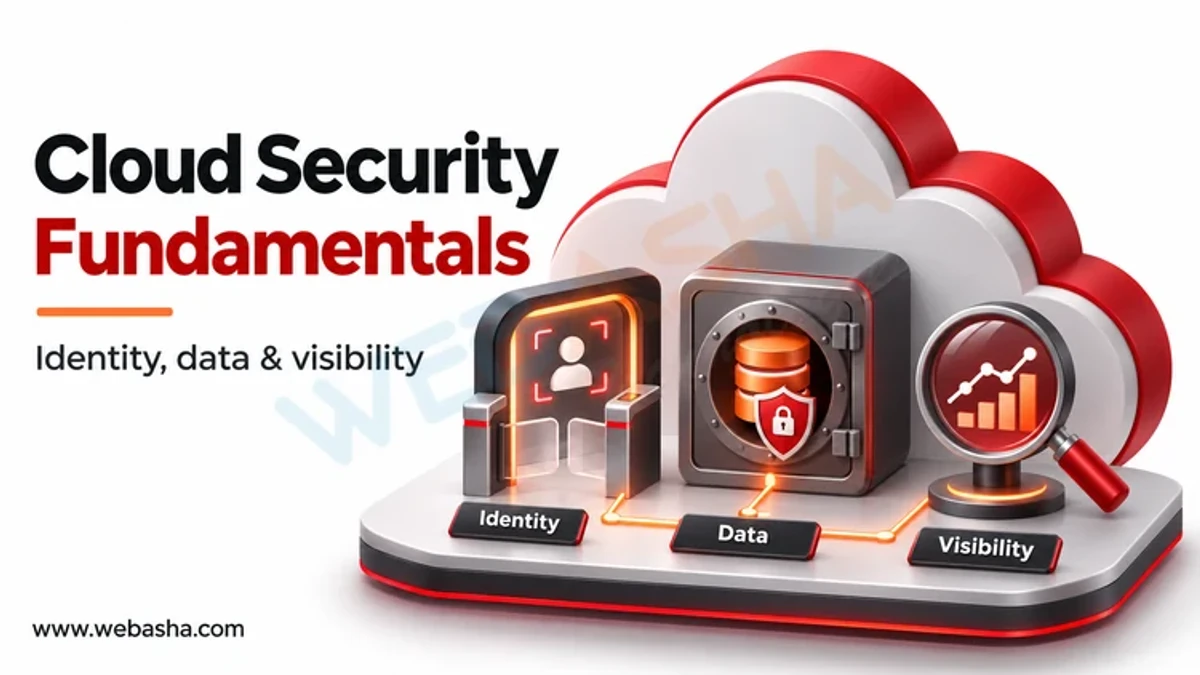
Quick answer: Cloud security is the set of controls that protect data, applications and infrastructure running in public, private or hybrid clouds. Its foundation is the shared responsibility model: the provider secures the underlying infrastructure, and the customer secures how they use it, including identities, data, configurations and, depending on the service model, operating systems and applications. The fundamentals are strong identity and access management, encryption, secure network design, workload protection, logging and monitoring, and governance through benchmarks and policy. Most cloud incidents come from customer-side mistakes such as weak credentials, excessive permissions and publicly exposed storage.
Key takeaways
- The provider secures the cloud; you secure what you put in it and how you configure it.
- Identity is the main perimeter in the cloud; protect it with MFA and least privilege.
- Turn on logging (CloudTrail, Azure Activity Logs, Cloud Audit Logs) in every account.
- Use benchmarks such as CIS and posture tools to catch misconfigurations continuously.
- CISA and NSA published ten cloud mitigation strategies in 2024 as a starting checklist.
Table of Contents
- What Is the Shared Responsibility Model?
- What Are the Core Domains of Cloud Security?
- Why Is Identity the New Perimeter?
- How Do You Protect Data in the Cloud?
- What Quick Checks Can You Run Today?
- What Do CISA and NSA Recommend?
- How Do Frameworks and Benchmarks Help?
- References
What Is the Shared Responsibility Model?
| Layer | IaaS | PaaS | SaaS |
|---|---|---|---|
| Data and access | Customer | Customer | Customer |
| Application | Customer | Customer | Provider |
| Operating system and runtime | Customer | Provider | Provider |
| Network controls | Shared | Shared | Provider |
| Physical infrastructure | Provider | Provider | Provider |
See AWS and Microsoft for each provider's version. The NIST definition of cloud computing explains the service models.
What Are the Core Domains of Cloud Security?
| Domain | Key controls |
|---|---|
| Identity and access | SSO, MFA, least privilege, no long-lived keys |
| Data protection | Encryption, key management, classification, backups |
| Network security | Private subnets, security groups, private endpoints |
| Workload security | Hardened images, patching, container scanning |
| Logging and detection | Audit logs, threat detection services, SIEM |
| Governance | Policies, benchmarks, posture management, IaC review |
For network design, see VPCs and cloud firewalls.
Why Is Identity the New Perimeter?
Cloud resources are managed through APIs reachable from anywhere, so a stolen access key or password can be as damaging as a breach of the data centre. Use single sign-on with phishing-resistant MFA, assign roles with only the permissions needed, prefer short-lived credentials over static keys, and protect the root or global administrator accounts with hardware keys and break-glass procedures. NIST SP 800-210 covers cloud access control.
How Do You Protect Data in the Cloud?
- Encrypt data at rest and in transit; use provider key management with rotation.
- Block public access to storage by default.
- Classify data and restrict sensitive data to specific accounts or regions.
- Keep backups in a separate account with immutability.
- Consider data residency requirements, such as those of Indian regulators and the DPDP Act.
What Quick Checks Can You Run Today?
# AWS: is account-wide S3 Block Public Access on?
aws s3control get-public-access-block --account-id 123456789012

# AWS: IAM users without MFA (from the credential report)
aws iam generate-credential-report >/dev/null
aws iam get-credential-report --query Content --output text | base64 -d | awk -F, '$8=="false"{print $1}'

# AWS: is CloudTrail logging in all regions?
aws cloudtrail describe-trails --query "trailList[].{Name:Name,MultiRegion:IsMultiRegionTrail}"

# Azure: storage accounts allowing public blob access
az storage account list --query "[?allowBlobPublicAccess==\`true\`].name"
What Do CISA and NSA Recommend?
In March 2024, CISA and NSA released ten cloud security mitigation strategies, covering topics including:
- Uphold the shared responsibility model.
- Use secure cloud identity and access management practices.
- Use secure cloud key management practices.
- Implement network segmentation and encryption.
- Secure data in the cloud.
- Defend continuous integration and delivery environments.
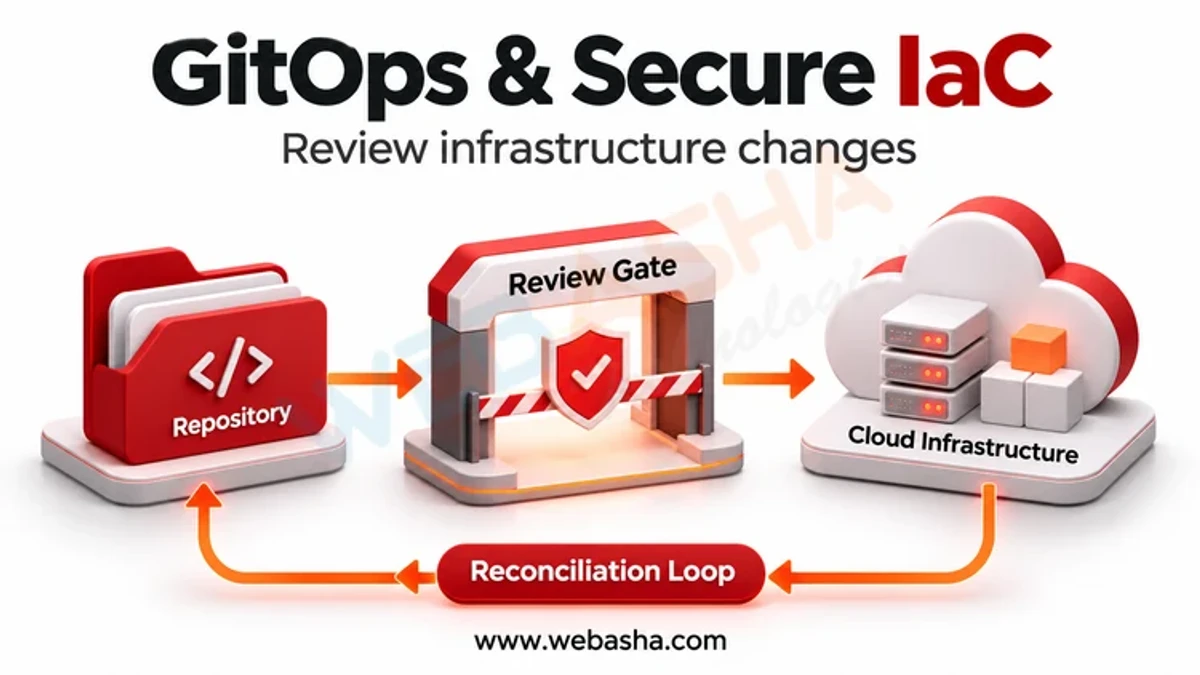
- Enforce secure automated deployment practices through infrastructure as code.
- Account for complexities of hybrid and multi-cloud environments.
- Mitigate risks from managed service providers.
- Manage cloud logs for effective threat hunting.
How Do Frameworks and Benchmarks Help?
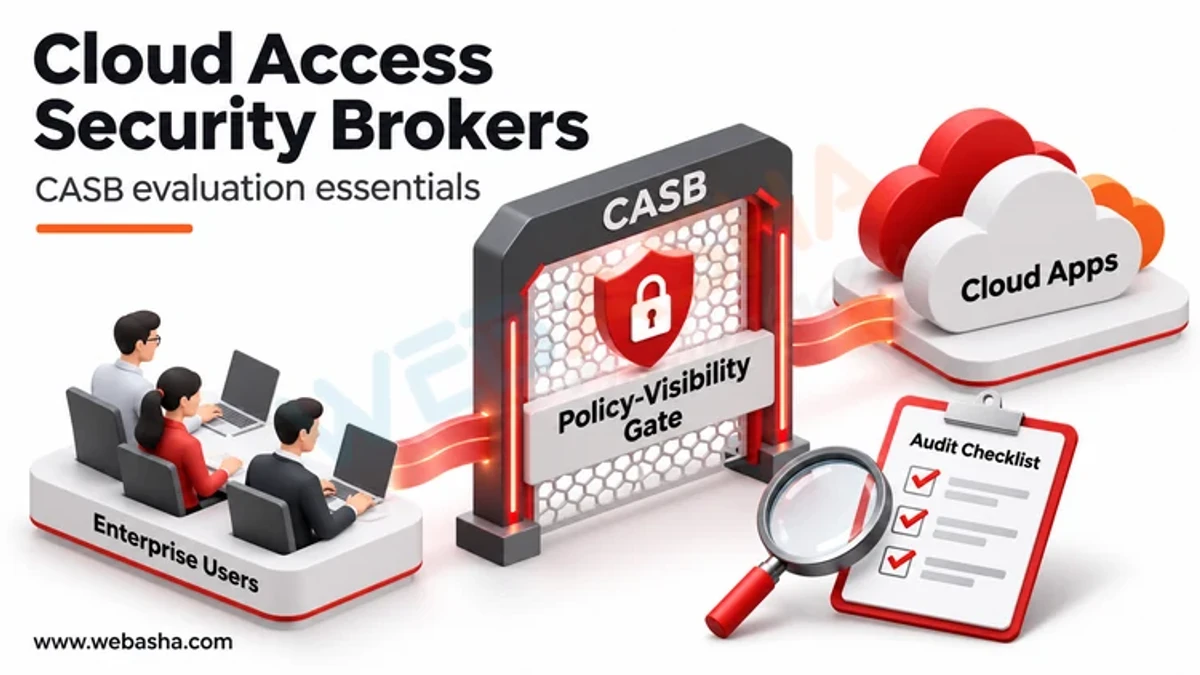
The CSA Cloud Controls Matrix maps cloud controls to standards such as ISO 27001, and CIS Benchmarks give specific configuration checks for AWS, Azure and Google Cloud. Cloud security posture management tools, including providers' own (AWS Security Hub, Microsoft Defender for Cloud, Google Security Command Center), check these continuously. Related: CASB solutions. WebAsha offers AWS and Azure security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.