What Are the Best Cybersecurity Frameworks? A Practical Comparison
There is no single best cybersecurity framework; the right one depends on your goal. NIST CSF 2.0 is a flexible, outcome-based guide organised into six functions: Govern, Identify, Protect, Detect, Respond and Recover. ISO/IEC 27001:2022 is the international standard for an information security management system and the one you can be certified against.
Topic: Cybersecurity Foundations in Cybersecurity & Ethical Hacking · Explainer
Quick answer: There is no single best cybersecurity framework; the right one depends on your goal. NIST CSF 2.0 is a flexible, outcome-based guide organised into six functions: Govern, Identify, Protect, Detect, Respond and Recover. ISO/IEC 27001:2022 is the international standard for an information security management system and the one you can be certified against. CIS Controls v8.1 gives a prioritised list of practical safeguards. COBIT covers IT governance. In India, organisations must also meet binding rules such as the CERT-In Directions, sector regulations from RBI or SEBI and the DPDP Act 2023. Many organisations combine two or more.
Key takeaways
- Frameworks are guides, standards or control lists; laws are mandatory.
- NIST CSF 2.0 added the Govern function in February 2024.
- ISO 27001 certification is often requested by clients and partners.
- CIS Controls are the most practical starting point for small teams.
- Indian regulations sit on top of any framework you choose.
Table of Contents
- What Is a Cybersecurity Framework?
- What Does NIST CSF 2.0 Offer?
- How Does ISO/IEC 27001:2022 Work?
- Why Use the CIS Controls v8.1?
- Where Do COBIT, SP 800-53 and ATT&CK Fit?
- Which Indian Rules Apply Alongside Frameworks?
- How Do You Choose the Right Framework?
- References
What Is a Cybersecurity Framework?
A framework is a structured set of practices that helps an organisation manage cyber risk consistently. Some describe outcomes, some list specific controls and some define a management system that can be audited. Using one gives a shared language for engineers, managers and auditors.
What Does NIST CSF 2.0 Offer?
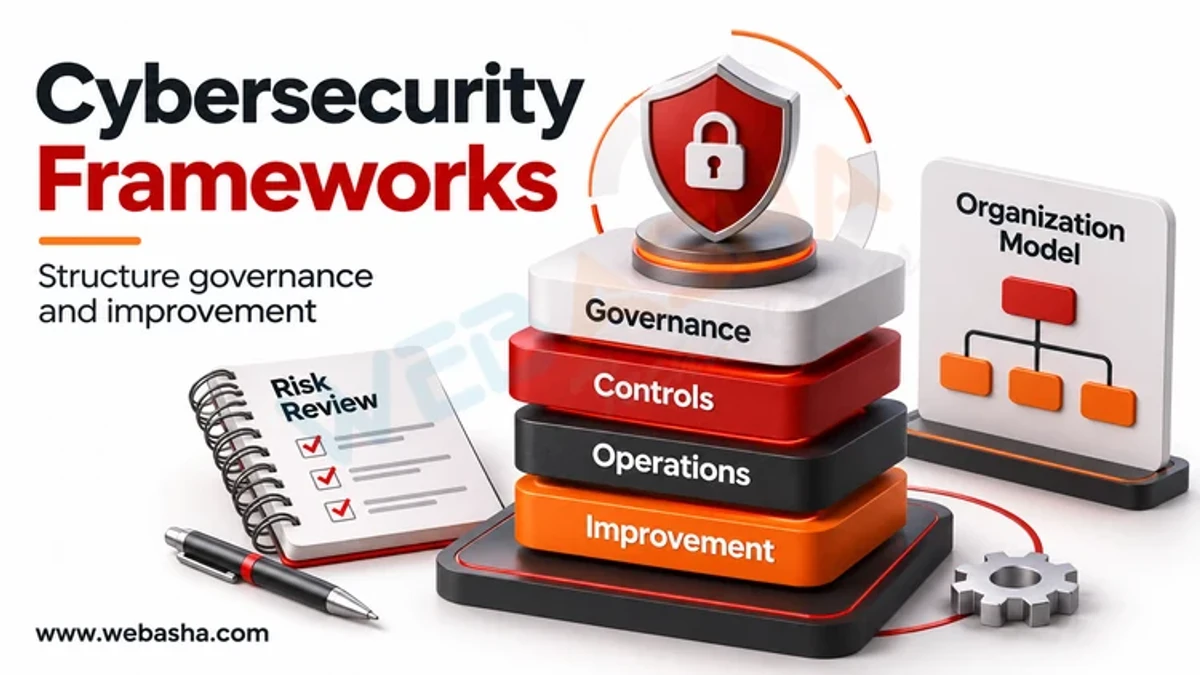
NIST released CSF 2.0 on 26 February 2024. It widened the scope from critical infrastructure to all organisations and added Govern, which covers strategy, roles, policy and supply chain risk. The six functions are Govern, Identify, Protect, Detect, Respond and Recover. CSF uses profiles and tiers so you can describe your current state, set a target and plan the gap. It is voluntary and free.
How Does ISO/IEC 27001:2022 Work?
ISO/IEC 27001:2022 defines requirements for an information security management system (ISMS): scope, risk assessment, risk treatment, internal audit and continual improvement. Annex A lists 93 controls grouped into four themes: organisational, people, physical and technological. Accredited bodies can certify an organisation, which is why clients often ask for it in contracts.
Why Use the CIS Controls v8.1?
The CIS Controls v8.1, released in June 2024, contain 18 controls broken into safeguards. Implementation Groups (IG1, IG2, IG3) tell you which safeguards to do first. IG1 is described as essential cyber hygiene for every organisation. Version 8.1 aligned its mappings with the new Govern function in NIST CSF 2.0.
Where Do COBIT, SP 800-53 and ATT&CK Fit?
| Framework | Type | Best use |
|---|---|---|
| COBIT | IT governance framework | Board-level governance and audit alignment |
| NIST SP 800-53 Rev. 5 | Detailed control catalogue | Large or government systems needing deep controls |
| MITRE ATT&CK | Knowledge base of attacker techniques | Detection engineering and threat-informed defence |
ATT&CK is not a compliance framework, but it shows whether your controls actually stop real techniques.
Which Indian Rules Apply Alongside Frameworks?
- CERT-In Directions (April 2022): report specified incidents within 6 hours, keep ICT logs for 180 days and synchronise clocks.
- RBI IT governance master direction: board oversight, IT risk management and assurance for regulated entities.
- SEBI cyber security requirements: for market intermediaries.
- DPDP Act 2023: reasonable security safeguards for personal data.
- IT Act 2000: offences such as unauthorised access under Sections 43 and 66.
How Do You Choose the Right Framework?
| If you are... | Start with | Add later |
|---|---|---|
| A small business or startup | CIS Controls IG1 | NIST CSF profile |
| Selling services to global clients | ISO/IEC 27001 | CIS Controls for technical depth |
| A bank or NBFC in India | RBI directions plus CERT-In | ISO 27001, NIST CSF |
| A large enterprise | NIST CSF 2.0 for strategy | SP 800-53, COBIT, ATT&CK |
| A student | NIST CSF and CIS Controls | ISO 27001 basics |
Map controls once and reuse evidence across frameworks to avoid duplicate work. Learn more in our NIST Cybersecurity Framework guide and our article on risk management in cybersecurity. WebAsha also runs ISO 27001 and GRC training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.