Top 10 DNS Attack Types: Examples, Techniques and Prevention
The main DNS attacks are cache poisoning and spoofing (forged answers that send users to fake sites), DNS hijacking (changing a domain's records or registrar settings), DNS tunnelling (hiding data or command traffic inside DNS queries), domain generation algorithms used by malware, DNS amplification DDoS, random-subdomain (NXDOMAIN) floods against DNS servers, subdomain takeover via dangling records, typosquatting…
Topic: Networking in IT Infrastructure · Explainer
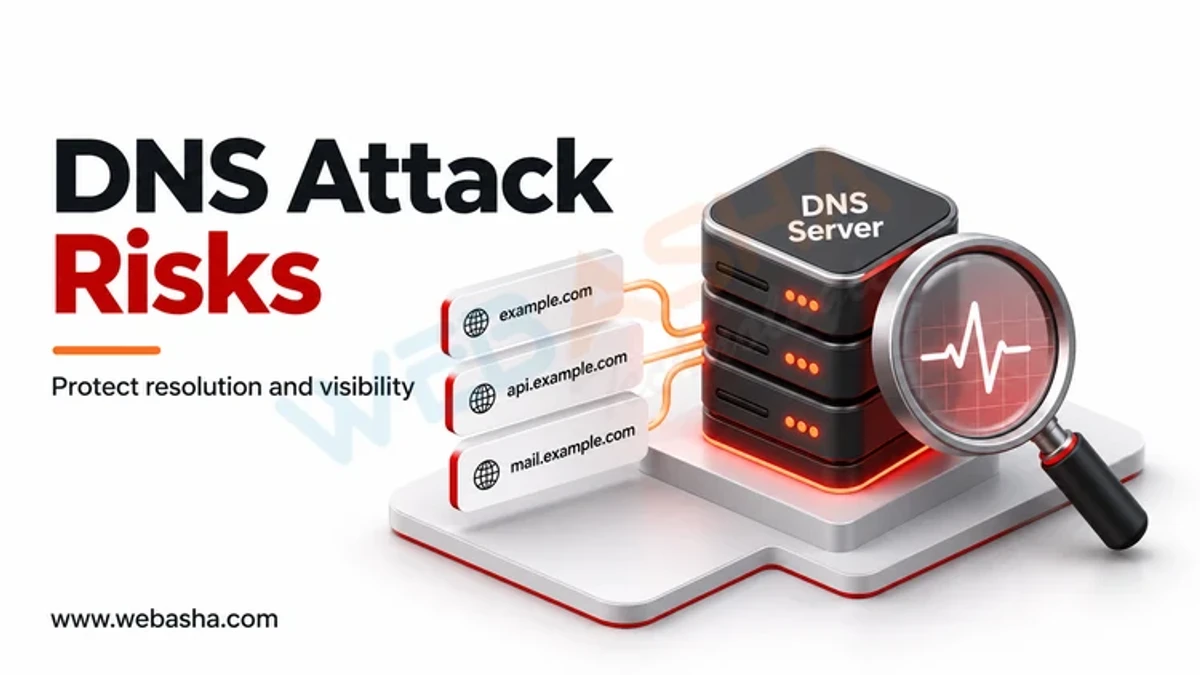
Quick answer: The main DNS attacks are cache poisoning and spoofing (forged answers that send users to fake sites), DNS hijacking (changing a domain's records or registrar settings), DNS tunnelling (hiding data or command traffic inside DNS queries), domain generation algorithms used by malware, DNS amplification DDoS, random-subdomain (NXDOMAIN) floods against DNS servers, subdomain takeover via dangling records, typosquatting and lookalike domains, and rogue or compromised resolvers. Defences include DNSSEC, registrar locks and MFA, monitoring DNS logs, rate limiting and response policy zones, removing dangling records, and encrypted DNS to trusted resolvers.
Key takeaways
- DNS is used both to attack users and as a hidden channel for malware.
- Registrar account security (MFA, locks) prevents domain hijacking.
- DNSSEC lets resolvers detect forged answers.
- DNS query logs are one of the best sources for detecting malware.
- Remove DNS records before deleting the cloud resources they point to.
Table of Contents
- What Are the Top 10 DNS Attacks?
- How Do Poisoning and Hijacking Work?
- How Do Attackers Abuse DNS for Command and Control?
- How Do DNS DDoS Attacks Work?
- How Do You Detect DNS Attacks?
- What Is the DNS Hardening Checklist?
- How Do Protective DNS and RPZ Help?
- References
What Are the Top 10 DNS Attacks?
| # | Attack | Defence |
|---|---|---|
| 1 | Cache poisoning | DNSSEC validation, source port randomisation (RFC 5452) |
| 2 | DNS spoofing on local networks | Encrypted DNS, DNSSEC, network protections |
| 3 | Domain and record hijacking | Registrar lock, MFA, change monitoring |
| 4 | DNS tunnelling (T1071.004) | Query analysis, block direct DNS from clients |
| 5 | Domain generation algorithms (T1568.002) | Threat feeds, anomaly detection |
| 6 | DNS amplification DDoS | No open resolvers, response rate limiting |
| 7 | Random subdomain / NXDOMAIN floods | Rate limiting, DNS provider DDoS protection |
| 8 | Subdomain takeover | Remove dangling records |
| 9 | Typosquatting and lookalike domains | Defensive registrations, monitoring, takedowns |
| 10 | Rogue or compromised resolvers | Trusted resolvers, DHCP snooping, router security |
How Do Poisoning and Hijacking Work?
Cache poisoning inserts a forged answer into a resolver's cache so many users are redirected. DNSSEC (RFC 4033) signs records so validating resolvers reject forgeries. Hijacking instead changes the authoritative records, often by compromising registrar or DNS hosting accounts. In 2019, CISA issued Emergency Directive 19-01 after a DNS infrastructure tampering campaign, requiring US agencies to audit records, change passwords and add MFA. See also DNS poisoning explained.
How Do Attackers Abuse DNS for Command and Control?
Malware can encode data in subdomains of an attacker's domain, so queries carry stolen data out and responses carry commands in. Signs include long or random-looking labels, high query volumes to one domain, and unusual record types such as TXT. Malware using domain generation algorithms tries many pseudo-random domains until one resolves.
How Do DNS DDoS Attacks Work?
Amplification attacks send small queries with a spoofed victim address to open resolvers, which reply with much larger responses to the victim. Random-subdomain floods send queries for nonexistent names to exhaust authoritative servers. Operators should not run open resolvers, should enable response rate limiting, and should use DNS providers with DDoS protection.
How Do You Detect DNS Attacks?
# Find unusually long query names in Zeek DNS logs (possible tunnelling)
zeek-cut query < dns.log | awk 'length($1) > 60' | sort | uniq -c | sort -rn | head

# Domains with the most unique subdomains queried
zeek-cut query < dns.log | awk -F. '{print $(NF-1)"."$NF}' | sort | uniq -c | sort -rn | head

# Check DNSSEC validation for a domain
dig +dnssec example.com | grep -E "flags|RRSIG"
What Is the DNS Hardening Checklist?
- Enable registrar lock and MFA on registrar and DNS hosting accounts.
- Sign zones with DNSSEC and validate on resolvers.
- Force clients to use internal or trusted resolvers; block direct outbound DNS.
- Log DNS queries and send them to your SIEM.
- Remove dangling records, per Microsoft's guidance.
- Use encrypted DNS (DoH or DoT) to trusted resolvers for roaming devices.
Related: DNS attacks for SOC teams. WebAsha offers network security training.
How Do Protective DNS and RPZ Help?
Protective DNS services block lookups of known malicious domains before connections happen. Organisations can run their own using Response Policy Zones (RPZ) in resolvers such as BIND or Unbound, fed by threat intelligence. CISA offers a Protective DNS service for US federal agencies, and the UK NCSC runs a similar PDNS service for public sector bodies.
# Unbound: block a malicious domain locally (example configuration snippet)
server:
    local-zone: "bad-example.top." always_nxdomain
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.