What Are the Steps of the APT Lifecycle? Guide to Persistent Threats
An advanced persistent threat (APT) is a well-resourced adversary that gains long-term access to a target to steal data or prepare for disruption.
Topic: Cyber Threats, Scams & Online Safety in Cybersecurity & Ethical Hacking · Tutorial
Also covers: Ethical Hacking, Penetration Testing
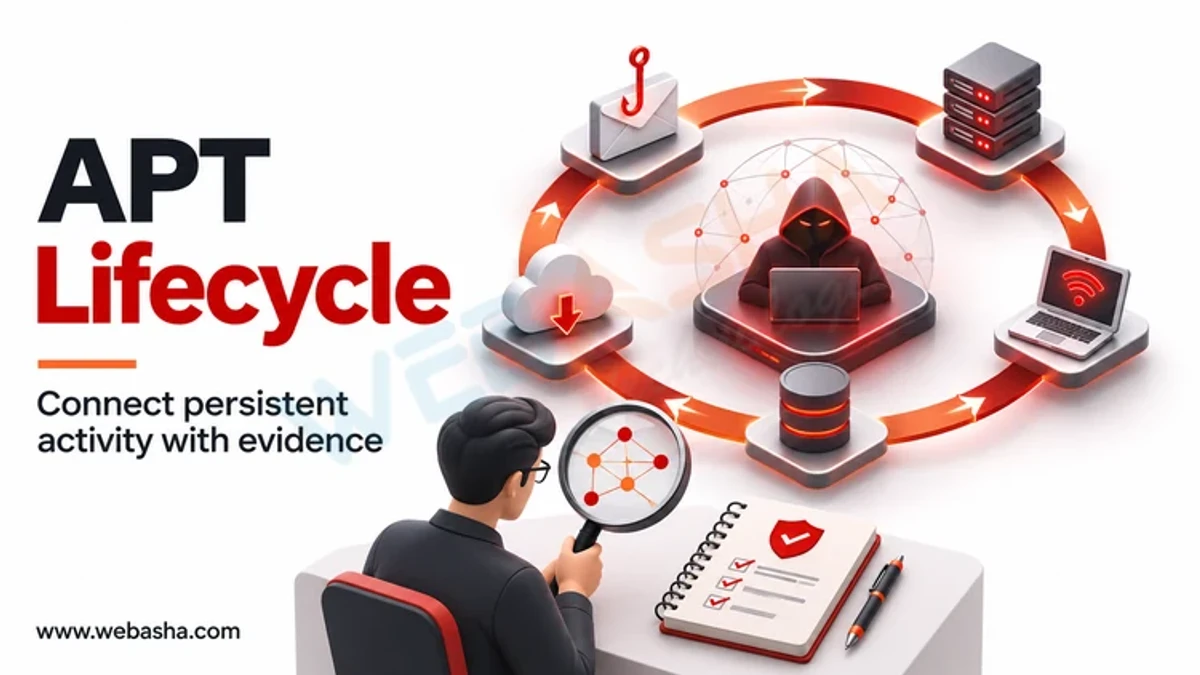
Quick answer: An advanced persistent threat (APT) is a well-resourced adversary that gains long-term access to a target to steal data or prepare for disruption. Its lifecycle usually runs through seven steps: reconnaissance, initial access, establishing a foothold and persistence, privilege escalation and credential theft, internal discovery and lateral movement, collection and exfiltration or impact, and maintaining access while evading defences. Each step maps to MITRE ATT&CK tactics. A documented example is Volt Typhoon: CISA advisory AA24-038A reports that this PRC state-sponsored group kept access to some US critical infrastructure networks for at least five years using built-in tools.
Key takeaways
- APTs aim for long dwell time, not quick damage.
- Each lifecycle step maps to ATT&CK tactics you can detect.
- Living off the land makes malicious activity look like administration.
- Identity and logging are the strongest defences.
- Rely on official advisories for attribution, not rumours.
Table of Contents
- What Is an Advanced Persistent Threat?
- What Are the Steps of the APT Lifecycle?
- What Can Defenders See at Each Step?
- What Does a Documented APT Campaign Look Like?
- How Do You Detect APT Activity?
- How Do You Reduce APT Risk?
- How Should You Respond to a Suspected APT?
- References
What Is an Advanced Persistent Threat?
NIST describes an APT as an adversary with sophisticated expertise and significant resources that pursues its objectives over an extended period, adapts to defenders, and works to keep its access. Many APTs are state-linked. MITRE tracks known groups and their techniques on its ATT&CK Groups pages.
What Are the Steps of the APT Lifecycle?
| Step | Goal | MITRE ATT&CK tactics |
|---|---|---|
| 1. Reconnaissance | Learn about the target | Reconnaissance, Resource Development |
| 2. Initial access | Get a first entry point | Initial Access, Execution |
| 3. Foothold | Survive reboots and password resets | Persistence, Command and Control |
| 4. Privilege escalation | Gain admin and steal credentials | Privilege Escalation, Credential Access |
| 5. Lateral movement | Find and reach valuable systems | Discovery, Lateral Movement |
| 6. Objective | Steal data or prepare disruption | Collection, Exfiltration, Impact |
| 7. Maintain and evade | Stay hidden over time | Defense Evasion, Persistence |
The steps are not strictly linear; attackers loop back as they find new systems. Tactic names follow the ATT&CK Enterprise matrix. Our Kill Chain vs ATT&CK comparison explains how these models relate.
What Can Defenders See at Each Step?
- Initial access: exploitation attempts on VPNs, firewalls and other edge devices; phishing.
- Foothold: new services, scheduled tasks, web shells, unusual outbound connections.
- Privilege escalation: access to LSASS memory, attempts to copy the Active Directory database.
- Lateral movement: remote logons from unusual hosts, admin tools run by unexpected accounts.
- Exfiltration: large or compressed uploads, traffic to new cloud storage.
What Does a Documented APT Campaign Look Like?
CISA and partner agencies published advisory AA24-038A on 7 February 2024 about Volt Typhoon, a PRC state-sponsored group.
| Lifecycle step | What the advisory describes |
|---|---|
| Initial access | Exploiting vulnerabilities in internet-facing network devices |
| Privilege escalation | Obtaining administrator credentials and targeting domain controllers |
| Maintain and evade | Living off the land with built-in tools to blend with normal activity |
| Objective | Pre-positioning for possible disruption of critical infrastructure |
The advisory states the actors kept access in some environments for at least five years.
How Do You Detect APT Activity?
CISA's living off the land guidance recommends behaviour baselines, detailed logging and proactive hunting. On Windows, enabling PowerShell script block logging and reviewing process creation events helps. A defender can check recent remote desktop logons with:
Get-WinEvent -FilterHashtable @{LogName='Security'; Id=4624} -MaxEvents 200 | Where-Object { $_.Properties[8].Value -eq 10 }Logon type 10 indicates remote interactive logons. Review them against expected admin activity.
How Do You Reduce APT Risk?
- Patch edge devices first and remove unsupported ones.
- Use phishing-resistant MFA and separate admin accounts.
- Segment networks and restrict admin protocols.
- Centralise logs and keep them; CERT-In requires 180 days in India.
- Map detections to ATT&CK; see our guide on defending with ATT&CK.
How Should You Respond to a Suspected APT?
Avoid alerting the attacker before you understand the scope. Preserve evidence, scope all affected accounts and hosts, then evict in a coordinated step, as described in NIST SP 800-61 Rev. 3. Indian organisations must report qualifying incidents to CERT-In within six hours under the April 2022 directions. Any testing of these defences needs written authorisation under the IT Act 2000, Sections 43 and 66. WebAsha offers threat hunting and incident response training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.