
Privilege escalation Articles, Guides & Tutorials
Broken Access Control Explained: How IDOR Bugs Are Found and Fixed
This detailed blog explores a real-world exploitation of Broken Access Control vulnerability reported on HackerOne that resulted in a $5000 bounty. It dives deep into how the researcher discovered insecure privilege e...
Top 10 Active Directory Attack Methods and How to Defend Against Them
Discover the top 10 Active Directory attacks like Kerberoasting, pass-the-hash, and LLMNR poisoning, plus expert tips to secure your AD environment.
Top 10 Active Directory Attack Methods and How to Defend Against Them
Discover the top 10 Active Directory attacks like Kerberoasting, pass-the-hash, and LLMNR poisoning, plus expert tips to secure your AD environment.
Top Active Directory Attack Techniques in 2026 and How to Stop Them | The Detailed Guide
Discover the most common Active Directory attack methods in 2026 like Kerberoasting, Pass-the-Hash, and BloodHound recon. Learn practical, beginner-friendly defenses to secure your domain controllers and stop attacker...
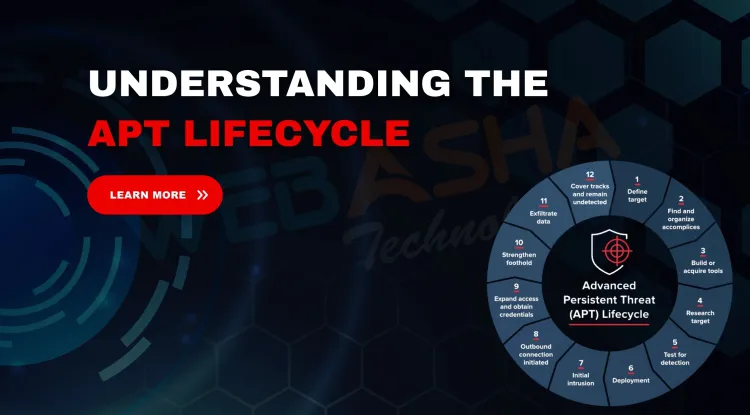
What Are the Steps of the APT Lifecycle? Full Guide to Advanced Persistent Threats
Learn the 7 critical steps of the Advanced Persistent Threat (APT) lifecycle, including reconnaissance, privilege escalation, lateral movement, and data exfiltration. Ideal for cybersecurity professionals and ethical ...
Msfvenom and Metasploit Payloads: How They Work and How Defenders Detect Them
This blog provides a detailed guide on how to create a payload using Msfvenom, its various uses in cybersecurity, and the role of Msfconsole in managing the payloads. It also covers how to send the created payload to ...
VMware Tools and CrushFTP Security Flaws With No Workaround | How to Protect Your Systems
Recent cybersecurity threats have emerged with the discovery of high-risk vulnerabilities in VMware Tools and CrushFTP. The VMware Tools authentication bypass vulnerability (CVE-2025-22230) allows non-administrative u...
Zoom Patches Four High-Severity Vulnerabilities | How Attackers Exploit Them and How to Stay Safe
Zoom recently patched five security vulnerabilities, four of which were classified as high severity. These flaws, identified as CVE-2025-27440, CVE-2025-27439, CVE-2025-0151, and CVE-2025-0150, could allow attackers t...
Which Penetration Testing Method is Best? Black Box, White Box, or Grey Box?
Penetration testing is an important cybersecurity practice that helps identify and fix security vulnerabilities before attackers can exploit them. The three main types of penetration testing, Black Box, White Box, and...

The Role of Cobalt Strike in Advanced Penetration Testing | Overview, Features, and Why Ethical Hackers Use It
Cobalt Strike is an essential tool for ethical hackers and penetration testers who need to simulate advanced cyberattacks and test the security of systems in a realistic manner. Its powerful features, including post-e...

Exploiting Android Applications with Drozer| Overview, Features, and How Ethical Hackers Use It
Drozer is an invaluable tool for ethical hackers focused on securing Android applications. Its features allow penetration testers to test for a variety of vulnerabilities, from insecure data storage to privilege escal...

PUMAKIT Linux Rootkit | A New Threat That Hides in Plain Sight
PUMAKIT Linux Rootkit is a newly discovered, sophisticated malware targeting Linux systems. This stealthy rootkit integrates into the Linux kernel as a Loadable Kernel Module (LKM), using advanced techniques like syst...

[2026] Top VAPT Post-Exploitation Techniques Interview Questions
Discover essential VAPT post-exploitation techniques interview questions and answers. Learn about persistence, privilege escalation, data exfiltration, and network mapping techniques. Prepare for your cybersecurity in...









