How to Implement Zero Trust: Pillars, Maturity Stages and a Roadmap
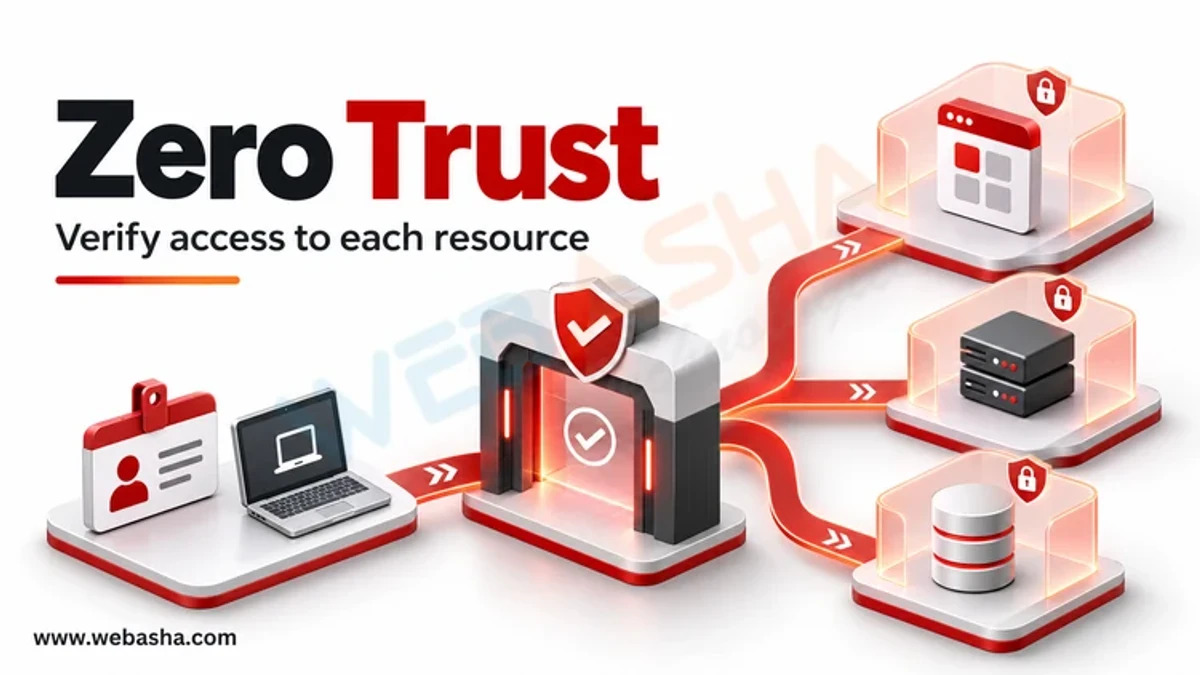
Zero trust enhances enterprise security by checking every access request against identity, device health and context, and granting only the access needed. To implement it, follow CISA's Zero Trust Maturity Model v2.0: assess your current stage across five pillars (identity, devices, networks, applications and workloads, data), then move each pillar from Traditional towards Initial, Advanced and Optimal.
Topic: Active Directory & Identity Security in Cybersecurity & Ethical Hacking · Explainer
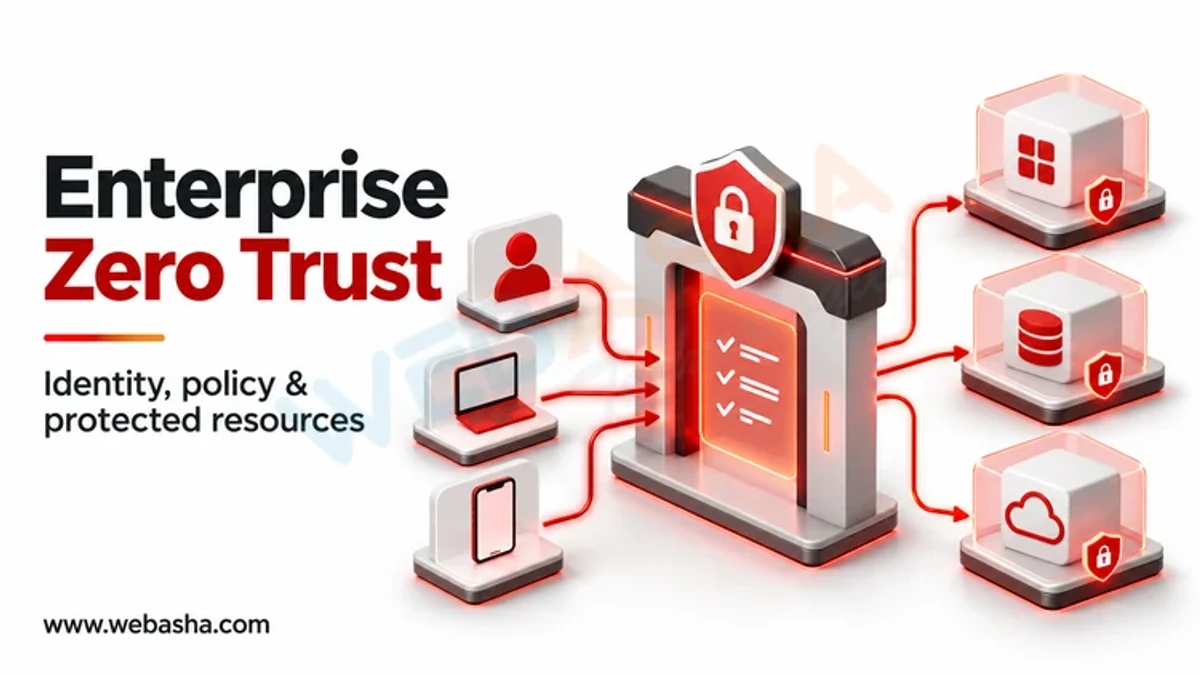
Quick answer: Zero trust enhances enterprise security by checking every access request against identity, device health and context, and granting only the access needed. To implement it, follow CISA's Zero Trust Maturity Model v2.0: assess your current stage across five pillars (identity, devices, networks, applications and workloads, data), then move each pillar from Traditional towards Initial, Advanced and Optimal. Most organisations start with strong identity and phishing-resistant MFA, add device compliance checks, replace broad VPN access with per-application access, then segment networks and classify data.
Key takeaways
- CISA's model has five pillars and three cross-cutting capabilities.
- Maturity moves through Traditional, Initial, Advanced and Optimal stages.
- Identity is the usual starting point.
- Progress pillar by pillar; a full switch-over at once is rarely practical.
- Measure progress with a self-assessment repeated each quarter.
Table of Contents
- What Are the Five Pillars?
- What Are the Maturity Stages?
- What Does a Phased Roadmap Look Like?
- How Do You Enforce Identity and Device Checks?
- How Do You Segment the Network?
- How Do You Measure Progress?
- References
What Are the Five Pillars?
| Pillar | Example controls |
|---|---|
| Identity | Single sign-on, phishing-resistant MFA, risk-based access |
| Devices | Inventory, compliance checks, endpoint detection and response |
| Networks | Microsegmentation, encrypted traffic, per-application access |
| Applications and workloads | Secure development, application-level authorisation, workload identity |
| Data | Classification, encryption, data loss prevention, access logging |
Across all pillars sit visibility and analytics, automation and orchestration, and governance, as described in the CISA Zero Trust Maturity Model v2.0.
What Are the Maturity Stages?
| Stage | Identity pillar example |
|---|---|
| Traditional | Passwords, some MFA, static access |
| Initial | MFA widely used, some automation of access lifecycle |
| Advanced | Phishing-resistant MFA, access tied to device and risk |
| Optimal | Continuous validation and fully automated just-in-time access |
What Does a Phased Roadmap Look Like?
- Discover: inventory users, devices, applications and data flows; pick protect surfaces such as payroll or customer data.
- Identity first: single sign-on for all apps, phishing-resistant MFA for admins and finance.
- Device trust: require managed, encrypted, patched devices for sensitive apps.
- Access: replace broad VPN access with per-application access through a proxy or gateway.
- Segment: microsegment data centre and cloud workloads.
- Data: classify, encrypt and monitor sensitive data.
- Automate: feed signals to a SIEM and automate responses.
NIST's NCCoE publishes example builds in SP 1800-35.
How Do You Enforce Identity and Device Checks?
In Microsoft Entra ID, a conditional access policy can require MFA and a compliant device for a sensitive application. The shape of the policy in the Microsoft Graph format:
{
  "displayName": "Payroll: require MFA and compliant device",
  "state": "enabledForReportingButNotEnforced",
  "conditions": {
    "users": { "includeGroups": ["<payroll-users-group-id>"] },
    "applications": { "includeApplications": ["<payroll-app-id>"] },
    "clientAppTypes": ["all"]
  },
  "grantControls": {
    "operator": "AND",
    "builtInControls": ["mfa", "compliantDevice"]
  }
}
Starting in report-only mode shows who would be blocked before you enforce it.
How Do You Segment the Network?
Allow only the flows each workload needs. A Kubernetes network policy that lets only the web tier reach the payroll API:
apiVersion: networking.k8s.io/v1
kind: NetworkPolicy
metadata:
  name: payroll-api-from-web-only
  namespace: payroll
spec:
  podSelector:
    matchLabels: { app: payroll-api }
  policyTypes: ["Ingress"]
  ingress:
  - from:
    - podSelector:
        matchLabels: { app: payroll-web }
    ports:
    - { protocol: TCP, port: 8443 }
How Do You Measure Progress?
Score each pillar every quarter and track the trend:
STAGES = ["Traditional", "Initial", "Advanced", "Optimal"]
current = {"Identity": 2, "Devices": 1, "Networks": 1, "Applications": 1, "Data": 0}
target  = {"Identity": 3, "Devices": 2, "Networks": 2, "Applications": 2, "Data": 1}

for pillar, now in current.items():
    gap = target[pillar] - now
    print(f"{pillar:13} {STAGES[now]:12} -> {STAGES[target[pillar]]:12} gap {gap}")
For the concepts behind this, read what zero trust architecture is and why it matters and AI in zero trust, or talk to a WebAsha training advisor.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.