Apple Native Containers on macOS: What Changes for Security Labs
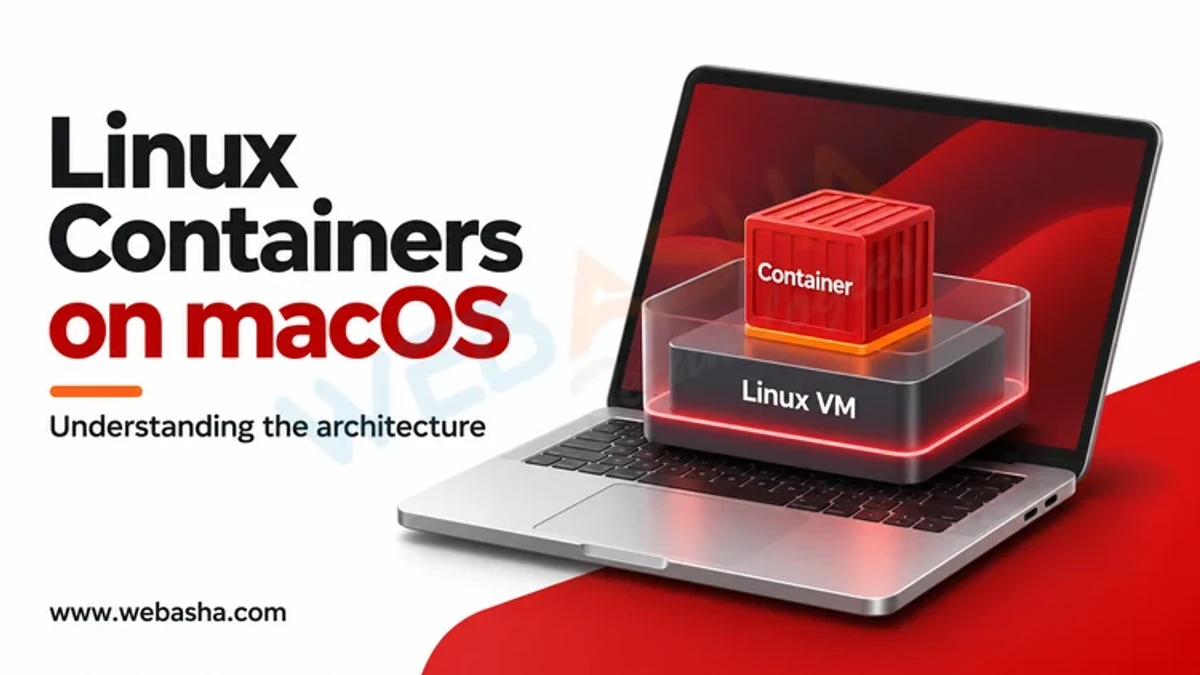
Apple's open-source container tool, built on its Swift Containerization framework, runs standard OCI Linux container images on Apple silicon Macs. Unlike Docker Desktop, which runs all containers inside one shared Linux virtual machine, it gives each container its own lightweight VM, which improves isolation between containers.
Topic: Security Tools, Authorized Labs & CTFs in Cybersecurity & Ethical Hacking · Explainer
Also covers: Containers: Docker & Podman
Quick answer: Apple's open-source container tool, built on its Swift Containerization framework, runs standard OCI Linux container images on Apple silicon Macs. Unlike Docker Desktop, which runs all containers inside one shared Linux virtual machine, it gives each container its own lightweight VM, which improves isolation between containers. For security learners it makes command-line Linux tools, including the official Kali image, quick to start on a Mac. It does not replace a full Kali VM for desktop tools, wireless adapters or low-level network labs.
Key takeaways
- It needs an Apple silicon Mac; Intel Macs are not supported.
- Apple targets macOS 26; macOS 15 works with limitations, per the README.
- One lightweight VM per container gives stronger isolation than a shared VM.
- It uses standard OCI images, so Docker Hub images such as Kali work.
- Keep a full VM for GUI tools, USB Wi-Fi adapters and complex lab networks.
Table of Contents
- What Did Apple Release?
- How Does It Compare With Docker Desktop and a VM?
- What Does Per-Container Isolation Mean for Security?
- What Works Well for Security Labs?
- What Are the Limits?
- How Do the Commands Compare With Docker?
- How Do You Control Resources and Clean Up?
- References
What Did Apple Release?
At WWDC in June 2025 Apple published two open-source projects: Containerization, a Swift framework, and container, a command-line tool built on it. They use Apple's Virtualization framework to start a small Linux VM for each container, with a minimal init system and fast boot.
How Does It Compare With Docker Desktop and a VM?
| Apple container | Docker Desktop | Full VM (UTM, Parallels, VMware) | |
|---|---|---|---|
| Isolation model | One lightweight VM per container | All containers share one Linux VM | One complete OS per VM |
| Image format | OCI | OCI | Disk images and installers |
| Desktop apps | No built-in GUI | No built-in GUI | Full desktop |
| USB devices such as Wi-Fi adapters | Not supported | Not on macOS | Usually supported |
| Compose and ecosystem tools | Limited | Mature | Not applicable |
| Platform | Apple silicon, macOS 26 target | macOS, Windows, Linux | Varies |
What Does Per-Container Isolation Mean for Security?
In a shared VM, containers rely on Linux namespaces and cgroups for separation, so a kernel escape can reach every container in that VM. With one VM per container, an escape lands inside a VM holding only that container. That is useful when running untrusted tools or samples, though a VM boundary is still not a reason to run live malware outside a dedicated analysis setup.
# each running container is its own VM; list them and inspect one
container ls
container inspect kali

# compare: Docker Desktop shows one Linux VM kernel for all containers
docker run --rm alpine uname -r
What Works Well for Security Labs?
- Command-line tools: Nmap, sqlmap, John the Ripper, Hashcat (CPU), Python tooling.
- Quick, disposable environments for practising commands.
- Running vulnerable web apps such as OWASP Juice Shop locally.
- Scripting and automation work against lab targets.
The official Kali image is documented on kali.org. Our Kali on macOS guide walks through installation and first commands.
What Are the Limits?
- No graphical desktop, so tools such as Burp Suite's GUI or Wireshark's GUI need another setup.
- No USB passthrough for wireless adapters, so Wi-Fi testing needs a full VM or separate machine.
- Newer and less mature than Docker, with fewer integrations.
- Issues on macOS 15 may not be fixed, per the project README.
To build a full penetration testing lab, see learning Kali Linux or talk to a WebAsha training advisor.
How Do the Commands Compare With Docker?
The container CLI deliberately feels familiar to Docker users:
| Task | Apple container | Docker |
|---|---|---|
| Start the runtime | container system start | Start Docker Desktop |
| Pull an image | container image pull docker.io/kalilinux/kali-rolling | docker pull kalilinux/kali-rolling |
| Run interactively | container run -it IMAGE bash | docker run -it IMAGE bash |
| List running | container ls | docker ps |
| Shell into running | container exec -it NAME bash | docker exec -it NAME bash |
| Build from a Dockerfile | container build -t NAME . | docker build -t NAME . |
Exact flags can change between releases, so check container --help on your installed version.
How Do You Control Resources and Clean Up?
Because each container is a VM, giving it CPU and memory limits matters more than with shared-kernel containers. The project README shows resource flags on run:
# give a tool-heavy Kali container 4 CPUs and 8 GB of memory
container run --name kali --cpus 4 --memory 8g -it docker.io/kalilinux/kali-rolling:latest bash

# clean up when finished
container stop kali
container rm kali
# list and remove images with the image subcommand; see: container image --help

# stop the runtime entirely
container system stop
Remove images you no longer need; security tool images grow large once metapackages are installed.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.