Canon DSLR Cameras Can Be Hacked Remotely With Ransomware
The threat of ransomware is turning into more prevalent and severe as attackers’ focus has currently moved on the far side computers to smartphones and different Internet-connected smart devices.
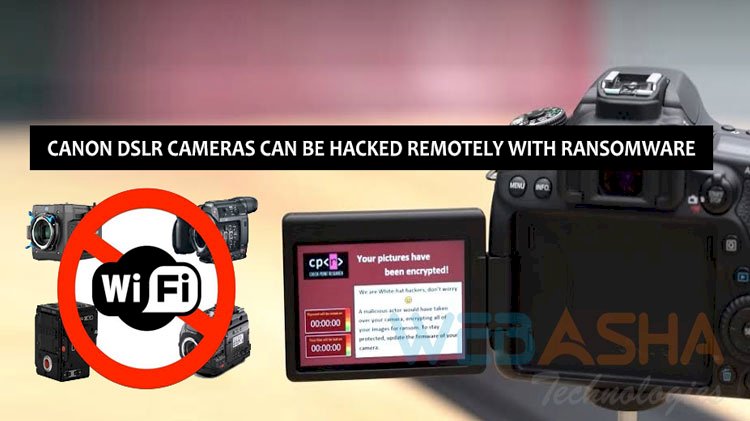
Quick answer: Security researcher Eyal Itkin found vulnerabilities in the Picture Transfer Protocol used by Canon DSLR cameras. Over Wi-Fi or USB, an attacker could install malicious firmware that encrypts photos and demands a ransom. The demo shows that ransomware can target any connected device as well as computers. Update camera firmware and turn off Wi-Fi when unused.
Key takeaways
- The attack abused the Picture Transfer Protocol, which accepts commands over Wi-Fi or USB with no authentication.
- Update camera firmware and switch off Wi-Fi when you do not need it.
- This shows that PCs and any other connected device can carry exploitable protocol flaws.
In its latest analysis, security researchers at cybersecurity firm stop incontestable however straightforward it’s for hackers to remotely infect a digital DSLR camera with ransomware and hold non-public photos and videos hostage until victims pay a ransom.
Security scientist Eyal Itkin discovered many security vulnerabilities within the computer code of Canon cameras which will be exploited over each USB and wifi, allowing attackers to compromise and take over the camera and its features.
According to a security advisory released by Canon, the reported security flaws affect Canon EOS-series digital SLR and mirrorless cameras, PowerShot SX740 HS, PowerShot SX70 HS, and PowerShot G5X Mark II.
“Imagine however would you respond if attackers inject ransomware into each your laptop and therefore the camera, causing them to hold all of your pictures hostage unless you pay a ransom,” Itkin warns.
Canon DSLR PTP and Firmware Vulnerabilities
All these vulnerabilities, listed below, reside in the way Canon implements Picture Transfer Protocol (PTP) in its firmware, a standard protocol that modern DSLR cameras use to transfer files between camera and computer or mobile devices via wired (USB) or wirelessly (WiFi).
Besides file transfer, Picture Transfer Protocol also supports dozens of commands to remotely handle many other tasks on camera, from taking live pictures to upgrading the camera’s firmware, many of which have been found vulnerable.
CVE-2019-5994: Buffer Overflow in SendObjectInfo
CVE-2019-5998: Buffer Overflow in NotifyBtStatus
CVE-2019-5999: Buffer Overflow in BLERequest
CVE-2019-6000: Buffer Overflow in SendHostInfo
CVE-2019-6001: Buffer Overflow in SetAdapterBatteryReport
CVE-2019-5995: Silent Malicious Firmware Update
Itkin found that Canon’s PTP operations neither require authentication nor use encryption in any way, allowing attackers to compromise the DSLR camera in the following scenarios:
Via USB: Malware that has already compromised your PC can propagate into your camera as soon as you connect it with your computer using a USB cable.
Over wifi: an attacker in shut proximity to a targeted DSLR camera will came upon a rogue wifi access point to infect your camera.
“This can be easily achieved by first sniffing the network and then faking the AP to have the same name as the one the camera automatically attempts to connect. Once the attacker is within the same LAN as the camera, he can initiate the exploit,” Itkin explains.
Exploiting Canon DSLR Flaw to Deploy Ransomware Over-the-Air
As a proof-of-concept, the researcher successfully exploited one of these vulnerabilities that allowed them to push and install a malicious firmware update on a targeted DSLR camera over WiFi, with no interaction required from the victim.
As shown within the video demonstration, the malicious firmware was modified to encrypt all files on the camera and display a ransom demand on its screen using the same built-in AES functions that Canon uses to protect its firmware.
“There is a PTP command for a remote firmware update, which requires zero user interaction,” the researcher explains. “This means although all of the implementation vulnerabilities area unit patched, an attacker can still infect the camera using a malicious firmware update file.”
A real ransomware attack of this kind is one of the most important threats to your precious reminiscences wherever hackers will usually demand cash in exchange for the decoding key that would unlock your photos, videos and audio files.
Researchers responsibility reportable these vulnerabilities to Canon in March this year. However, the corporate has presently only discharged an updated computer code for Canon eos 80D model and suggested users of other affected models to follow basic security practices until patches for their devices become available.
To take this further with guided labs and an instructor, see our online cyber security training.
Related reading
- The Power of Smart Cameras in Cybersecurity | 5 Benefits You Should Know
- Inside Trident Spyware | How iPhones Get Hacked via Zero-Click Attacks
- Bluetooth Flaws Could Let Hackers Spy Through Your Microphone | Vulnerabilities in Airoha Chips Explained
Reference
For the authoritative details, see CVE.
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0
With a passion for staying on the cutting edge of technology trends, I am dedicated to delivering content that not only informs but also inspires. Whether you need in-depth analysis pieces, informative guides, or thought-provoking opinion pieces, I craft content that resonates with tech enthusiasts and professionals alike.