What Is a Honeypot in Cybersecurity and How Does It Detect Attacks?
A honeypot is a decoy system, service or piece of data set up to attract attackers. Because it has no legitimate business use, any connection or login attempt is suspicious, which makes honeypots a high-signal, low-noise way to detect intruders. Low-interaction honeypots imitate services such as SSH to log attempts; high-interaction honeypots are real systems that let researchers watch attacker behaviour.
Topic: Cyber Threats, Scams & Online Safety in Cybersecurity & Ethical Hacking · Explainer
Also covers: SOC & Blue Team
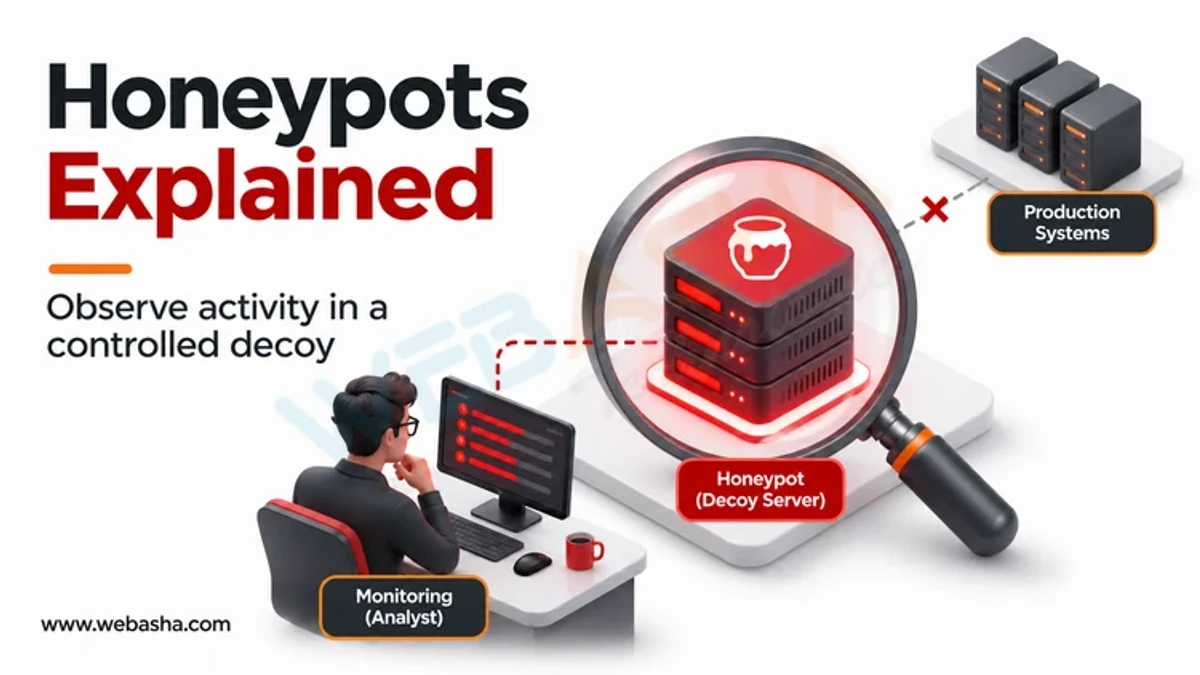
Quick answer: A honeypot is a decoy system, service or piece of data set up to attract attackers. Because it has no legitimate business use, any connection or login attempt is suspicious, which makes honeypots a high-signal, low-noise way to detect intruders. Low-interaction honeypots imitate services such as SSH to log attempts; high-interaction honeypots are real systems that let researchers watch attacker behaviour. Inside networks, decoy servers, fake credentials (honeytokens) and canary files can reveal a breach early. Honeypots must be isolated and monitored so attackers cannot use them to reach real systems.
Key takeaways
- Any interaction with a honeypot is suspicious, so alerts are highly reliable.
- Internal decoys detect lateral movement that other tools miss.
- Honeytokens such as fake admin accounts are cheap and effective.
- Research honeypots reveal attacker techniques and new malware.
- Isolation and monitoring are essential to avoid creating a new risk.
Table of Contents
- What Is a Honeypot?
- What Types of Honeypots Exist?
- What Are Honeytokens and Canaries?
- How Do Honeypots Help Detect Attacks?
- How Do You Deploy a Honeypot Safely?
- What Are the Risks and Legal Considerations?
- What Does a Simple Internal Deception Setup Look Like?
- How Do You Measure Deception Value?
- References
What Is a Honeypot?
NIST's glossary defines a honeypot as a system or system resource designed to be attractive to potential attackers and intruders. The broader practice of deception, including decoys and engagement, is described in MITRE Engage.
What Types of Honeypots Exist?
| Type | Description | Use |
|---|---|---|
| Low-interaction | Emulates services with limited responses | Logging scans and login attempts |
| Medium-interaction | Emulates a shell or service in more depth, such as Cowrie | Capturing commands and downloads |
| High-interaction | Real systems, heavily monitored | Research into attacker behaviour |
| Production (internal) | Decoys inside the corporate network | Early breach detection |
| Research (internet-facing) | Exposed to collect threat data | Threat intelligence |
What Are Honeytokens and Canaries?
- Fake credentials placed in scripts or memory; any use triggers an alert.
- Decoy admin accounts in Active Directory monitored for login attempts; Microsoft Defender for Identity supports honeytoken tagging.
- Canary files such as "passwords.xlsx" that alert when opened.
- Fake API keys in code repositories that alert if used.
How Do Honeypots Help Detect Attacks?
Attackers who get inside a network scan and explore. A decoy file server or database that real users never touch will only see attacker traffic, so an alert is almost always meaningful. Internet-facing honeypots run by groups such as the Honeynet Project collect data on scanning campaigns, credential attacks and malware, which feeds threat intelligence.
How Do You Deploy a Honeypot Safely?
- Define the goal: internal detection or external research.
- Place internal decoys where attackers explore, such as server subnets.
- Isolate external honeypots in a separate network with strict outbound controls.
- Send all honeypot logs to the SIEM with high-priority alerts.
- Make decoys believable: realistic names, services and data that is fake.
- Review and refresh regularly.
Platforms such as T-Pot bundle many honeypots with dashboards for research use.
What Are the Risks and Legal Considerations?
- A compromised honeypot could be used to attack others if outbound traffic is not restricted.
- Decoys must not contain real personal or business data.
- Captured data may include attackers' and third parties' information; handle it under applicable law, including India's DPDP Act.
- Honeypots detect; they do not replace patching and other controls.
Related: insider threat detection and free SIEM tools. WebAsha offers SOC analyst training.
What Does a Simple Internal Deception Setup Look Like?
| Decoy | Placement | Alert trigger |
|---|---|---|
| Fake file server share | Server subnet | Any SMB connection |
| Decoy admin account | Active Directory | Any authentication attempt |
| Canary document | Finance share | Document opened |
| Fake cloud access key | Code repository | Key used in API call |
Send alerts to the SIEM at high priority and include them in incident playbooks. MITRE's ATT&CK T1087 (account discovery) and T1135 (network share discovery) describe the attacker behaviours these decoys catch.
How Do You Measure Deception Value?
- Time from decoy interaction to analyst response.
- Number of true positives versus false alerts.
- Red team exercises: did decoys detect the testers?
The NIST CSF 2.0 Detect function provides a way to report this coverage.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.