What Is a Virtual Private Cloud (VPC)? How It Secures Cloud Networks
A Virtual Private Cloud (VPC) is a logically isolated private network inside a public cloud. You choose its IP address range, divide it into subnets, control routing with route tables, and decide which parts can reach the internet.
Topic: Cloud Computing: AWS, Azure & GCP in IT Infrastructure · Explainer
Also covers: Cloud & Container Security
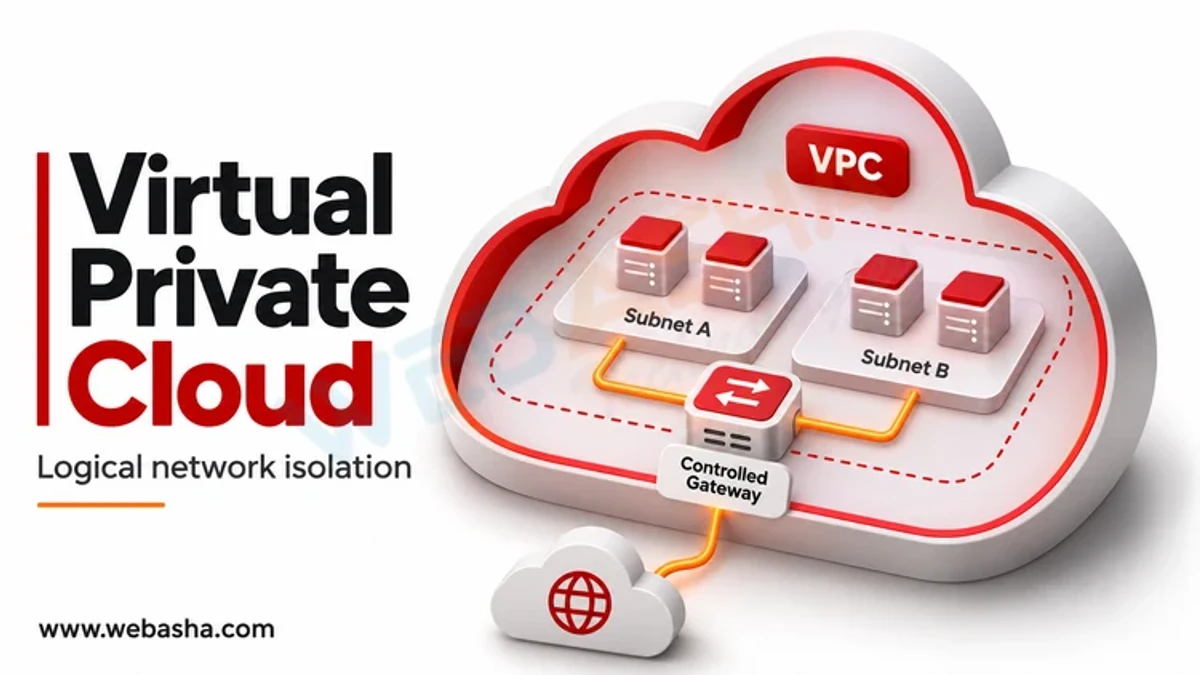
Quick answer: A Virtual Private Cloud (VPC) is a logically isolated private network inside a public cloud. You choose its IP address range, divide it into subnets, control routing with route tables, and decide which parts can reach the internet. It secures workloads by keeping them on private addresses by default, filtering traffic with security groups or firewall rules, routing outbound traffic through NAT, reaching cloud services through private endpoints, and recording traffic with flow logs. AWS and Google Cloud call it a VPC; Azure calls it a Virtual Network (VNet).
Key takeaways
- A VPC is isolated from other customers' networks by the provider's virtualisation layer.
- Public subnets have a route to an internet gateway; private subnets do not.
- NAT gateways let private servers download updates without being reachable from the internet.
- AWS VPCs and Azure VNets are regional; a Google Cloud VPC is global with regional subnets.
- Most VPC breaches come from misconfiguration: open security groups or public storage, not broken isolation.
Table of Contents
- What Is a VPC?
- What Are the Components of a VPC?
- How Does Traffic Flow In and Out?
- How Do AWS, Azure and Google Cloud Differ?
- How Do You Build a Basic VPC?
- How Do VPCs Connect to Each Other?
- What Is the VPC Security Checklist?
- What Are Common Use Cases?
- References
What Is a VPC?
In a traditional data centre, you buy switches and routers and assign address ranges. In a VPC, the cloud provider runs the physical network and gives you a software-defined slice of it. NIST SP 800-145 describes this shared, on-demand model of cloud computing. You define the network in an API or console, and it is ready in seconds.
What Are the Components of a VPC?
| Component | Purpose |
|---|---|
| CIDR block | Private address range, such as 10.20.0.0/16 |
| Subnets | Smaller ranges tied to an availability zone (AWS) or region (GCP, Azure) |
| Route tables | Decide where traffic from a subnet goes |
| Internet gateway | Two-way path to the internet for resources with public IPs |
| NAT gateway | Outbound-only internet access for private subnets |
| Security groups / NSGs / firewall rules | Stateful traffic filters |
| Network ACLs (AWS) | Stateless subnet filters |
| Endpoints / Private Link | Private access to cloud services without the internet |
| Flow logs | Records of accepted and rejected traffic |
The AWS VPC guide explains each component in detail.
How Does Traffic Flow In and Out?
- Internet to web server: internet gateway, then a load balancer in a public subnet, then the security group, then the server in a private subnet.
- Private server to the internet: route table sends 0.0.0.0/0 to the NAT gateway, which uses its public address.
- Server to cloud storage: a gateway or interface endpoint keeps traffic on the provider's network.
- Between subnets: the local route allows it, and security groups decide whether it is permitted.
How Do AWS, Azure and Google Cloud Differ?
| AWS VPC | Azure VNet | Google Cloud VPC | |
|---|---|---|---|
| Scope | Regional | Regional | Global |
| Subnet scope | One availability zone | Region (spans zones) | Region |
| Traffic filter | Security groups, NACLs | NSGs | VPC firewall rules, policies |
| Private service access | VPC endpoints, PrivateLink | Private endpoints, service endpoints | Private Service Connect, Private Google Access |
| Connect networks | Peering, Transit Gateway | Peering, Virtual WAN | Peering, Shared VPC, NCC |
See Azure Virtual Network and Google Cloud VPC documentation.
How Do You Build a Basic VPC?
This AWS CLI sequence creates a VPC with one public and one private subnet in Mumbai:
REGION=ap-south-1
VPC=$(aws ec2 create-vpc --cidr-block 10.20.0.0/16 --region $REGION --query Vpc.VpcId --output text)
PUB=$(aws ec2 create-subnet --vpc-id $VPC --cidr-block 10.20.1.0/24 --availability-zone ${REGION}a --query Subnet.SubnetId --output text)
PRIV=$(aws ec2 create-subnet --vpc-id $VPC --cidr-block 10.20.2.0/24 --availability-zone ${REGION}a --query Subnet.SubnetId --output text)

# Internet gateway and public route
IGW=$(aws ec2 create-internet-gateway --query InternetGateway.InternetGatewayId --output text)
aws ec2 attach-internet-gateway --vpc-id $VPC --internet-gateway-id $IGW
RT=$(aws ec2 create-route-table --vpc-id $VPC --query RouteTable.RouteTableId --output text)
aws ec2 create-route --route-table-id $RT --destination-cidr-block 0.0.0.0/0 --gateway-id $IGW
aws ec2 associate-route-table --route-table-id $RT --subnet-id $PUB

# Flow logs to CloudWatch (log group and IAM role must exist)
aws ec2 create-flow-logs --resource-type VPC --resource-ids $VPC --traffic-type ALL \
  --log-group-name vpc-flow --deliver-logs-permission-arn arn:aws:iam::123456789012:role/flowlogs
The private subnet keeps the main route table with only the local route until you add a NAT gateway. In production, use two or more availability zones and define all of this in Terraform or CloudFormation.
How Do VPCs Connect to Each Other?
- Peering: a direct link between two VPCs; not transitive.
- Transit hub: AWS Transit Gateway or Azure Virtual WAN for many networks.
- PrivateLink / Private Service Connect: expose one service, not the whole network.
- VPN or dedicated circuits: to on-premises networks.
What Is the VPC Security Checklist?
- Put application servers and databases in private subnets.
- No security group allows SSH or RDP from 0.0.0.0/0.
- Use endpoints for storage and other managed services.
- Turn on flow logs and send them to your SIEM.
- Avoid overlapping CIDR ranges so you can connect networks later.
- Remove the default VPC in regions you do not use, or leave it empty.
- Review changes through infrastructure-as-code pull requests.
What Are Common Use Cases?
Hosting multi-tier web applications, isolating development from production, extending a corporate network to the cloud, and meeting compliance requirements that demand network segmentation. Read cloud firewalls and NSGs next, or prepare with cloud networking interview questions. WebAsha runs AWS and Azure training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.