DevOps Security Best Practices: Challenges, Controls and Tools
DevOps security protects the whole delivery system, not just the application: source code, the CI/CD platform, dependencies, secrets, container images, infrastructure as code, Kubernetes clusters and production runtime.
Topic: DevOps & Platform Engineering in IT Infrastructure · Tools
Also covers: Cloud & Container Security
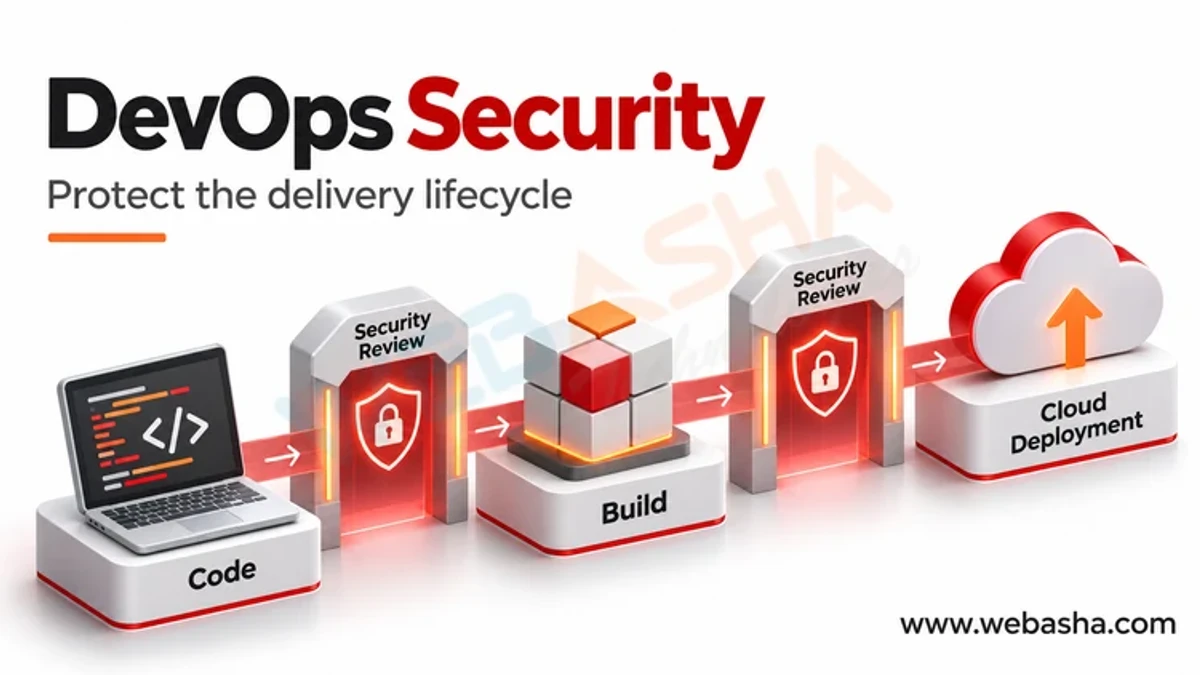
Quick answer: DevOps security protects the whole delivery system, not just the application: source code, the CI/CD platform, dependencies, secrets, container images, infrastructure as code, Kubernetes clusters and production runtime. The most valuable practices are protected branches with required reviews, least-privilege and short-lived pipeline credentials, secrets kept in a vault and scanned for in code, automated dependency and image scanning, signed artefacts with provenance, policy checks on infrastructure code, hardened clusters, and centralised logging. The OWASP Top 10 CI/CD Security Risks and the CISA and NSA CI/CD guidance are good checklists.
Key takeaways
- The CI/CD system holds the keys to production; secure it like production.
- Most pipeline incidents involve leaked or over-privileged credentials.
- Automated scans only help if findings block merges or are triaged quickly.
- Sign what you build and verify signatures before deployment.
- Start with a few high-value controls and add more each quarter.
Table of Contents
- What Are the Main DevOps Security Challenges?
- What Is the Practice Checklist by Asset?
- How Do You Secure the CI/CD System?
- How Should Secrets Be Handled?
- How Do You Secure Containers and Kubernetes?
- How Do You Check Infrastructure as Code?
- What Is a 30-60-90 Day Plan?
- References
What Are the Main DevOps Security Challenges?
- Speed: many deployments a day leave no time for manual reviews.
- Sprawl: hundreds of repositories, pipelines and cloud accounts.
- Secrets everywhere: tokens in code, CI variables and laptops.
- Third-party code: open source packages and base images make up most of what ships.
- Tool noise: scanners that produce more findings than teams can handle.
- Skills: developers are not security specialists, and security teams are small.
What Is the Practice Checklist by Asset?
| Asset | Practice | Example tools |
|---|---|---|
| Source code | Protected branches, required reviews, signed commits, SAST | GitHub rulesets, Semgrep, CodeQL |
| Dependencies | Scanning, pinned versions, SBOM | Dependabot, Trivy, Syft |
| Secrets | Vault storage, scanning, rotation | HashiCorp Vault, cloud secret managers, gitleaks |
| CI/CD | Least privilege, OIDC credentials, isolated runners | GitHub OIDC, GitLab CI |
| Artefacts | Signing and provenance | Sigstore Cosign, SLSA |
| Containers | Minimal base images, non-root, scanning | Distroless, Trivy, Grype |
| Infrastructure as code | Policy checks before apply | Checkov, OPA/Conftest, tfsec |
| Kubernetes | Pod Security Standards, RBAC, network policies | Pod Security Admission, Kyverno |
| Runtime | Logging, detection, patching | Falco, SIEM, CSPM |
How Do You Secure the CI/CD System?
The OWASP Top 10 CI/CD Security Risks include insufficient flow control, inadequate identity management, poisoned pipeline execution and insufficient credential hygiene. The CISA and NSA guidance gives matching mitigations. In GitHub Actions, two quick wins are read-only default permissions and short-lived cloud credentials through OIDC instead of stored keys:
permissions:
  contents: read
  id-token: write          # allow OIDC token for this job only

steps:
  - uses: aws-actions/configure-aws-credentials@v4
    with:
      role-to-assume: arn:aws:iam::123456789012:role/deploy-prod
      aws-region: ap-south-1
Also pin third-party actions to a commit SHA, require approval for production deployments, and never run untrusted pull request code with access to secrets.
How Should Secrets Be Handled?
- Store secrets in a vault or cloud secret manager, not in code or plain CI variables where avoidable.
- Block commits containing secrets with a pre-commit hook and scan history:
gitleaks detect --source . --redact - Rotate any secret that has ever been committed, even if the commit was deleted.
- Prefer short-lived credentials issued per job.
How Do You Secure Containers and Kubernetes?
Build from minimal base images, run as non-root, and scan images in the pipeline. In Kubernetes, enforce the Pod Security Standards per namespace:
kubectl label namespace shop \
  pod-security.kubernetes.io/enforce=restricted \
  pod-security.kubernetes.io/warn=restricted
Add role-based access control with least privilege, network policies that deny traffic by default, and the CIS Kubernetes Benchmark for node and control plane settings.
How Do You Check Infrastructure as Code?
# Scan Terraform before apply; fail on high-severity issues
checkov -d infra/ --compact --hard-fail-on HIGH

# Review the plan in CI and require approval before apply
terraform plan -out tfplan && terraform show -json tfplan > plan.json
Policy as code catches public storage buckets, open security groups and unencrypted databases before they exist.
What Is a 30-60-90 Day Plan?
| Period | Actions |
|---|---|
| First 30 days | Protected branches, secrets scanning, dependency scanning, MFA on code and CI platforms |
| Days 31 to 60 | OIDC credentials, read-only pipeline defaults, container scanning, IaC scanning |
| Days 61 to 90 | Artefact signing, Kubernetes Pod Security, centralised pipeline audit logs, security champions |
Map progress to NIST SP 800-218 practices. For the concepts behind this, read DevOps vs DevSecOps and the Amazon Q extension compromise, a real CI token lesson. WebAsha offers DevSecOps training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.