What is the importance of cyber resilience in the age of ransomware? The Detailed Guide
In the age of ransomware, simply having backups is not enough. Cyber resilience ensures that an organization can withstand and recover from cyberattacks without major disruption. Unlike traditional backup strategies that focus on restoring data post-incident, cyber resilience integrates real-time threat detection, immutable storage, fast recovery, and Zero Trust security principles. With ransomware attacks becoming more sophisticated—often involving data theft, backup deletion, and double extortion—IT leaders must rethink their approach. Cyber resilience enables proactive defense, minimizes downtime, protects brand reputation, and ensures business continuity.
Quick answer: Cyber resilience is an organisation's ability to withstand, recover from and adapt to cyberattacks, while backup only stores copies of data. Modern ransomware also steals data and targets backups, so restoring files is not enough. Resilience adds prevention, detection, response and tested recovery to keep the business running.
Key takeaways
- Backups restore data, while resilience also covers prevention, detection, response and tested recovery.
- Modern ransomware steals data and targets backups, so restoring files is not enough.
- Run a recovery drill and time it, so you know your real downtime.
Table of Contents
- What Is Cyber Resilience and How Is It Different from Backup?
- Why Backup Alone Fails Against Modern Ransomware
- The Ransomware Evolution: Why IT Leaders Must Act
- Key Pillars of Cyber Resilience
- Real-World Impact: Backup vs. Resilience
- Moving from Reactive to Proactive
- Conclusion
Traditional data backup is no longer enough. As ransomware grows more advanced and frequent, IT leaders must shift from a mindset of “backup and restore” to one of cyber resilience: the ability to withstand, recover from, and adapt to cyberattacks. Here is why this shift is needed, how ransomware is changing the rules, and what strategies leaders must adopt to ensure true business continuity.
What Is Cyber Resilience and How Is It Different from Backup?
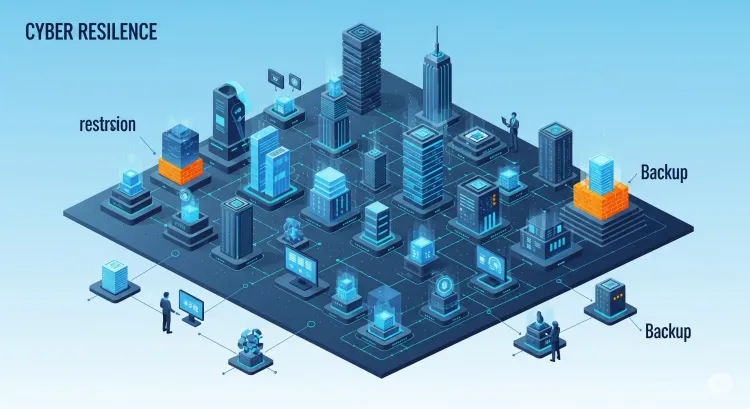
Backup is a component of resilience, but not the whole story. Backups store copies of data, while cyber resilience ensures that your organization can continue operating even during an ongoing attack. It includes proactive defense, rapid recovery, detection, incident response, and continuity planning.
While a backup helps you restore data after an incident, cyber resilience helps you minimize the impact of the attack in real time and recover operations faster, without prolonged downtime or data loss.
Why Backup Alone Fails Against Modern Ransomware
Modern ransomware doesn't just encrypt files, it exfiltrates data, deletes backups, targets hypervisors, and spreads laterally across systems. Here are ways traditional backup strategies fall short:
-
Backup deletion: Attackers often gain admin access and delete backup copies before encryption.
-
Data exfiltration: Sensitive files are stolen and used for double extortion, rendering backups useless.
-
Slow recovery: Even with backups, restoring terabytes of data can take days.
-
Corrupted or encrypted backups: If the malware remains undetected for weeks, it may have infected backup files as well.
Relying solely on backup creates a false sense of security. What’s needed is an integrated cyber resilience approach.
The Ransomware Evolution: Why IT Leaders Must Act
Ransomware attacks have become industrialized. Some key trends include:
| Attack Vector | Modern Trend | Risk to Organizations |
|---|---|---|
| Ransomware-as-a-Service (RaaS) | Cybercriminals sell attack kits | More frequent, scalable attacks |
| AI-Driven Phishing | Spear phishing using deepfakes | Harder to detect socially engineered threats |
| Double/Triple Extortion | Encrypt + exfiltrate + threaten | High reputational and compliance risk |
| Supply Chain Attacks | Compromised vendors | Wider impact, hard to trace |
The speed and sophistication of ransomware now outpace traditional defenses. IT leaders must respond by embedding resilience across people, process, and technology.
Key Pillars of Cyber Resilience
To build cyber resilience, organizations must focus on five essential pillars:
1. Immutable and Air-Gapped Backups
Ensure that backups cannot be altered or deleted, even by administrators. Use air-gapped or object-locked storage with versioning and encryption.
2. Continuous Threat Detection
Use EDR/XDR tools, network anomaly detection, and AI-based monitoring to identify threats early, before ransomware spreads.
3. Zero Trust Architecture
Implement Zero Trust principles: never trust, always verify. Authenticate all access, segment networks, and apply least privilege access.
4. Fast, Orchestrated Recovery
Use automation and orchestration to recover systems and data quickly. Consider instant recovery or live mount features that reduce downtime.
5. Regular Testing and Simulation
Conduct regular disaster recovery (DR) drills, ransomware simulations, and red teaming exercises to ensure recovery processes actually work.
Real-World Impact: Backup vs. Resilience
Imagine two companies attacked by ransomware:
-
Company A relied on scheduled daily backups stored on the same network. The attacker encrypted their data and backups. They spent 12 days offline.
-
Company B had immutable cloud backups, segmented networks, and automated failover systems. They restored operations in 2 hours, with minimal impact.
Which one would you rather be?
Moving from Reactive to Proactive
Cyber resilience isn’t just about defense. It’s about preparedness, speed, and adaptability. IT leaders must collaborate with security teams, business units, and vendors to implement:
-
Real-time monitoring and response
-
Automated patching and endpoint hardening
-
Clear incident response plans
-
Staff awareness and phishing simulations
Conclusion
The age of ransomware demands a new mindset. Backups are necessary but not sufficient. IT leaders must shift to resilience-first strategies that combine smart architecture, real-time defense, and recovery automation.
Cyber resilience is no longer a luxury, it’s a necessity. In a world where ransomware is not a question of "if" but "when", resilience determines who survives and who doesn’t.
Stay resilient. Stay ready. Stay in business.
To take this further with guided labs and an instructor, see our hands-on SOC analyst labs.
Related reading
- What are the latest modern ransomware tactics, including double extortion and AI-powered delivery methods?
- [2026] Top 50+ Cloud Disaster Recovery Interview Questions and Answers
- [2026] Top 50+ Cloud Backup and Recovery Interview Questions and Answers
Reference
For the authoritative details, see NIST Cybersecurity Framework.
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.