Amazon Q Developer Extension Compromise: Lessons for AI Tool Security
In July 2025, an attacker got malicious code into version 1.84.0 of the Amazon Q Developer extension for Visual Studio Code. According to AWS security bulletin AWS-2025-015, this happened because a GitHub token in the project's AWS CodeBuild configuration had broader permissions than it needed (CVE-2025-8217).
Topic: AI Security & Governance in AI & Data · News & analysis
Also covers: AI in Cybersecurity, Cyber Threats, Scams & Online Safety
Quick answer: In July 2025, an attacker got malicious code into version 1.84.0 of the Amazon Q Developer extension for Visual Studio Code. According to AWS security bulletin AWS-2025-015, this happened because a GitHub token in the project's AWS CodeBuild configuration had broader permissions than it needed (CVE-2025-8217). The injected change contained instructions telling the AI agent to delete local files and cloud resources, but AWS said the code was inert because of a formatting error and did not affect customer environments. AWS removed the code, rotated credentials and released version 1.85.0. Anyone with 1.84.0 should remove it.
Key takeaways
- The root cause was a supply chain weakness: an over-scoped CI token let an outsider's code be released.
- The payload was a prompt aimed at an AI agent with tool access, a new kind of malicious code.
- AWS reported no impact on customer resources; the code did not run as intended.
- Version 1.85.0 or later is safe; 1.84.0 should be removed, including from forks.
- AI coding agents need least privilege, confirmation for destructive actions and pinned extensions.
Table of Contents
- What Happened?
- How Did the Code Get In?
- Why Is This Also a Prompt Injection Story?
- What Was the Impact?
- How Do You Check Your Extension Version?
- What Should Open Source Maintainers Change?
- How Should Teams Control AI Coding Agents?
- How Do You Manage IDE Extensions Safely?
- How Do You Check AWS for Unexpected Deletions?
- References
What Happened?
Amazon Q Developer is an AI coding assistant that can run commands and use AWS tools on a developer's behalf. Its VS Code extension is developed in a public GitHub repository and built with AWS CodeBuild. In July 2025, a malicious change was merged and shipped in version 1.84.0, published to the VS Code Marketplace. AWS published security bulletin AWS-2025-015 on 23 July 2025.
How Did the Code Get In?
AWS's bulletin attributes the issue to an inappropriately scoped GitHub token in the CodeBuild configuration, recorded as CVE-2025-8217. A token with write access that could be obtained by an outside contributor allowed code to be committed without the normal review path. Reports describe the attacker submitting pull requests to public AWS repositories. The general lesson is that build credentials are among the most sensitive secrets in a project.
Why Is This Also a Prompt Injection Story?
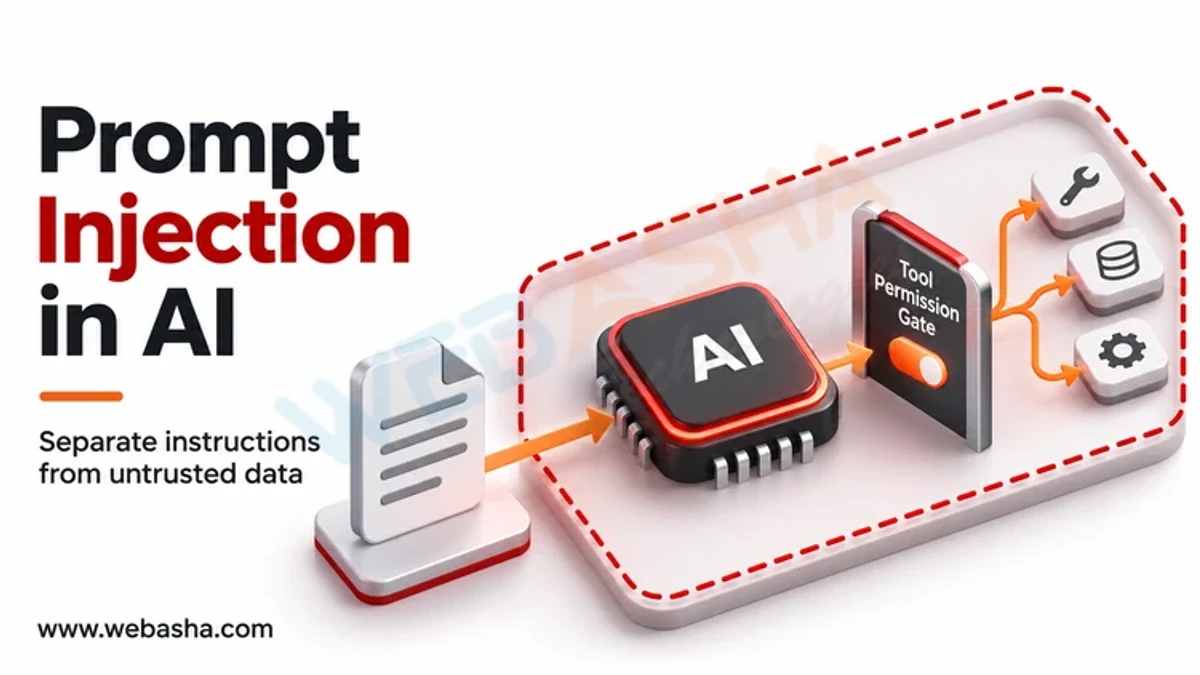
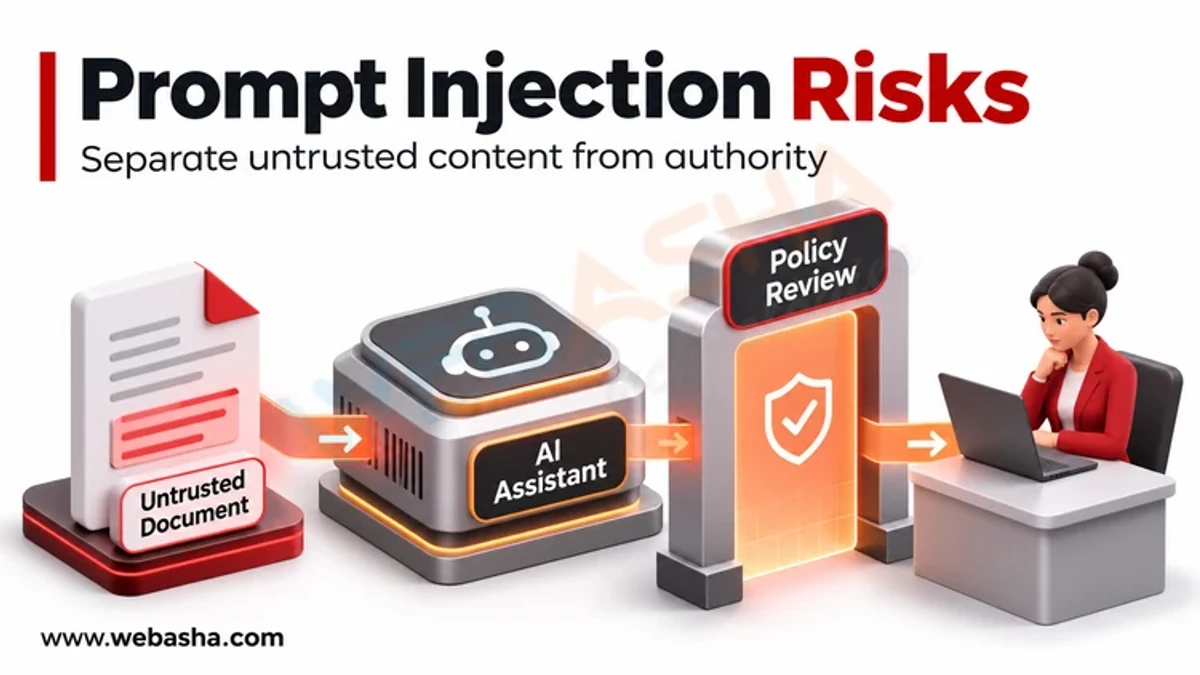
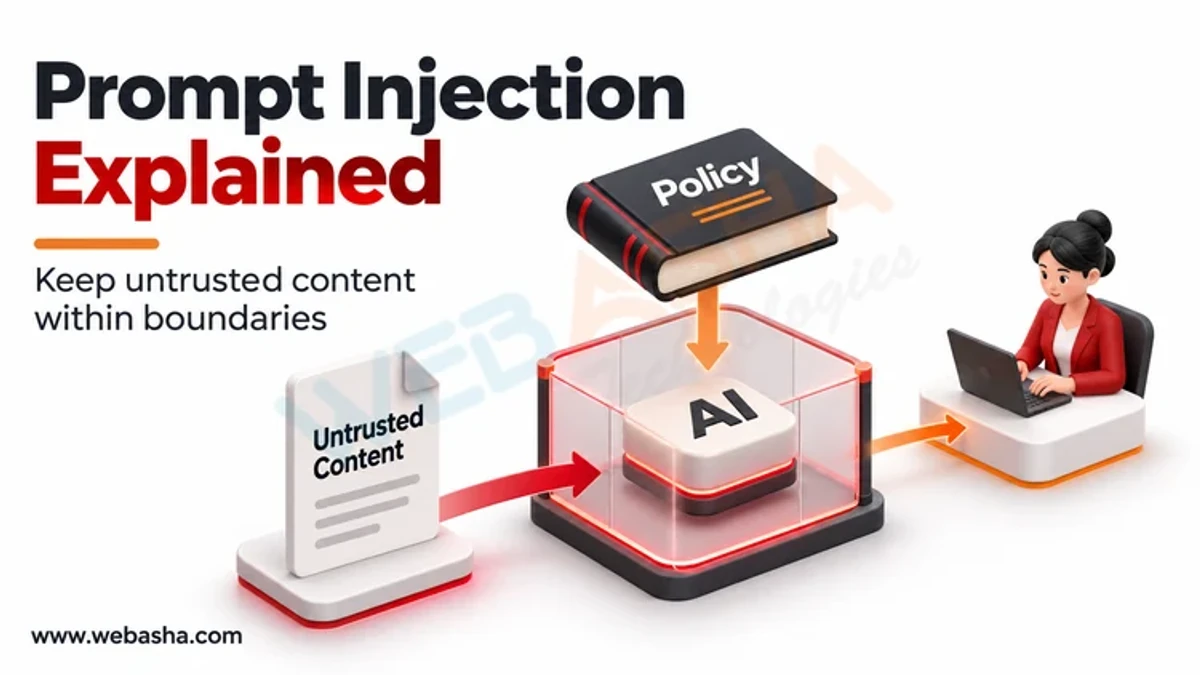
The injected code did not contain traditional malware. It contained natural-language instructions for the AI agent, asking it to clean the system to a near-factory state and delete cloud resources using the AWS CLI. If an agent with shell and cloud access had followed those instructions, the "malware" would have been the model acting on a prompt. This matches the risks in the OWASP Top 10 for LLM Applications: prompt injection (LLM01) and excessive agency (LLM06).
What Was the Impact?
AWS said the code was inert and could not affect services or customer environments, with reporting attributing the failure to a formatting error in the injected prompt. AWS revoked and replaced credentials, removed the code, and released 1.85.0. It advised customers to remove 1.84.0 everywhere, including forks and derivative copies.
How Do You Check Your Extension Version?
# List installed VS Code extensions with versions
code --list-extensions --show-versions | grep -i amazonwebservices

# Update or reinstall the latest version
code --install-extension amazonwebservices.amazon-q-vscode --force
If any machine shows @1.84.0, update it and review shell history and AWS CloudTrail for unexpected delete calls during the period it was installed.
What Should Open Source Maintainers Change?
- Use the least privileged tokens possible; prefer short-lived OIDC credentials in CI over long-lived personal access tokens (GitHub token guidance).
- Do not expose write-capable secrets to workflows triggered by untrusted pull requests.
- Require reviews and protected branches for every release path.
- Sign releases and publish provenance so users can verify builds.
- Check projects with OpenSSF Scorecard.
In GitHub Actions, set read-only permissions by default:
permissions:
  contents: read      # grant write only to the specific job that needs it
How Should Teams Control AI Coding Agents?
- Run agents with developer credentials limited to non-production accounts.
- Require human confirmation for destructive commands and cloud changes.
- Pin extension versions in managed environments and roll out updates after review.
- Log agent actions and alert on bulk deletions in CloudTrail or equivalent.
- Treat files, issues and web pages the agent reads as untrusted input that may contain instructions.
Related: root access in Copilot Enterprise's sandbox and securing MLOps pipelines. WebAsha offers DevSecOps and AI security training.
How Do You Manage IDE Extensions Safely?
- Keep an allowlist of approved extensions. VS Code supports organisation policies; see the VS Code enterprise documentation, which covers allowed-extension policies.
- Disable automatic extension updates on sensitive machines and roll out updates after a short delay.
- Prefer extensions from verified publishers with public source code.
- Remove extensions nobody uses; each one runs with the developer's permissions.
// settings.json on managed machines
{
  "extensions.autoUpdate": false,
  "extensions.autoCheckUpdates": true
}
How Do You Check AWS for Unexpected Deletions?
If an AI agent or compromised tool might have run AWS commands, search CloudTrail for destructive API calls:
# Delete and terminate calls in the last 7 days (CloudTrail event history, one region)
aws cloudtrail lookup-events --region ap-south-1   --start-time "$(date -u -d '7 days ago' +%Y-%m-%dT%H:%M:%SZ)"   --query "Events[?starts_with(EventName,'Delete') || starts_with(EventName,'Terminate')].[EventTime,EventName,Username]"   --output table
See viewing CloudTrail events with the AWS CLI. For prevention, apply service control policies that deny deletion of critical resources from developer accounts, and follow CISA's Secure by Design principles when building AI tools.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.