Cyber Kill Chain vs MITRE ATT&CK: Comparison and Integration
The Cyber Kill Chain and MITRE ATT&CK both describe how attacks unfold, but at different levels. The Kill Chain, published by Lockheed Martin researchers in 2011, is a simple seven-phase sequence that helps explain and break an intrusion. MITRE ATT&CK is a large, regularly updated knowledge base of adversary tactics and techniques based on real-world observations, with 14 tactics in its Enterprise matrix.
Topic: SOC & Blue Team in Cybersecurity & Ethical Hacking · Comparison
Learning path: SOC Analyst, lesson 11 of 16
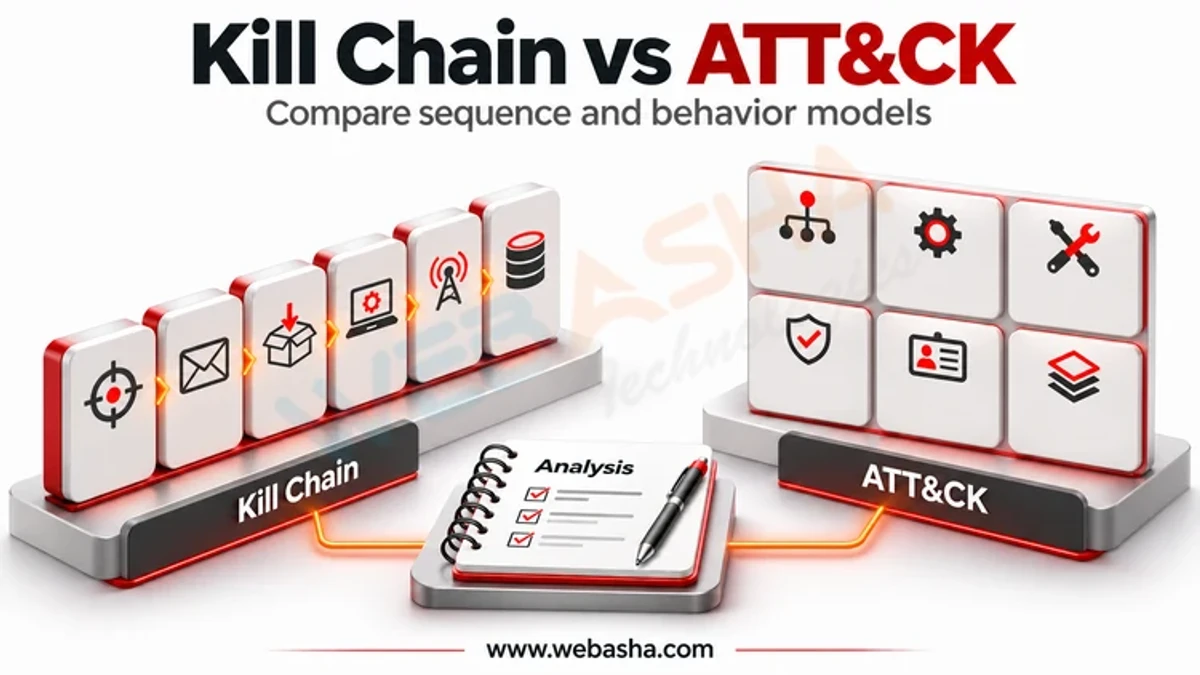
Quick answer: The Cyber Kill Chain and MITRE ATT&CK both describe how attacks unfold, but at different levels. The Kill Chain, published by Lockheed Martin researchers in 2011, is a simple seven-phase sequence that helps explain and break an intrusion. MITRE ATT&CK is a large, regularly updated knowledge base of adversary tactics and techniques based on real-world observations, with 14 tactics in its Enterprise matrix. The Kill Chain is better for communication and high-level triage; ATT&CK is better for detection engineering, threat hunting and measuring coverage. Most mature teams use both: Kill Chain phases for the story, ATT&CK technique IDs for the detail.
Key takeaways
- The Kill Chain is linear and high level; ATT&CK is detailed and non-linear.
- ATT&CK is updated by MITRE; the Kill Chain is a fixed model.
- ATT&CK covers post-compromise behaviour in far more depth.
- A mapping table lets teams use both together.
- Choose by task, not by popularity.
Table of Contents
- What Are the Kill Chain and ATT&CK?
- What Are the Main Differences?
- How Do Kill Chain Phases Map to ATT&CK Tactics?
- What Are the Strengths and Weaknesses of Each?
- Which Should You Use for Which Task?
- How Do You Integrate Both?
- What Mistakes Should You Avoid?
- Which Framework Should You Use for Which Task?
- References
What Are the Kill Chain and ATT&CK?
The Cyber Kill Chain comes from the 2011 paper by Hutchins, Cloppert and Amin. MITRE ATT&CK was released publicly in 2015 and organises adversary behaviour into tactics (the why), techniques and sub-techniques (the how), as described in MITRE's design and philosophy paper. For day-to-day SOC use of the Kill Chain, see our guide on how SOC teams use the Kill Chain.
What Are the Main Differences?
| Aspect | Cyber Kill Chain | MITRE ATT&CK |
|---|---|---|
| Origin | Lockheed Martin, 2011 | MITRE, public since 2015 |
| Structure | 7 sequential phases | 14 Enterprise tactics with many techniques |
| Detail level | Strategic | Technical, with procedure examples |
| Order | Linear | Non-linear; tactics can repeat |
| Updates | Fixed model | Regular releases |
| Coverage | Strong on pre-compromise | Strong on post-compromise, also cloud, mobile and ICS |
How Do Kill Chain Phases Map to ATT&CK Tactics?
| Kill Chain phase | Closest ATT&CK tactics |
|---|---|
| Reconnaissance | Reconnaissance |
| Weaponization | Resource Development |
| Delivery | Initial Access |
| Exploitation | Execution, Privilege Escalation |
| Installation | Persistence, Defense Evasion |
| Command and control | Command and Control |
| Actions on objectives | Credential Access, Discovery, Lateral Movement, Collection, Exfiltration, Impact |
Consider a phishing intrusion. In Kill Chain terms, the story is short: an email delivered a document, the document exploited the user, malware installed, it called home, and the attacker stole files. In ATT&CK terms, the same incident might be tagged with spearphishing attachment, user execution, a scheduled task for persistence, credential dumping, remote services for lateral movement and exfiltration over a web service. The first version helps a manager understand where defences failed. The second tells a detection engineer exactly which behaviours to write rules for.
The mapping is approximate. Many ATT&CK tactics, such as Lateral Movement and Discovery, sit inside what the Kill Chain treats as one final phase.
What Are the Strengths and Weaknesses of Each?
- Kill Chain strengths: easy to explain to leadership; shows where to break an attack.
- Kill Chain weaknesses: malware-centric; little detail after initial compromise; weak for insiders and cloud identity abuse.
- ATT&CK strengths: shared vocabulary; technique IDs for detections; group and software profiles.
- ATT&CK weaknesses: large and can overwhelm beginners; coverage heatmaps can give false confidence.
Which Should You Use for Which Task?
| Task | Better fit |
|---|---|
| Board or executive briefing | Kill Chain |
| Alert triage by urgency | Kill Chain |
| Writing detection rules | ATT&CK |
| Threat hunting hypotheses | ATT&CK |
| Red team and purple team planning | ATT&CK |
| Incident report narrative | Both |
How Do You Integrate Both?
- Tag every detection with an ATT&CK technique ID.
- Roll technique tags up to Kill Chain phases using the mapping table.
- Use ATT&CK Navigator to view coverage, and report phase coverage to leaders.
- Follow CISA's ATT&CK mapping best practices when writing reports.
- Add defensive countermeasures from MITRE D3FEND.
More background is in our ATT&CK framework explainer.
What Mistakes Should You Avoid?
- Treating a coloured ATT&CK heatmap as proof of protection.
- Forcing every attack into seven linear Kill Chain steps.
- Mapping techniques without evidence from logs or reports.
- Ignoring updates to ATT&CK between releases.
WebAsha runs SOC and threat hunting training covering both frameworks.
Which Framework Should You Use for Which Task?
| Task | Better fit |
|---|---|
| Explaining an attack to executives | Kill Chain |
| Building detection coverage | ATT&CK |
| Threat hunting hypotheses | ATT&CK |
| Choosing where to break an attack | Kill Chain, with ATT&CK detail |
MITRE ATT&CK is maintained openly by MITRE, and both models support the Detect and Respond functions of the NIST Cybersecurity Framework 2.0.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.