
Welcome!

Unlock your personalized experience.
Sign Up
Tag

MITRE ATT&CK Articles, Guides & Tutorials

3 posts

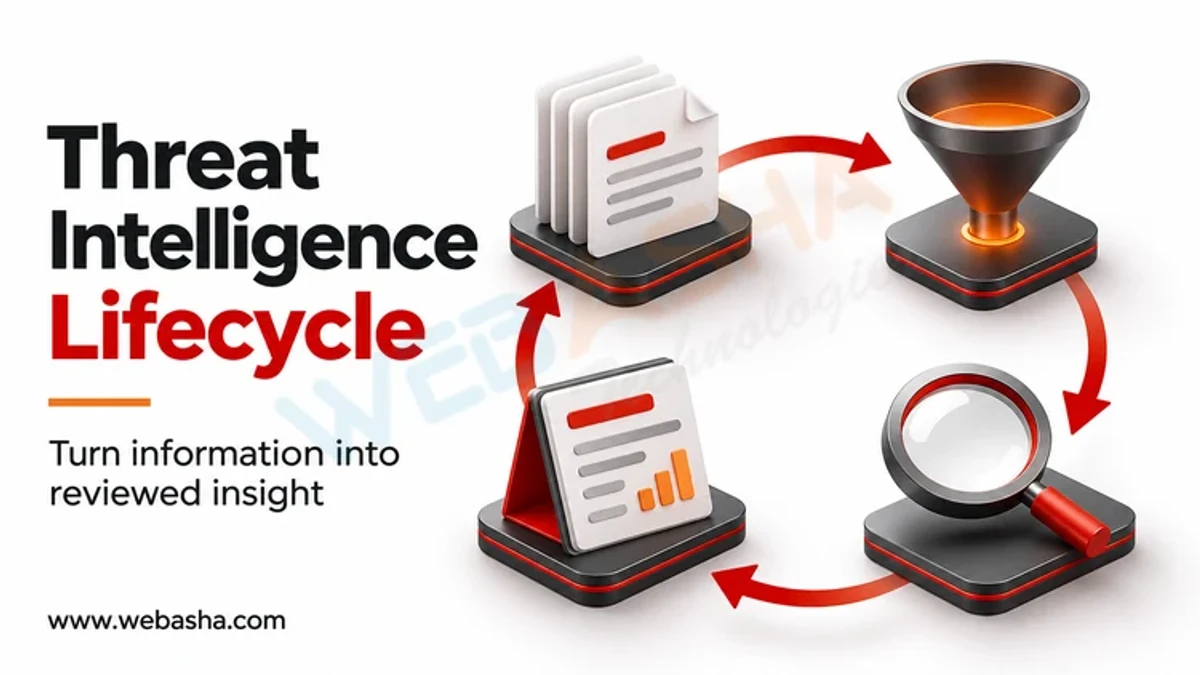
Threat Intelligence Lifecycle: A Step-by-Step Guide

The threat intelligence lifecycle is the repeating process that turns raw threat data into decisions. Most teams use six phases: direction (set requirements), collection (gather data), processing (clean and normalise it), analysis (turn it into assessments), dissemination (deliver it to the right audience) and feedback (check whether it helped). The cycle then starts again with updated requirements.
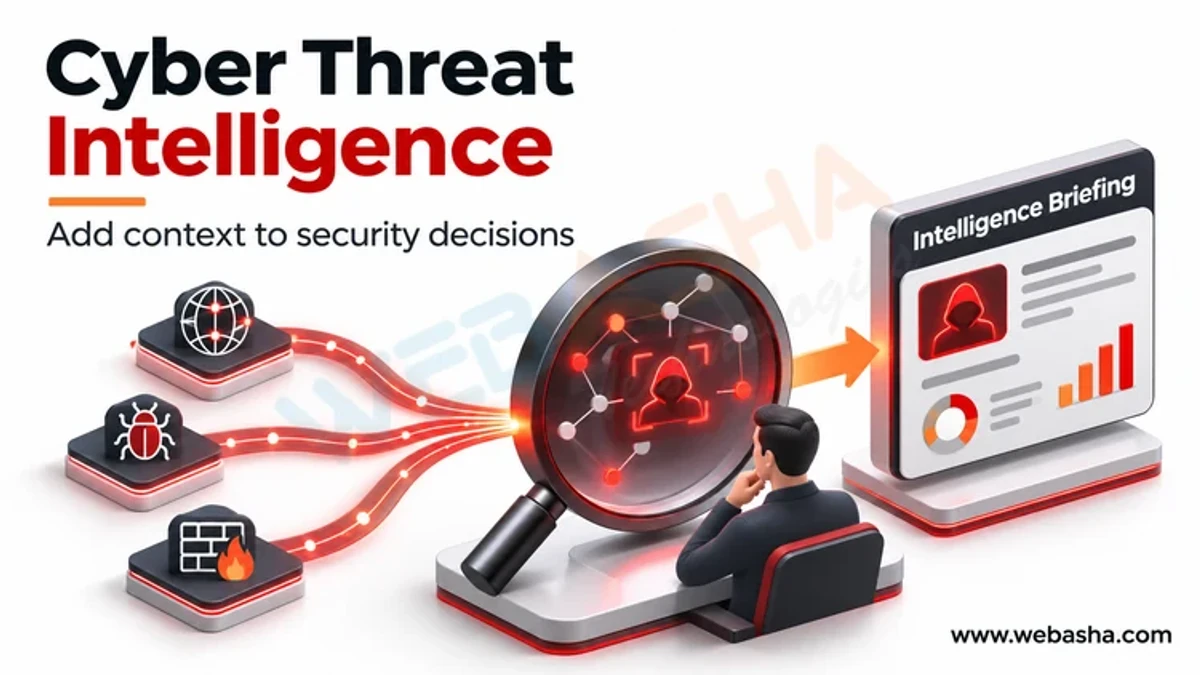
Cyber Threat Intelligence Explained: Types, Tools and Benefits

Cyber threat intelligence (CTI) is analysed information about threats that helps an organisation decide how to defend itself. It comes in four common types: strategic (trends and risks for leaders), operational (details of campaigns and actors), tactical (adversary techniques, often mapped to MITRE ATT&CK) and technical (indicators such as IP addresses, domains and file hashes).

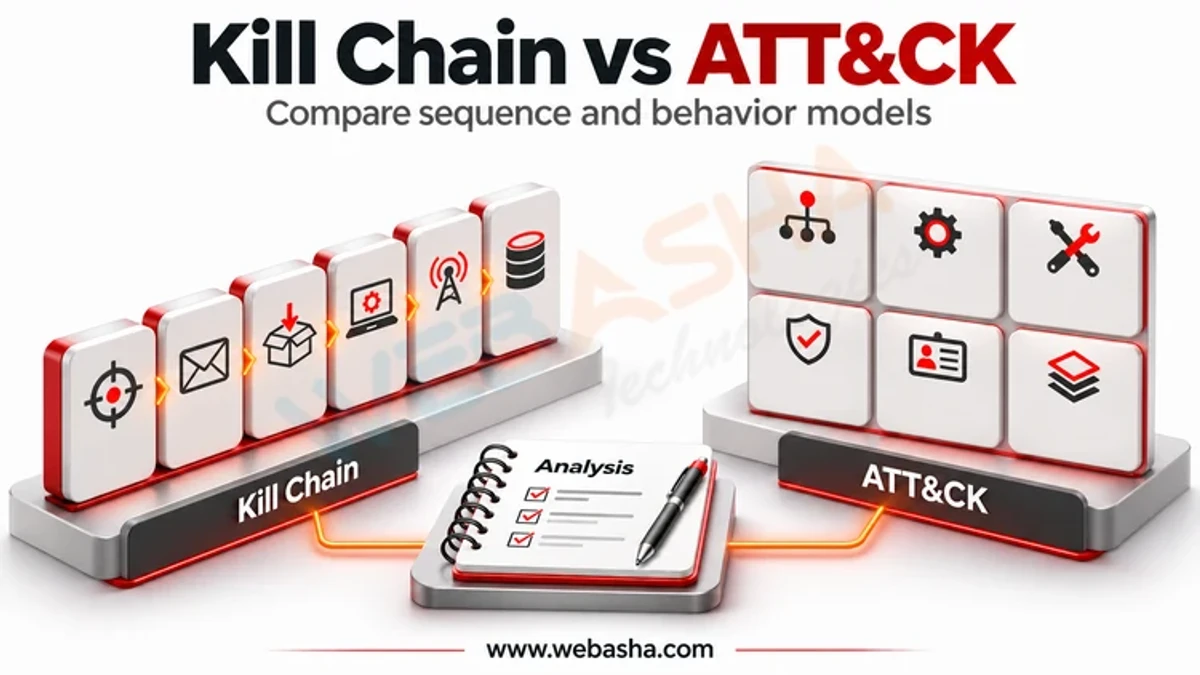
Cyber Kill Chain vs MITRE ATT&CK: Comparison and Integration

The Cyber Kill Chain and MITRE ATT&CK both describe how attacks unfold, but at different levels. The Kill Chain, published by Lockheed Martin researchers in 2011, is a simple seven-phase sequence that helps explain and break an intrusion. MITRE ATT&CK is a large, regularly updated knowledge base of adversary tactics and techniques based on real-world observations, with 14 tactics in its Enterprise matrix.









