Cyber Threat Intelligence Explained: Types, Tools and Benefits
Cyber threat intelligence (CTI) is analysed information about threats that helps an organisation decide how to defend itself. It comes in four common types: strategic (trends and risks for leaders), operational (details of campaigns and actors), tactical (adversary techniques, often mapped to MITRE ATT&CK) and technical (indicators such as IP addresses, domains and file hashes).
Topic: SOC & Blue Team in Cybersecurity & Ethical Hacking · Tools
Also covers: Cyber Threats, Scams & Online Safety
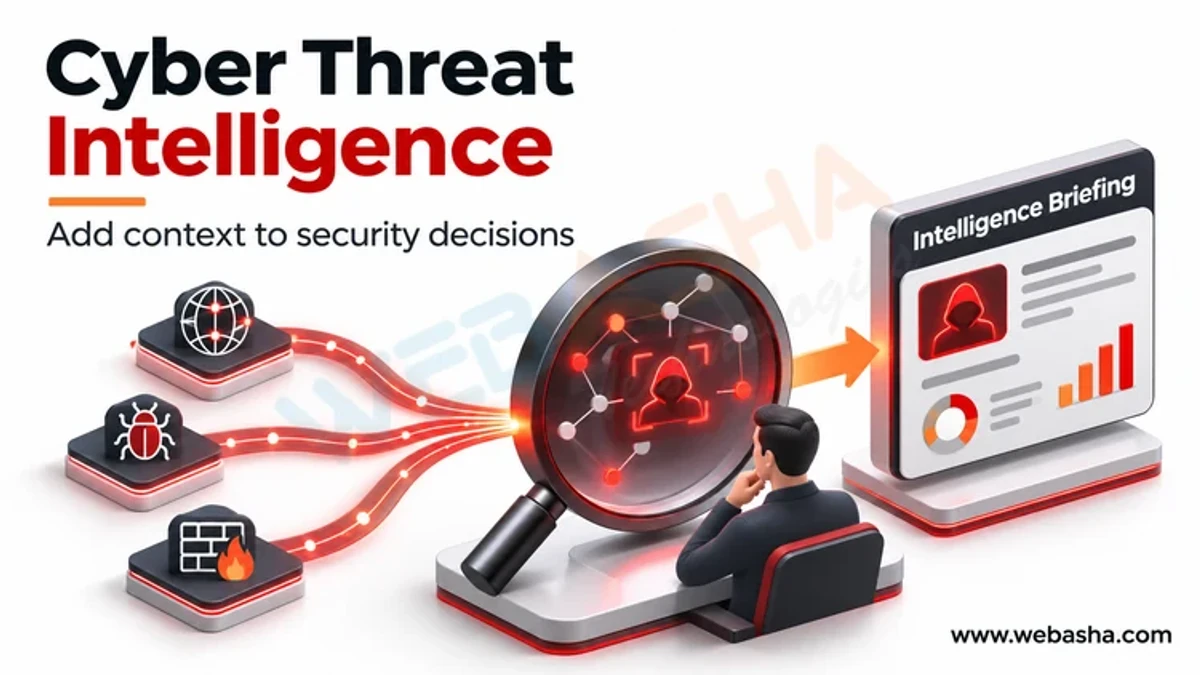
Quick answer: Cyber threat intelligence (CTI) is analysed information about threats that helps an organisation decide how to defend itself. It comes in four common types: strategic (trends and risks for leaders), operational (details of campaigns and actors), tactical (adversary techniques, often mapped to MITRE ATT&CK) and technical (indicators such as IP addresses, domains and file hashes). Tools fall into categories: threat intelligence platforms such as MISP and OpenCTI, SIEM and SOAR integrations, free government sources like the CISA KEV catalog, and ATT&CK Navigator. Organisations need CTI to prioritise patching, tune detections and respond faster.
Key takeaways
- CTI is analysed and contextual, not just a list of indicators.
- Each type serves a different audience and time horizon.
- Free government sources cover a lot of practical need.
- A platform helps store, enrich and share, but analysts make it useful.
- Value shows up in faster patching and better detections.
Table of Contents
- What Is Cyber Threat Intelligence?
- What Are the Four Types of CTI?
- Where Does Threat Intelligence Come From?
- Which Tools Do CTI Teams Use?
- How Do You Choose a CTI Tool?
- Why Does Your Organisation Need CTI?
- How Can a Small Team Start?
- How Should a Small Team Start With CTI?
- References
What Is Cyber Threat Intelligence?
NIST defines threat intelligence as threat information that has been aggregated, transformed, analysed, interpreted or enriched to provide context for decision making. The process that produces it is covered in our threat intelligence lifecycle guide. This post focuses on the types and the tools.
What Are the Four Types of CTI?
| Type | Audience | Example | Lifespan |
|---|---|---|---|
| Strategic | Board, CISO | Ransomware risk trends for your sector | Months to years |
| Operational | IR leads, SOC managers | An active campaign targeting a product you use | Weeks |
| Tactical | Detection engineers, hunters | ATT&CK techniques a group favours | Months |
| Technical | SOC tools and analysts | Malicious domains, IPs, hashes | Hours to days |
The types work together. A strategic brief might warn leaders that ransomware groups are targeting Indian manufacturing. Operational intelligence then names the campaign and the products it exploits. Tactical intelligence lists the techniques the group uses after entry, such as credential dumping or remote service abuse. Technical intelligence supplies the domains and hashes your SOC can block today. A team that only collects indicators misses the context that tells it why they matter and what to do next.
Technical indicators expire fastest because attackers change infrastructure. Tactical intelligence based on MITRE ATT&CK behaviours stays useful longer.
Where Does Threat Intelligence Come From?
- Internal: your own incidents, alerts and logs, often the most relevant source.
- Government: CISA advisories, the CISA KEV catalog, CISA AIS and CERT-In advisories.
- Communities: sector ISACs and trusted peer groups.
- Open source: researcher blogs, vendor reports, malware repositories.
- Commercial: paid feeds and analyst services.
Which Tools Do CTI Teams Use?
| Category | Purpose | Examples |
|---|---|---|
| Threat intelligence platform | Store, correlate and share intelligence | MISP, OpenCTI, commercial TIPs |
| SIEM and SOAR | Match indicators against logs and automate response | Microsoft Sentinel, Splunk, open source stacks |
| Framework tooling | Map and compare techniques | ATT&CK Navigator |
| Enrichment | Add reputation, WHOIS and passive DNS context | Sandbox and reputation services |
| Vulnerability intelligence | Know what is actually exploited | CISA KEV, vendor advisories |
How Do You Choose a CTI Tool?
- Support for STIX 2.1 and TAXII for sharing.
- Integration with your SIEM, EDR and firewall.
- Indicator scoring and automatic expiry.
- TLP handling, using FIRST TLP 2.0.
- Staff time to run and tune it.
Sharing rules should follow NIST SP 800-150 and India's DPDP Act 2023 when personal data is involved.
Why Does Your Organisation Need CTI?
- Patch exploited vulnerabilities first, using KEV and advisories.
- Write detections for techniques groups actually use.
- Give incident responders context during an investigation.
- Brief leaders on risks with evidence instead of guesswork.
- Support CERT-In incident reporting within six hours with better facts.
How Can a Small Team Start?
Begin with free sources: subscribe to CISA and CERT-In advisories, track KEV against your asset list, and run MISP or OpenCTI in a lab. Map your top threats to ATT&CK and check detection coverage. For background, read our earlier CTI overview. WebAsha runs cyber threat intelligence training with practical labs.
How Should a Small Team Start With CTI?
| Step | Detail |
|---|---|
| Define three to five intelligence requirements | Focus on threats to your sector |
| Use free sources first | CERT-In advisories, CISA KEV, vendor blogs |
| Track adversary techniques | Map them to detections you already have |
| Share with peers | Sector ISACs multiply value |
MITRE ATT&CK gives a common language for techniques, and the NIST Cybersecurity Framework 2.0 helps place CTI inside the wider programme.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.