Threat Intelligence Lifecycle: A Step-by-Step Guide
The threat intelligence lifecycle is the repeating process that turns raw threat data into decisions. Most teams use six phases: direction (set requirements), collection (gather data), processing (clean and normalise it), analysis (turn it into assessments), dissemination (deliver it to the right audience) and feedback (check whether it helped). The cycle then starts again with updated requirements.
Topic: SOC & Blue Team in Cybersecurity & Ethical Hacking · Lab / project
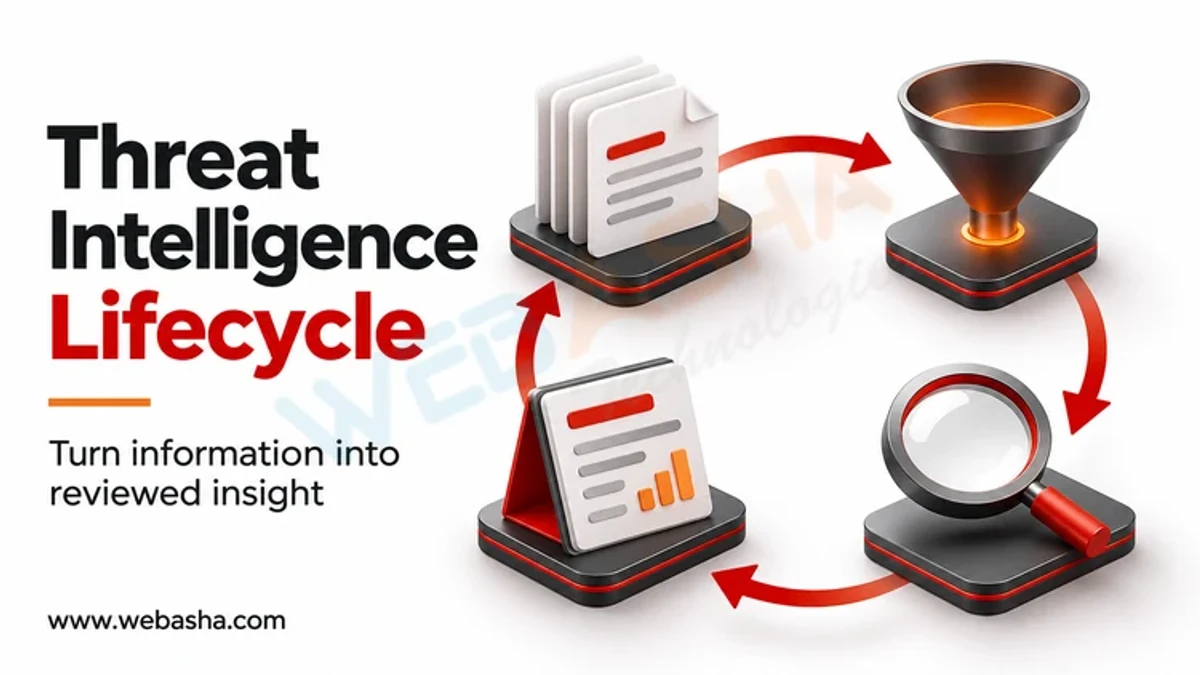
Quick answer: The threat intelligence lifecycle is the repeating process that turns raw threat data into decisions. Most teams use six phases: direction (set requirements), collection (gather data), processing (clean and normalise it), analysis (turn it into assessments), dissemination (deliver it to the right audience) and feedback (check whether it helped). The cycle then starts again with updated requirements. No single standard fixes the number of phases, but this model is widely used. Sharing guidance from NIST SP 800-150, the FIRST Traffic Light Protocol and the STIX and TAXII formats supports the later phases.
Key takeaways
- Intelligence starts with questions from stakeholders, not with feeds.
- Processing and analysis separate intelligence from raw data.
- Each audience needs a different product and format.
- TLP labels control how far shared intelligence can travel.
- Feedback keeps requirements current and removes useless sources.
Table of Contents
- What Is the Threat Intelligence Lifecycle?
- How Do You Set Direction and Requirements?
- What Happens in Collection and Processing?
- How Does Analysis Turn Data Into Intelligence?
- How Should Intelligence Be Disseminated?
- Why Does the Feedback Phase Matter?
- What Mistakes Break the Lifecycle?
- How Do You Know the Intelligence Programme Works?
- References
What Is the Threat Intelligence Lifecycle?
It is a loop that keeps intelligence work focused on real needs. For the different types of intelligence and tools, see our companion guide to CTI types and tools. This post covers the process.
| Phase | Input | Output |
|---|---|---|
| Direction | Business risks, stakeholder questions | Priority intelligence requirements |
| Collection | Requirements | Logs, feeds, reports, advisories |
| Processing | Raw data | Normalised, deduplicated records |
| Analysis | Processed data | Assessments with confidence levels |
| Dissemination | Assessments | Reports, alerts, detection rules |
| Feedback | Consumer responses | Updated requirements |
How Do You Set Direction and Requirements?
Ask decision makers what they need to know. Examples: which ransomware groups target our sector, which exposed products are being exploited, and which phishing themes are hitting our staff. Write these as priority intelligence requirements, each with an owner and a review date. Linking them to risks in the NIST CSF 2.0 Govern and Identify functions keeps them tied to the business.
What Happens in Collection and Processing?
Collection gathers data that answers the requirements:
- Internal: SIEM alerts, EDR telemetry, firewall and proxy logs, incident records.
- Government: CISA advisories, CISA AIS and CERT-In advisories for Indian organisations.
- Communities: sector ISACs and trusted peer groups.
- Open and commercial feeds.
Processing makes the data usable: parsing, removing duplicates, translating, enriching indicators, and storing them in a common format such as STIX. Keep logs available for incident work; CERT-In directions require 180 days of log retention in India.
How Does Analysis Turn Data Into Intelligence?
Analysts answer the requirement, state confidence, and explain what to do. Common techniques include:
- Mapping behaviour to MITRE ATT&CK techniques.
- Structuring events with the Diamond Model.
- Comparing competing hypotheses to reduce bias.
- Separating facts from assessments in every report.
How Should Intelligence Be Disseminated?
| Audience | Product | Format |
|---|---|---|
| Board and leadership | Strategic risk brief | Short written summary |
| Security managers | Campaign and actor reports | Report with recommendations |
| SOC and detection engineers | Indicators and detection logic | STIX over TAXII, SIEM rules |
| Partners and ISACs | Shared indicators | Labelled with TLP |
Label shared material with FIRST TLP 2.0 (CLEAR, GREEN, AMBER, AMBER+STRICT, RED). NIST SP 800-150 describes how to set sharing rules and protect sensitive data, which also matters under India's DPDP Act 2023.
Why Does the Feedback Phase Matter?
Feedback tells you whether intelligence changed a decision or a detection. Ask consumers if products were timely, relevant and actionable. Track simple measures such as how many detections came from intelligence and how many indicators produced false positives. Drop sources that never help, and retire answered requirements.
What Mistakes Break the Lifecycle?
- Buying feeds before defining requirements.
- Loading indicators into blocklists without checking age or quality.
- Writing one report for every audience.
- Sharing without TLP labels or legal review.
- Skipping feedback, so the cycle never improves.
WebAsha offers hands-on threat intelligence and SOC analyst training.
How Do You Know the Intelligence Programme Works?
| Measure | What it shows |
|---|---|
| Requirements answered on time | Relevance to decision makers |
| Indicators that led to detections | Operational value |
| Feedback scores from consumers | Whether reports are useful |
| False positive rate from feeds | Quality of sources |
The Identify and Detect functions of the NIST Cybersecurity Framework 2.0 give a structure for these measures, and CISA, Event logging best practices covers the telemetry intelligence depends on.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.