How SNMP Works: Protocol, Ports, Messages and Monitoring Explained
SNMP (Simple Network Management Protocol) lets a central manager read status from, and sometimes change settings on, routers, switches, servers, printers and UPS units. Each device runs an agent that exposes data in a tree called the MIB, where every value has a numeric object identifier (OID).
Topic: Networking in IT Infrastructure · Tutorial
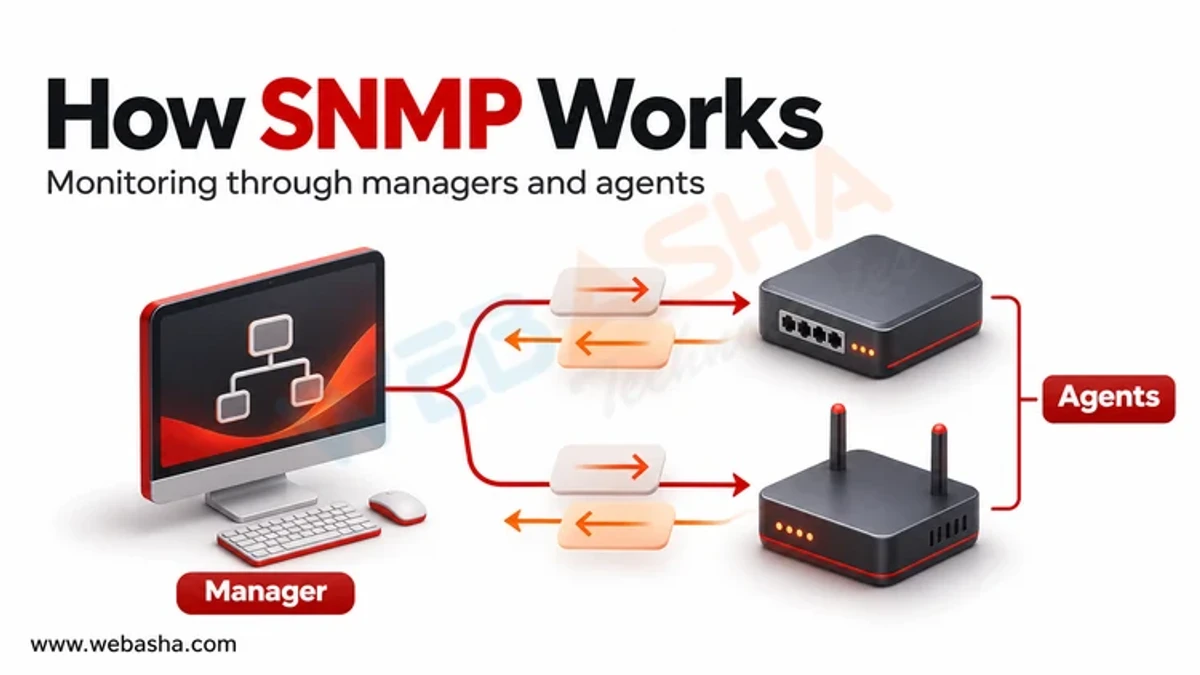
Quick answer: SNMP (Simple Network Management Protocol) lets a central manager read status from, and sometimes change settings on, routers, switches, servers, printers and UPS units. Each device runs an agent that exposes data in a tree called the MIB, where every value has a numeric object identifier (OID). The manager polls agents on UDP port 161, and agents send unsolicited alerts called traps or informs to the manager on UDP port 162. SNMPv1 and v2c rely on clear-text community strings, while SNMPv3, defined in RFCs 3411 to 3418, adds user authentication, encryption and access control.
Key takeaways
- SNMP has three parts: manager, agent and MIB.
- Polling uses UDP 161; traps and informs use UDP 162.
- SNMPv1 and v2c send community strings in clear text.
- SNMPv3 with authPriv (authentication plus encryption) is the secure choice.
- Default community strings such as public and private must be removed.
Table of Contents
- What Is SNMP and Why Is It Used?
- What Are the Manager, Agent, MIB and OID?
- Which SNMP Messages Exist and What Do They Do?
- Which Ports Does SNMP Use?
- How Do SNMPv1, v2c and v3 Differ?
- How Does SNMPv3 Security Work?
- How Do You Secure SNMP on Your Network?
- References
What Is SNMP and Why Is It Used?
Network teams need to know when a link is down, a disk is full or a switch port is dropping packets. SNMP gives them one standard way to collect that data from thousands of devices from different vendors. Monitoring tools such as Zabbix, PRTG, LibreNMS and Nagios use it to draw bandwidth graphs and raise alarms.
What Are the Manager, Agent, MIB and OID?
The RFC 3411 architecture describes these roles.
- Manager: the monitoring server that asks questions and receives alerts.
- Agent: software on the device that answers.
- MIB: the Management Information Base, a structured catalogue of what can be read or set.
- OID: a dotted number naming one value. For example, 1.3.6.1.2.1.1.3.0 is sysUpTime, the time since the agent restarted.
Which SNMP Messages Exist and What Do They Do?
The operations are defined in RFC 3416.
| PDU | Direction | Purpose |
|---|---|---|
| GetRequest | Manager to agent | Read one or more values |
| GetNextRequest | Manager to agent | Read the next OID, used to walk a tree |
| GetBulkRequest | Manager to agent | Read many values at once (v2c and v3) |
| SetRequest | Manager to agent | Change a value |
| Response | Agent to manager | Answer to any request |
| SNMPv2-Trap | Agent to manager | Unacknowledged alert |
| InformRequest | Agent to manager | Alert that must be acknowledged |
| Report | Between engines | SNMPv3 errors and engine discovery |
Which Ports Does SNMP Use?
RFC 3417 maps SNMP to UDP. Agents listen on UDP 161 for requests. Managers listen on UDP 162 for traps and informs. SNMP over TLS or DTLS uses 10161 and 10162, though it is less common. On your own server you can confirm the agent is listening with:
sudo ss -ulpn | grep -E ':161|:162'How Do SNMPv1, v2c and v3 Differ?
| Feature | SNMPv1 | SNMPv2c | SNMPv3 |
|---|---|---|---|
| Authentication | Community string | Community string | Per-user, HMAC based |
| Encryption | None | None | Yes, AES recommended |
| Bulk retrieval | No | GetBulk | GetBulk |
| Counters | 32-bit | 64-bit added | 64-bit |
| Access control | Basic | Basic | VACM views per user |
How Does SNMPv3 Security Work?
SNMPv3 uses the User-based Security Model in RFC 3414. Each user has an authentication key and a privacy key, and messages carry timeliness values to resist replay. Three security levels exist:
- noAuthNoPriv: username only. Avoid.
- authNoPriv: messages are authenticated but readable.
- authPriv: authenticated and encrypted. Use this.
Choose AES for privacy (RFC 3826) and SHA-2 for authentication (RFC 7860) where devices support them, instead of DES and MD5. The View-based Access Control Model in RFC 3415 limits each user to specific parts of the MIB.
How Do You Secure SNMP on Your Network?
- Disable SNMP on devices that are not monitored.
- Move to SNMPv3 authPriv; retire v1 and v2c.
- If v2c must stay, replace public and private with long random strings and make them read-only.
- Allow SNMP only from the monitoring server using ACLs; block UDP 161 and 162 at the internet edge.
- Disable write access unless it is truly needed.
- Log SNMP authentication failures and keep logs for 180 days under CERT-In directions.
CISA alert TA17-156A warns that exposed SNMP can leak device configurations and be abused for amplification. For the attacker's view of these weaknesses, see our SNMP security risks guide, and check our port numbers list for related services. Testing SNMP on devices you do not own needs written permission under India's IT Act 2000. Learn monitoring in our CCNA and network security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.