Risk Management in Cybersecurity: Strategies, Frameworks and Tools
Cybersecurity risk management is the ongoing process of identifying what could harm your information systems, estimating how likely and how damaging each risk is, deciding how to treat it, and monitoring it over time. The four treatment options are mitigate, accept, transfer and avoid. The main frameworks are NIST SP 800-30 Rev. 1 for risk assessment, NIST SP 800-37 Rev.
Topic: Cybersecurity Foundations in Cybersecurity & Ethical Hacking · Tools
Also covers: Cyber Threats, Scams & Online Safety
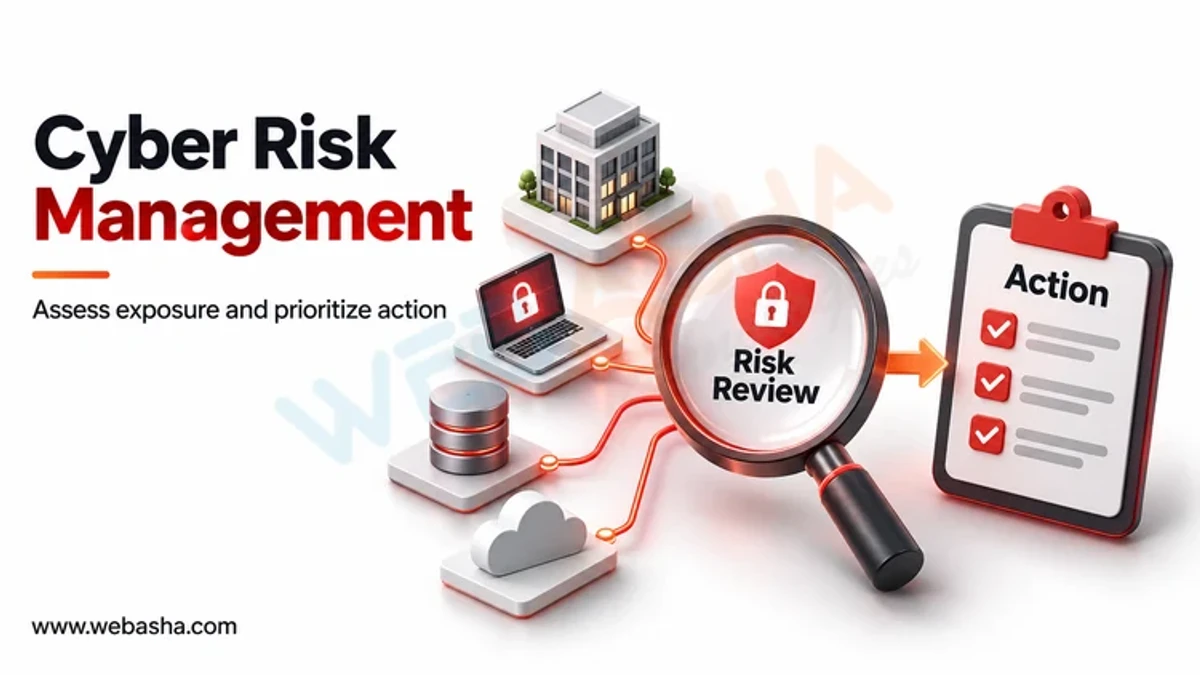
Quick answer: Cybersecurity risk management is the ongoing process of identifying what could harm your information systems, estimating how likely and how damaging each risk is, deciding how to treat it, and monitoring it over time. The four treatment options are mitigate, accept, transfer and avoid. The main frameworks are NIST SP 800-30 Rev. 1 for risk assessment, NIST SP 800-37 Rev. 2 (the Risk Management Framework) for managing system risk across a lifecycle, ISO/IEC 27005:2022 for risk management inside an ISO 27001 programme, and NIST CSF 2.0 for organisation-wide governance. Tools range from a simple risk register to GRC platforms.
Key takeaways
- Risk combines likelihood and impact on the business.
- Assessment is one step; management is the whole cycle.
- NIST and ISO frameworks describe compatible processes.
- Every risk needs an owner and a treatment decision.
- Monitoring keeps the register current as threats change.
Table of Contents
- What Is Cybersecurity Risk Management?
- What Are the Steps of the Risk Management Process?
- How Does NIST SP 800-30 Assess Risk?
- What Is the NIST Risk Management Framework?
- How Does ISO/IEC 27005 Compare?
- How Do You Choose a Risk Treatment?
- Which Tools Support Risk Management?
- References
What Is Cybersecurity Risk Management?
NIST SP 800-39 describes risk management at three tiers: organisation, mission or business process, and information system. Decisions at the top set the risk appetite that guides choices below. NIST IR 8286 explains how to feed cyber risk into enterprise risk registers so leaders compare it with financial and operational risks. Related posts cover adaptive security, which focuses on continuous monitoring, and information assurance, which focuses on protecting information properties.
What Are the Steps of the Risk Management Process?
- Frame: set scope, appetite and criteria.
- Identify: list assets, threats and vulnerabilities.
- Assess: estimate likelihood and impact.
- Treat: mitigate, accept, transfer or avoid.
- Monitor: track changes, controls and new threats.
- Communicate: report to owners and leadership.
A practical walkthrough of the assessment part is in our risk assessment guide.
How Does NIST SP 800-30 Assess Risk?
NIST SP 800-30 Rev. 1 models risk from threat sources and events, vulnerabilities and predisposing conditions, likelihood and impact. It supports qualitative, semi-quantitative and quantitative scales. A simple qualitative risk register looks like this:
| Risk | Likelihood | Impact | Rating | Owner |
|---|---|---|---|---|
| Ransomware via unpatched VPN | High | High | High | IT infrastructure head |
| Phishing leads to account takeover | High | Medium | High | IAM lead |
| Cloud storage misconfiguration | Medium | High | Medium | Cloud team lead |
| Laptop theft | Medium | Low | Low | IT support manager |
Use threat data such as the CISA KEV catalog to justify likelihood ratings.
What Is the NIST Risk Management Framework?
NIST SP 800-37 Rev. 2 defines seven steps: Prepare, Categorize, Select, Implement, Assess, Authorize and Monitor. It links risk decisions to SP 800-53 controls and requires a formal authorisation by an accountable official. It is mandatory for US federal systems and widely borrowed elsewhere.
How Does ISO/IEC 27005 Compare?
| Framework | Best for | Focus |
|---|---|---|
| NIST SP 800-30 Rev. 1 | Running assessments | Threat, vulnerability, likelihood, impact |
| NIST SP 800-37 Rev. 2 | System lifecycle risk | Seven RMF steps and authorisation |
| ISO/IEC 27005:2022 | ISO 27001 programmes | Event-based and asset-based risk identification |
| NIST CSF 2.0 | Organisation-wide governance | Govern function and outcomes |
ISO/IEC 27005:2022 gives guidance for the risk requirements in ISO/IEC 27001. NIST CSF 2.0 added a Govern function that places risk strategy with leadership.
How Do You Choose a Risk Treatment?
- Mitigate: add controls such as MFA, patching or backups.
- Accept: document approval when the risk is within appetite.
- Transfer: use cyber insurance or contracts, while keeping accountability.
- Avoid: stop the risky activity.
In India, treatment plans should also cover legal duties: CERT-In 6-hour incident reporting and 180-day log retention, and DPDP Act 2023 obligations for personal data.
Which Tools Support Risk Management?
Small teams can start with a spreadsheet register reviewed each quarter. Larger organisations use GRC platforms that link risks, controls, audits and evidence. Vulnerability scanners, asset inventories and SIEM data feed likelihood estimates. WebAsha offers GRC and ISO 27001 training for people building these programmes.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.