VLAN Hopping Attack Explained: Risks and How to Prevent It
VLAN hopping is when a device on one VLAN gets traffic into another VLAN it should not reach, bypassing the separation that VLANs provide. There are two classic methods. Switch spoofing abuses Dynamic Trunking Protocol (DTP) so an access port turns into a trunk. Double tagging abuses the native VLAN so a frame is forwarded into a second VLAN. Both rely on default or careless switch settings.
Topic: Networking in IT Infrastructure · Explainer
Also covers: Penetration Testing
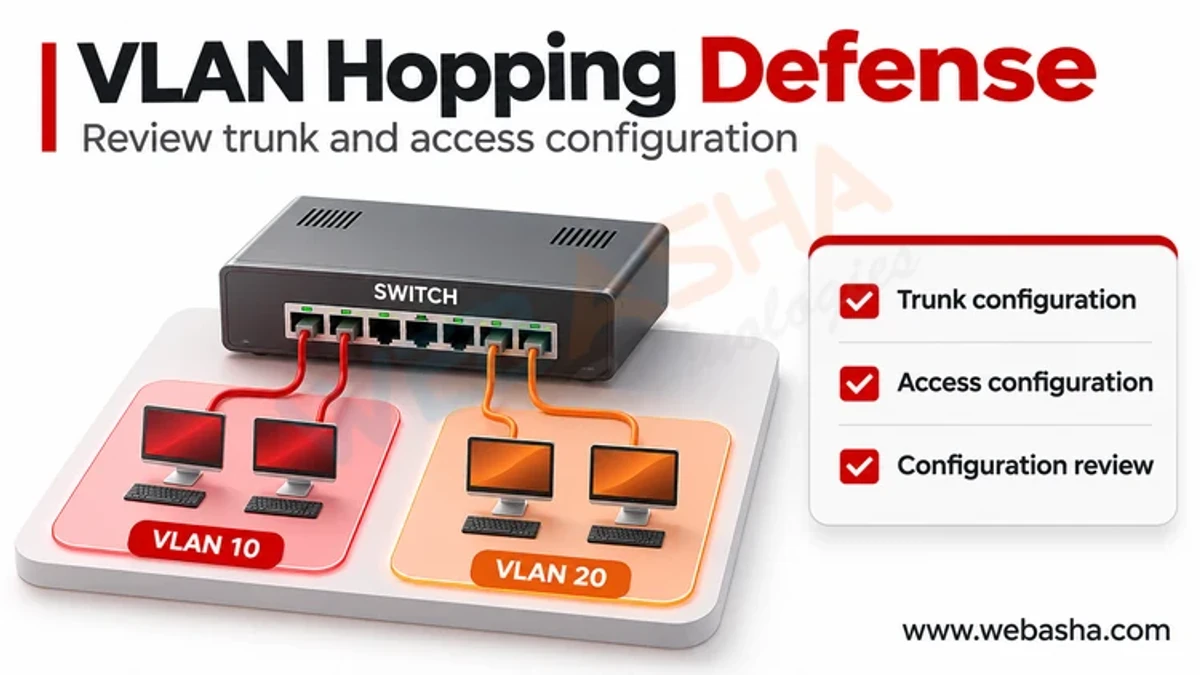
Quick answer: VLAN hopping is when a device on one VLAN gets traffic into another VLAN it should not reach, bypassing the separation that VLANs provide. There are two classic methods. Switch spoofing abuses Dynamic Trunking Protocol (DTP) so an access port turns into a trunk. Double tagging abuses the native VLAN so a frame is forwarded into a second VLAN. Both rely on default or careless switch settings. You prevent it by disabling DTP, setting user ports to static access mode, using a dedicated unused native VLAN, limiting allowed VLANs on trunks and shutting unused ports.
Key takeaways
- VLANs separate traffic logically, but only if switch ports are configured carefully.
- Switch spoofing depends on ports that negotiate trunks automatically.
- Double tagging depends on user ports sharing the trunk native VLAN.
- Static access ports, disabled DTP and an unused native VLAN close both routes.
- VLANs are not a full security boundary; use ACLs and firewalls between zones.
Table of Contents
- What Is VLAN Hopping?
- What Are the Two Main Methods?
- Why Does VLAN Hopping Matter?
- How Do You Prevent VLAN Hopping?
- How Do You Check Your Switches?
- References
What Is VLAN Hopping?
A VLAN groups switch ports into a separate broadcast domain, for example staff, guests, cameras and servers. Trunk links carry many VLANs between switches using 802.1Q tags. VLAN hopping breaks that separation. MITRE groups the wider idea of crossing segmentation as Network Boundary Bridging (T1599). For revision on VLAN basics, see our CCNA VLAN questions.
What Are the Two Main Methods?
| Method | Weakness it relies on | Main fix |
|---|---|---|
| Switch spoofing | Access ports left in a dynamic DTP mode that can form a trunk | Static access mode and disabled DTP |
| Double tagging | User ports in the same VLAN as the trunk native VLAN | Unused native VLAN, or tag the native VLAN |
Double tagging is one way only: traffic can reach the target VLAN, but replies do not come back the same way. That limits it, but it can still deliver harmful traffic.
Why Does VLAN Hopping Matter?
- A guest or IoT device could reach servers or management interfaces.
- Segmentation used for compliance, such as payment or OT zones, may fail.
- Attackers can sniff or inject traffic in VLANs they should never see.
- Voice, camera and building management VLANs often have weaker monitoring, so misuse can go unnoticed for longer.
NIST SP 800-215 treats segmentation as one layer, not a complete control. Boundary protection (SC-7) in NIST SP 800-53 expects filtering between zones as well.
How Do You Prevent VLAN Hopping?
| Control | Applies to | Stops |
|---|---|---|
| switchport mode access | All user ports | Switch spoofing |
| switchport nonegotiate | Access and trunk ports | DTP negotiation |
| Dedicated unused native VLAN | Trunks | Double tagging |
| vlan dot1q tag native | Platforms that support it | Untagged native traffic |
| Prune allowed VLANs | Trunks | Unneeded VLANs crossing links |
| Shut unused ports, park in black-hole VLAN | Spare ports | Rogue connections |
A Cisco IOS example, based on the Catalyst 9300 trunk guide:
interface range GigabitEthernet1/0/1 - 40
 switchport mode access
 switchport access vlan 10
 switchport nonegotiate
!
interface GigabitEthernet1/0/48
 switchport mode trunk
 switchport nonegotiate
 switchport trunk native vlan 999
 switchport trunk allowed vlan 10,20,30
!
vlan dot1q tag native
The NSA Network Infrastructure Security Guide also recommends disabling unused services and ports on network devices.
How Do You Check Your Switches?
show interfaces trunk
show interfaces status
show interfaces GigabitEthernet1/0/1 switchport
Confirm user ports show static access with negotiation off, and that trunks list only expected VLANs and the unused native VLAN. Combine this with the STP controls in our STP attack prevention guide. Keep switch logs for 180 days under the CERT-In directions. Test only in your own lab or with written authorisation under the IT Act 2000, Sections 43 and 66. WebAsha offers CCNA and network security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.