Fake Wi-Fi Hotspots: How Evil Twin Traps Catch Travellers
A Wi-Fi honeypot, often called an evil twin, is a fake hotspot named like a real one, such as an airport or hotel network. When you join, the attacker controls your connection: they can show a fake sign-in page to collect email or social media passwords, redirect you to phishing sites, or watch unencrypted traffic.
Topic: Network Security in Cybersecurity & Ethical Hacking · Explainer
Also covers: Cyber Threats, Scams & Online Safety
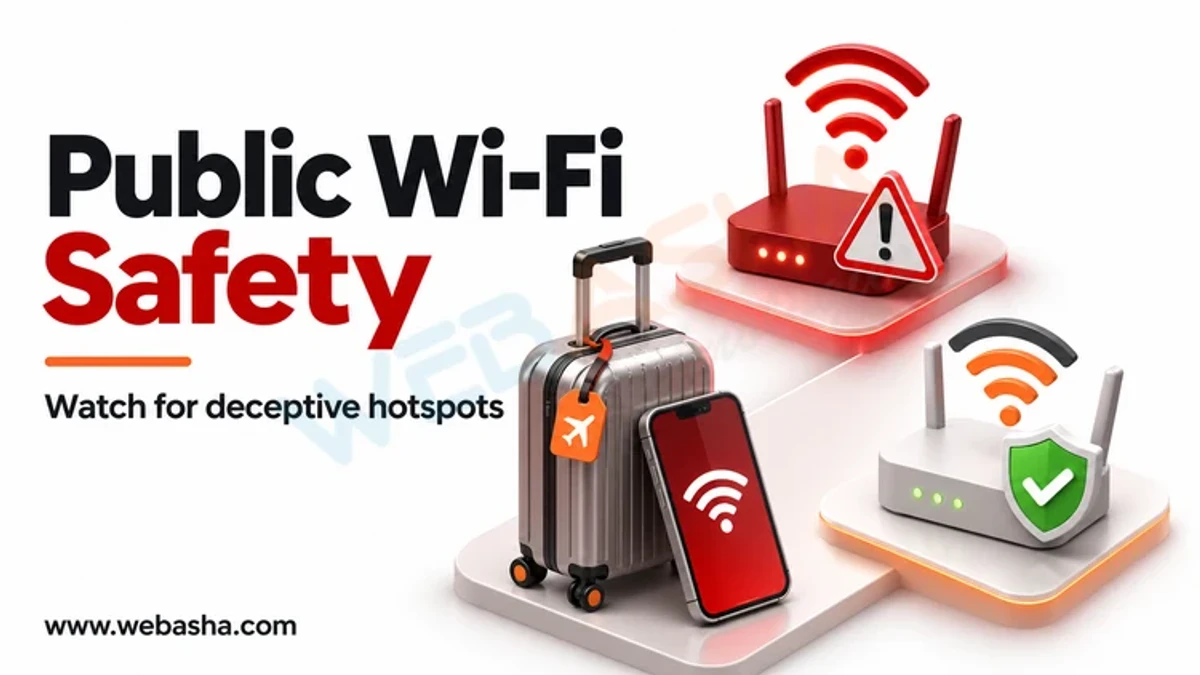
Quick answer: A Wi-Fi honeypot, often called an evil twin, is a fake hotspot named like a real one, such as an airport or hotel network. When you join, the attacker controls your connection: they can show a fake sign-in page to collect email or social media passwords, redirect you to phishing sites, or watch unencrypted traffic. Protect yourself by confirming the network name with staff, turning off auto-join, never entering account passwords on a Wi-Fi sign-in page, and using your phone's hotspot or a VPN for anything sensitive.
Key takeaways
- Network names are not verified; anyone can broadcast Free Airport WiFi.
- Fake captive portals that ask for email or social logins are the most common trap.
- In 2024 Australian police charged a man over alleged evil twin networks at airports and on flights.
- Auto-join for open networks makes phones connect without asking.
- Passkeys and MFA limit the damage of a stolen password.
Table of Contents
- How Does an Evil Twin Attack Work?
- Has This Happened in Real Life?
- What Are the Warning Signs?
- Which Phone and Laptop Settings Help?
- How Can Venues Detect Fake Access Points?
- What If You Entered Details on a Fake Page?
- References
How Does an Evil Twin Attack Work?
| Step | What the attacker does | Your defence |
|---|---|---|
| 1 | Broadcasts a network named like the venue's | Confirm the exact name with staff |
| 2 | Uses a stronger signal so devices prefer it | Disable auto-join for open networks |
| 3 | Shows a sign-in page asking for an email or social login | Never enter account passwords on Wi-Fi portals |
| 4 | Sits in the middle of traffic (MITRE T1557) | HTTPS, VPN, heed certificate warnings |
| 5 | Uses stolen logins later | MFA or passkeys, unique passwords |
Has This Happened in Real Life?
Yes. In 2024 the Australian Federal Police announced charges against a Western Australian man accused of setting up fake free Wi-Fi networks at Perth, Melbourne and Adelaide airports and on domestic flights that led users to pages collecting email and social media credentials. The case shows the attack needs only a portable device and is aimed at busy travel locations.
What Are the Warning Signs?
- Two networks with almost the same name, or one with an extra word such as Free.
- A sign-in page asking for your email password or social media login.
- Certificate warnings in your browser after joining.
- An open network where the venue said a password is used.
Which Phone and Laptop Settings Help?
| Platform | Setting |
|---|---|
| iPhone | Settings, Wi-Fi, Ask to Join Networks; forget networks after use |
| Android | Wi-Fi preferences: turn off notifications and auto-connect for open networks |
| Windows | Mark the network as Public; untick Connect automatically |
| macOS | Untick Auto-Join for the network in Wi-Fi settings |
# Windows: list and remove saved Wi-Fi profiles
netsh wlan show profiles
netsh wlan delete profile name="Free Airport WiFi"

# Linux (NetworkManager): stop a saved open network from auto-connecting
nmcli connection modify "Free Airport WiFi" connection.autoconnect no
How Can Venues Detect Fake Access Points?
Venue IT teams can scan for networks using their name but unknown hardware addresses. On a Linux laptop:
# list nearby networks with BSSID (hardware address) and signal
nmcli -f SSID,BSSID,CHAN,SIGNAL,SECURITY dev wifi list | grep -i "airport"
Any BSSID not on the venue's access point inventory is suspicious. Enterprise wireless systems include rogue access point detection, and using WPA3 or Wi-Fi Enhanced Open gives guests encrypted links.
What If You Entered Details on a Fake Page?
- Disconnect and change the password from a trusted network.
- Sign out of all sessions and turn on MFA.
- Check account recovery settings for changes.
- Report it: in India at cybercrime.gov.in or 1930; in the UAE through the UAE Cyber Security Council channels or local police.
Read our guides on VPNs on public Wi-Fi and honeypots in cybersecurity, or talk to a WebAsha training advisor about wireless security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.