IoT and OT Cyberattacks: How They Threaten Critical Infrastructure
IoT and OT cyberattacks target the connected devices and control systems that run power grids, water plants, pipelines, factories, hospitals and transport. Because these systems control physical processes, a successful attack can cause outages, safety incidents or environmental damage, not just data loss.
Topic: Cyber Threats, Scams & Online Safety in Cybersecurity & Ethical Hacking · Explainer
Quick answer: IoT and OT cyberattacks target the connected devices and control systems that run power grids, water plants, pipelines, factories, hospitals and transport. Because these systems control physical processes, a successful attack can cause outages, safety incidents or environmental damage, not just data loss. Documented examples include the 2015 attack that cut power to customers in Ukraine, the 2021 Colonial Pipeline ransomware incident that led to a precautionary shutdown, and the Volt Typhoon campaign that CISA says pre-positioned access in US infrastructure. Defences combine segmentation, asset visibility, controlled remote access, monitoring and practised incident response.
Key takeaways
- OT controls physical processes, so availability and safety come first.
- Many incidents start in IT networks and spread or force shutdowns in OT.
- Nation-state actors seek long-term access for potential disruption.
- Remote access paths and internet-exposed devices are common entry points.
- India protects critical sectors through NCIIPC alongside CERT-In.
Table of Contents
- What Are IT, OT and IoT?
- Why Is Critical Infrastructure Targeted?
- What Do Documented Incidents Show?
- How Do Attacks Affect Each Sector?
- How Can Operators Defend?
- How Is Critical Infrastructure Protected in India?
- What Should an OT Incident Response Plan Include?
- References
What Are IT, OT and IoT?
| Term | Meaning | Examples |
|---|---|---|
| IT | Business information systems | Email, ERP, databases |
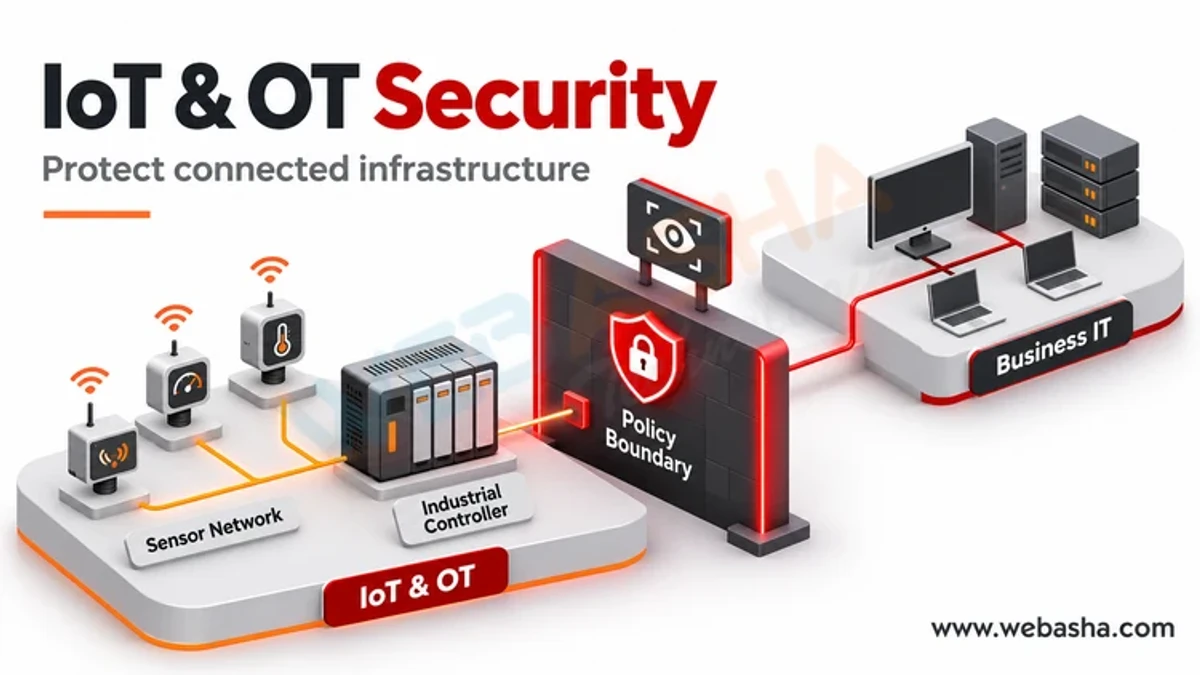
| OT | Systems that monitor and control physical processes | PLCs, SCADA, DCS, safety systems |
| IoT / IIoT | Connected sensors and devices | Smart meters, cameras, industrial sensors |
NIST SP 800-82 Rev. 3 is the main guide to OT security.
Why Is Critical Infrastructure Targeted?
- Nation states: espionage and pre-positioning for conflict.
- Ransomware gangs: operators under pressure to restore service may pay.
- Hacktivists: publicity, often against poorly secured internet-exposed devices.
- Weaknesses: old equipment, long patch cycles, flat networks and vendor remote access.
What Do Documented Incidents Show?
| Incident | What happened | Lesson |
|---|---|---|
| Ukraine power grid, December 2015 | Attackers used stolen credentials and remote access to open breakers, cutting power to customers (CISA alert) | Secure remote access; plan manual operations |
| Colonial Pipeline, May 2021 | Ransomware hit IT systems; the company shut down pipeline operations as a precaution | IT incidents can halt OT operations |
| Volt Typhoon, 2023 to 2024 | CISA reported PRC state actors pre-positioning in communications, energy, water and transport (AA24-038A) | Hunt for "living off the land" activity |
How Do Attacks Affect Each Sector?
| Sector | Possible impact |
|---|---|
| Energy | Outages affecting homes, hospitals and industry |
| Water | Unsafe chemical levels, service disruption |
| Healthcare | Medical devices and building systems disrupted |
| Manufacturing | Production stoppage, equipment damage |
| Transport | Signalling and logistics disruption |
How Can Operators Defend?
- Inventory all OT and IoT assets and their connections.
- Segment IT from OT with controlled conduits and a DMZ.
- Remove internet exposure; route vendor remote access through monitored, MFA-protected gateways.
- Monitor OT networks with tools that understand industrial protocols.
- Maintain offline backups of configurations and practise manual operation.
- Map detections to MITRE ATT&CK for ICS.
CISA's ICS resources include free assessments and advisories.
How Is Critical Infrastructure Protected in India?
The National Critical Information Infrastructure Protection Centre (NCIIPC) is the nodal agency for critical information infrastructure in sectors such as power, banking, telecom, transport and government. CERT-In handles incident response, and specified incidents must be reported within six hours. Power sector entities also follow sector-specific cyber security guidelines. Related: IoT and OT attacks on industrial networks and why IoT security matters. WebAsha offers OT and ICS security training.
What Should an OT Incident Response Plan Include?
- Clear authority for deciding when to isolate or shut down processes safely.
- Contacts for operations, safety, vendors, regulators and CERT-In.
- Procedures for manual operation if control systems are unavailable.
- Offline copies of PLC programs, configurations and network diagrams.
- Evidence collection that does not disrupt running processes.
- Regular joint exercises between IT security and plant operations.
CISA's primary OT mitigations stress practising manual operations, and NIST SP 800-61 Rev. 3 provides the general incident response structure.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.