IoT and OT Cyberattacks: How They Impact Industrial Networks
IoT and OT attacks affect industrial networks by reaching the controllers, sensors and operator stations that run physical processes. Many industrial protocols such as Modbus and older versions of DNP3 have no authentication, and many PLCs cannot be patched without stopping production, so an attacker who reaches the control network can change setpoints, stop equipment or disrupt operator visibility.
Topic: Cyber Threats, Scams & Online Safety in Cybersecurity & Ethical Hacking · Explainer
Quick answer: IoT and OT attacks affect industrial networks by reaching the controllers, sensors and operator stations that run physical processes. Many industrial protocols such as Modbus and older versions of DNP3 have no authentication, and many PLCs cannot be patched without stopping production, so an attacker who reaches the control network can change setpoints, stop equipment or disrupt operator visibility. Common entry points are IT networks connected to OT, vendor remote access and internet-exposed devices. Defend with IEC 62443 zones and conduits, an accurate asset inventory, controlled remote access, passive monitoring and tested recovery plans.
Key takeaways
- Industrial protocols often trust any device that can reach them.
- The Purdue model and IEC 62443 zones guide segmentation.
- Passive monitoring is preferred because active scanning can disrupt fragile devices.
- Patching follows maintenance windows, so compensating controls matter.
- CISA's 2025 OT mitigations start with removing internet exposure.
Table of Contents
- How Are Industrial Networks Structured?
- Why Are Industrial Networks Vulnerable?
- How Do Attackers Get In?
- How Do IEC 62443 Zones and Conduits Help?
- How Do You Monitor an OT Network Safely?
- How Do You Handle Patching?
- References
How Are Industrial Networks Structured?
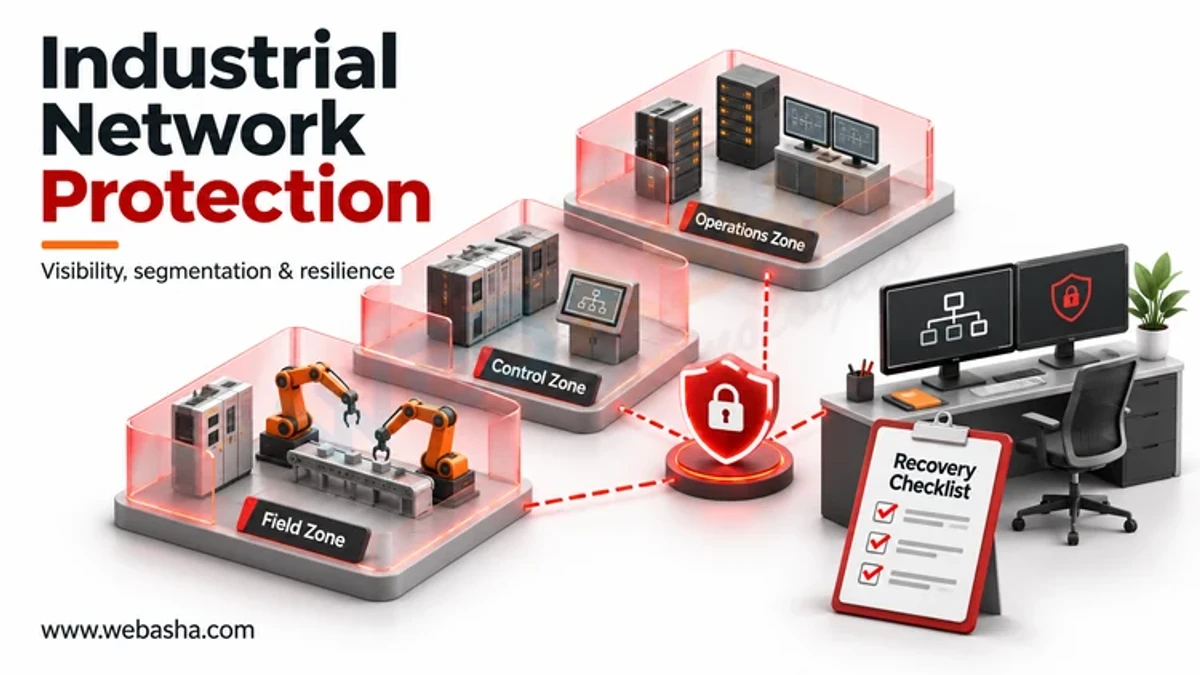
| Level | Contents |
|---|---|
| 4-5 Enterprise | Business IT, ERP, email |
| 3.5 Industrial DMZ | Historian replicas, patch servers, remote access gateways |
| 3 Site operations | Historians, engineering workstations |
| 2 Supervisory control | SCADA servers, HMIs |
| 1 Basic control | PLCs, RTUs, controllers |
| 0 Process | Sensors, actuators, motors |
Cloud and IIoT connections increasingly bypass these layers, which is why NIST SP 800-82 Rev. 3 stresses documenting every data flow.
Why Are Industrial Networks Vulnerable?
- Protocols such as Modbus/TCP send commands with no authentication or encryption.
- Equipment lasts decades and runs old operating systems.
- Downtime is costly, so updates are delayed.
- Shared accounts and default passwords on HMIs and controllers.
- Undocumented connections added for convenience.
How Do Attackers Get In?
| Path | ATT&CK for ICS example | Control |
|---|---|---|
| From compromised IT network | Exploitation of remote services | Firewalled DMZ, no direct IT-to-OT |
| Vendor remote access | External remote services | Brokered, recorded, MFA access |
| Internet-exposed HMIs or PLCs | Internet accessible device | Remove exposure |
| Infected USB or laptops | Replication through removable media | Media scanning kiosks |
See MITRE ATT&CK for ICS for the full technique list.
How Do IEC 62443 Zones and Conduits Help?
The ISA/IEC 62443 standards group assets with similar security needs into zones and allow communication only through defined conduits with controls such as firewalls and protocol filtering. Each zone gets a target security level based on risk. The standards also cover product development and integrator requirements, so buyers can ask vendors for certified components.
How Do You Monitor an OT Network Safely?
Use passive monitoring from SPAN ports or taps rather than active scans, which can crash older controllers. Tools that parse industrial protocols can alert on unusual commands, such as a PLC program download outside a maintenance window. Open source Zeek includes Modbus and DNP3 analysers:
# Zeek on a mirrored OT port: log Modbus function codes
zeek -i eth1 -C
# Review modbus.log for write functions (e.g. 5, 6, 15, 16) from unexpected hosts
zeek-cut id.orig_h func < modbus.log | sort | uniq -c
How Do You Handle Patching?
- Track vendor and CISA ICS advisories for your assets.
- Prioritise by exposure and known exploitation.
- Test patches in a lab or on a standby system.
- Apply in planned maintenance windows.
- Use compensating controls (segmentation, allowlisting) where patching is impossible.
CISA's 2025 primary OT mitigations list removing internet exposure, changing default passwords, securing remote access, segmentation and practising manual operation. Related: OT attacks on critical infrastructure. WebAsha offers ICS and OT security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.