9 Types of API Testing: What Each Checks and Which Tools to Use
API testing checks that an application programming interface returns the right data, enforces its rules, performs under load and resists attack. Nine common types are functional, contract, integration, end-to-end, load and performance, security, fuzz, validation (schema) and reliability testing.
Topic: Web & API Security in Cybersecurity & Ethical Hacking · Explainer
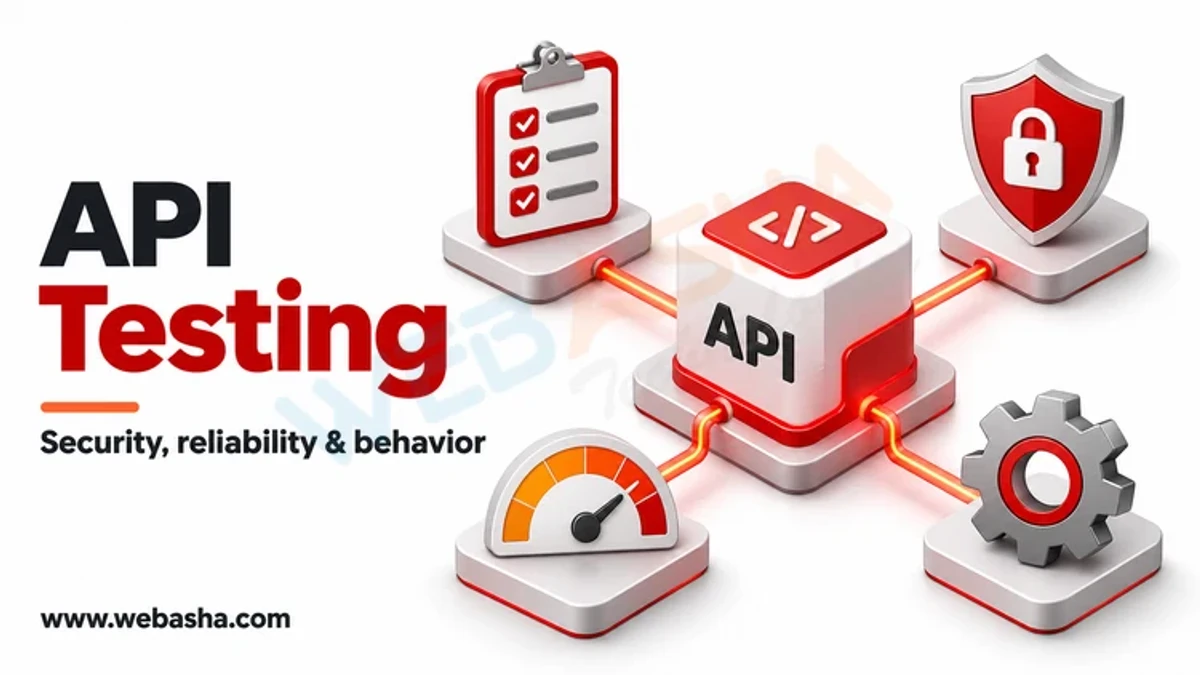
Quick answer: API testing checks that an application programming interface returns the right data, enforces its rules, performs under load and resists attack. Nine common types are functional, contract, integration, end-to-end, load and performance, security, fuzz, validation (schema) and reliability testing. Fast functional and contract tests run on every code change; load, security and fuzz tests run before releases and on a schedule. Together they catch broken responses, breaking changes between services, slowdowns and the authorization flaws listed in the OWASP API Security Top 10.
Key takeaways
- Test the API directly, not only through the user interface; it is faster and finds more.
- Contract tests stop one team's change from breaking another team's service.
- Security testing must include authorization checks between users, not just scanning.
- An OpenAPI description lets tools generate validation and fuzz tests automatically.
- Put cheap tests in every pipeline run and expensive ones on a schedule.
Table of Contents
- What Are the Nine Types at a Glance?
- How Do Functional and Validation Tests Work?
- What Are Contract and Integration Tests?
- When Do You Need End-to-End Tests?
- How Do You Load Test an API?
- What Does API Security Testing Cover?
- What Is API Fuzzing?
- What Is Reliability Testing?
- Where Does Each Test Run in CI/CD?
- References
What Are the Nine Types at a Glance?
| Type | Question it answers | Example tools |
|---|---|---|
| Functional | Does each endpoint return the right result? | pytest + requests, Postman, REST Assured |
| Validation (schema) | Do responses match the documented format? | OpenAPI validators, schemathesis |
| Contract | Do consumer and provider still agree? | Pact |
| Integration | Does the API work with its database and dependencies? | Testcontainers, docker compose |
| End-to-end | Does a full business flow work across services? | Postman collections, Playwright API |
| Load and performance | How fast is it, and at what load does it fail? | k6, JMeter, Locust |
| Security | Can users access or change what they should not? | Burp Suite, OWASP ZAP |
| Fuzz | Does unexpected input crash it or leak errors? | schemathesis, RESTler, ffuf |
| Reliability | Does it recover from failures and timeouts? | Fault injection, chaos tools |
How Do Functional and Validation Tests Work?
Functional tests send a request and assert on the status code, body and headers. Status codes have defined meanings in RFC 9110: 201 for created, 400 for bad input, 401 for missing authentication, 403 for forbidden, 404 for not found.
# test_orders.py  (pip install pytest requests)
import requests
BASE = "http://localhost:8000/api"

def test_create_order(token):
    r = requests.post(f"{BASE}/orders", json={"sku": "BOOK-1", "qty": 2},
                      headers={"Authorization": f"Bearer {token}"}, timeout=5)
    assert r.status_code == 201
    body = r.json()
    assert body["qty"] == 2 and "id" in body

def test_rejects_negative_quantity(token):
    r = requests.post(f"{BASE}/orders", json={"sku": "BOOK-1", "qty": -1},
                      headers={"Authorization": f"Bearer {token}"}, timeout=5)
    assert r.status_code == 400
Validation testing checks every response against the OpenAPI schema, catching missing fields and wrong types. In Postman, the same checks are written as test scripts:
pm.test("status is 201", () => pm.response.to.have.status(201));
pm.test("qty is a number", () => pm.expect(pm.response.json().qty).to.be.a("number"));
What Are Contract and Integration Tests?
Contract tests record what a consumer expects (fields, types, status codes) and verify the provider still delivers it. Pact is the common tool. When a provider team renames a field, the contract test fails in their pipeline before the change reaches the consumer.
Integration tests run the API with real dependencies, such as a database in a container, to catch problems mocks hide: migrations, query errors, transaction behaviour.
When Do You Need End-to-End Tests?
End-to-end tests follow a complete business flow, such as register, log in, add to cart, pay and fetch the receipt. They are slow and brittle, so keep a small number covering the most valuable flows and rely on lower-level tests for detail.
How Do You Load Test an API?
Load tests measure response times and error rates as traffic rises. With k6:
// load.js  run: k6 run load.js
import http from 'k6/http';
import { check } from 'k6';
export const options = {
  stages: [{ duration: '1m', target: 50 }, { duration: '3m', target: 50 }, { duration: '1m', target: 0 }],
  thresholds: { http_req_duration: ['p(95)<500'], http_req_failed: ['rate<0.01'] },
};
export default function () {
  const r = http.get('http://localhost:8000/api/products');
  check(r, { 'status 200': (res) => res.status === 200 });
}
Thresholds turn the test into a pass or fail result your pipeline can enforce. Load test against a staging environment sized like production, never against systems you do not own.
What Does API Security Testing Cover?
The OWASP API Security Top 10 2023 lists the main risks. The most common, broken object level authorization (BOLA), is found by repeating requests with a second user's token. Our guide to broken access control explains how. Other checks: authentication on every endpoint, rate limiting, excessive data in responses, mass assignment of fields such as role, and server-side request forgery in URL parameters. Practise with API penetration testing in Postman.
What Is API Fuzzing?
Fuzzing sends large numbers of generated, unexpected inputs to find crashes, 500 errors and validation gaps. If you have an OpenAPI file, schemathesis generates the cases:
pip install schemathesis
st run http://localhost:8000/openapi.json --checks all
Any 5xx response or schema violation it reports is a bug to fix.
What Is Reliability Testing?
Reliability tests check behaviour when things go wrong: a dependency times out, the database restarts, or a request is retried. Confirm the API returns clear errors, uses timeouts, and that retried requests do not create duplicates (idempotency keys for payments are a common fix).
Where Does Each Test Run in CI/CD?
| Stage | Tests |
|---|---|
| Every commit | Functional, validation, contract |
| Merge to main | Integration, short fuzz run, authorization tests |
| Before release | End-to-end, load, security scan |
| Scheduled | Long fuzzing, reliability drills, full penetration test |
For tool walkthroughs, see API testing with Postman. WebAsha's training advisors can suggest API security courses.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.