Best Free Malware Analysis Tools for Reverse Engineering and Detection
Defenders can analyse malware with free tools grouped by stage. For triage, use hashing, file type identification, strings and YARA rules to classify samples. For static analysis and reverse engineering, the NSA's open source Ghidra disassembles and decompiles binaries.
Topic: Incident Response & Digital Forensics in Cybersecurity & Ethical Hacking · Lab / project
Also covers: Cyber Threats, Scams & Online Safety, SOC & Blue Team
Quick answer: Defenders can analyse malware with free tools grouped by stage. For triage, use hashing, file type identification, strings and YARA rules to classify samples. For static analysis and reverse engineering, the NSA's open source Ghidra disassembles and decompiles binaries. For dynamic analysis, Microsoft Sysinternals tools such as Process Monitor and Process Explorer, and sandboxes like CAPE, show what malware does when run. For memory forensics, Volatility 3 examines RAM captures. Ready-made toolkits REMnux (Linux) and FLARE-VM (Windows) bundle many of these. Always work in an isolated lab, never on production systems.
Key takeaways
- Analysis moves from quick triage to static, dynamic and memory analysis.
- Ghidra, Sysinternals, YARA and Volatility are core free tools.
- REMnux and FLARE-VM save setup time.
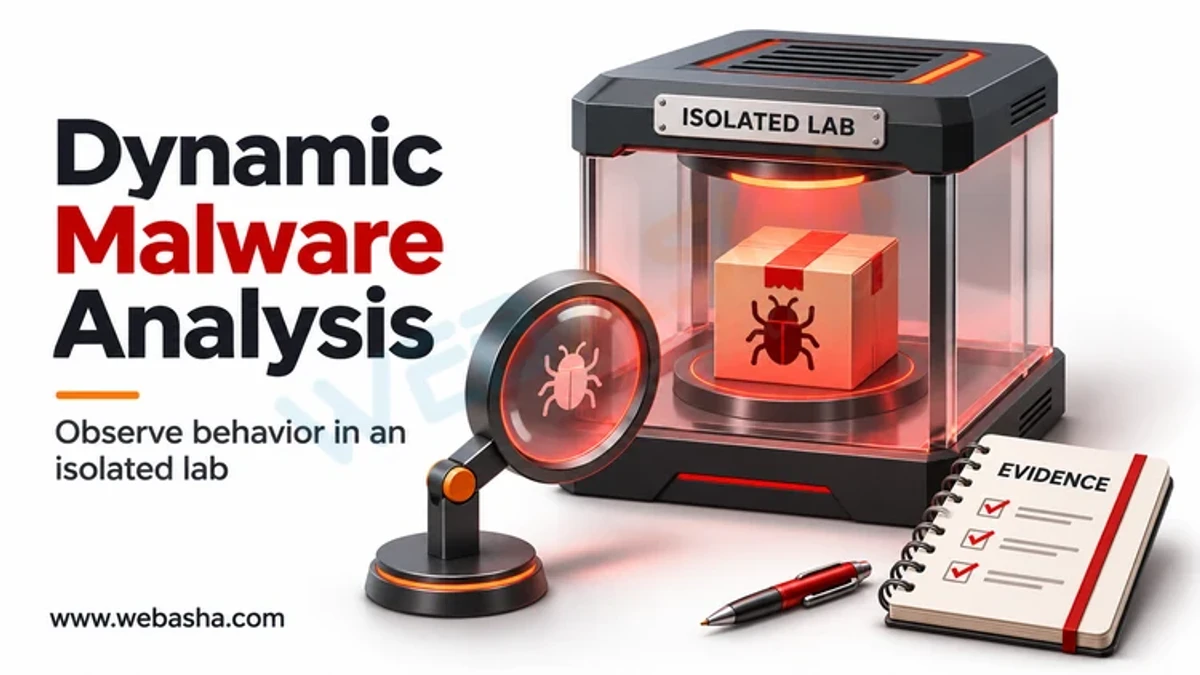
- Always use isolated virtual machines without access to real networks.
- Turn findings into detections: YARA rules, IOCs and SIEM queries.
Table of Contents
- What Are the Stages of Malware Analysis?
- Which Free Tools Fit Each Stage?
- How Do YARA Rules Help?
- How Do You Build a Safe Analysis Lab?
- How Do You Turn Analysis Into Detection?
- References
What Are the Stages of Malware Analysis?
| Stage | Goal |
|---|---|
| Triage | Identify file type, hashes, known family, obvious indicators |
| Static analysis | Examine code and structure without running it |
| Dynamic analysis | Observe behaviour when executed in a controlled environment |
| Memory forensics | Find injected code and artefacts in RAM |
| Reporting | Document behaviour, indicators and detections |
NIST SP 800-83 places malware analysis within incident handling.
Which Free Tools Fit Each Stage?
| Tool | Stage | Use |
|---|---|---|
| sha256sum, file, strings | Triage | Hashes, file type, readable text |
| YARA | Triage, hunting | Pattern-based classification |
| Ghidra | Static | Disassembly and decompilation |
| Sysinternals | Dynamic | Process, file, registry and network monitoring |
| CAPE Sandbox | Dynamic | Automated detonation and reporting |
| Volatility 3 | Memory | Process lists, injected code, network artefacts |
| REMnux / FLARE-VM | All | Prebuilt analysis environments |
How Do YARA Rules Help?
YARA describes patterns of strings or bytes that identify a malware family, so analysts can scan files and memory for matches.
rule Example_Suspicious_Downloader
{
    meta:
        description = "Example rule: script that downloads and runs a payload"
    strings:
        $a = "DownloadString" ascii nocase
        $b = "Invoke-Expression" ascii nocase
    condition:
        all of them
}
# Scan a folder of samples in your lab
yara -r example.yar ./samples/
How Do You Build a Safe Analysis Lab?
- Use virtual machines with snapshots; revert after each analysis.
- Disconnect from real networks; use host-only networking or simulated internet services.
- Disable shared folders and clipboard sharing.
- Store samples in password-protected archives, clearly labelled.
- Never analyse samples on work laptops or production machines.
How Do You Turn Analysis Into Detection?
- Extract indicators: hashes, domains, IPs, file paths, registry keys.
- Write YARA and SIEM detection rules for behaviour, not just hashes.
- Map behaviour to MITRE ATT&CK techniques.
- Share indicators with CERT-In and trusted communities where appropriate.
Related: types of malware and how SIEM works. WebAsha offers malware analysis training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.