Mobile Device Authentication Strategies for Secure Access
Effective mobile authentication works at three levels: unlocking the device (a strong PIN or passcode backed by biometrics such as fingerprint or face recognition stored in secure hardware), signing in to apps and services (passkeys, authenticator apps or push approvals with number matching, rather than SMS codes), and verifying the device itself (managed and compliant devices checked through mobile device…
Topic: Active Directory & Identity Security in Cybersecurity & Ethical Hacking · Explainer
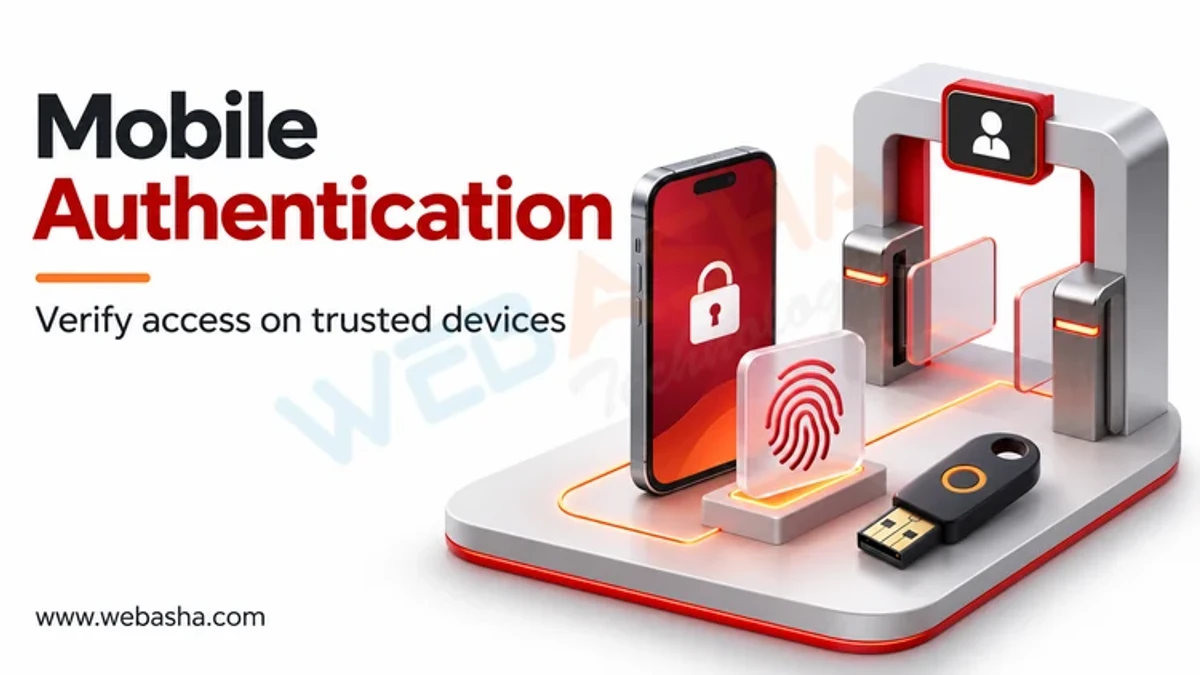
Quick answer: Effective mobile authentication works at three levels: unlocking the device (a strong PIN or passcode backed by biometrics such as fingerprint or face recognition stored in secure hardware), signing in to apps and services (passkeys, authenticator apps or push approvals with number matching, rather than SMS codes), and verifying the device itself (managed and compliant devices checked through mobile device management and conditional access). Organisations implement this by enrolling devices in MDM, requiring device encryption and passcodes, deploying phishing-resistant sign-in such as passkeys or certificate-based authentication, and blocking access from unmanaged or non-compliant devices.
Key takeaways
- Biometrics unlock a key stored in secure hardware; the biometric itself stays on the device.
- Passkeys give phishing-resistant sign-in on Android and iOS.
- Push MFA should use number matching to resist fatigue attacks.
- Device compliance checks stop access from rooted or unpatched phones.
- SMS codes are the weakest common option.
Table of Contents
- What Are the Levels of Mobile Authentication?
- How Secure Are PINs and Biometrics?
- Which App Sign-In Methods Are Strongest?
- How Do Device Compliance and MDM Fit In?
- How Do Organisations Implement This?
- What Should App Developers Do?
- How Do You Handle Lost Phones and Account Recovery?
- References
What Are the Levels of Mobile Authentication?
| Level | Methods |
|---|---|
| Device unlock | PIN, passcode, fingerprint, face recognition |
| User sign-in to apps | Passkeys, authenticator apps, push with number matching, SSO |
| Device trust | MDM enrolment, compliance checks, device certificates |
How Secure Are PINs and Biometrics?
Modern phones store biometric templates in secure hardware and use them to unlock keys, as described in Apple's platform security guide; Android uses similar protections. Biometrics are convenient, but the PIN or passcode remains the fallback, so it should be at least six digits or an alphanumeric passcode. NIST SP 800-63B treats biometrics as acceptable only when bound to a specific device and combined with another factor.
Which App Sign-In Methods Are Strongest?
| Method | Phishing resistant | Notes |
|---|---|---|
| Passkeys | Yes | Synced via iCloud Keychain or Google Password Manager; see FIDO Alliance |
| Certificate-based authentication | Yes | Device certificates deployed by MDM |
| Push with number matching | Partly | Resists approval fatigue |
| Authenticator app codes (TOTP) | No | Better than SMS |
| SMS codes | No | Vulnerable to SIM swap and interception |
How Do Device Compliance and MDM Fit In?
Mobile device management can require encryption, a passcode, a minimum OS version and no jailbreak or root. Conditional access then allows corporate apps only from compliant devices, as in Microsoft Intune device compliance. NIST SP 800-124 Rev. 2 covers enterprise mobile device security. For personal devices (BYOD), app protection policies can secure corporate data without full device control.
How Do Organisations Implement This?
- Enrol corporate devices in MDM; use app protection for BYOD.
- Set compliance rules: encryption, passcode, OS version, no root or jailbreak.
- Enable SSO with phishing-resistant methods (passkeys, certificates).
- Disable SMS as an MFA method where possible; enable number matching for push.
- Block access from non-compliant devices with conditional access.
- Plan account recovery that does not weaken security.
What Should App Developers Do?
- Support passkeys through Android Credential Manager and Apple's AuthenticationServices.
- Use platform biometric APIs tied to keys in secure hardware, not custom biometric checks.
- Store tokens in the Keychain or Android Keystore, never in plain storage.
- Re-authenticate for sensitive actions such as payments.
Related: authentication mechanisms and secure mobile protocols. WebAsha offers mobile security training.
How Do You Handle Lost Phones and Account Recovery?
- Register at least two phishing-resistant methods (for example a passkey on the phone and a hardware security key).
- Use MDM remote lock and wipe for corporate devices.
- Require strong identity checks before help desk recovery, not just answers to security questions.
- Revoke sessions and tokens for the lost device: in Microsoft Entra,
Revoke-MgUserSignInSession.
Apple and Google document Find My and Find My Device for locating and erasing lost phones.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.