Tokenization vs Encoding vs Encryption: Differences and Uses
Encoding changes data into another format so systems can handle it, and anyone can reverse it, so it provides no security. Encryption uses a key to make data unreadable; only someone with the right key can decrypt it. Tokenization replaces sensitive data, such as a card number, with a random substitute that has no mathematical link to the original; the real value is kept in a protected vault.
Topic: Cybersecurity Foundations in Cybersecurity & Ethical Hacking · Comparison
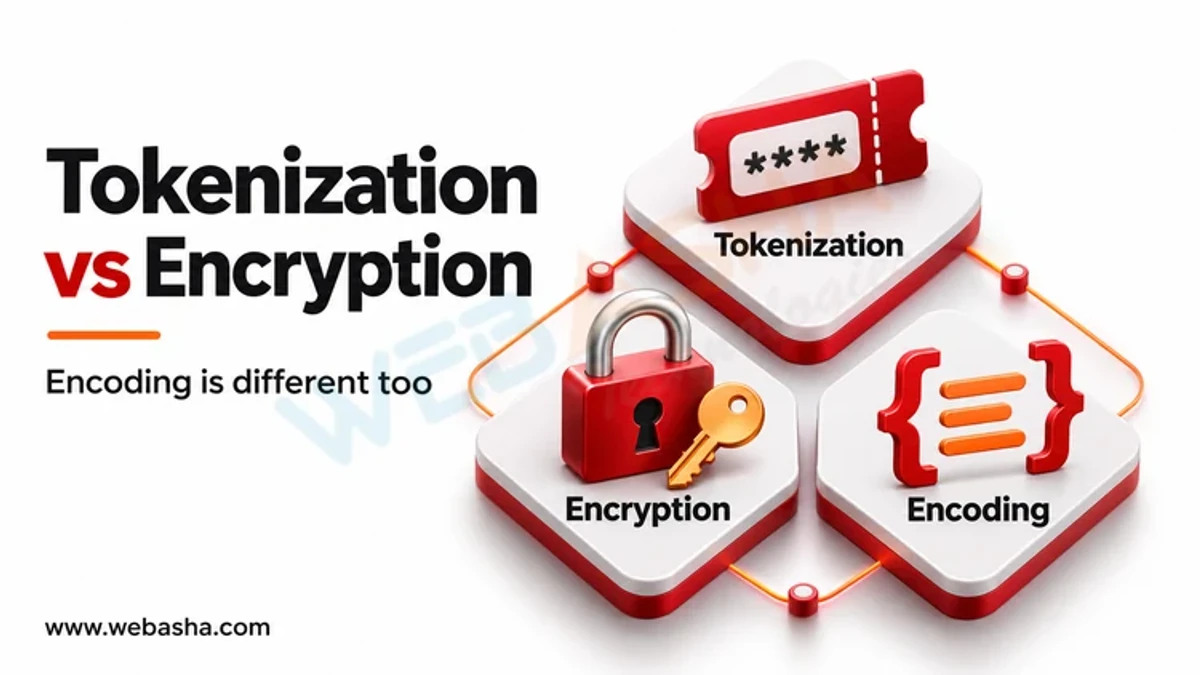
Quick answer: Encoding changes data into another format so systems can handle it, and anyone can reverse it, so it provides no security. Encryption uses a key to make data unreadable; only someone with the right key can decrypt it. Tokenization replaces sensitive data, such as a card number, with a random substitute that has no mathematical link to the original; the real value is kept in a protected vault. Use encoding for compatibility, encryption to protect data in storage and transit, and tokenization to remove sensitive data from systems that do not need it.
Key takeaways
- Base64 and URL encoding are not security controls.
- Encryption security depends entirely on key management.
- A token cannot be reversed without access to the token vault.
- Tokenization can shrink PCI DSS scope because systems hold tokens, not card numbers.
- Hashing is a fourth, one-way technique used for passwords and integrity checks.
Table of Contents
- What Is Encoding?
- What Is Encryption?
- What Is Tokenization?
- Where Does Hashing Fit?
- How Do They Compare?
- What Does Each Look Like in Code?
- When Should You Use Each?
- What Mistakes Should You Avoid?
- How Should Encryption Keys Be Managed?
- Where Is Tokenization Required in India?
- References
What Is Encoding?
Encoding represents data using a public, reversible scheme. Base64 (RFC 4648) turns binary data into text so it can travel in email or JSON. URL encoding replaces spaces and special characters. UTF-8 encodes characters as bytes. No key is involved, so encoding hides nothing. A common audit finding is "encrypted" credentials that are actually Base64 strings.
What Is Encryption?
Encryption transforms data with an algorithm and a key. Symmetric encryption such as AES (FIPS 197) uses one key for both directions and protects stored data and bulk traffic. Asymmetric encryption such as RSA or elliptic-curve schemes uses a public key to encrypt and a private key to decrypt, and is used for key exchange and signatures. Authenticated modes such as AES-GCM also detect tampering.
Encrypted data keeps its sensitivity: whoever gets the key gets the data. Format-preserving encryption (NIST SP 800-38G) produces ciphertext in the same format as the input, such as 16 digits for a card number, which helps legacy systems but is still encryption.
What Is Tokenization?
A tokenization service receives a sensitive value, stores it in a secured vault, and returns a random token. Applications store and pass around the token. Only systems allowed to call the detokenization service can get the original back.
- Vault-based: a database maps tokens to values. Simple and strong; the vault becomes the critical system.
- Vaultless: tokens are derived using cryptographic techniques and keys, avoiding a large lookup table. Security then depends on key protection, much like encryption.
- Payment network tokens: card schemes issue device- or merchant-specific tokens for mobile wallets and stored cards.
The PCI Security Standards Council's tokenization guidance explains how systems that only see tokens may fall outside PCI DSS scope, provided they cannot detokenize.
Where Does Hashing Fit?
Hashing produces a fixed-length fingerprint that cannot be reversed. It suits password storage (with slow algorithms such as Argon2id or bcrypt) and integrity checks (SHA-256). It is not suitable when you need the original value back. Unsalted hashes of short values such as card numbers or phone numbers can be reversed by brute force, so they are not a substitute for tokenization.
How Do They Compare?
| Encoding | Encryption | Tokenization | Hashing | |
|---|---|---|---|---|
| Purpose | Compatibility | Confidentiality | Remove sensitive data | Integrity, passwords |
| Reversible | Yes, by anyone | Yes, with the key | Yes, via the vault | No |
| Needs a secret | No | Key | Vault access or key | No (salt is not secret) |
| Output format | Defined by scheme | Binary, or same format with FPE | Often same format | Fixed length |
| Example | Base64 | AES-256-GCM | Card token | SHA-256, Argon2id |
What Does Each Look Like in Code?
This Python example uses the standard library and the cryptography package (pip install cryptography). The token vault is a dictionary purely for demonstration.
import base64, hashlib, secrets
from cryptography.hazmat.primitives.ciphers.aead import AESGCM

card = "4111111111111111"   # standard test card number

# Encoding: reversible by anyone
enc = base64.b64encode(card.encode()).decode()
print("base64:", enc, "->", base64.b64decode(enc).decode())

# Encryption: reversible only with the key
key = AESGCM.generate_key(bit_length=256)
nonce = secrets.token_bytes(12)
ct = AESGCM(key).encrypt(nonce, card.encode(), None)
print("aes-gcm:", ct.hex()[:32], "...")
print("decrypt:", AESGCM(key).decrypt(nonce, ct, None).decode())

# Tokenization: random token, real value kept in a vault
vault = {}
token = "tok_" + secrets.token_hex(8)
vault[token] = card
print("token:", token, "last4:", card[-4:])
print("detokenize:", vault[token])

# Hashing: one way
print("sha256:", hashlib.sha256(card.encode()).hexdigest()[:32], "...")
When Should You Use Each?
- Encoding: sending binary in text formats, building URLs, storing characters correctly.
- Encryption: disks, backups, database fields, files and all network traffic (TLS).
- Tokenization: card numbers, national identity numbers such as Aadhaar, and bank details in systems that only need a reference.
- Hashing: passwords, file integrity, deduplication.
What Mistakes Should You Avoid?
- Calling Base64 "encryption" in documentation or code.
- Storing encryption keys next to the encrypted data.
- Allowing every application to detokenize.
- Using fast hashes such as MD5 or plain SHA-256 for passwords.
The OWASP Cryptographic Storage Cheat Sheet covers algorithm and key choices. See also encryption best practices for sharing data, or ask WebAsha about data security training.
How Should Encryption Keys Be Managed?
Encryption moves the problem from protecting data to protecting keys. NIST SP 800-57 Part 1 covers key lifecycles. In practice:
- Keep keys in a key management service (AWS KMS, Azure Key Vault, Google Cloud KMS) or a hardware security module, not in code or configuration files.
- Use envelope encryption: a data key encrypts the data, and a master key in the KMS encrypts the data key.
- Rotate keys on a schedule and when staff with access leave.
- Log every use of a key and alert on unusual decrypt activity.
# AWS KMS: generate a data key for envelope encryption
aws kms generate-data-key --key-id alias/app-data --key-spec AES_256   --query "{Plain:Plaintext,Encrypted:CiphertextBlob}"
# Use the plaintext key in memory to encrypt, store only the encrypted key.
Where Is Tokenization Required in India?
The Reserve Bank of India's card-on-file tokenisation rules took effect on 1 October 2022. Merchants and payment aggregators may no longer store customers' full card numbers; instead, they store tokens issued by card networks or banks with the customer's consent. The RBI's FAQ on card tokenisation explains how it works. The practical effect is that most Indian e-commerce sites now save a token rather than your card number when you choose to save a card.
References
- RFC 4648, Base16, Base32 and Base64 Encodings
- NIST FIPS 197, Advanced Encryption Standard
- NIST SP 800-38G, Format-Preserving Encryption
- PCI SSC Document Library (tokenization guidelines)
- OWASP Cryptographic Storage Cheat Sheet
- NIST SP 800-57 Part 1 Rev. 5, Recommendation for Key Management
- RBI, FAQs on tokenisation of card transactions
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.