Public vs Private DNS Zones: Differences and How DNS Works
A public DNS zone holds records anyone on the internet can look up, such as the address of your website or your mail servers. A private DNS zone holds records that only resolve inside a specific network, such as a corporate network or a cloud VPC, for internal servers and databases.
Topic: Networking in IT Infrastructure · Comparison
Also covers: Cloud Computing: AWS, Azure & GCP, Network Security
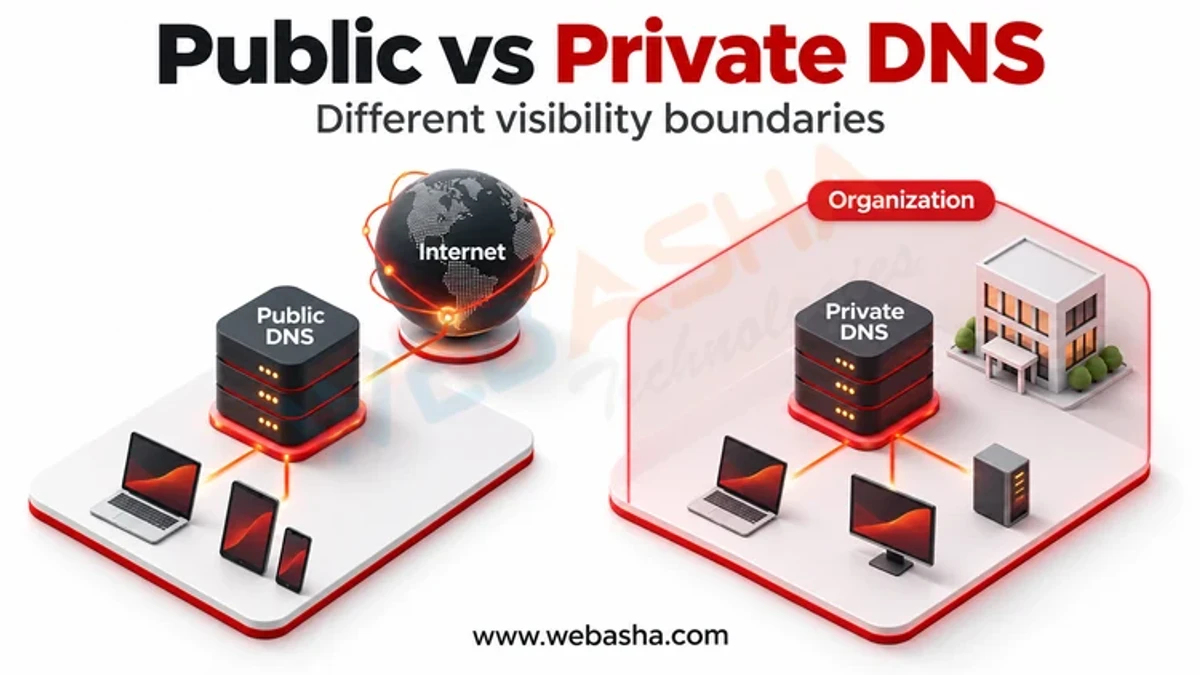
Quick answer: A public DNS zone holds records anyone on the internet can look up, such as the address of your website or your mail servers. A private DNS zone holds records that only resolve inside a specific network, such as a corporate network or a cloud VPC, for internal servers and databases. DNS itself works by your device asking a recursive resolver, which queries the root servers, then the top-level domain servers, then the domain's authoritative servers, and caches the answer. Many organisations use both, sometimes with the same domain name returning different answers inside and outside (split-horizon DNS).
Key takeaways
- Public zones are for internet-facing services; private zones for internal ones.
- Cloud providers offer private zones attached to virtual networks.
- Never publish internal hostnames or IP addresses in public zones.
- Restrict zone transfers and sign public zones with DNSSEC.
- Split-horizon DNS needs careful management to avoid confusion.
Table of Contents
- How Does DNS Resolution Work?
- What Is a DNS Zone?
- How Do Public and Private Zones Differ?
- How Do Private Zones Work in the Cloud?
- What Is Split-Horizon DNS?
- Which Record Types Should You Know?
- How Do You Secure DNS Zones?
- References
How Does DNS Resolution Work?
- Your device's stub resolver asks a recursive resolver (your company's, your ISP's, or a public one).
- If not cached, the resolver asks a root server where to find
.com. - The
.comTLD servers point to the domain's authoritative name servers. - The authoritative server returns the record, for example the A record for www.example.com.
- The resolver caches it for the record's TTL and returns it to your device.
# Follow the full resolution path
dig +trace www.example.com

# Ask a specific resolver for a record
dig @8.8.8.8 example.com MX
The concepts are defined in RFC 1034, and current terminology in RFC 8499.
What Is a DNS Zone?
A zone is a portion of the DNS namespace managed as a unit by one set of authoritative servers, for example everything under example.com except any delegated subdomains. It contains records such as SOA, NS, A, AAAA, MX, CNAME and TXT.
How Do Public and Private Zones Differ?
| Public zone | Private zone | |
|---|---|---|
| Who can query | Anyone on the internet | Only clients in linked networks |
| Typical records | Website, mail, public APIs | Internal apps, databases, domain controllers |
| Delegated from TLD | Yes | No |
| Examples | Public hosted zone, registrar DNS | Route 53 private hosted zone, Azure Private DNS, AD-integrated DNS |
| Main risk | Hijacking, information exposure | Misconfiguration breaking internal access |
How Do Private Zones Work in the Cloud?
- AWS: Route 53 private hosted zones are associated with one or more VPCs.
- Azure: Azure Private DNS zones link to virtual networks, with optional auto-registration of VMs.
- Google Cloud: Cloud DNS private zones are visible to authorised VPC networks.
Hybrid setups use resolver endpoints or conditional forwarders so on-premises and cloud systems can resolve each other's private names.
What Is Split-Horizon DNS?
Split-horizon (split-brain) DNS serves different answers for the same name depending on where the query comes from: for example, app.example.com resolves to a private IP inside the network and a public load balancer outside. It is useful, but records must be kept in sync, and troubleshooting needs you to know which view a client sees.
Which Record Types Should You Know?
| Record | Purpose |
|---|---|
| A / AAAA | IPv4 / IPv6 address |
| CNAME | Alias to another name |
| MX | Mail servers |
| TXT | Verification, SPF, DKIM, DMARC |
| NS / SOA | Zone authority information |
| PTR | Reverse lookup |
How Do You Secure DNS Zones?
- Keep internal names out of public zones.
- Allow zone transfers (AXFR) only to your secondary servers.
- Sign public zones with DNSSEC.
- Remove dangling records that point to deleted cloud resources.
- Protect registrar and DNS hosting accounts with MFA, as NIST SP 800-81-2 and later guidance recommend.
# Check that your server refuses zone transfers to outsiders
dig @ns1.example.com example.com AXFR
Related: DNS attacks and SOC defences and DNS poisoning. WebAsha offers networking and cloud training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.