12-Step Checklist for Cloud Incident Response: Step-by-Step Guide
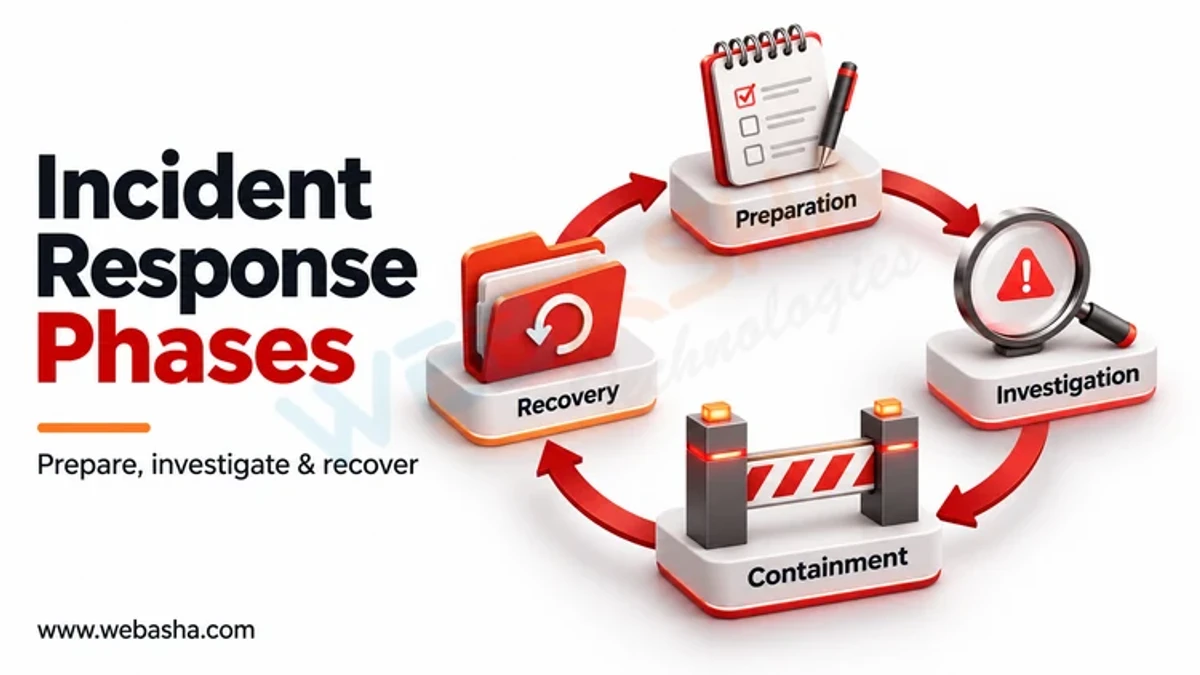
A cloud incident response checklist covers twelve steps: prepare roles and access in advance, make sure logging is on, detect and triage alerts, scope affected accounts and resources, contain compromised identities first, then isolate affected resources, preserve evidence such as logs and disk snapshots, remove the attacker's access and persistence, recover from clean sources, notify regulators and customers on…
Topic: Incident Response & Digital Forensics in Cybersecurity & Ethical Hacking · Lab / project
Also covers: Cloud & Container Security, Cloud Computing: AWS, Azure & GCP
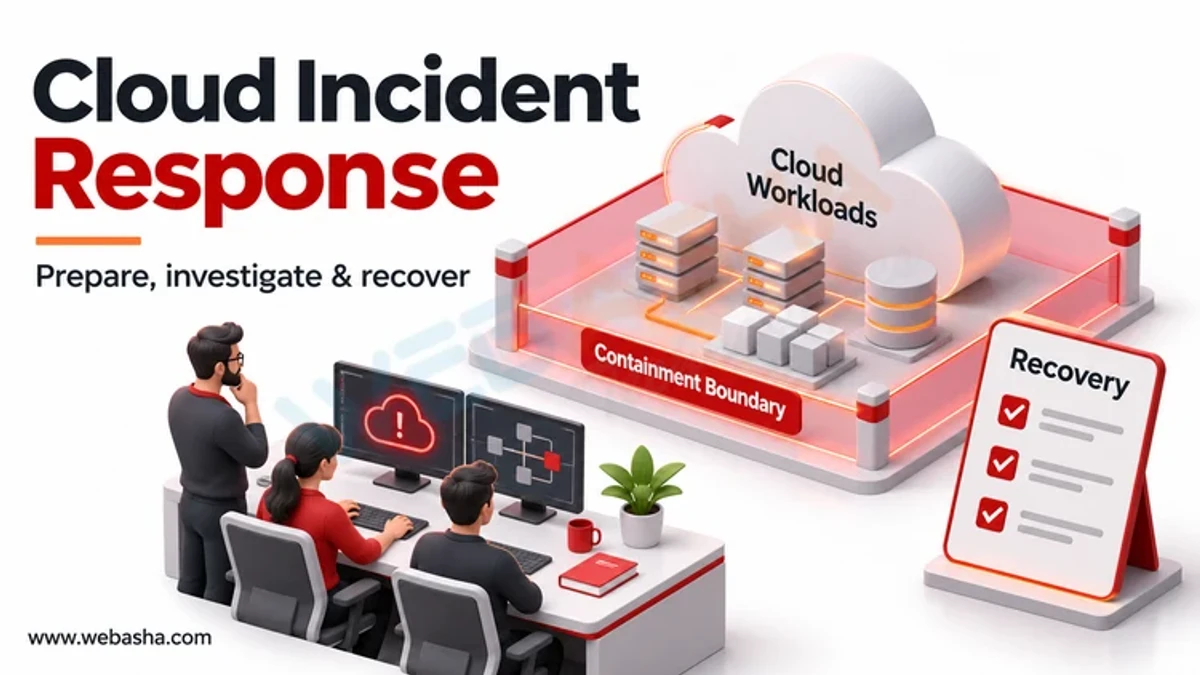
Quick answer: A cloud incident response checklist covers twelve steps: prepare roles and access in advance, make sure logging is on, detect and triage alerts, scope affected accounts and resources, contain compromised identities first, then isolate affected resources, preserve evidence such as logs and disk snapshots, remove the attacker's access and persistence, recover from clean sources, notify regulators and customers on time, and review lessons learned. Cloud incidents differ from on-premises ones because identities and API keys are the main attack path, evidence lives in provider logs, and responsibilities are shared with the provider.
Key takeaways
- In the cloud, compromised credentials are the most common starting point, so contain identities first.
- Audit logs such as CloudTrail or Azure Activity Logs must be enabled before an incident.
- Snapshot before you delete; evidence disappears quickly in cloud environments.
- NIST SP 800-61 Rev. 3 aligns incident response with the CSF 2.0 functions.
- In India, report specified incidents to CERT-In within six hours.
Table of Contents
- What Are the 12 Steps?
- What Should Be Ready Before an Incident?
- Which Logs Matter Most?
- How Do You Contain a Cloud Incident?
- How Do You Preserve Evidence?
- Who Must Be Notified?
- How Does Shared Responsibility Affect Response?
- References
What Are the 12 Steps?
| # | Step | Key action |
|---|---|---|
| 1 | Prepare | Playbooks, contacts, break-glass accounts, forensic account |
| 2 | Enable logging | Audit, network flow and service logs centralised and retained |
| 3 | Detect | Alerts from GuardDuty, Defender for Cloud, Security Command Center or SIEM |
| 4 | Triage | Confirm it is real; assign severity and an incident lead |
| 5 | Scope | Which accounts, identities, regions and data are affected |
| 6 | Contain identities | Disable keys, revoke sessions, reset credentials |
| 7 | Contain resources | Isolate instances with restrictive security groups |
| 8 | Preserve evidence | Snapshots, memory where possible, log exports |
| 9 | Eradicate | Remove backdoor users, roles, keys, functions and policies |
| 10 | Recover | Rebuild from clean images and infrastructure-as-code |
| 11 | Notify | Regulators, customers, provider and law enforcement as required |
| 12 | Learn | Post-incident review and control improvements |
These steps follow NIST SP 800-61 Rev. 3 and the AWS Security Incident Response Guide.
What Should Be Ready Before an Incident?
- A named incident lead and contacts for legal, communications and the cloud provider.
- Pre-approved responder roles with read access to all accounts.
- A separate forensic account or subscription to copy evidence into.
- Playbooks for common cases: leaked access key, exposed storage, compromised VM, ransomware.
- Exercises at least yearly; CISA's response playbooks are a useful template.
Which Logs Matter Most?
| Need | AWS | Azure | Google Cloud |
|---|---|---|---|
| API and control plane activity | CloudTrail | Activity Log | Cloud Audit Logs |
| Sign-ins | CloudTrail (console logins) | Entra ID sign-in logs | Cloud Identity / Workspace logs |
| Network | VPC Flow Logs | VNet flow logs | VPC Flow Logs |
| Threat detection | GuardDuty | Defender for Cloud | Security Command Center |
How Do You Contain a Cloud Incident?
Start with identities, because attackers usually act through stolen keys or tokens:
# AWS: deactivate a leaked access key
aws iam update-access-key --user-name app-user --access-key-id AKIAEXAMPLE --status Inactive

# AWS: isolate an instance with a security group that has no rules
aws ec2 modify-instance-attribute --instance-id i-0abc123 --groups sg-0isolation

# Microsoft Entra ID: revoke a user's sessions (Microsoft Graph PowerShell)
Revoke-MgUserSignInSession -UserId [email protected]
Check for persistence the attacker may have added: new users, access keys, roles with trust to outside accounts, Lambda functions or automation runbooks. Microsoft's incident response guidance covers equivalent steps in Azure.
How Do You Preserve Evidence?
- Snapshot affected disks before terminating instances.
- Export relevant logs to the forensic account with write-once storage.
- Record every action responders take, with times.
- Hash exported evidence and document chain of custody, which matters for court use under the Bharatiya Sakshya Adhiniyam 2023, Section 63.
# AWS: snapshot an instance volume for forensics
aws ec2 create-snapshot --volume-id vol-0abc123 --description "IR-2026-014 evidence"
Who Must Be Notified?
- CERT-In: specified incidents within six hours, with logs kept for 180 days (CERT-In directions).
- Data Protection Board and affected individuals: personal data breaches under the DPDP Act 2023 and its rules.
- Sector regulators: RBI, SEBI or IRDAI for regulated entities.
- Your cloud provider: for abuse reports and support.
- Customers and partners as contracts require.
How Does Shared Responsibility Affect Response?
The provider secures the underlying infrastructure; you secure your identities, configurations, data and workloads. Most cloud incidents fall on the customer side, so you cannot wait for the provider to respond. Google Cloud describes its own side in its data incident response process. Related: preparing for incident response and common security misconfigurations. WebAsha offers cloud security and incident response training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.