DNS Blind Spots: How Attackers Hide Malware in DNS Records
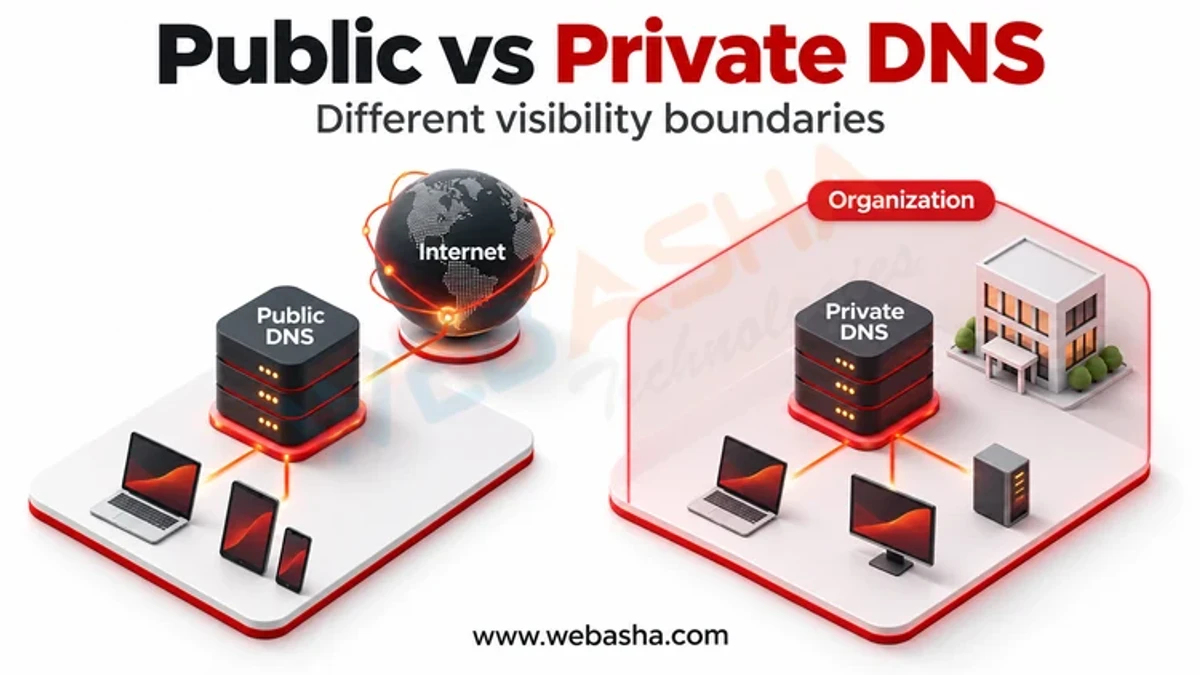
In July 2025, DomainTools researchers reported a technique where hackers exploit DNS blind spots to store and deliver malware using DNS TXT records. By partitioning executable files into hexadecimal chunks and embedding them across subdomains, attackers bypass traditional security tools that don't monitor DNS traffic. This technique, seen in DNS records from 2021 and 2022, uses encrypted DNS protocols like DoH and DoT, further complicating detection. Organizations must now prioritize DNS monitoring, filtering, and inspection strategies as core parts of their cyber defense frameworks to combat this stealthy malware delivery method.