Is a VPN Enough on Public Wi-Fi? What It Protects and What It Misses
A VPN encrypts traffic between your device and the VPN server, so other people on the same public Wi-Fi cannot read or tamper with it. That protects you from eavesdropping and some fake-hotspot attacks. It does not stop phishing pages, malware, weak or reused passwords, risky app permissions or tracking by the websites you visit, and it moves trust to the VPN provider.
Topic: Network Security in Cybersecurity & Ethical Hacking · Explainer
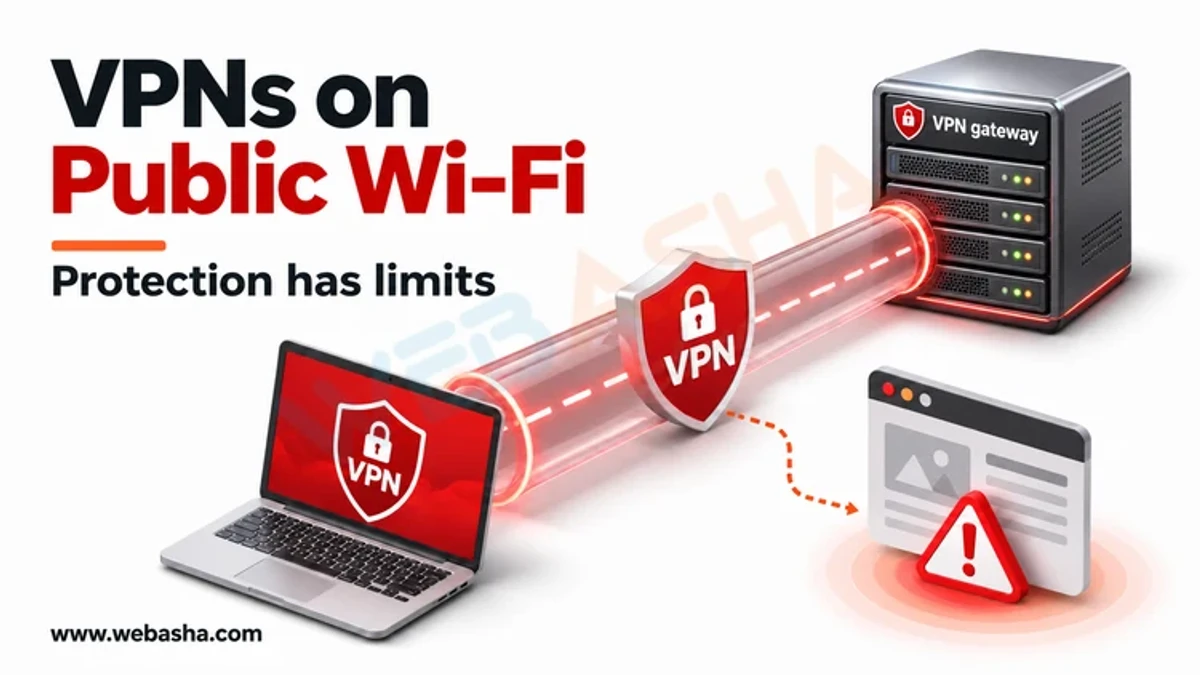
Quick answer: A VPN encrypts traffic between your device and the VPN server, so other people on the same public Wi-Fi cannot read or tamper with it. That protects you from eavesdropping and some fake-hotspot attacks. It does not stop phishing pages, malware, weak or reused passwords, risky app permissions or tracking by the websites you visit, and it moves trust to the VPN provider. Use it as one layer with HTTPS, multi-factor authentication, updated devices and, where possible, your own mobile hotspot.
Key takeaways
- Most websites already use HTTPS, so a VPN mainly adds protection for DNS, older apps and metadata.
- A VPN cannot help if you type your password into a fake login page.
- Captive portals on hotel and airport Wi-Fi run before the VPN connects.
- Your VPN provider can see your traffic metadata; choose one you trust.
- In India, CERT-In's 2022 directions require VPN service providers to keep subscriber records.
Table of Contents
- What Does a VPN Actually Do?
- Which Public Wi-Fi Threats Does It Stop?
- Why Are Captive Portals a Weak Spot?
- How Do You Check Your VPN Is Working?
- How Should You Choose a VPN?
- What Is a Safe Public Wi-Fi Routine?
- How Do VPN Protocols Compare?
- What Can Your VPN Provider See?
- References
What Does a VPN Actually Do?
A VPN builds an encrypted tunnel from your device to a server run by the VPN provider or your employer. Everything inside the tunnel, including DNS lookups if configured correctly, is unreadable to the café router and other users. From the server onwards, traffic travels normally to the website, so the site sees the VPN server's address instead of yours.
Which Public Wi-Fi Threats Does It Stop?
| Threat | Does a VPN help? | What else you need |
|---|---|---|
| Eavesdropping on unencrypted traffic | Yes | HTTPS everywhere |
| DNS spoofing by the hotspot | Yes, if DNS goes through the tunnel | Leak test, or DNS over HTTPS |
| Evil twin hotspot | Partly: it protects traffic after connection | Verify network name; avoid auto-join |
| Phishing pages | No | Passkeys or MFA, careful link checks |
| Malware downloads | No | Updates, endpoint protection |
| Attacks on open file sharing | Partly | Firewall set to public network profile |
| Website tracking and cookies | No | Browser privacy settings |
The NSA's guidance on securing wireless devices in public settings recommends avoiding public Wi-Fi where possible and using an encrypted VPN when you must. Networks that use WPA3 or Wi-Fi Enhanced Open encrypt each user's link to the access point, which reduces, but does not remove, the risk.
Why Are Captive Portals a Weak Spot?
Hotel and airport networks show a sign-in page before allowing internet access. Your VPN cannot connect until you complete it, so for that moment you are exposed. Never enter account passwords or card details on a portal page, and check the page uses HTTPS. Some VPN apps have an always-on mode that blocks other traffic until the tunnel is up; enable it after you pass the portal.
How Do You Check Your VPN Is Working?
Compare your public address and DNS resolver with the VPN on and off:
# public IP address seen by the internet
curl -s https://ifconfig.me ; echo

# which DNS servers your system uses (Linux with systemd-resolved)
resolvectl status | grep -A2 "DNS Servers"

# WireGuard: confirm a recent handshake and traffic counters
sudo wg show

# Windows PowerShell: list active VPN connections
Get-VpnConnection | Where-Object ConnectionStatus -eq "Connected"
If the DNS servers listed belong to the hotspot while the VPN is on, you have a DNS leak. Enable the VPN app's DNS protection, or use DNS over HTTPS (RFC 8484) in your browser.
How Should You Choose a VPN?
- Use your employer's VPN for work; personal VPNs are not a replacement.
- Prefer modern protocols such as WireGuard or IKEv2, and avoid PPTP.
- Read the privacy policy and any independent audits.
- Look for a kill switch and DNS leak protection.
- Be wary of free VPNs that earn money from your data.
In India, CERT-In's April 2022 directions require VPN service providers to keep subscriber details such as names, addresses and purpose of use for five years, so a VPN is a privacy tool against the network you are on, not against lawful requests.
What Is a Safe Public Wi-Fi Routine?
- Prefer your phone's hotspot for banking and work.
- Confirm the exact network name with staff before joining.
- Turn off auto-join for open networks and forget them afterwards.
- Set the network as public so file sharing and discovery are off.
- Connect the VPN after the portal and before anything else.
- Use passkeys or MFA so a stolen password is not enough.
Read our guides on how a VPN works and fake Wi-Fi hotspots, or talk to a WebAsha training advisor about network security courses.
How Do VPN Protocols Compare?
| Protocol | Strengths | Watch out for |
|---|---|---|
| WireGuard | Small codebase, modern cryptography, fast reconnects on mobile | Static peer keys need careful management |
| IKEv2/IPsec (RFC 7296) | Built into Windows, macOS, iOS and Android; handles network changes well | Configuration is complex; some networks block it |
| OpenVPN | Mature, flexible, can run over TCP 443 to pass restrictive networks | Slower than WireGuard on many devices |
| PPTP | None worth relying on | Broken security; do not use |
A WireGuard client configuration that sends all traffic, including DNS, through the tunnel looks like this:
[Interface]
PrivateKey = <client-private-key>
Address = 10.8.0.2/32
DNS = 10.8.0.1

[Peer]
PublicKey = <server-public-key>
Endpoint = vpn.example.com:51820
AllowedIPs = 0.0.0.0/0, ::/0     # route everything through the VPN
PersistentKeepalive = 25
Setting AllowedIPs to all addresses is what makes it a full tunnel. A split tunnel that lists only company ranges leaves your other browsing exposed to the hotspot.
What Can Your VPN Provider See?
| Data | Hotspot operator | VPN provider | Website |
|---|---|---|---|
| Your real IP address | Yes | Yes | No |
| Domains you visit | No, with VPN DNS | Yes, unless you use encrypted DNS inside the tunnel | Only its own |
| Page content on HTTPS sites | No | No | Yes |
| Your account logins and cookies | No | No | Yes |
This is why choosing a trustworthy provider matters: you move visibility of your browsing from the café to the VPN company.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.