Vulnerability Management Life Cycle: The 5 Essential Stages
The vulnerability management life cycle is a continuous process for finding and fixing security weaknesses before attackers use them. A common five-stage version is: 1) discover assets and scan for vulnerabilities, 2) prioritise findings by risk, 3) remediate or mitigate, 4) verify that fixes worked, and 5) report and improve.
Topic: Penetration Testing in Cybersecurity & Ethical Hacking · Lab / project
Also covers: Cybersecurity Foundations, Cyber Threats, Scams & Online Safety, Ethical Hacking
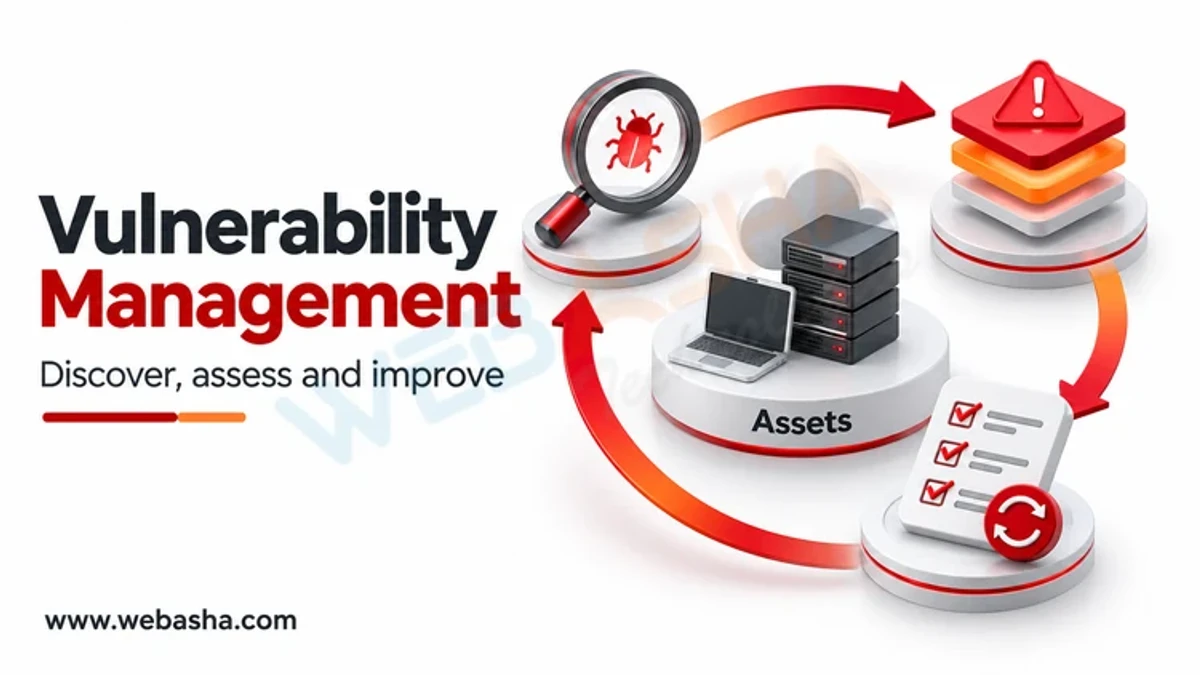
Quick answer: The vulnerability management life cycle is a continuous process for finding and fixing security weaknesses before attackers use them. A common five-stage version is: 1) discover assets and scan for vulnerabilities, 2) prioritise findings by risk, 3) remediate or mitigate, 4) verify that fixes worked, and 5) report and improve. Prioritisation should combine severity (FIRST CVSS), exploitation likelihood (FIRST EPSS), confirmed exploitation (the CISA KEV catalog) and how important the asset is. NIST SP 800-40 Rev. 4 frames patching as routine preventive maintenance. The cycle repeats because new assets and new vulnerabilities appear every day.
Key takeaways
- You cannot protect assets you do not know about.
- CVSS measures severity, not the chance of attack.
- KEV and EPSS help put exploited flaws first.
- Verification closes the loop; a ticket is not a fix.
- Metrics show whether the programme actually reduces risk.
Table of Contents
- What Is the Vulnerability Management Life Cycle?
- How Do You Discover Assets and Vulnerabilities?
- How Should Vulnerabilities Be Prioritised?
- What Are the Remediation Options?
- How Do You Verify Fixes?
- What Should You Report and Measure?
- What Are Common Mistakes?
- References
What Is the Vulnerability Management Life Cycle?
It is the repeating loop that keeps exposure low. Vendors describe it with five to seven stages, but the work is the same.
| Stage | Main activity | Output |
|---|---|---|
| 1. Discover | Inventory assets, scan | Asset list and findings |
| 2. Prioritise | Rank by risk | Ordered remediation queue |
| 3. Remediate | Patch, configure, mitigate | Changes applied |
| 4. Verify | Rescan and test | Confirmed closure |
| 5. Report and improve | Metrics and reviews | Updated SLAs and process |
For a tool-focused view, see our guide to Qualys vulnerability management. This post covers the process regardless of tool.
How Do You Discover Assets and Vulnerabilities?
- Build an inventory from CMDB, cloud APIs, EDR and network discovery.
- Run authenticated scans where possible; they find more than unauthenticated ones.
- Include cloud, containers, web apps and internet-facing assets.
- Track vendor and CERT-In advisories for systems scanners miss.
Scanning systems you do not own needs written authorisation; unauthorised access is an offence under Sections 43 and 66 of India's IT Act 2000.
How Should Vulnerabilities Be Prioritised?
| Signal | What it tells you | Source |
|---|---|---|
| CVSS score | Technical severity | FIRST CVSS v4.0, NVD |
| EPSS probability | Estimated chance of exploitation in the next 30 days | FIRST EPSS |
| KEV listing | Confirmed exploitation in the wild | CISA KEV |
| Decision tree | Act, attend, track based on context | CISA SSVC |
| Asset criticality | Business impact if exploited | Your inventory |
These signals answer different questions. A flaw with a CVSS score of 9.8 on an isolated test server may matter less than a 7.5 on an internet-facing VPN that appears in KEV. EPSS adds a data-driven estimate for the many vulnerabilities that are not yet in KEV. SSVC turns the inputs into a decision, such as act now or track, which is easier for IT teams to follow than raw scores. Write the rules down as service level targets, for example days to fix by category, so owners know what is expected.
A practical rule: internet-facing assets with KEV-listed flaws go first. US federal agencies must fix KEV entries by set deadlines under BOD 22-01, a useful benchmark for others. Prioritisation feeds your wider risk management process.
What Are the Remediation Options?
- Remediate: apply the patch or upgrade.
- Mitigate: apply workarounds, disable features, segment or add WAF rules until a patch is possible.
- Accept: document risk acceptance with an owner and expiry date.
NIST SP 800-40 Rev. 4 recommends defined maintenance groups and plans, including emergency patching for urgent cases.
How Do You Verify Fixes?
Rescan the asset, confirm the version, and check that services restarted. On Windows, an administrator can list installed updates to confirm a patch:
Get-HotFix | Sort-Object InstalledOn -Descending | Select-Object -First 10On Debian or Ubuntu, list packages with pending updates:
apt list --upgradableClose the ticket only after verification passes.
What Should You Report and Measure?
- Mean time to remediate, by severity and KEV status.
- Percentage of assets scanned in the last cycle.
- Open KEV-listed vulnerabilities on internet-facing assets.
- Overdue items against SLA, and active risk acceptances.
What Are Common Mistakes?
- Fixing by CVSS score alone.
- Scanning without a current asset inventory.
- Closing tickets without rescanning.
- Letting risk acceptances never expire.
WebAsha offers vulnerability assessment and VAPT training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.