What Is a Polymorphic Virus and How Do Defenders Detect It?
A polymorphic virus is malicious code that changes how it looks each time it copies itself, while its behaviour stays the same. It usually does this by encrypting its main body with a new key and wrapping it in a decryptor that is rewritten on every infection. Because the file bytes differ each time, a single fixed signature cannot match every copy.
Topic: Cyber Threats, Scams & Online Safety in Cybersecurity & Ethical Hacking · Tutorial
Also covers: SOC & Blue Team, Cybersecurity Foundations
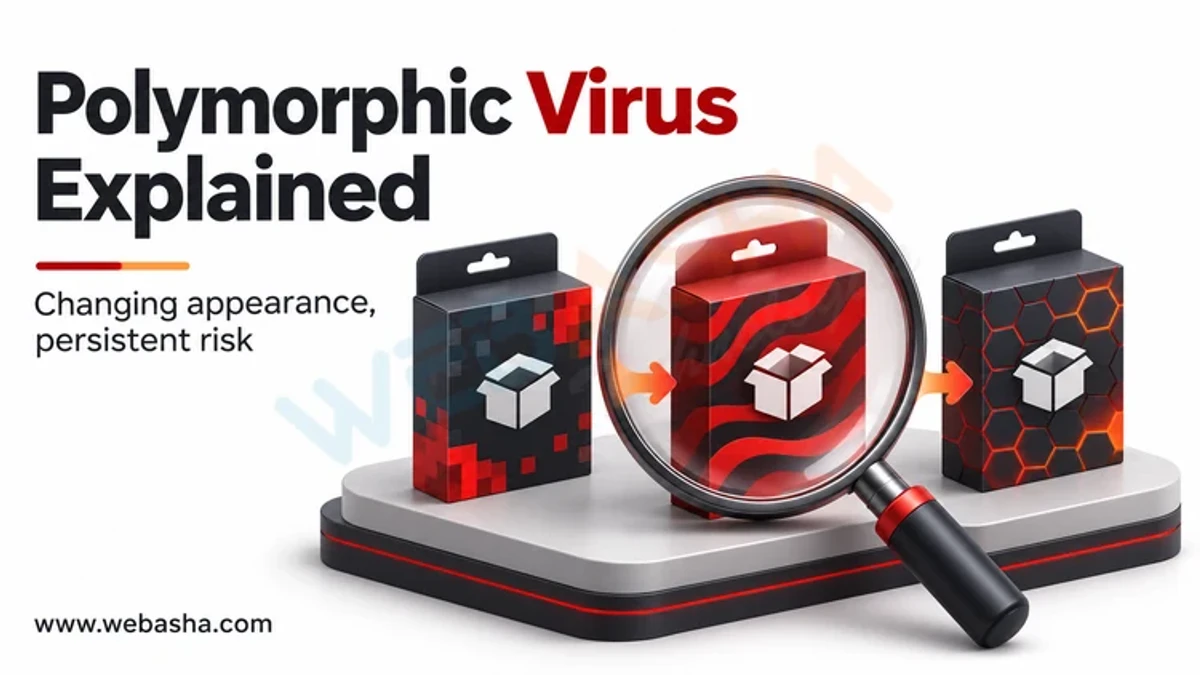
Quick answer: A polymorphic virus is malicious code that changes how it looks each time it copies itself, while its behaviour stays the same. It usually does this by encrypting its main body with a new key and wrapping it in a decryptor that is rewritten on every infection. Because the file bytes differ each time, a single fixed signature cannot match every copy. Defenders detect it by watching what the code does when it runs, scanning memory after it decrypts itself, using cloud reputation and machine learning, and limiting what untrusted programs can execute. Updated endpoint protection plus application control handles most polymorphic threats.
Key takeaways
- Polymorphism changes appearance, not purpose.
- Encryption plus a mutating decryptor is the classic design.
- Metamorphic code goes further and rewrites its whole body.
- Behaviour, memory and cloud analysis beat fixed signatures.
- Patching, application control and least privilege cut the risk.
Table of Contents
- How Does a Polymorphic Virus Change Itself?
- How Is Polymorphic Different From Metamorphic Code?
- Why Do Signatures Struggle?
- How Do Modern Tools Detect Polymorphic Malware?
- How Can You Protect Systems?
- What Should You Do After a Detection?
- References
How Does a Polymorphic Virus Change Itself?
A virus, in NIST terms, is code that replicates by inserting copies of itself into other programs or files. A polymorphic virus adds a mutation step. The usual parts are:
- Encrypted body: the payload is stored encrypted, with a fresh key per copy.
- Decryptor stub: a small routine that decrypts the body at run time.
- Mutation engine: rewrites the stub using junk instructions, reordered steps and different registers so no two stubs look alike.
MITRE tracks this family of tricks under T1027 Obfuscated Files or Information, and packers that compress or encrypt executables under T1027.002.
How Is Polymorphic Different From Metamorphic Code?
| Feature | Polymorphic | Metamorphic |
|---|---|---|
| What changes | Decryptor and encryption key | The entire code body |
| Payload in memory | Same after decryption | Differs between copies |
| Weak point for defenders | Decrypted body can be scanned in memory | Behaviour is still the same |
| Complexity for authors | Moderate | High |
Today the same idea appears beyond classic file infectors. Server-side polymorphism, where a download site repacks each file before serving it, gives every victim a unique hash.
Why Do Signatures Struggle?
A traditional signature is a byte pattern or file hash. If every copy has different bytes, a hash list never catches up. Analysts can still write signatures for the decryptor's structure or the decrypted body, but that takes time. NIST SP 800-83 Rev. 1 notes that antivirus should combine signatures with heuristic and behaviour techniques for this reason.
How Do Modern Tools Detect Polymorphic Malware?
| Method | Why it works |
|---|---|
| Emulation and sandboxing | Runs the code safely until it decrypts itself |
| Memory scanning | Finds the stable payload after decryption |
| Behaviour monitoring (EDR) | Flags actions such as injecting into other processes |
| Cloud protection and machine learning | Scores never-seen files within seconds |
| Reputation and prevalence | A unique, unsigned, brand-new file is suspicious |
Microsoft documents cloud-delivered protection for exactly this gap. On Windows you can confirm it is on with a read-only check:
Get-MpPreference | Select-Object MAPSReporting, CloudBlockLevel, DisableRealtimeMonitoringHow Can You Protect Systems?
- Keep the OS, browsers and office software patched.
- Turn on real-time, cloud and behaviour protection, and keep it updated.
- Use application control and attack surface reduction rules to block untrusted executables and macros.
- Remove local admin rights from daily accounts.
- Keep offline, tested backups.
For the wider family of threats, see types of malware and protection, and for where polymorphic viruses sit among other virus classes, see types of viruses in cybersecurity.
What Should You Do After a Detection?
Isolate the device, keep the alert details and hashes, and check whether the same behaviour appears on other hosts, since every copy may have a different hash. Rebuild if you cannot confirm full cleanup. In India, CERT-In requires covered organisations to report notable incidents within 6 hours, and CISA publishes general malware response guidance. Analysing samples is lab work that needs isolation and written authorisation. WebAsha offers malware analysis and SOC training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.