What Is XDR? How It Compares With EDR, NDR and SIEM
XDR, or extended detection and response, is a security platform that collects telemetry from endpoints, network, email, identity and cloud, correlates it into incidents, and lets analysts respond from one console. EDR covers only endpoints, NDR only network traffic, and a SIEM collects and stores logs from everything but needs more tuning to turn them into incidents.
Topic: SOC & Blue Team in Cybersecurity & Ethical Hacking · Explainer
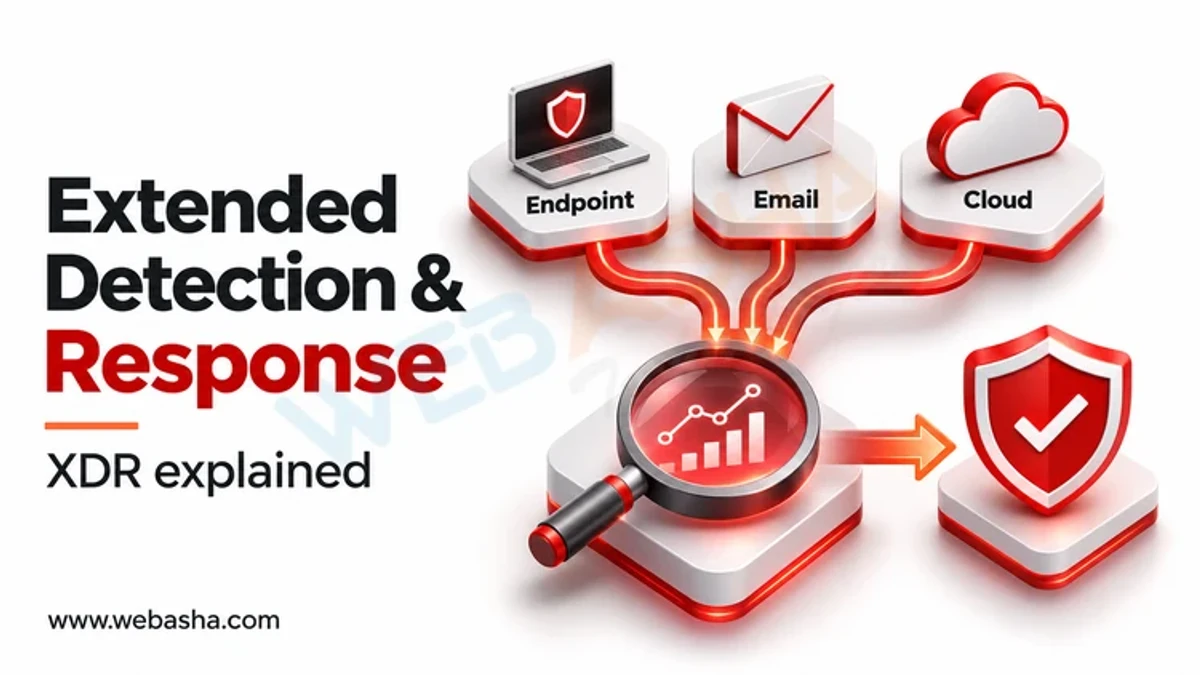
Quick answer: XDR, or extended detection and response, is a security platform that collects telemetry from endpoints, network, email, identity and cloud, correlates it into incidents, and lets analysts respond from one console. EDR covers only endpoints, NDR only network traffic, and a SIEM collects and stores logs from everything but needs more tuning to turn them into incidents. XDR's value is correlation and built-in response, such as isolating a host and disabling an account together. It works best when its data sources cover your real environment and analysts still review what it automates.
Key takeaways
- XDR extends EDR to more data sources and adds cross-source correlation.
- Native XDR uses one vendor's tools; open XDR connects tools from many vendors.
- XDR does not replace a SIEM for long-term log retention and compliance in many organisations.
- Map detections to MITRE ATT&CK to see coverage gaps.
- Automated response should begin with reversible actions.
Table of Contents
- What Is XDR?
- How Does XDR Compare With EDR, NDR and SIEM?
- What Is the Difference Between Native and Open XDR?
- Which Data Sources Does XDR Use?
- What Does an XDR Incident Look Like?
- How Are Detections Written?
- How Should You Evaluate an XDR Platform?
- Who Needs XDR?
- References
What Is XDR?
The term was introduced in 2018 by Nir Zuk, CTO of Palo Alto Networks, to describe detection and response that extends beyond the endpoint. Instead of separate alerts from the email gateway, the endpoint agent and the identity provider, XDR links them into one incident with a timeline, so an analyst sees the whole attack.
How Does XDR Compare With EDR, NDR and SIEM?
| EDR | NDR | SIEM | XDR | |
|---|---|---|---|---|
| Main data | Endpoint processes, files, memory | Network traffic | Logs from any source | Endpoint plus email, identity, cloud, network |
| Correlation | Within the endpoint | Within network flows | Rules written by the team | Built-in, across sources |
| Response | Isolate host, kill process | Limited, often via firewall | Through SOAR integrations | Built-in across connected tools |
| Retention and compliance | Short | Short | Long, flexible | Varies by vendor |
| Tuning effort | Low to medium | Medium | High | Medium |
Many SOCs run XDR for detection and response alongside a SIEM for wide log coverage and audit retention.
What Is the Difference Between Native and Open XDR?
- Native XDR: one vendor's endpoint, email, identity and cloud tools feed its own platform. Integration is deep, but you depend on that vendor.
- Open or hybrid XDR: the platform ingests data from third-party tools through connectors. More flexible, but correlation quality depends on each integration.
Which Data Sources Does XDR Use?
| Source | What it shows |
|---|---|
| Endpoints and servers | Process trees, file changes, registry, scripts |
| Delivered phishing, attachments, clicked links | |
| Identity | Sign-ins, MFA prompts, privilege changes |
| Cloud and SaaS | API calls, configuration changes, data access |
| Network | Connections, DNS, lateral movement |
What Does an XDR Incident Look Like?
One incident, built from five sources and mapped to MITRE ATT&CK:
- Email: a user receives an invoice lure with a link (T1566 Phishing).
- Identity: the user's account signs in from a new country after an MFA push is approved.
- Cloud: the account creates a mailbox forwarding rule (T1114 Email Collection).
- Endpoint: a script launched from the browser downloads a tool (T1059 Command and Scripting Interpreter).
- Network: the laptop connects to a rare external host.
XDR groups these into one incident. The analyst confirms, then responds in one place: reset the password and revoke sessions, remove the forwarding rule and isolate the laptop. These steps fit the detect, respond and recover functions in NIST SP 800-61 Rev. 3.
How Are Detections Written?
Vendors ship built-in detections, and most platforms accept custom rules. Sigma is a vendor-neutral format that can be converted to many query languages. A simple rule for Office applications starting a script interpreter:
title: Office application spawns script interpreter
logsource:
  product: windows
  category: process_creation
detection:
  parent:
    ParentImage|endswith: ['\winword.exe', '\excel.exe', '\outlook.exe']
  child:
    Image|endswith: ['\powershell.exe', '\wscript.exe', '\mshta.exe', '\cmd.exe']
  condition: parent and child
level: high
tags: [attack.execution, attack.t1059]
How Should You Evaluate an XDR Platform?
- Does it cover the tools you already run, especially identity and email?
- Test it with your own attack simulations; compare with MITRE ATT&CK Evaluations results.
- Which response actions are available, and can each be undone?
- How long is data kept, and can you export it to your SIEM?
- What does pricing depend on: endpoints, users or data volume?
Who Needs XDR?
Teams with small SOCs benefit most because XDR reduces manual correlation. Large SOCs often combine XDR with a SIEM and SOAR. Organisations without staff to watch alerts usually buy XDR as a managed service (MDR). Read more on antivirus versus EDR and XDR and MDR and XDR, or talk to a WebAsha training advisor about SOC analyst training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.